

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


GDPR
Every data subject right is operationally supported not just written into a policy
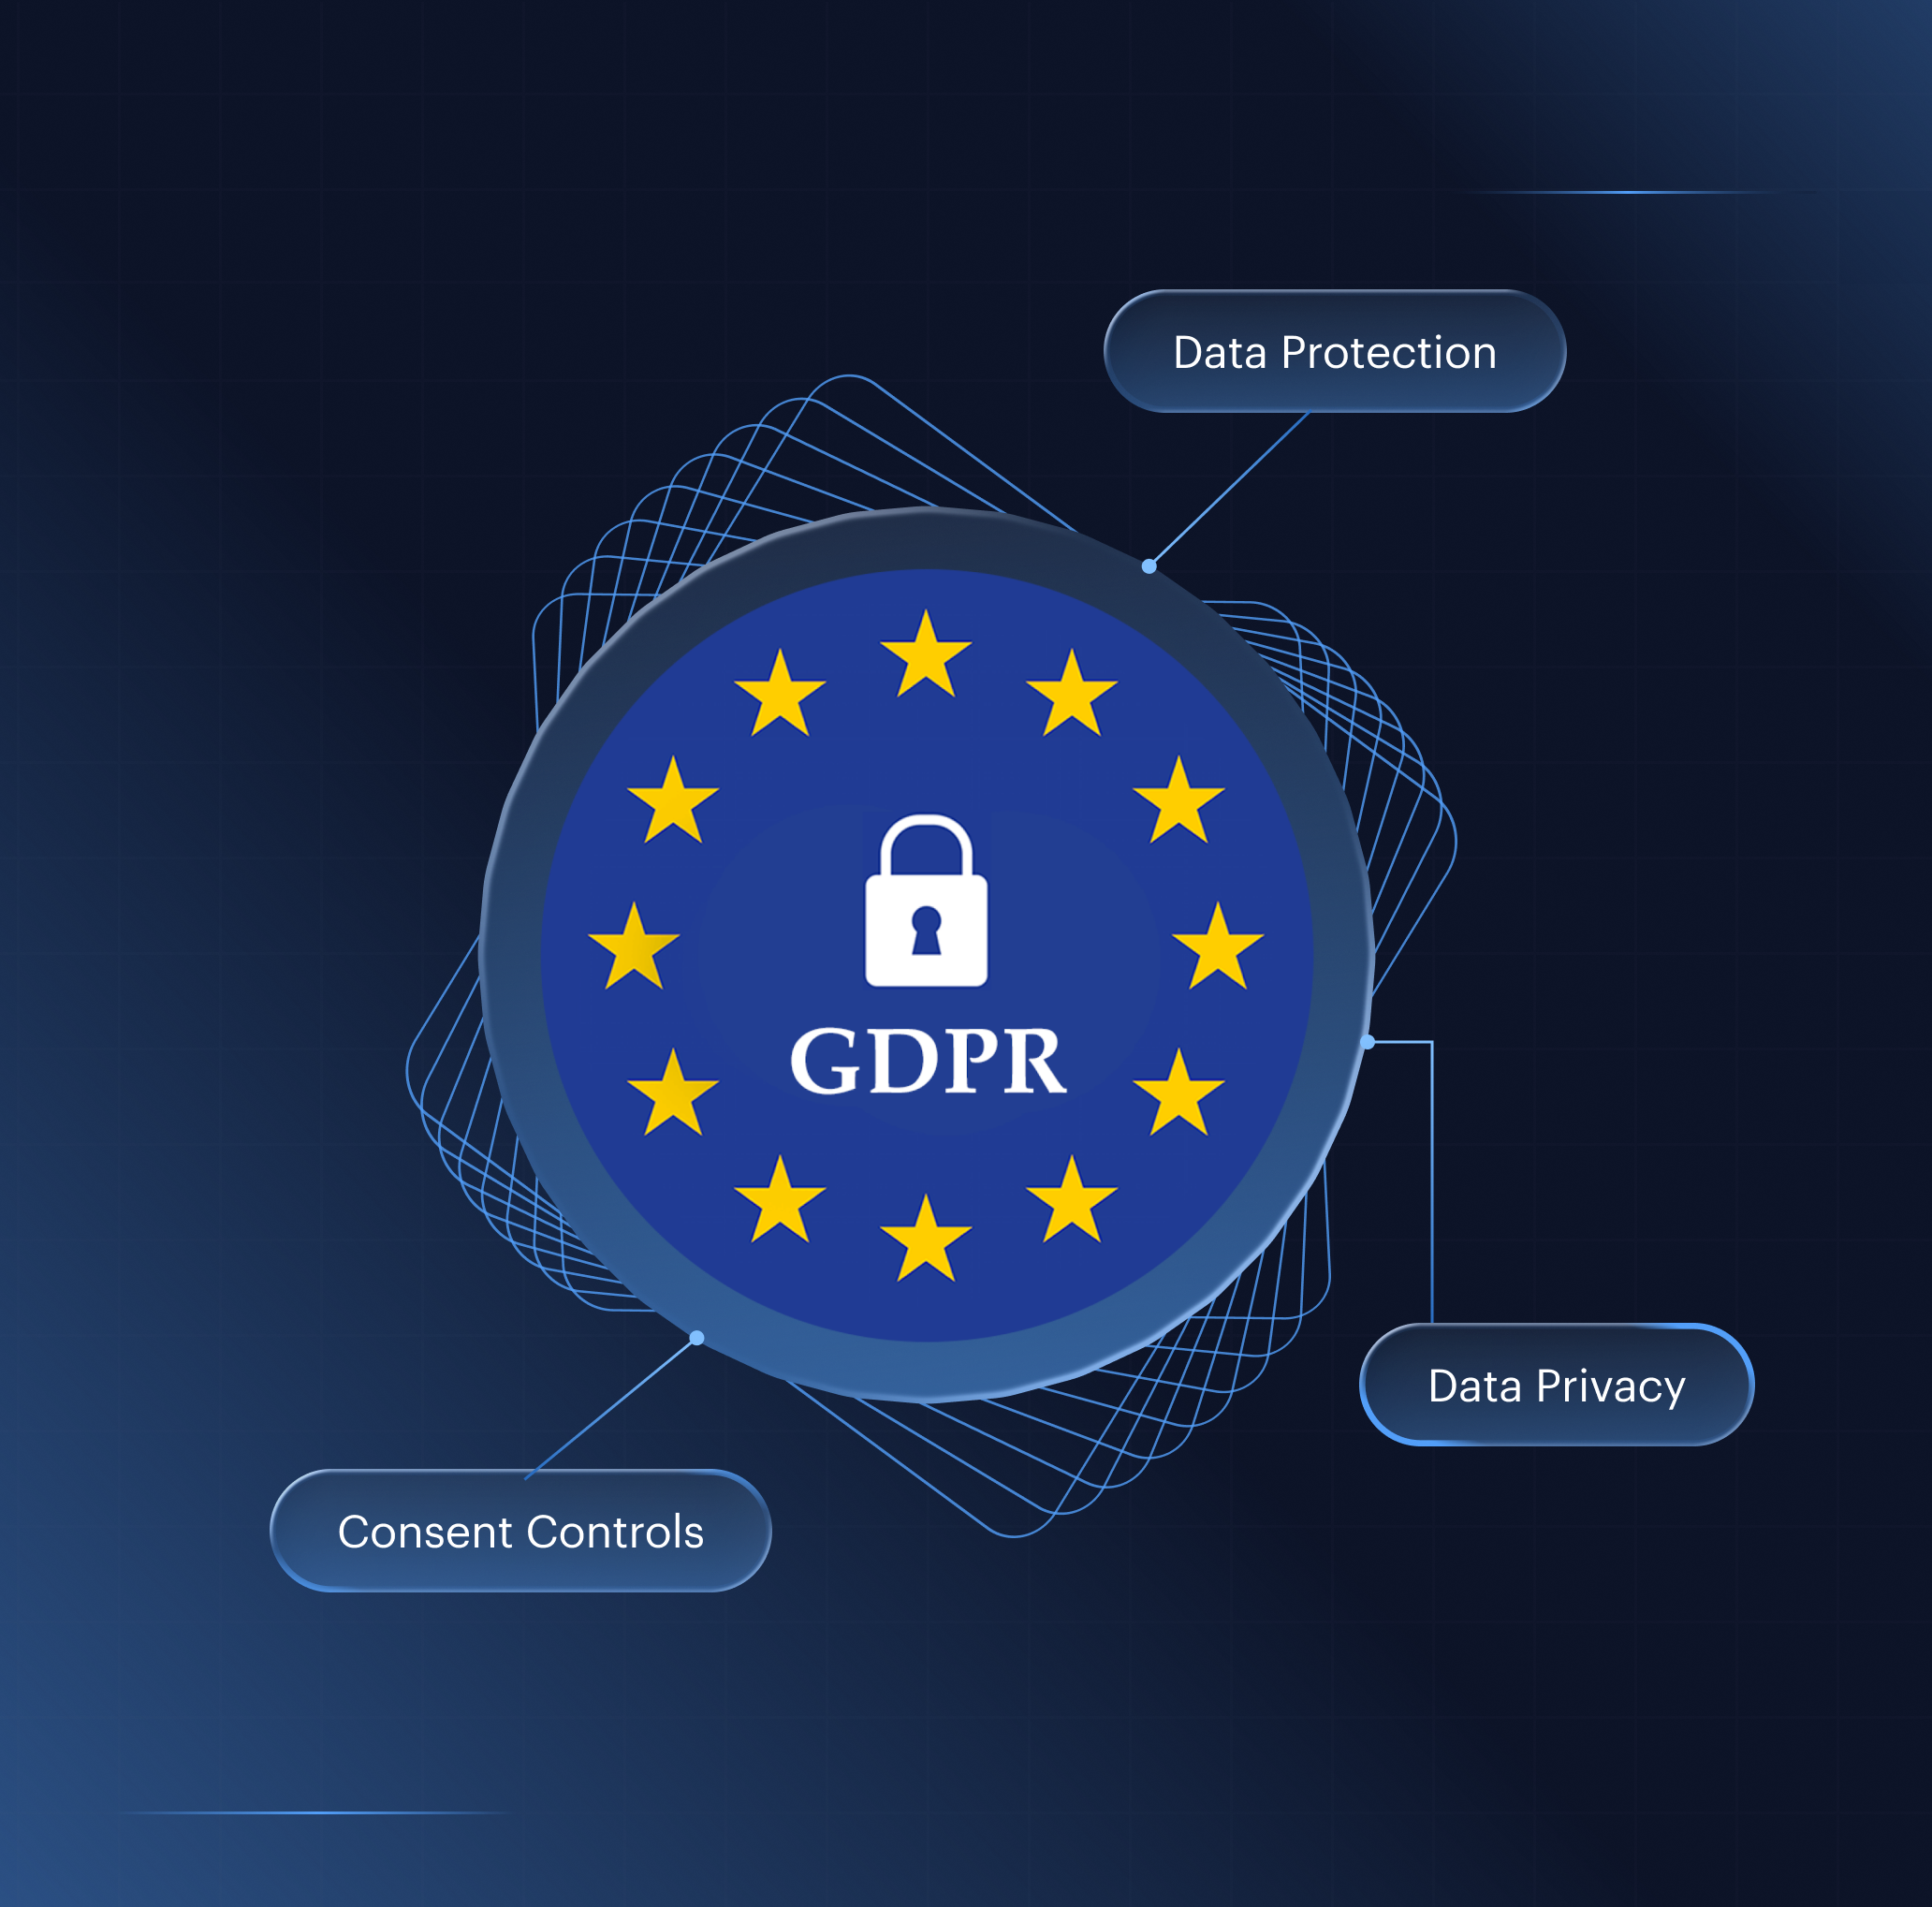
Biometric data and identity documents are Article 9 special category personal data under GDPR, the most tightly regulated data category in EU law. Shufti processes this data under a documented legal basis, retains it only as long as you configure, and operationally supports every data subject right your users may exercise. Shufti GDPR Data Processing Agreement is included in the standard enterprise contract, not an optional add-on.
Certification Overview
What GDPR Covers
Standard Personal Data
Name, email address, phone number, IP address, regulated under GDPR Articles 5 and 6. Requires a lawful basis for processing, reasonable security measures, and data subject rights. Most SaaS platforms operate under this category.
Article 9 Special Category Data
Biometric data used to uniquely identify a person, facial images, and identity document data, the most tightly regulated GDPR category. Requires explicit consent or legal obligation as processing basis, stricter security controls, mandatory data minimisation, full data subject rights support, and a documented Data Protection Agreement before any processing begins.
Why It Matters
Supervisory authorities, Italy's Garante, Ireland's DPC, and France's CNIL, have specifically investigated digital onboarding flows where verification providers retained biometric data beyond necessity, lacked a documented processing basis, or could not operationally support data subject rights. Enforcement actions followed against the businesses that contracted with those providers.
When a user exercises their right to erasure
Your team needs to operationally deliver it, not just acknowledge it. Shufti's API and admin console let you trigger deletion of individual verification records and receive a deletion confirmation as your audit evidence.
EUR 1.2B+
Assessed by an independent AICPA-registered auditor, not a point-in-time snapshot. All five Trust Services Criteria covered: Security, Availability, Processing Integrity, Confidentiality, Privacy.
Certification Assurance
Independently Verified Compliance Standards
Standard
Compliance framework, legal basis, or certification standard covered.
Assessed By
Independent auditor, authority, or responsible assessing party.
Scope
Systems, data flows, regions, features, or operational areas included.
Documentation
Reports, policies, registers, agreements, or evidence available.
How Shufti Maintains It

Shufti GDPR documentation package includes: the Article 28-compliant DPA, sub-processor register (updated within 30 days of any change), data retention and deletion policy, and technical documentation of how data subject rights are operationally supported. All available on request before you sign a contract.
EU-resident data is processed on EU infrastructure. UK-resident data is processed under UK GDPR. US and APAC regional deployments are available for non-EU data flows.