

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


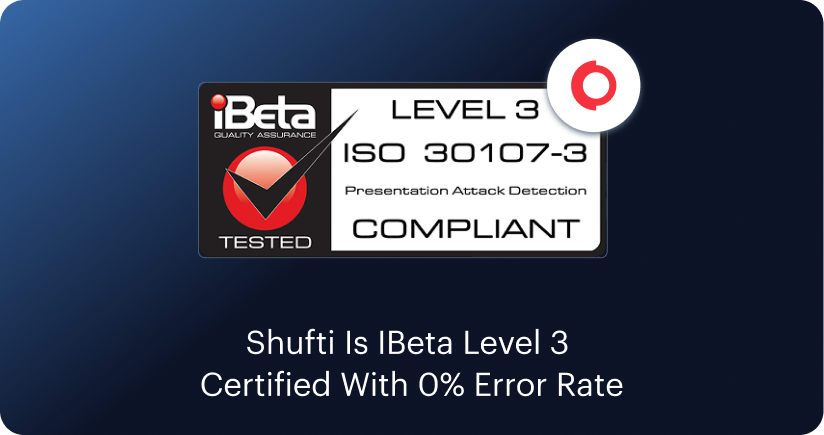
QG-GDPR
Shufti’s GDPR compliance was independently tested not self-declared
QG-GDPR Fundamentals is a third-party certification issued by QG Business Solutions, a UK-based accreditation and certification body. It is distinct from GDPR regulatory compliance: it is an independent audit that validates how an organisation's internal GDPR processes, data handling procedures, and risk controls actually operate. Shufti holds QG-GDPR Fundamentals certification.
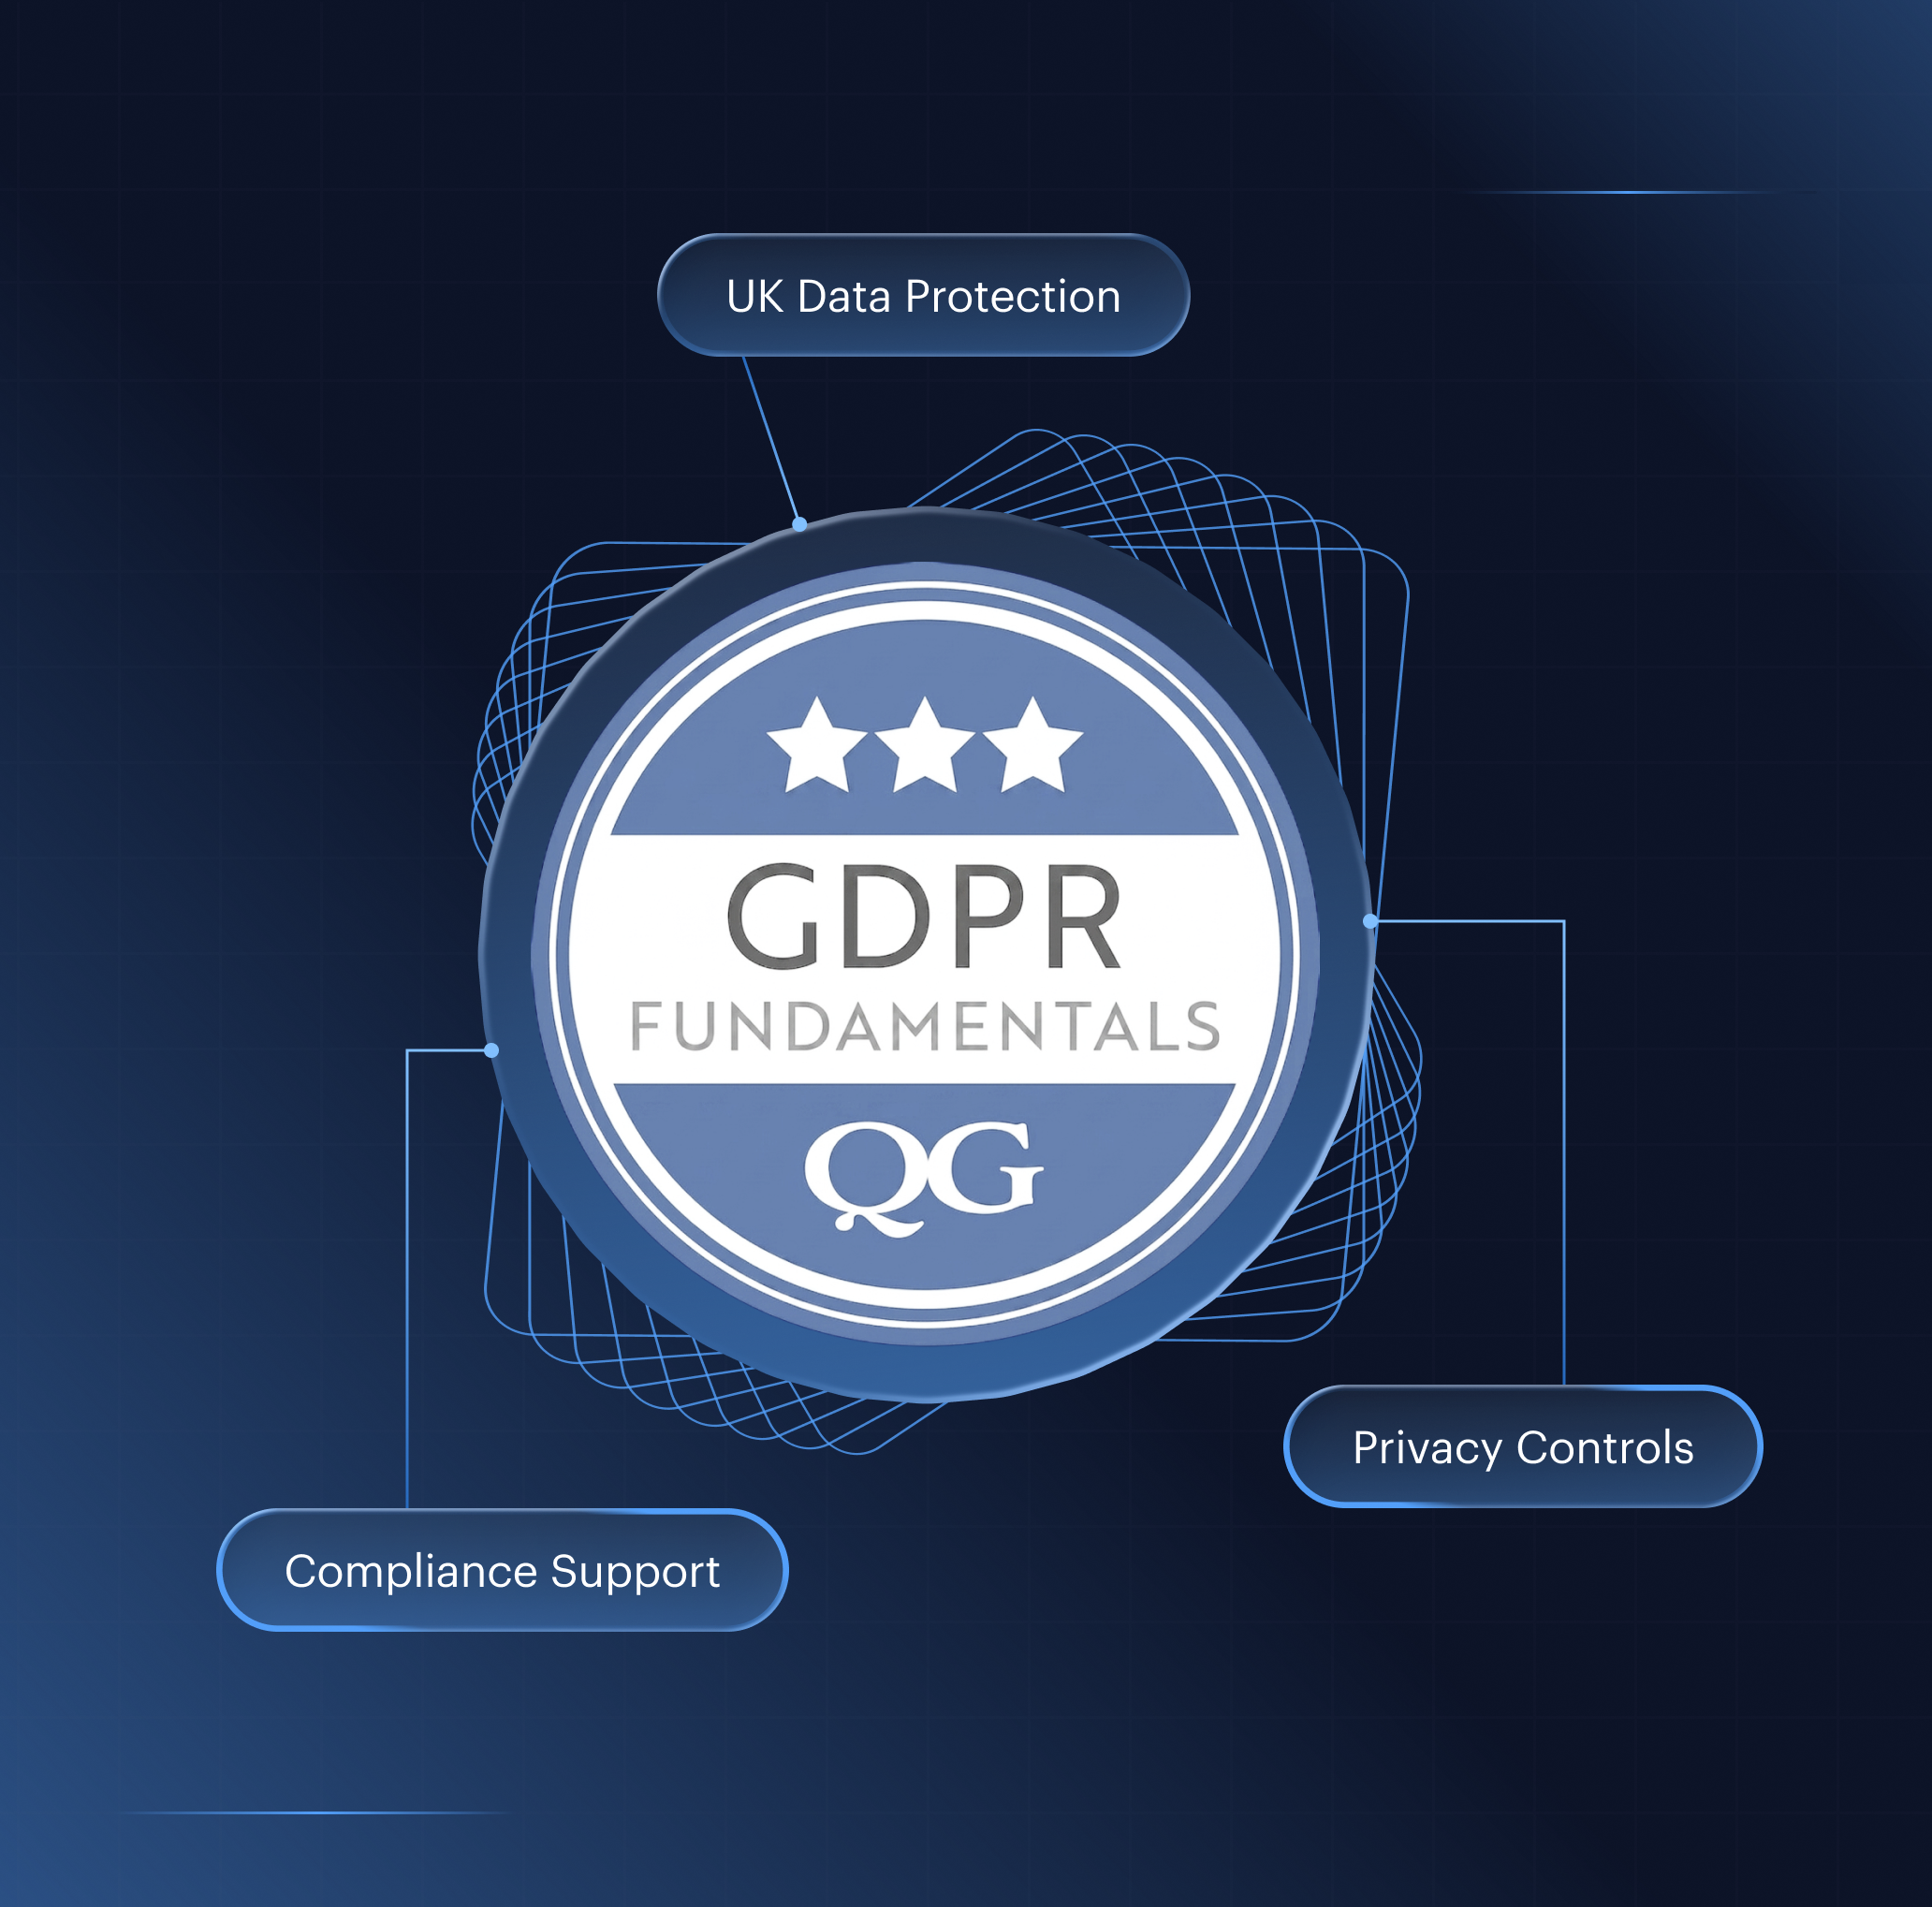
Certification Overview
What QG-GDPR Covers
GDPR Regulatory Compliance
The legal obligations: a lawful basis for processing, an Article 28-compliant DPA, data minimisation, deletion workflows, and data subject rights support. What Shufti must do, and does, as a data processor under EU and UK law. Documented in contracts and technical controls.
QG-GDPR Certification
What QG Business Solutions independently assessed: how Shufti's internal GDPR processes actually operate, whether data processing documentation is complete and enforceable, whether risk assessment procedures are robust, and whether technical measures to prevent data breaches are implemented. An external audit, not a self-declared compliance statement.
Why It Matters
A vendor who self-declares GDPR compliance has no external validation of that claim. They may have a privacy policy, a DPA template, and a deletion procedure, but whether those processes actually function as documented is untested. QG-GDPR certification means a third party has tested ours.
For procurement and legal teams evaluating verification vendors
QG-GDPR certification provides a layer of assurance beyond contractual promises. It confirms that Shufti's GDPR compliance infrastructure has been independently reviewed and meets an audited standard, reducing the due diligence burden on your team.
QG Fundamentals
QG Business Solutions is a UK accreditation body, not a self-certification framework. Verifiable at qgstandards.co.uk certified companies register.
Certification Assurance
Independently Verified Compliance Standards
Standard
QG-GDPR Fundamentals Management Standards, structured against UK and EU GDPR requirements.
Assessed By
QG Business Solutions, a UK-based independent accreditation and certification body.
Scope
Data collection, storage processes, risk assessment procedures, and organisational data protection measures.
Documentation
Certificate available on request, with verification through the QG certified companies register.
How Shufti Maintains It

Shufti's QG-GDPR certification is issued by QG Business Solutions and is verifiable on the QG-GDPR certified companies register at qgstandards.co.uk. The certificate is available on request and can be included in vendor due diligence packs alongside Shufti GDPR Data Processing Agreement.
This certification complements Shufti broader GDPR compliance posture: Article 28-compliant DPA, configurable data retention and deletion, data subject rights via API, and EU-resident data processing on EU infrastructure. Together they give your legal and compliance team both the contractual protections and the independent validation.