

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


IDENTITY VERIFICATION FOR BANKS
One platform to secure
the full banking customer lifecycle
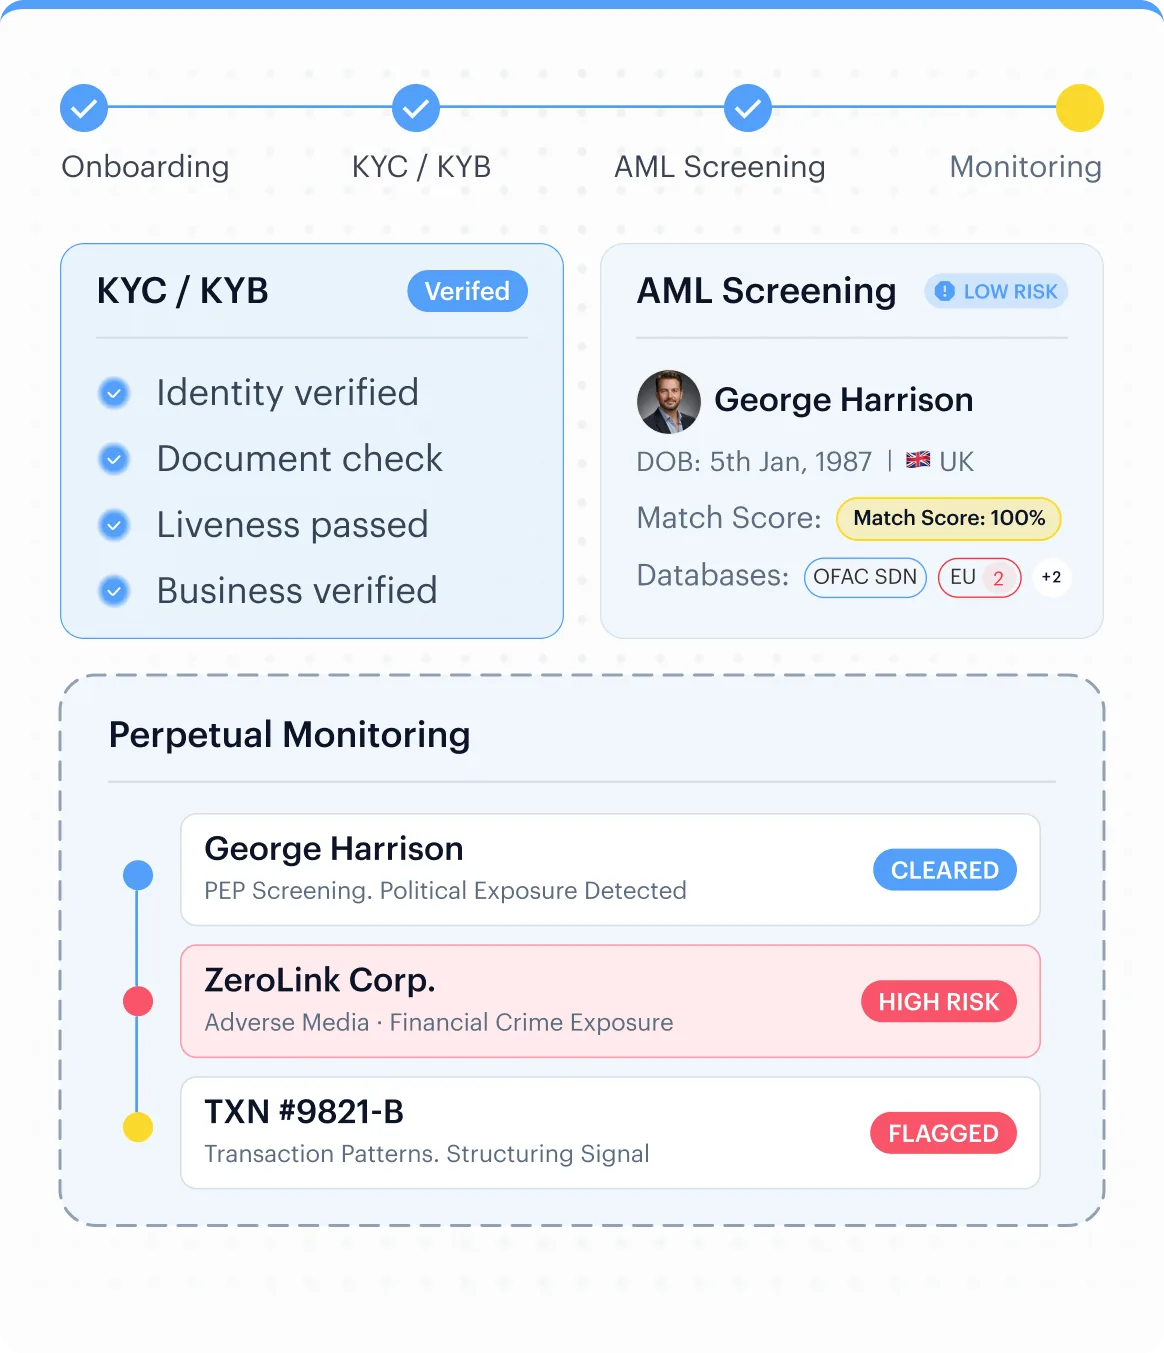
KYC, KYB, AML screening and perpetual monitoring in one integration, with no aggregators, no fragmented audit trail, and full data processor status under GDPR Article 28.
Proven Performance
Shufti impact, by the numbers
Trusted by Leading Digital Enterprises Worldwide
COMPLIANCE WITHOUT COMPROMISE
Why banks choose Shufti
Stay Examination-Ready
TD Bank’s $3.09B BSA/AML settlement (October 2024) reinforced what OCC Bulletin 2023-17 and AMLD6 (deadline: 10 July 2027) demand: every CDD and EDD decision must come from a single, auditable source. Shufti records every verification, screening and monitoring decision in a tamper-evident audit trail, exportable in under five minutes.
Stop Fraud Before It Onboards
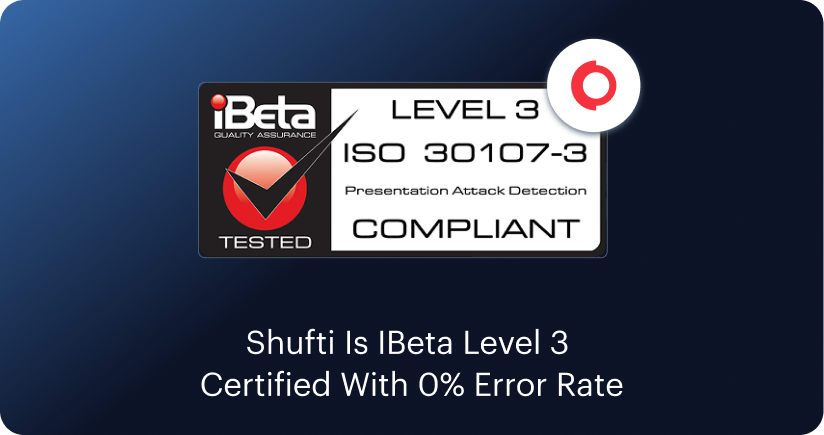
Synthetic identity fraud is retail banking’s largest fraud-loss vector, with AI-generated documents and deepfakes bypassing legacy checks. Shufti’s passive liveness detection is ISO/IEC 30107-3 PAD Level 3 certified, validated by iBETA in May 2026 with 0% APCER and 0% BPCER.
Scale Without Adding Vendors
67% of banks have lost clients due to slow onboarding. Multiple vendors create integration debt, additional DPAs and audit gaps. Shufti’s single REST API combines document verification, biometrics, AML screening, KYB with UBO resolution and perpetual monitoring, replacing 3–5 vendor relationships with one platform.
Secure every stage of the
banking customer lifecycle
Sign Up
Bot Account Farming
Challenge
Fraud rings bulk-register accounts to exploit sign-up bonuses and overdrafts.
Solution
Shufti flags emulator use, proxy rotation and machine-speed form fills before creation.
Stolen Identity Application
Challenge
Fraudsters use breached PII to open accounts without the victim's knowledge.
Solution
Shufti flags mismatched contact details and requires a live selfie matching the document holder.
Mule Recruitment Onboarding
Challenge
Scam-recruited individuals open accounts to layer criminal proceeds.
Solution
Shufti checks identity signals against mule patterns and screens applicants against mule watchlists before opening.
Velocity and Anomaly Attacks
Challenge
Fraud rings flood sign-up flows from shared infrastructure to slip past manual review.
Solution
Shufti identifies coordinated device and network signals, then correlates velocity against prior rejections.
Duplicate Registration
Challenge
One person opens multiple accounts under name variations to exceed FSCS limits or claim bonuses twice.
Solution
Shufti catches the same biometric across different identities and links applications from shared infrastructure.

Synthetic Identity Registration
Challenge
Attackers blend real and fabricated PII to open accounts with no genuine financial history.
Solution
Shufti cross-references details against government and credit bureau records, and flags packages linked to previously rejected profiles.
Verify Identity (KYC)
Document Forgery
Challenge
Fraudsters submit tampered or AI-generated IDs bought on dark-web markets.
Solution
Shufti applies forensic tamper detection across MRZ, fonts and AI artefacts, and reads the chip in e-passports and chip-enabled IDs to bypass image manipulation.
Deepfake and AI Face Attack
Challenge
Attackers present an AI-generated face video at the selfie step to impersonate the account holder.
Solution
Shufti uses 3D depth analysis and micro-movement detection to spot synthetic video, and flags virtual camera drivers at OS level before capture.

Camera Injection Attack
Challenge
Fraudsters inject a pre-recorded or synthetic image into the KYC stream, bypassing the physical camera.
Solution
Shufti flags virtual camera drivers at OS level before capture, and adds a liveness layer that rejects injected feeds.
Identity Pack Fraud
Challenge
Dark-web KYC kits pair a forged ID with a synthetic selfie to clear onboarding in one submission.
Solution
Shufti requires the chip a purchased kit cannot replicate, runs forensic checks on the document, and cross-references identity against authoritative sources.
Business Ownership Concealment
Challenge
A sanctioned or criminal UBO hides behind nominee directors and layered holding structures.
Solution
Shufti traces the full ownership chain across 140+ jurisdictions to identify the true owner, and screens every UBO against 4,000+ watchlists and 215+ sanctions regimes.
KYC Recycling
Challenge
The same identity package, verified or misused at another bank, is reused to avoid re-screening.
Solution
Shufti flags the biometric as already linked to a known identity under different documents, and surfaces prior rejection signals for that identity.
Risk Screening
PEP or Sanctioned Person Onboarding
Challenge
A politically exposed or sanctioned individual uses aliases or transliterated names to slip past the initial check.
Solution
Shufti applies fuzzy matching across 4,000+ watchlists and 215+ sanctions regimes, covering all four PEP tiers, and confirms or excludes the hit.
Adverse Media Concealment
Challenge
A customer's criminal history sits only in regional or local-language publications that English-only tools miss.
Solution
Shufti covers 50,000+ adverse media sources across 80+ languages, and attaches flagged evidence to the customer's CDD profile.
Beneficial Owner Sanctions Concealment
Challenge
A sanctioned UBO hides behind a chain of nominees, trusts or holding companies.
Solution
Shufti traces the ownership structure layer by layer using the FATF 25% threshold, and runs every UBO against global sanctions and PEP lists.
High-Risk Jurisdiction Misrepresentation
Challenge
A customer in a FATF grey-listed country declares a false address and uses a VPN to mask their IP.
Solution
Shufti cross-references the declared address against authoritative sources, and flags mismatches with the customer's verifiable data footprint.
Source-of-Funds Fabrication
Challenge
Fabricated payslips or bank statements are submitted to pass source-of-funds EDD checks.
Solution
Shufti detects template fraud, font anomalies and digital artefacts in supporting documents, and cross-references declared income against the applicant's financial footprint.
Accreditation and Eligibility Fraud
Challenge
A customer misrepresents income, residency or financial status for preferential rates or higher credit limits.
Solution
Shufti validates eligibility documents against authoritative sources, applies forensic analysis to supporting documentation, and checks for adverse media or watchlist hits.
Account Opening
Application and Loan Fraud
Challenge
A customer submits false information on a credit or mortgage application to obtain funds they wouldn't qualify for.
Solution
Shufti validates identity fields against government and credit bureau records, applies forensic analysis to supporting documents, and captures a non-repudiable consent record.
Bust-out Fraud
Challenge
A fraudster builds a credit history over months, then maxes out all lines and disappears before the bureau updates.
Solution
Shufti tracks behavioural and network signals for bust-out patterns, and flags unusual credit utilisation alongside shared device or identity signals.
Loan Stacking
Challenge
The same applicant submits simultaneous applications to multiple lenders before bureau data updates.
Solution
Shufti links applications from the same device or network, surfaces the cross-institution pattern, and flags the identity as already active elsewhere.
Second-Party Fraud
Challenge
A real account holder knowingly acts as a mule, opening accounts or sharing credentials for payment.
Solution
Shufti detects the same face across multiple accounts with coordinated timing, and cross-references device and identity signals between applicants.
Fraudulent Business Account Application
Challenge
A newly incorporated shell company applies for a business account to access credit or launder funds.
Solution
Shufti flags entities with no genuine operating history, maps the ownership chain for sanctioned or PEP-exposed UBOs, and screens each person before opening.
First-Party Fraud
Challenge
A legitimate customer intentionally submits inaccurate income or employment data for better credit terms.
Solution
Shufti cross-references declared income and residency against authoritative data, checks documents for signs of editing, and matches known first-party fraud signals.
Fund Account
Money Mule Deposit
Challenge
A verified account holder receives criminal funds from third parties and rapidly moves the balance out.
Solution
Shufti detects the third-party funding pattern, flags the rapid inbound-to-outbound sequence, and checks each transfer against sanctions and watchlist data.
Structuring and Smurfing
Challenge
Criminal proceeds are broken into sub-threshold cash deposits timed to avoid CTR and AML alerts.
Solution
Shufti analyses deposit patterns over time for structuring, and surfaces coordinated activity across accounts sharing device or identity signals.
Stolen Card Funding
Challenge
A stolen debit or credit card funds an account ahead of a rapid cash-out.
Solution
Shufti flags devices with known fraud associations at the funding instruction, and detects the deposit-to-withdrawal velocity typical of card cashing.
Chargeback Fraud
Challenge
A customer funds and extracts their account, then disputes the original charge to recover the payment.
Solution
Shufti captures a timestamped, non-repudiable record of the funding authorisation, removing the repudiation basis when a dispute is raised.
Terrorist Financing
Challenge
Funds linked to a FATF-designated terrorist organisation are structured to stay below reporting thresholds.
Solution
Shufti checks every inbound funding event against terrorism financing watchlists, PEP lists and adverse media, and escalates unusual deposit patterns for SAR review.
Transact / Pay

Authorised Push Payment (APP) Fraud
Challenge
A customer is socially engineered into authorising a payment to a fraudster.
Solution
Shufti detects hesitation and interaction patterns inconsistent with a routine transfer, captures a timestamped UK PSR evidence record, and flags the destination against known APP indicators.
Romance and Investment Scams
Challenge
A customer is manipulated over weeks into transferring large sums to fake platforms or romance fraudsters.
Solution
Shufti identifies interaction patterns consistent with an emotionally manipulated customer, flags unusual destinations and escalating amounts, and records the event for regulatory reporting.
Impersonation Scams
Challenge
A fraudster impersonates a bank, regulator or law enforcement officer to coerce an urgent transfer.
Solution
Shufti detects authorisation under unusual pressure and deviation from established patterns, checks the destination against known scam indicators, and creates a timestamped record.
Layering and Structuring
Challenge
Illicit funds move through multiple transactions and accounts to obscure their origin.
Solution
Shufti analyses the full transaction sequence for layering patterns, including cross-account flows and round-number amounts, and checks each transaction against watchlists.
Withdraw / Transfer
Account Takeover Withdrawal
Challenge
An attacker with a compromised account attempts to drain the balance externally.
Solution
Shufti requires a live selfie matched to the enrolled KYC record above a set threshold, and flags attempts from unrecognised devices.
Transfer to Sanctioned Account
Challenge
A customer initiates a transfer to a beneficiary linked to a sanctioned or OFAC-listed entity.
Solution
Shufti checks every destination against live sanctions databases, 4,000+ watchlists and 215+ regimes before executing, and flags patterns tied to illicit fund movement.
Rapid Cash-Out Scheme
Challenge
Funds are deposited and withdrawn within minutes, before monitoring alerts can fire.
Solution
Shufti detects deposit-to-withdrawal velocity in real time, applies an automatic hold on full-balance withdrawals, and requires re-verification to lift it.
Invoice Redirection
Challenge
Payment instructions are intercepted and replaced with the fraudster's details, redirecting funds.
Solution
Shufti requires re-verification when a new beneficiary is added, and flags the first payment to it for review.
Fraudulent Beneficiary Addition
Challenge
An attacker with partial access adds their own account as a payout destination to drain funds later.
Solution
Shufti requires a live selfie matched to the enrolled KYC record before confirming any new payout destination, and triggers a step-up challenge from unrecognised devices.
Account Management
Password Reset Account Takeover
Challenge
An attacker intercepts a password reset via SIM swap or email compromise for full control.
Solution
Shufti requires a live selfie matched to the enrolled KYC record during recovery, removes SMS interception via TOTP-based MFA, and escalates attempts from unrecognised devices.
Support Social Engineering
Challenge
An attacker uses stolen PII to impersonate a customer in a support call, requesting changes or limit increases.
Solution
Shufti requires biometric re-verification for sensitive changes, and flags anomalies distinguishing a scripted attacker from the genuine holder.
Identity Detail Change to Evade Screening
Challenge
A customer who received an AML flag alters their name or address to reset or bypass the result.
Solution
Shufti re-runs screening automatically on any identity-field change against 4,000+ watchlists, confirms new documents are genuine, and determines if the change is legitimate.
Limit Upgrade Document Fraud
Challenge
A customer submits forged documents to move to a higher tier or lower-risk classification.
Solution
Shufti applies full forensic checks at the upgrade stage, including tamper detection and MRZ validation, checks any chip-enabled document, and requires the face to match the biometric enrolled at opening.
Session Hijacking
Challenge
A stolen session token changes account settings or adds beneficiaries without a new login.
Solution
Shufti monitors interaction patterns to detect a mid-session operator change, corroborates the device environment, and triggers re-authentication on deviation.
MFA Fatigue Attack
Challenge
An attacker floods the customer with repeated MFA pushes until one is accepted by mistake.
Solution
Shufti limits prompt frequency, escalates repeated rejections as a fraud signal, and replaces SMS-based MFA with biometrics for high-risk actions.
Account Maintenance
Sanctions Re-listing Not Caught
Challenge
A customer clean at onboarding is later added to a sanctions or PEP list, unnoticed for months.
Solution
Shufti monitors all active records against watchlist updates on a 15-minute cycle, and routes flagged accounts into EDD automatically.
Risk Profile Drift
Challenge
A customer's transactions gradually shift toward money laundering patterns while the onboarding risk rating never updates.
Solution
Shufti monitors behavioural and transactional signals continuously, updates the risk score dynamically, and escalates the account once a threshold is crossed.
Periodic Review Evasion
Challenge
A customer suppresses suspicious activity ahead of the annual review, then resumes it once it passes.
Solution
Shufti is event-driven, not calendar-driven, evaluating the full account history so a suppression-then-resumption pattern triggers review regardless of timing.
PEP Status Change Not Reflected
Challenge
A customer's PEP status changes after onboarding, but the CDD record keeps applying standard diligence.
Solution
Shufti detects PEP changes within the 15-minute refresh cycle, reclassifies the customer, and triggers an EDD workflow for updated source-of-funds documentation.
Emerging Adverse Media
Challenge
Negative news links an existing customer to fraud or organised crime in a regional publication, after opening.
Solution
Shufti monitors 50,000+ adverse media sources continuously, attaching sourced, severity-classified evidence to the customer's risk profile.
Identity Swap at Re-Verification
Challenge
A customer submits different documents at scheduled re-KYC, claiming the original was lost, to assume a new identity.
Solution
Shufti requires the current selfie to match the biometric enrolled at opening regardless of new documents, and applies forensic analysis to what's submitted.
Account Closure
Pre-SAR Closure
Challenge
A customer who suspects an AML investigation requests closure and invokes GDPR erasure before a SAR can be filed.
Solution
Shufti enforces BSA five-year and FATF Recommendation 11 retention periods that erasure requests cannot override, and runs a final review before closure.
Regulatory Data Destruction Request
Challenge
A customer requests deletion of records that must be retained under BSA, FATF or local AML legislation, citing GDPR.
Solution
Shufti enforces statutory retention minimums that requests cannot override, deletes data outside the retention period, and generates a certificate or notice per item.
Re-application Under New Identity
Challenge
An offboarded customer reapplies with different documents to bypass the closure record.
Solution
Shufti screens every new applicant's selfie against all previous accounts, including deactivated ones, and checks the identity against watchlists.
Bust-out at Closure
Challenge
A customer maxes out all available credit lines immediately before requesting closure.
Solution
Shufti detects rapid credit utilisation preceding a closure request, distinct from normal wind-down, and cross-references accounts with coordinated bust-out timing.
Balance Extraction Before Closure
Challenge
A customer withdraws their full balance right after a compliance communication, then requests closure before a hold lands.
Solution
Shufti flags full-balance withdrawals following compliance-related activity, applies an automatic hold, and requires biometric authentication before funds release.
Built for every role that owns the onboarding decision
Combine products across identity, compliance, and fraud defence to build a verification stack that meets your regulatory requirements; without rebuilding the integration each time the rulebook changes.
CCO
No more reconciling vendor data by hand. Shufti generates a unified, jurisdiction-specific evidence package per customer, with every CDD, EDD, screening and monitoring decision stored in one tamper-evident log, exportable in under five minutes.
Head of Digital Banking
67% of banks lose customers at identity verification. Risk-tier orchestration applies lighter checks to low-risk applicants and reserves document capture and liveness for higher-risk profiles, keeping median time-to-decision under 30 seconds without cutting compliance where it matters.
Head of Engineering
One REST API covers the full customer lifecycle: document verification, biometric liveness, AML screening, KYB and perpetual monitoring. Sandbox setup takes minutes, SR 11-7 evidence packages support AI/ML validation, and uptime has held at 99.95% across all regions.
Fraud Analyst
Fraud Hub surfaces the reason behind every flag before the case opens, with cross-customer network signals, device links and biometric deduplication results in one view, cutting review time because context is already assembled when the alert fires.
Don’t just take our word for it, hear from our customers
The confidence our clients share
The future of digital identity is defined by trust, interoperability, and regulatory alignment, so our partnership with Shufti reinforces DevCode Identity’s commitment to supporting our global customers with the most secure, best-in-class, compliant identity verification solutions available today.
Combining our Conversion Driven Compliance Orchestration Platform with Shufti’s global KYC and IDV capabilities allows our customers not only to navigate complex regulatory demands but also to maintain a seamless customer onboarding experience with the highest achievable conversion rates.
Everything you need to know in one place
Frequently asked questions
Banks in the US are subject to the BSA, the PATRIOT Act CIP requirements and the FinCEN CDD Final Rule (31 CFR § 1010.230). EU-supervised banks must comply with AMLR 2024/1624, which applies from 10 July 2027, and AMLD6, which member states must transpose by the same date. OCC Bulletin 2023-17 governs third-party risk for US national banks. FATF Recommendations 10, 11 and 17 apply globally.
Risk-based orchestration routes low-risk customers through passive eIDV and reserves document capture and biometric liveness for higher-risk profiles. Every route produces a CIP-compliant evidence package with extracted fields, document hashes and confidence scores. Median time-to-decision is under 30 seconds at P50.
ISO/IEC 30107-3 PAD Level 3 is the highest independent certification tier for presentation attack detection. iBETA tested Shufti's passive liveness system against physical artefacts, video replay attacks and deepfake injection vectors in May 2026. The system passed with 0% APCER and 0% BPCER on both iOS and Android, making Shufti the third company globally and the first European company to achieve this conformance.
Shufti operates as a data processor under GDPR Article 28 and UK DPA 2018. The bank retains full controller status. A single DPA covers all Shufti products. Data residency options include EU, UK and US hosting. Deletion certificates are generated for every erasure request, exportable for examination and audit purposes.
Yes. Deployment options include cloud (SaaS), hybrid, on-premise and private cloud. For banks with data sovereignty requirements or internal policies against cloud processing of biometric data, the full verification and screening stack runs within the bank's own infrastructure. All deployment models produce the same tamper-evident audit trail and evidence exports.
Sandbox setup takes under five minutes. Production integration typically takes two to eight weeks depending on the number of verification flows configured and whether on-premise deployment is required. A single REST API covers the full customer lifecycle, which eliminates the multi-vendor integration cycles that extend most deployment timelines.
Give your next examiner one source of truth
BSA, AMLR, FATF and OCC 2023-17 all expect a verification architecture that connects onboarding identity to ongoing transaction monitoring. Fragmented vendor stacks cannot produce a unified audit trail, cannot share identity records across compliance functions, and cannot update rules from one source. See how Shufti's platform holds up against your current stack.
Your Go-To for KYC/AML & Fraud
Resources
26 February, 2026
eIDV for Banking
Docless verification for banks, covering how database-backed checks onboard new customers without any document upload at all, while still meeting AML obligations.
Brochure
22 October, 2021
On-Premises Identity Verification for Banks
Written for banks that cannot send identity data off premise. Covers data sovereignty, security requirements, and guarding against fraud and loss at every stage.
Guide
10 September, 2026
ACU Credit Union Became the Caribbean's First Financial Institution to Offer Fully Digital Onboarding
How ACU Curaçao, working with implementation partner Axioma, became the first financial institution in the Caribbean to onboard members fully online, at 86.9% approval.
Case Study