

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


FRAUD PREVENTION
Fraud Prevention Software for the Full Customer Lifecycle
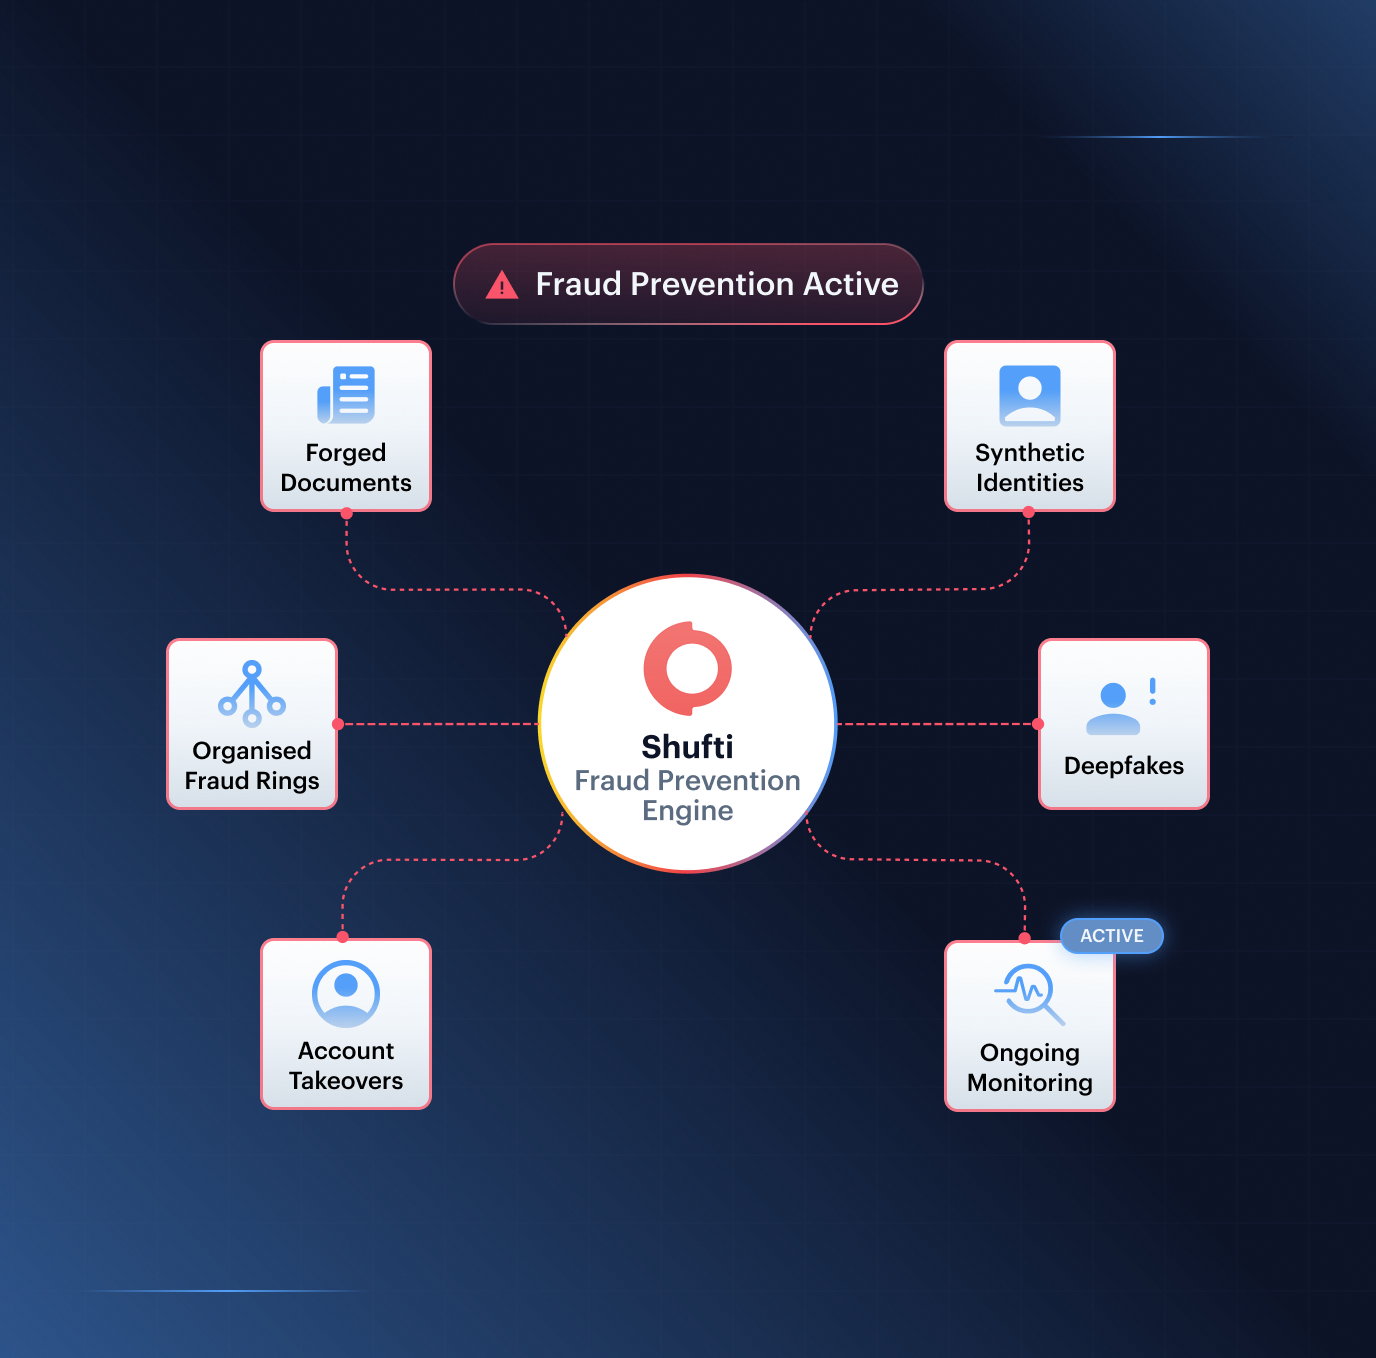
Shufti's fraud prevention platform connects identity, device, behavioural, and transaction signals in one place. 40+ ensemble AI models score risk across the full customer lifecycle, from onboarding through every session after login.


Three Operational Failures That Let Fraud Through
Verification Gaps Let Fraud Through
Legacy verification stacks were built for older risk patterns. Fraud teams now face threats that move faster than these systems can detect. The gap is no longer a rare edge case. It creates live exposure. Shufti's detection is built against the fraud methods that current verification stacks cannot catch.
Fragmented Tools, Incomplete Risk View
Identity, AML, transaction, and device checks often sit in separate tools. This leaves analysts without a full view of user risk. Shufti connects verification, device, behaviour, and AML signals in one user record.
False Positives Are Consuming Compliance Capacity
Legacy AML engines can produce 90 to 95% false positives at tier-1 banks. MLROs spend 80% or more of their time on Level 1 triage. Shufti checks each AML alert against the verified identity before analyst review.
EXPLORE THE STACK
Fraud Detection and Prevention Across Onboarding, Login and Transactions
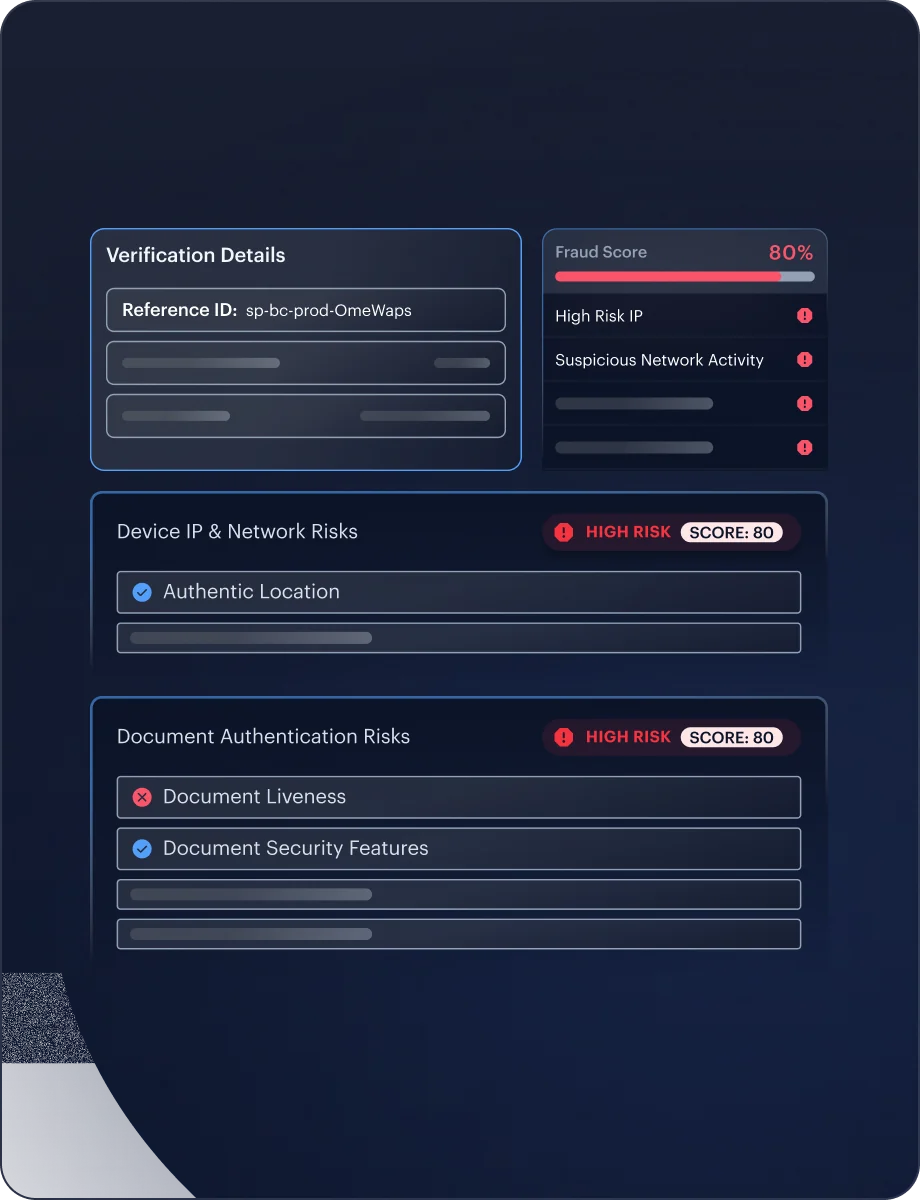
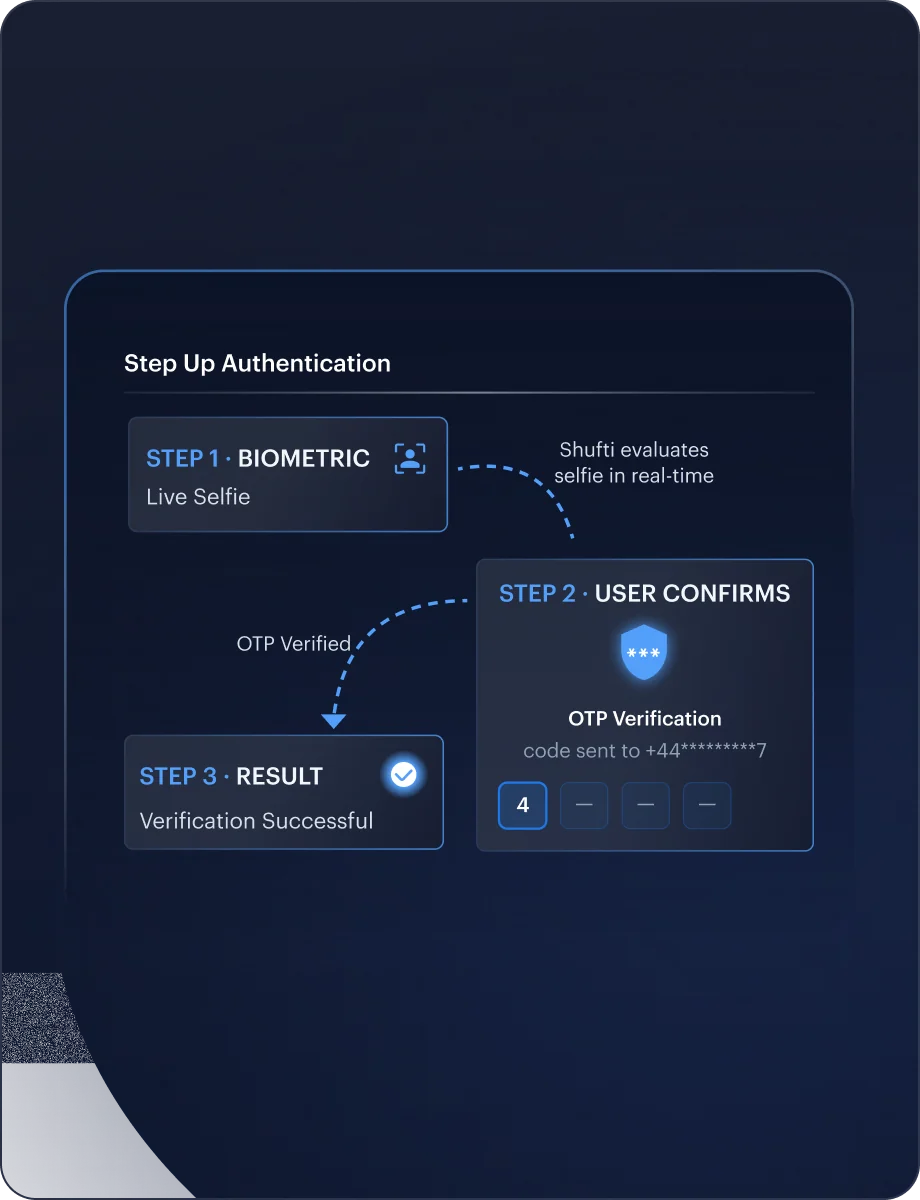
Every session monitored to block account takeover
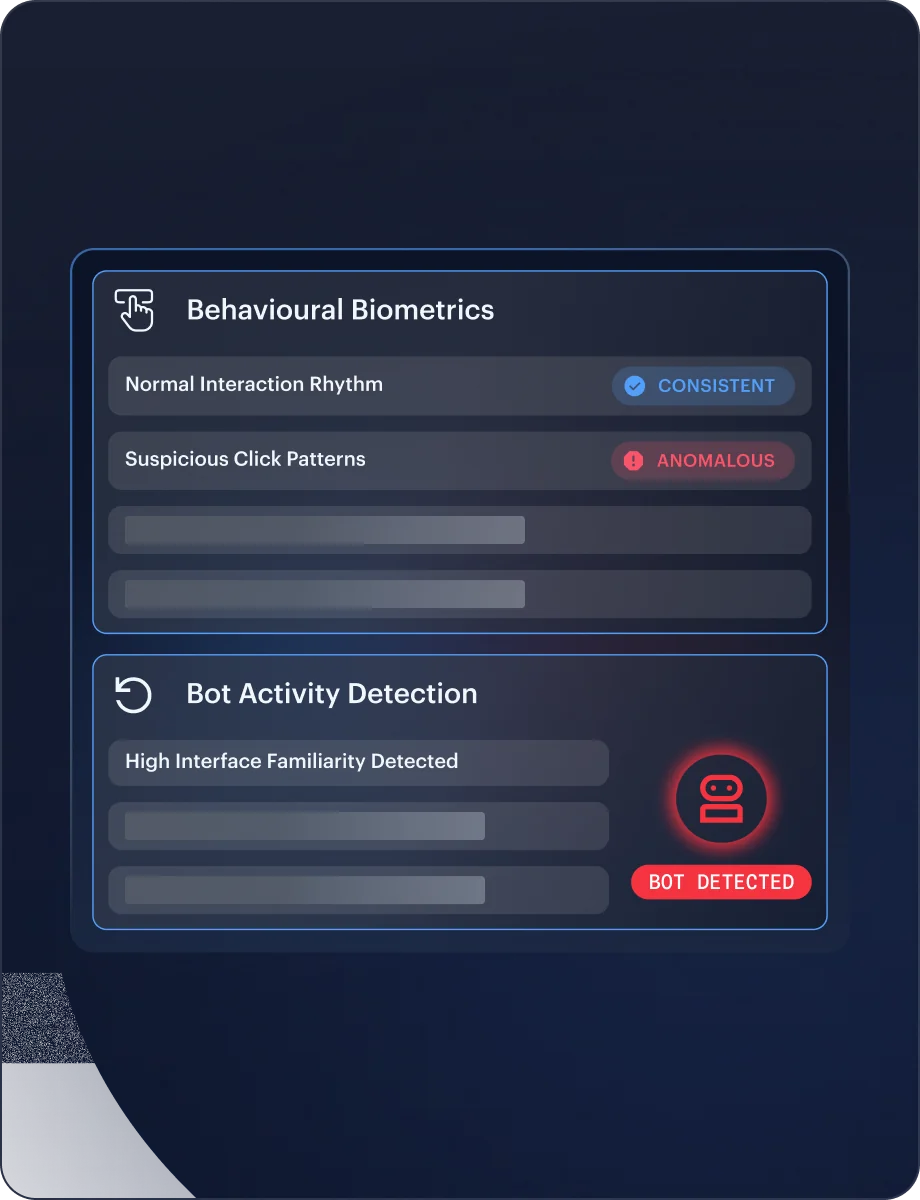
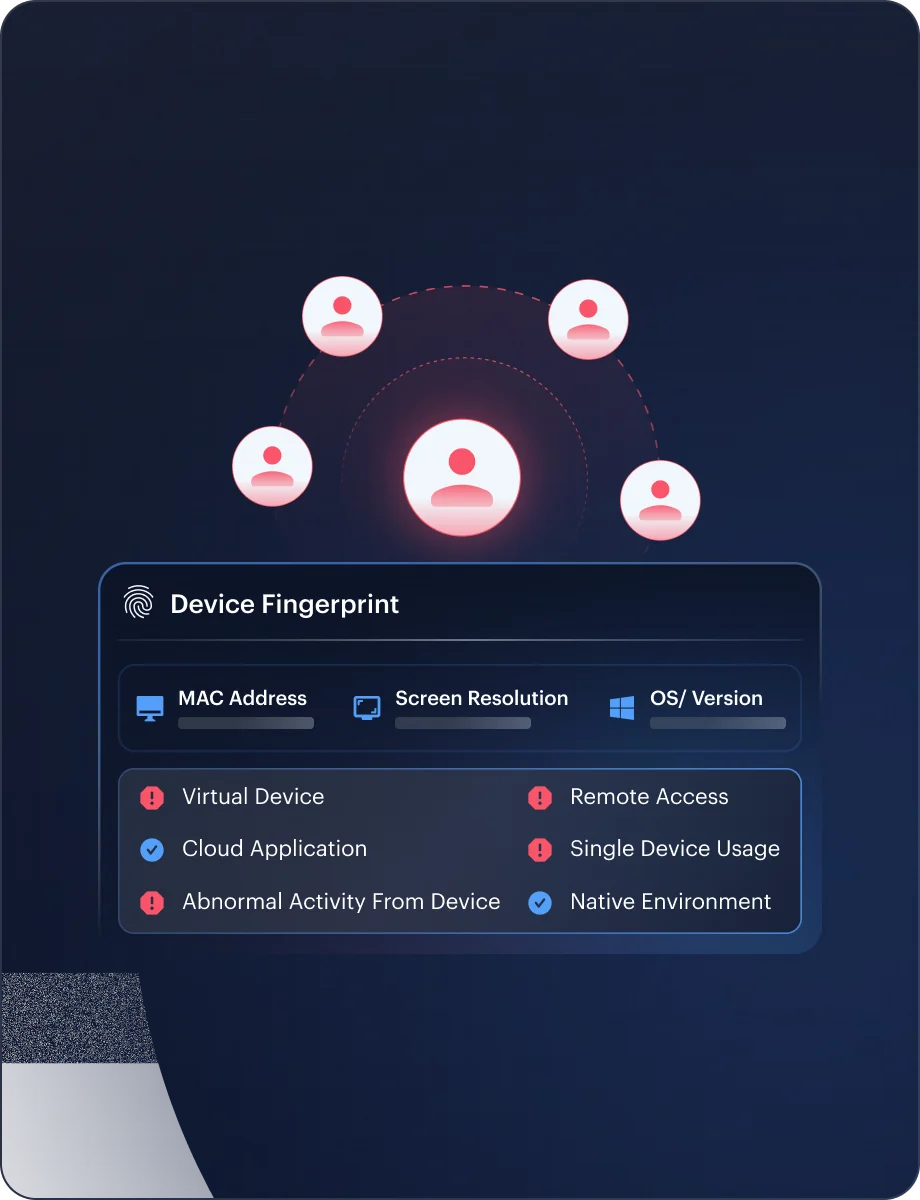
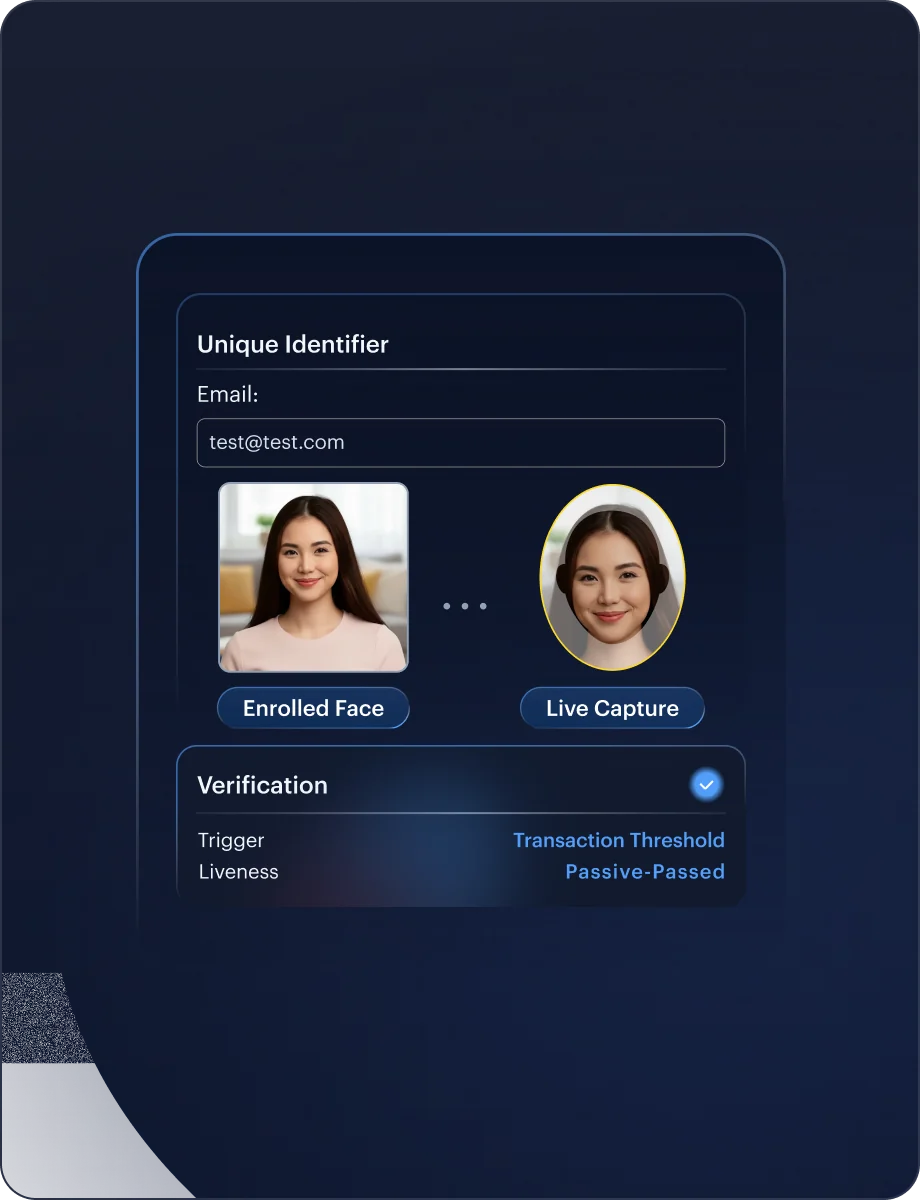
Fraud does not stop at onboarding. Behavioural signals, device intelligence, and biometric step-up verification monitor every session after login, blocking account takeover and bot-driven abuse without disrupting verified users.
-
Monitors keystroke dynamics, mouse movement, and session interaction patterns continuously after login. Detects credential-stuffed sessions, bot-driven automation, remote access tools, and account sharing without adding friction to verified users.
-
Builds a proprietary persistent device profile from hardware signals, browser attributes, and network characteristics. Identifies the same device operating under multiple identities and flags clusters linked to organised fraud rings.
-
Intelligently triggers biometric step-up re-verification at high-risk moments: large transactions, new device registration, and account changes. Compares the live selfie against the original verified identity record, blocking account takeover through stolen credentials.
-
Aggregates identity, device, behavioural, and transaction risk signals into one configurable risk score per session.
-
Configurable multi-factor authentication layered on top of primary identity verification. Applies OTP, TOTP, or biometric challenge at defined risk thresholds without disrupting low-risk user journeys.


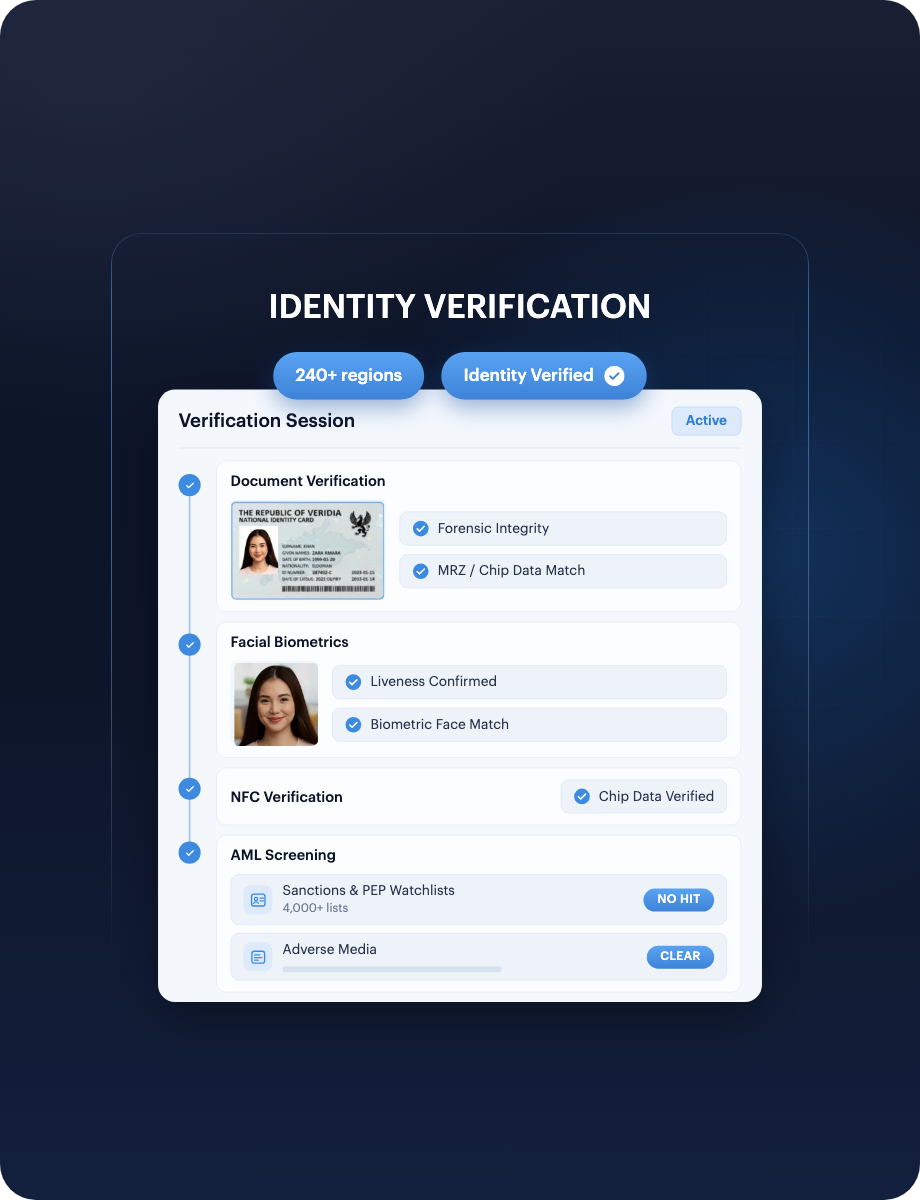
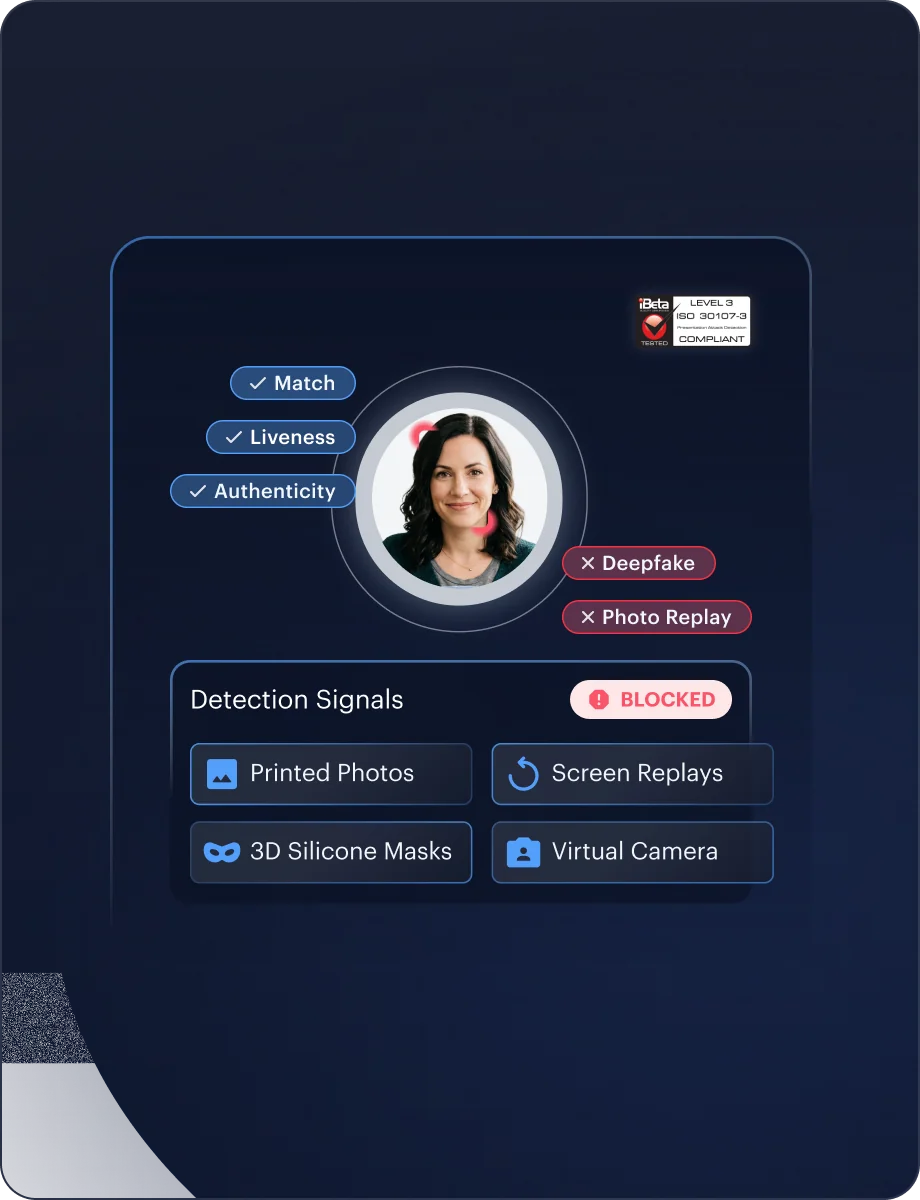
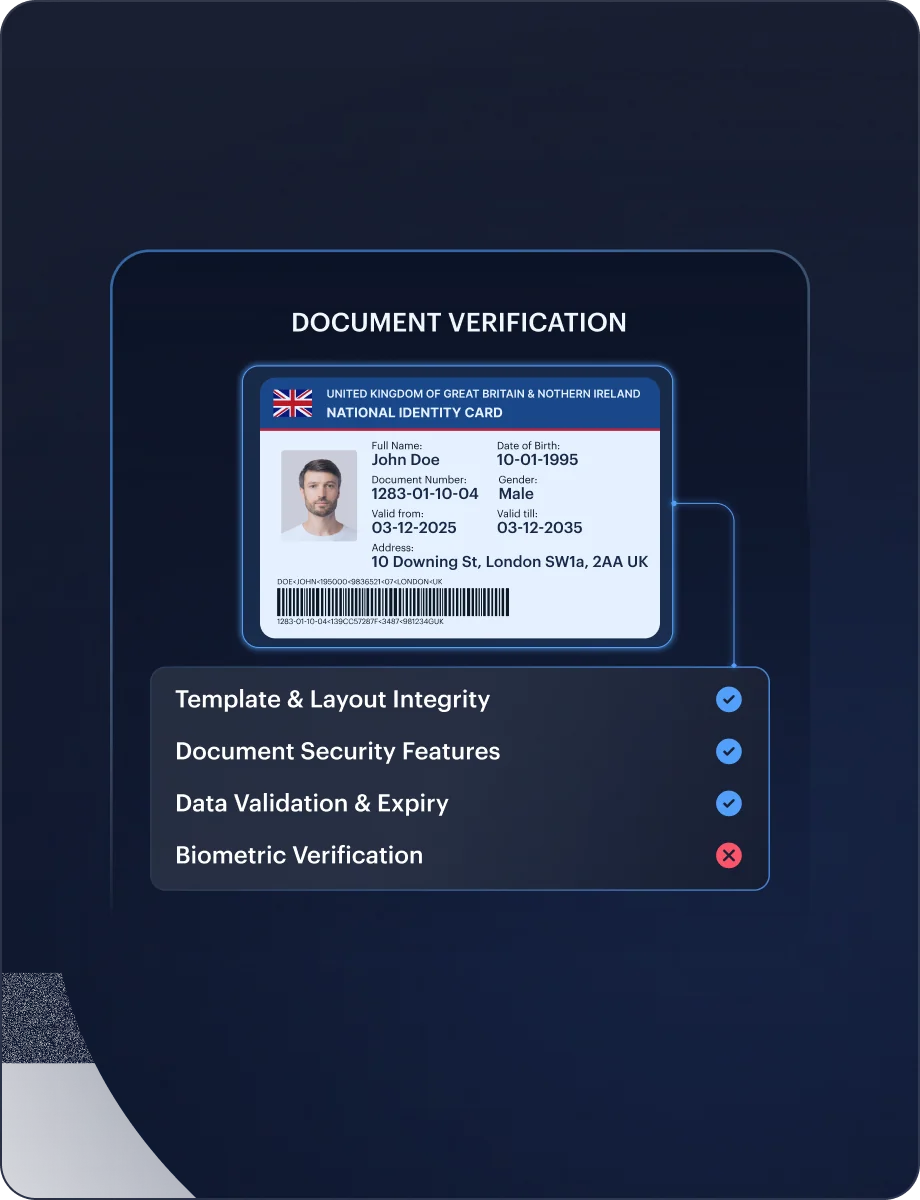
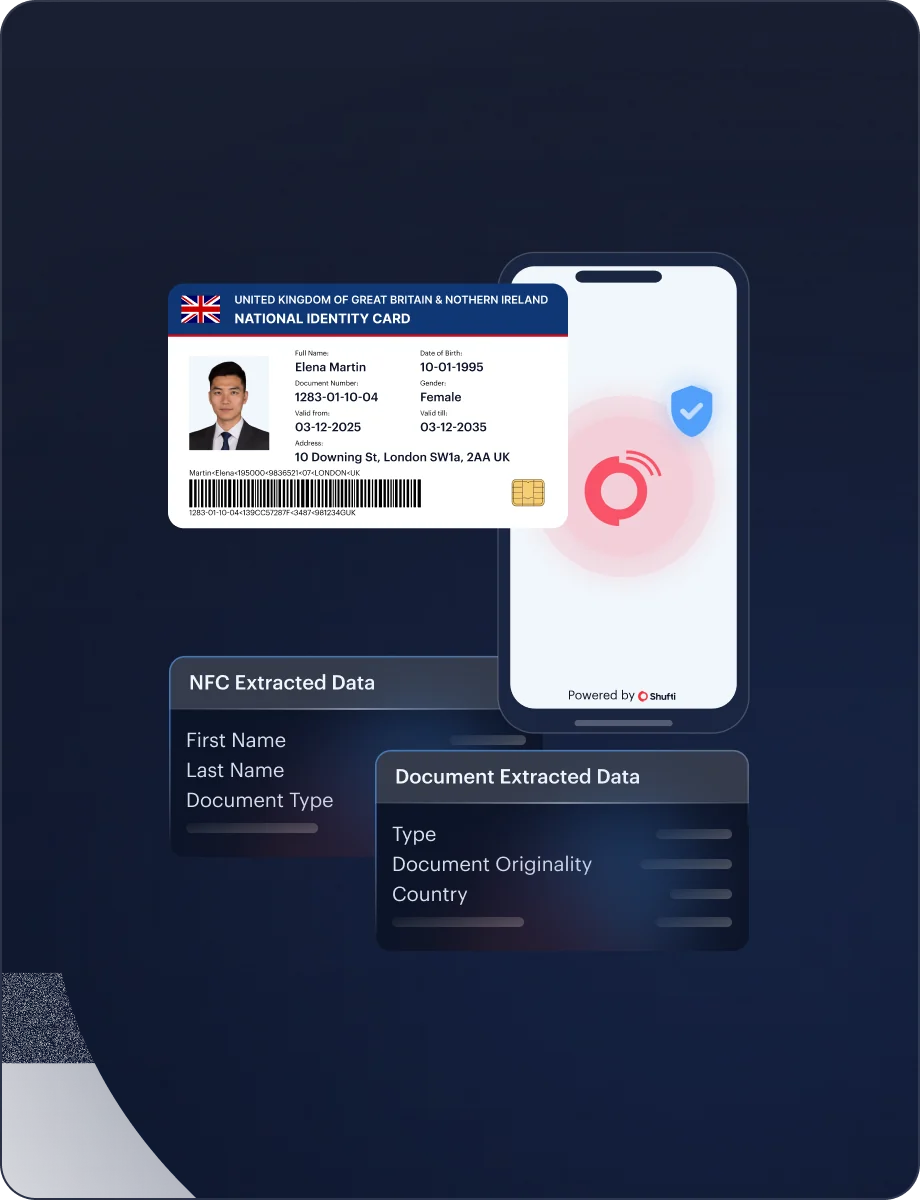
Every synthetic identity stopped before account activation
Synthetic identities, deepfakes, and AI-generated documents enter platforms at onboarding. A 9-layer forensic engine and iBeta PAD Level 3 certified liveness detection stop them before account activation.
-
Confirm real identities in seconds, worldwide.
-
iBeta PAD Level 3 certified passive and active liveness detection defends against printed photos, screen replays, 3D silicone masks, and Gen 5 virtual camera injection attacks. Passive mode analyses a single frame with no user challenge required.
-
iBeta PAD Level 3 certified passive and active liveness detection confirms the person at onboarding matches the submitted identity document. Defends against impersonation and synthetic identity fraud across the compliance evidence trail.
-
Reads the cryptographically signed chip in ICAO-compliant ePassports and national eID cards. Chip-level validation confirms the document is genuine and unmodified, regardless of how convincing the physical or digital forgery appears.


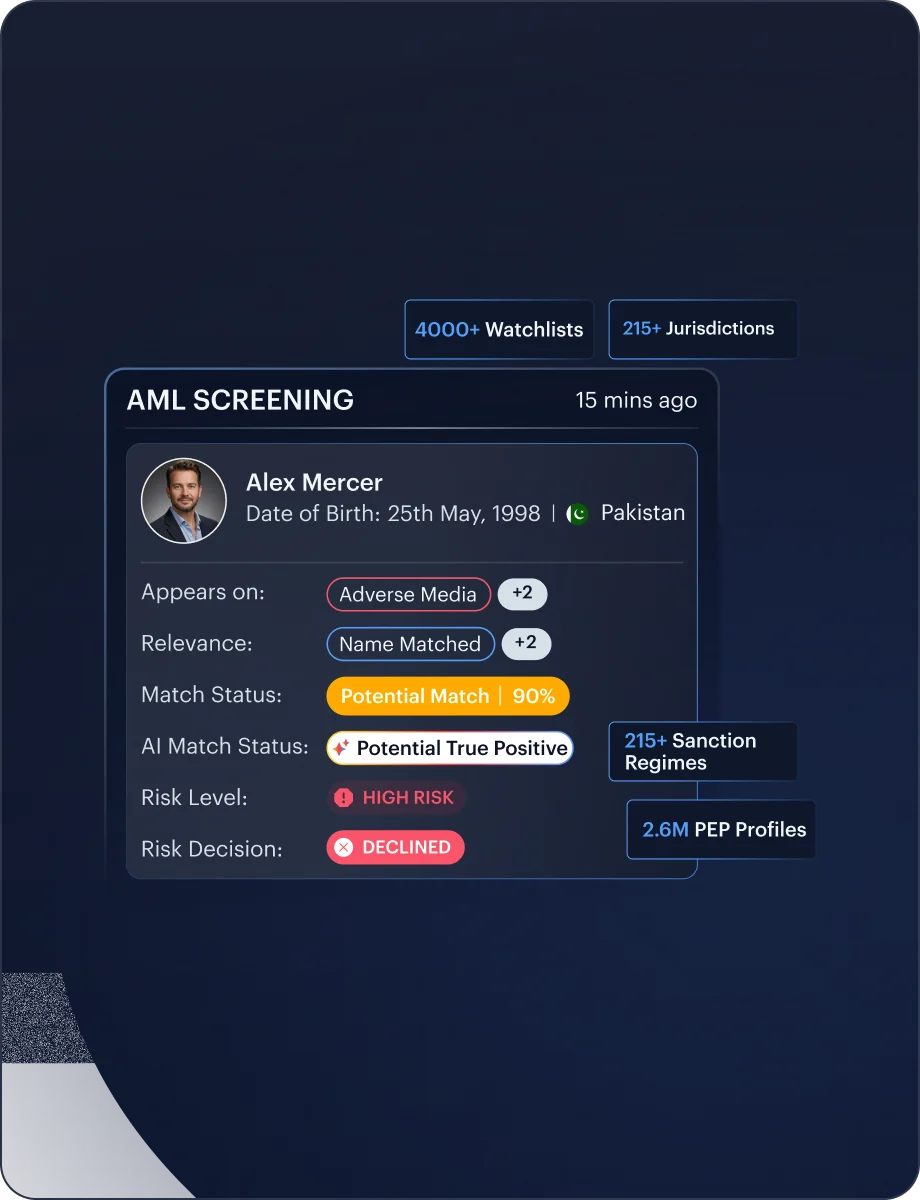
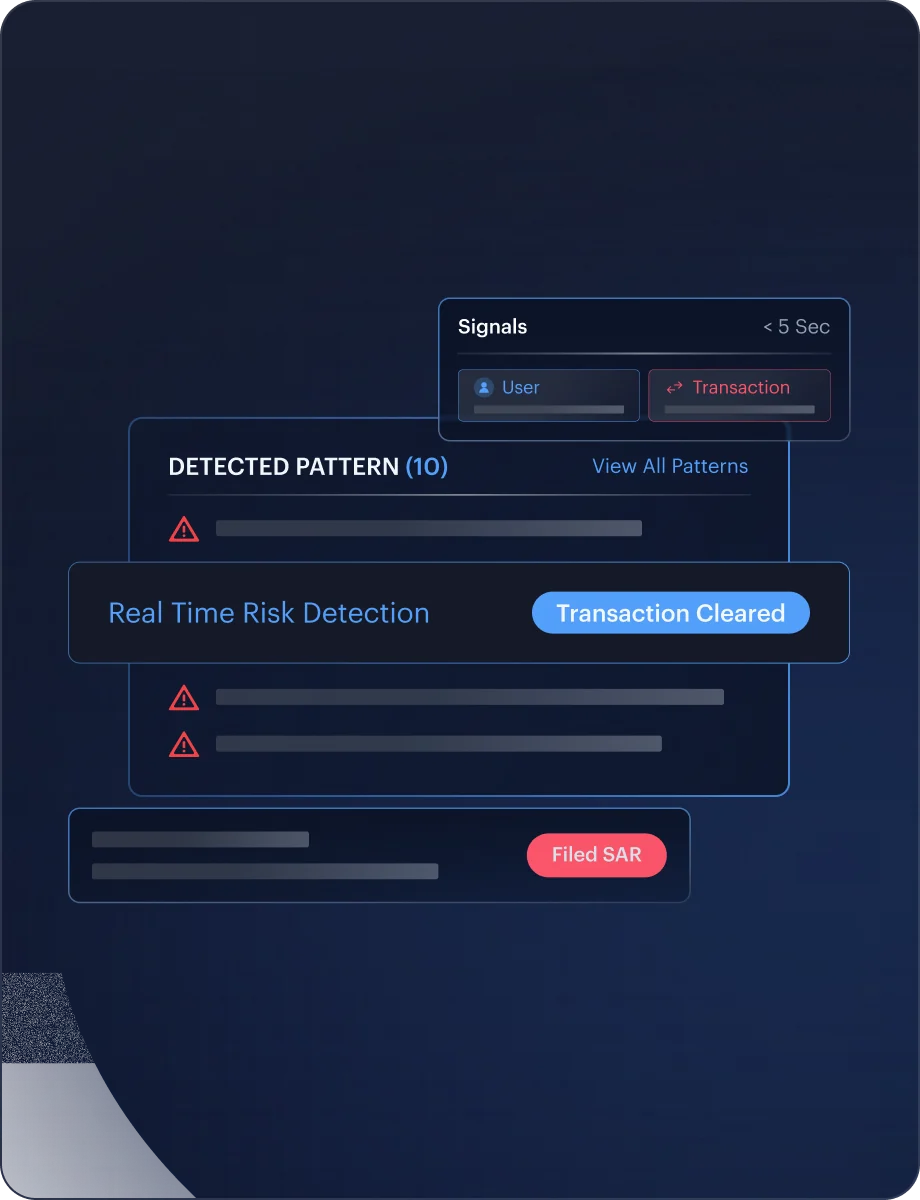
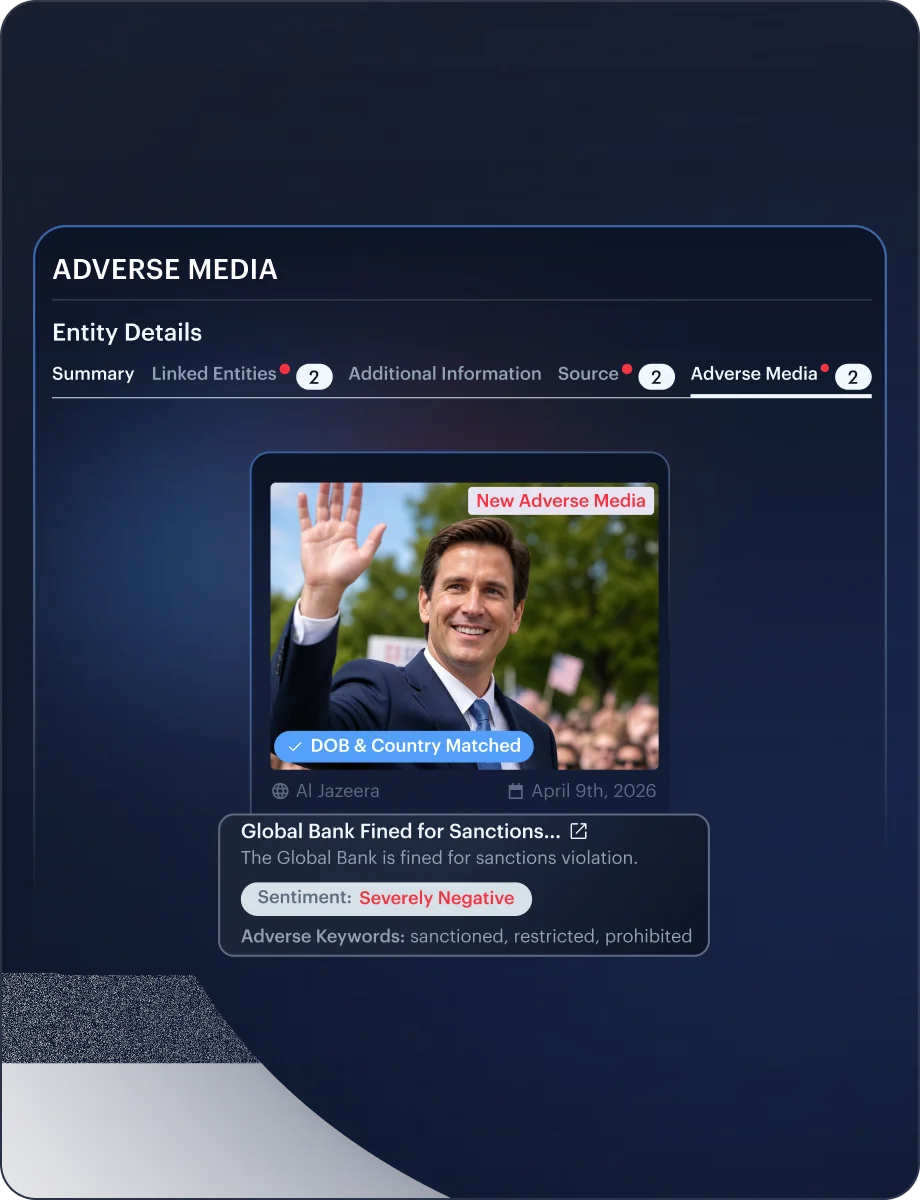
Fraud patterns caught before enforcement ever begins
Fraud patterns often emerge weeks after onboarding. Continuous AML screening, transaction monitoring, and adverse media surveillance detect financial crime risk as it develops, not after enforcement begins.
-
Screens against 4,000+ watchlists covering 215+ sanction regimes and 2.6M PEP profiles across 215+ jurisdictions, refreshed every 15 minutes. Every alert is bound to a biometrically verified identity. The MLRO AI Agent reduces Level 1 triage time by up to 60%.
-
Detects 10 distinct financial crime patterns in real time, including structuring, round-tripping, money mule coordination, chargeback patterns, and velocity anomalies. Each transaction evaluated in under 5 seconds.
-
Screen investor applicants against global news sources for links to fraud, financial crime, or regulatory enforcement action. NLP entity disambiguation filters false positives from common investor names, so your compliance queue stays focused.


Built For Every Role On The Fraud And Compliance Team
Shufti's fraud prevention system covers the full customer lifecycle, giving each role the signals, controls and evidence it needs without separate tooling.
Compliance Officer
Audit-ready evidence on every verification, structured for regulatory inspection across every jurisdiction you operate in.
Product Manager
Configurable verification flows that balance speed against risk tolerance, without rebuilding the integration each time.
Developer
REST API, mobile SDKs, and sandbox access. First verification call within hours of integration start.
Fraud Analyst
Pre-scored evidence and fraud signals on every flagged case, so your team reviews decisions, not raw submissions.
One Fraud Prevention Platform, Every Fraud Type Covered
Deepfake
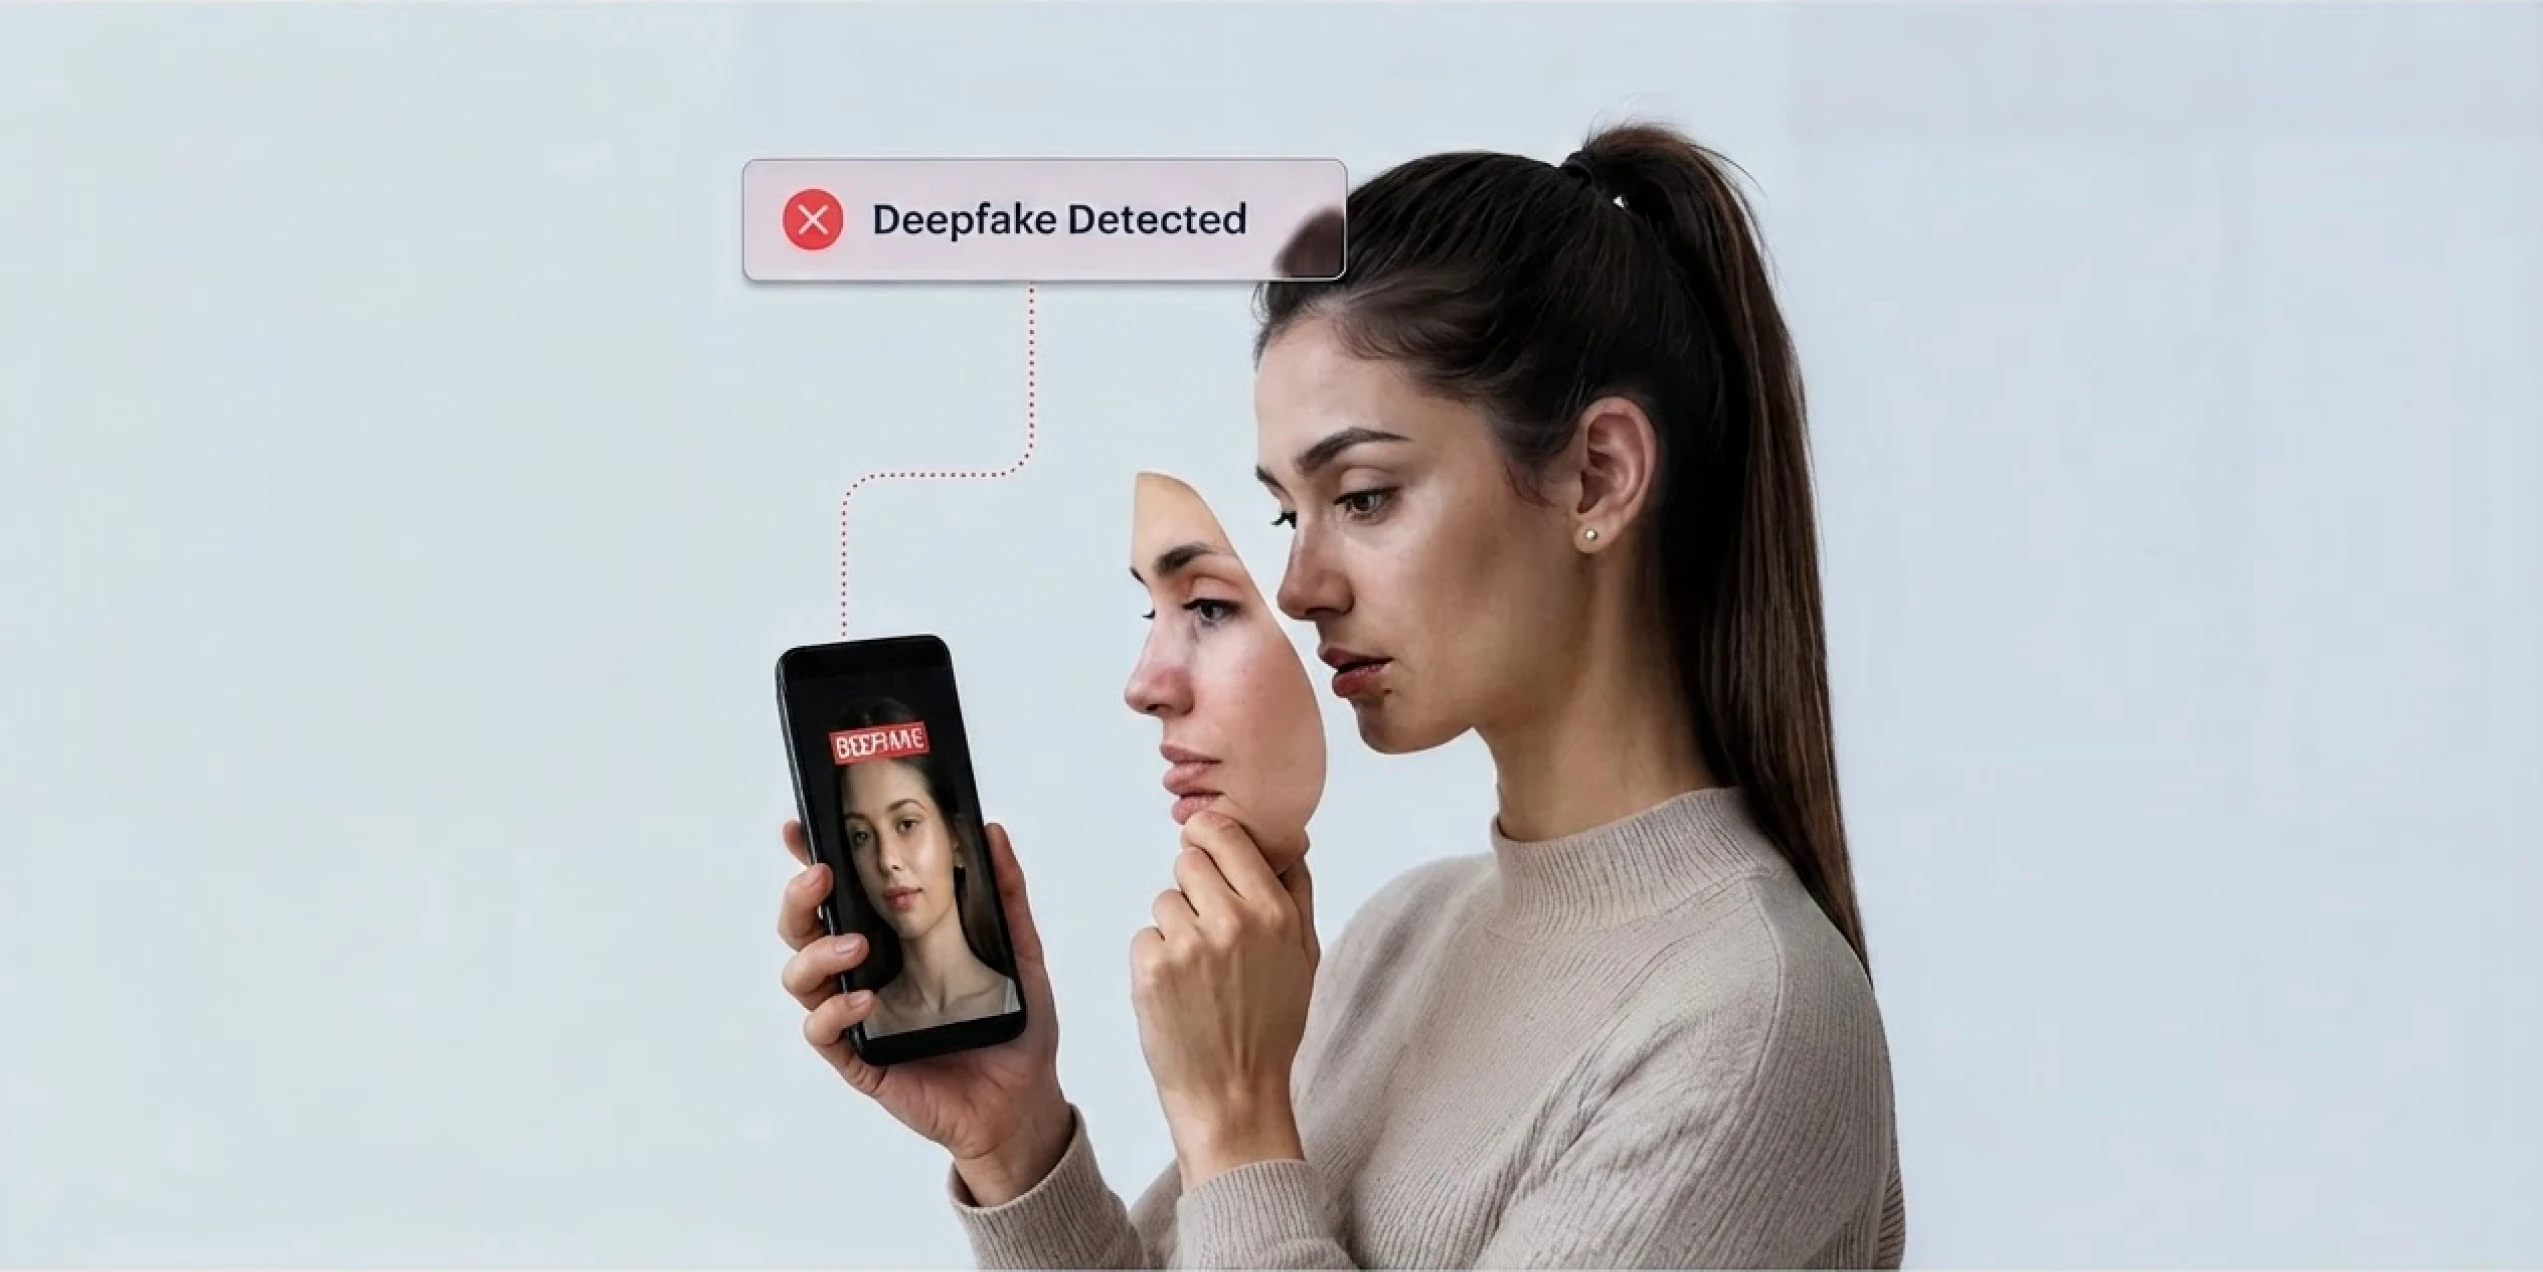
AI-generated faces and synthetically forged documents bypass legacy liveness checks at scale. Shufti's passive liveness & document forensics detects synthetic media before it reaches your onboarding flow.
Identity Fraud
Credential theft, blended synthetic identities, and manipulated documents exploit gaps in manual review. Shufti's layered verification surfaces fraud signals before accounts are created.
Account & Platform Abuse
Duplicate registrations, bot-driven sign-ups, and referral exploits erode platform economics. Shufti links device, identity, and behavioural signals to flag abuse rings at scale.
Transaction & Payment Fraud
False chargeback claims, money mule networks, and sanctions evasion expose your business to financial and regulatory risk. Shufti ties identity verification directly to transaction context.
Validated By Leading Analysts And Certification Bodies
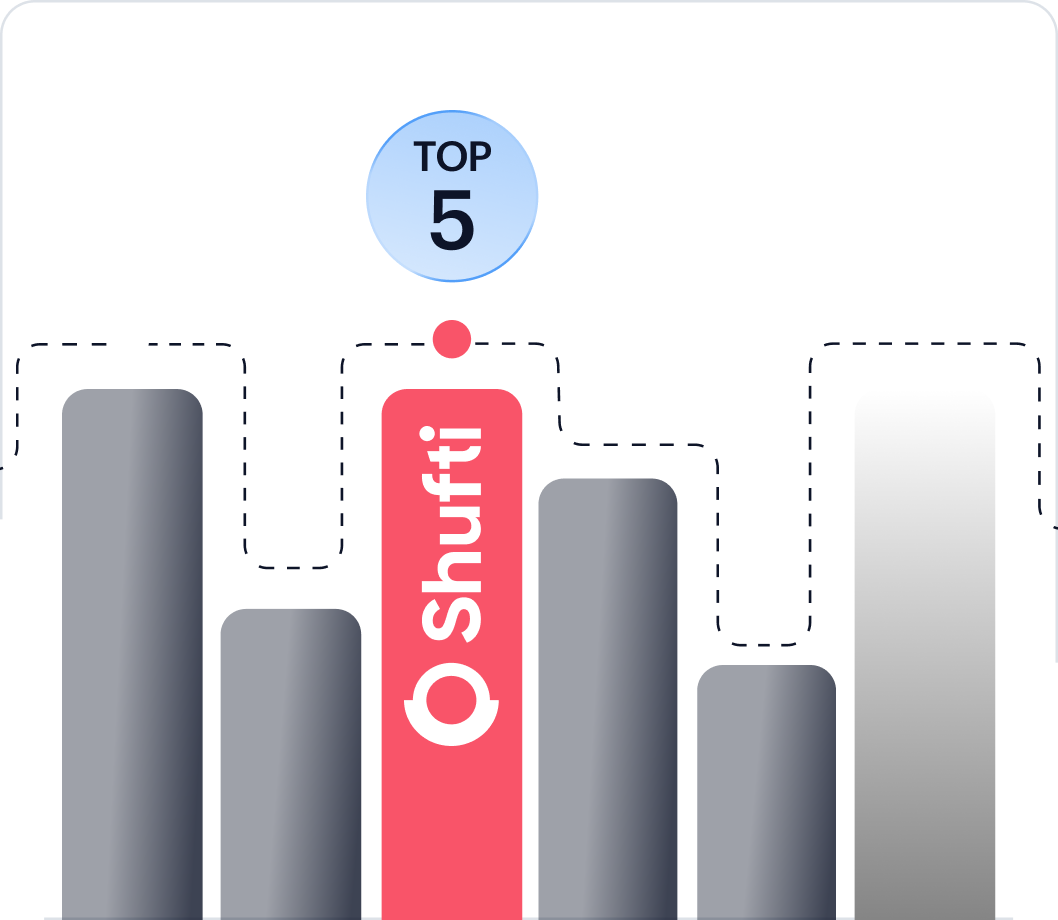
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
Ranked Exceptional for age verification by Liminal Index 2026
View Report
Recognised as a Leader in G2 Summer 2026 reports
View Reviews
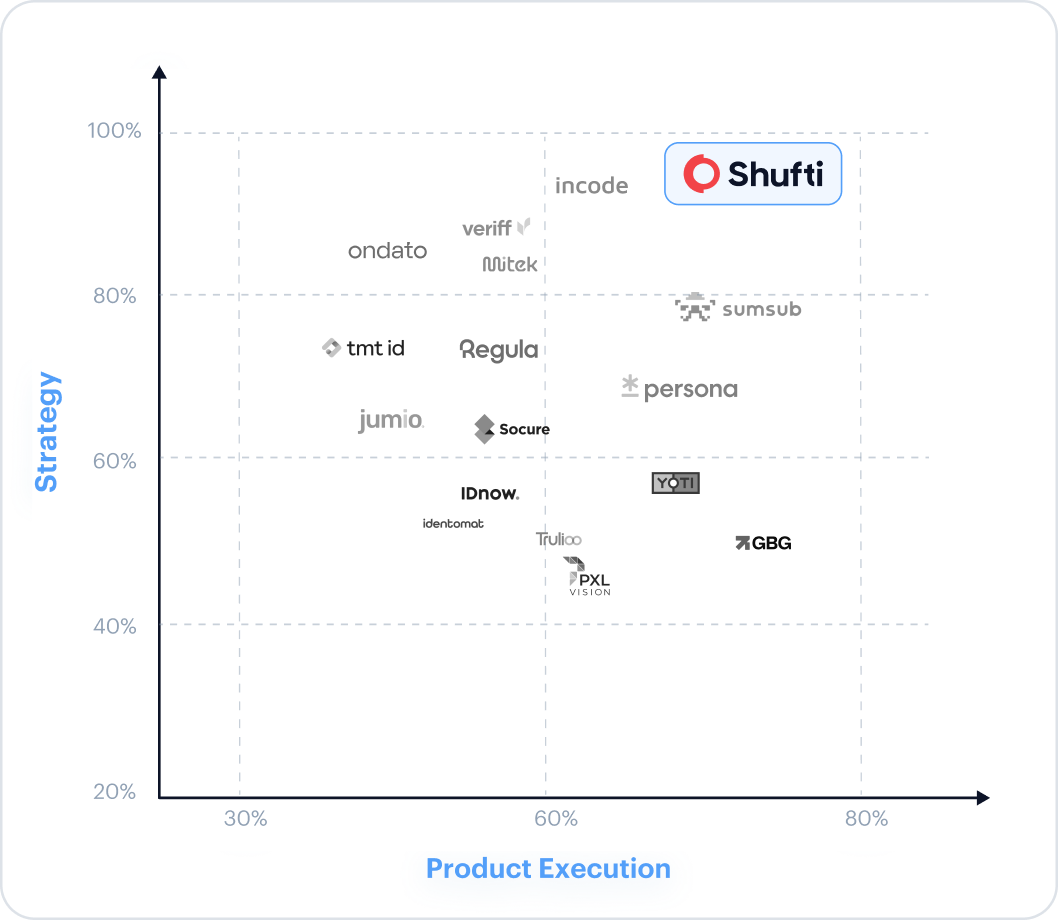
Differentiated by Gartner on document diversity and country coverage
Read more
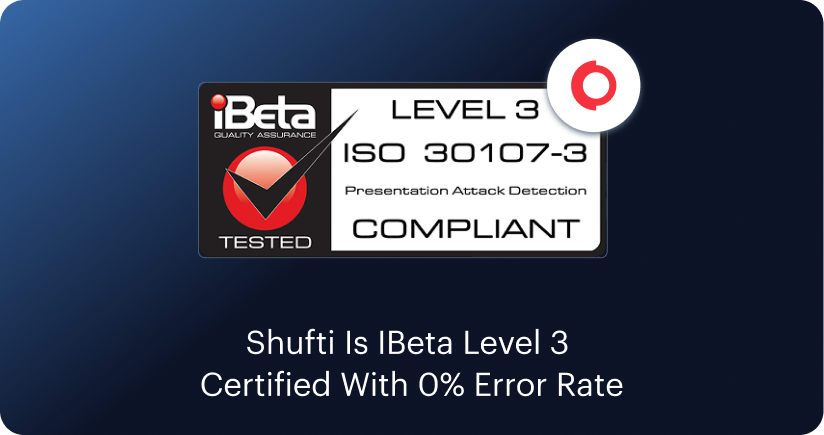
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
Don’t just take our word for it, hear from our customers
The Confidence Our Clients Share
The future of digital identity is defined by trust, interoperability, and regulatory alignment, so our partnership with Shufti reinforces DevCode Identity’s commitment to supporting our global customers with the most secure, best-in-class, compliant identity verification solutions available today.
Combining our Conversion Driven Compliance Orchestration Platform with Shufti’s global KYC and IDV capabilities allows our customers not only to navigate complex regulatory demands but also to maintain a seamless customer onboarding experience with the highest achievable conversion rates.
We’re proud to continue our partnership with Shufti as we expand into new jurisdictions.
Shufti’s verification technology not only strengthens our compliance framework but also ensures our players enjoy a smooth, secure onboarding experience.
We aim to offer our clients and their traders the very best tools with which to do their jobs, we’re excited to be able to work with Shufti.
They’re a leading company, and we’re looking forward to offering their solutions to our clients through our CRM.
The relationship with Shufti was born out of frustration with an existing provider, so we started our discussion with Shufti.
The response time was excellent, from the start of speaking to sales to getting up and running with the demo.
BUILT FOR YOUR INDUSTRY
Digital Fraud Prevention Solutions for High-Risk Industries
New Account Fraud, Blocked At Entry
Fraudsters open accounts with synthetic or stolen identities to access credit facilities and payment rails. Shufti verifies identity at onboarding and flags synthetic profiles before account activation.
Frequently Asked Questions
What happens when a customer fails a fraud check?
Failed checks route to manual review with the full signal trail attached, rather than a hard decline. Analysts see the document, device, and behavioural evidence on one screen.
What is the difference between fraud detection and fraud prevention?
Fraud detection finds fraud after it has happened. Fraud prevention blocks it at the decision point: onboarding, login, step-up, or transaction. Shufti runs both against one identity record.
What fraud prevention services does Shufti provide?
Shufti provides identity and document verification, facial biometrics, device fingerprinting, behavioural biometrics, AML screening, transaction monitoring, and risk scoring. Businesses can combine the checks that match their risk, customer journey, and deployment requirements.
How does Shufti detect synthetic identity fraud?
Every government-issued document passes a 9-layer forensic engine: MRZ extraction, template classification, font consistency forensics, microprint analysis, holographic detection, deepfake intelligence, and metadata forensics. Template-specific models are trained on verified genuine specimens. In independent testing, Shufti detected 8 of 8 forgeries that legacy systems passed.
How does Shufti detect money mule activity and organised fraud networks?
Transaction Trust Monitoring detects structuring, round-tripping, mule coordination patterns, and velocity anomalies in real time at under 5 seconds per transaction. Device Fingerprinting identifies shared infrastructure across accounts. Behavioural Biometrics flags coordinated bot-driven session patterns. AML Screening screens every user against 4,000+ watchlists refreshed every 15 minutes.
Do fraud signals captured at onboarding carry forward through the lifecycle?
Every session generates one unified record: document images, AI confidence scores, face match result, liveness outcome, device fingerprint, and AML screening result. This record persists and is available to transaction monitoring and ongoing AML screening. When a fraud pattern emerges post-onboarding, analysts see the full identity context, not an isolated alert.
Does Shufti support on-premise deployment for fraud detection?
On-premise and private cloud deployment is available for biometric liveness detection, document verification, and face matching. AML screening operates through regional cloud processing (EU, UK, US, APAC, MENA) with configurable data retention and DPA coverage.
How long does API integration take?
API integration typically takes 2 to 5 business days. SDK integration takes 1 to 3 business days. Sandbox access is provisioned within 24 hours. These timelines reflect actual enterprise deployment experience, not estimates. A dedicated integration support team is available throughout the process.
See How Shufti Fits Your Fraud Stack
AI-generated documents, advanced deepfakes, synthetic identities, and organised fraud rings are outpacing legacy verification systems. Evaluate your detection coverage across identity, device, behavioural, and transaction signals through one integration.
Your Go-To for KYC/AML & Fraud
Resources
21 August, 2026
Identity Fraud Report 2026
Identity fraud hit 22.49% of crypto verifications in H1 2026. Shufti's report breaks down AI document fraud and linked fraud networks across 11 named sectors of risk.
Report