

Sift vs Shufti
A Sift alternative
for fraud controls and AML monitoring
Bring fraud rules, anti-money laundering (AML) screening and transaction monitoring into one review workflow. Shufti helps analysts assess the available customer evidence behind an alert and prepare reports for your firm's review and submission.
DETAILED CAPABILITY COMPARISON
Sift vs Shufti on fraud controls, native AML and
transaction monitoring
Sift is built for fraud prevention. Payment Protection scores payments in real time and Account Defense handles account takeover. Sift does not market native AML screening, AML transaction monitoring or SAR and STR preparation. Teams that need AML screening and regulatory reporting may need separate AML functionality alongside Sift. How customer evidence moves between systems depends on the integration. Shufti closes that gap. Screening against 4,000+ watchlists, Transaction Trust Monitoring and FinCEN and goAML report packs run on one platform, so the analyst reviewing a transaction sees the KYC result, screening outcome and device signals behind it.
Every transaction is scored with the customer's KYC result, screening outcome and device signals attached, across 1,600+ data points.
Payment Protection scores stolen-card and card-testing risk in real time.
Verified identity, KYC status, screening outcome, beneficiary and device data in one decision trail.
Device, behavioural, velocity and network signals for fraud decisions.
Matched rules, supporting signals and score explanations on every alert.
Score Explainability on fraud decisions.
Account-takeover behaviour, device mismatch and velocity spikes flagged in monitoring. Session-level login controls are not part of Transaction Trust Monitoring.
Account Defense, with post-login monitoring and session-level controls.
Yes. 4,000+ watchlists, 215+ sanctions regimes, PEPs and associates, adverse media in 80+ languages.
Not identified in the Sift product documentation reviewed on 29 September 2026. Confirm AML coverage and integration options with Sift.
Yes. 800,000+ business profiles, with directors, officers and UBOs screened.
Not advertised.
Yes. Lists refreshed every 15 minutes, alerts by API, webhook or email.
Not advertised.
Configurable weighted scoring with scored due-diligence forms.
Not advertised as an AML risk model.
Customer due diligence, screening, transaction monitoring and audit evidence on one record, with rescreening scheduled by risk tier to meet the one-year and five-year refresh limits.
Fraud controls only. No CDD, AML screening or transaction-monitoring evidence advertised, so AMLR evidence sits with your separate AML tool.
Batch AML rescreening, repeat identity verification and ownership checks on existing customers, each written to the audit trail as remediation evidence.
Not advertised. Sift keeps fraud decision history, not customer-file evidence, so remediation runs in the separate AML or KYC tool.
500+ pre-built fraud typologies. 15+ velocity checks from one minute to 180 days.
Configurable fraud workflows and thresholds. No AML typology library advertised.
Batch review workflows and 90-day behavioural baselining alongside real-time scoring.
Historical network visualisation for fraud investigations. No AML batch review advertised.
Backtesting on 90 days of history with projected alert volume and precision. Full version history.
Policy and threshold testing against historical traffic.
One alert queue with L1, L2 and MLRO escalation, four-eyes review and SLA tracking.
Fraud case investigation and review queues. No AML case workflow advertised.
Action history, closure rationale and a five-year immutable audit trail.
Fraud case history. No AML audit workflow advertised.
SAR, STR and CTR packs in FinCEN BSA XML 2.0 and goAML, authorised by your MLRO and filed by your firm.
Not advertised.
REST API and SDKs with sandbox access.
APIs, JavaScript snippet and SDKs.
Cloud, on-premises, hybrid and offsite, with data residency in the EU, UK, US, APAC and MENA.
SaaS.
See the customer context behind a transaction decision
Bring a scenario, such as a mule-account pattern or a sanctions hit on a beneficiary. We’ll walk through how Shufti Transaction Trust Monitoring uses the customer and screening data you provide, from the transaction activity and rule that triggered an alert to the case your analyst reviews.
Book A Fraud And AML Demo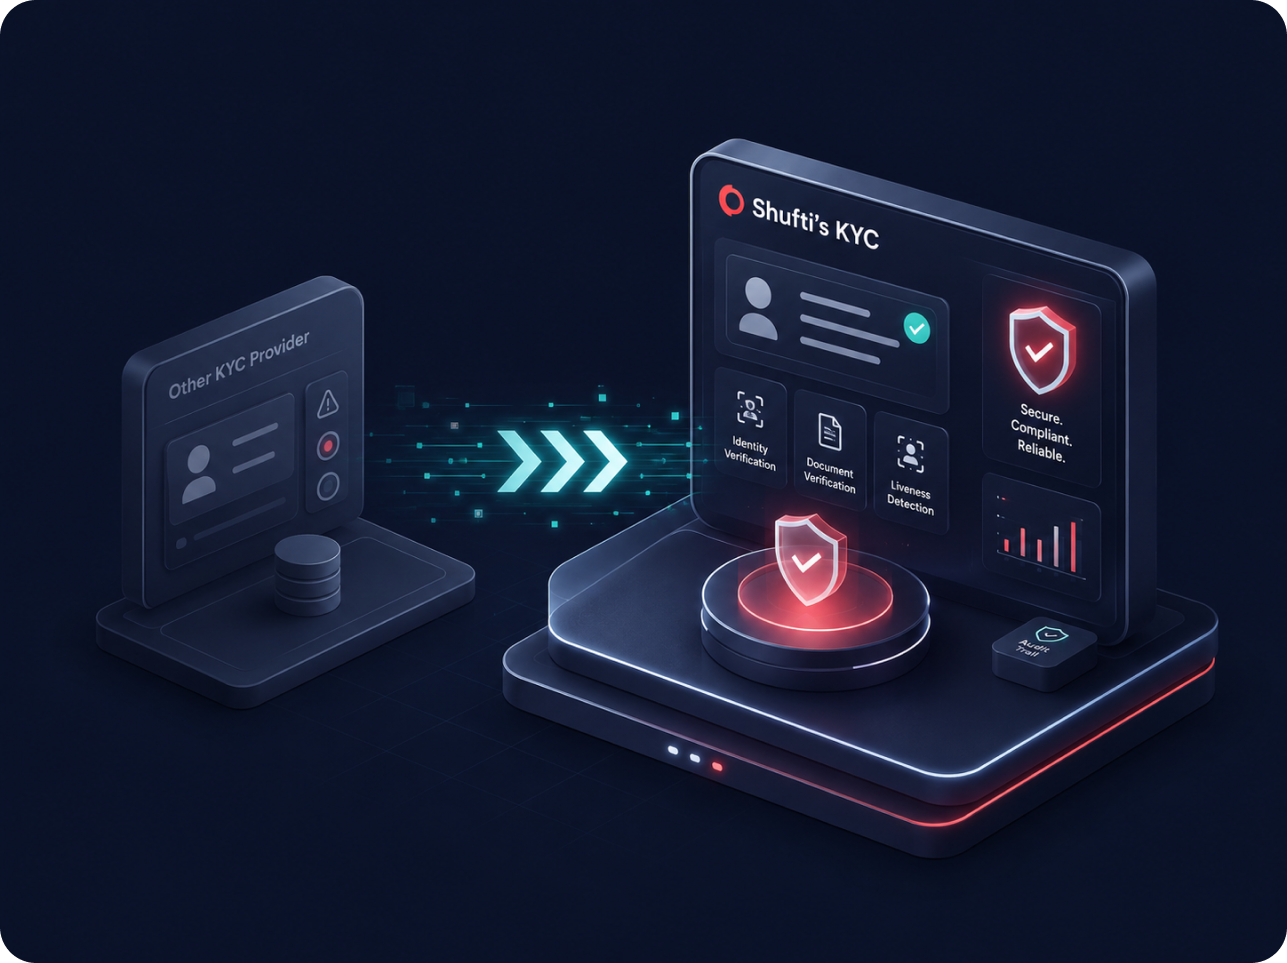
TWO-PANEL ARCHITECTURE COMPARISON
One platform for identity, screening and transaction risk
Shufti runs screening and transaction analysis as one service. The customer, beneficiary and device data you send with a transaction is already linked to the KYC and screening record behind it, so nothing has to be stitched together later.
Fraud Control on One Case File
How a transaction moves from identity check to regulatory report with Shufti, and where the seam sits with Sift plus a separate AML vendor.
sift
Identity and Screening
Native
KYC result plus 4,000+ watchlists on the customer record
Separate AML Vendor
Screening is not advertised by Sift
Transaction Risk
Native
1,600+ data points scored in under 500 ms
Screening is not advertised by Sift
Payment Protection, real-time fraud scoring on device and behavioural signals
Case and Review
Native
One queue, L1 to L2 to MLRO, four-eyes review
Split
Fraud cases in Sift, AML cases in the other vendor's queue
Regulatory Report
Native
FinCEN BSA XML 2.0 and goAML packs, filed by your firm
Separate AML Vendor
SAR and STR preparation is not advertised by Sift
5 years
immutable audit trail on every case
1
integration, case history and audit trail
500+
Pre built Rule Library
FOUR CAPABILITY CARDS
Turn your risk policy into rules your analysts can defend
Write the detection logic, test it on your own history and keep the evidence behind every decision.
Write the Rule
Describe a scenario in plain English and get reviewable rule logic.
Backtest on 90 Days
See projected alert volume and precision before the rule goes live.
See Why It Fired
Every alert shows matched rules, score explanation and customer context.
Defend the Decision
L1, L2 and MLRO routing, four-eyes sign-off, five-year audit trail.
90 days
of history behind every backtest
1,600+
data points scored per transaction
500 ms
or less to score a transaction
500+
pre built rules library
DON’T JUST TAKE OUR WORD FOR IT, HEAR FROM OUR CUSTOMERS
The Confidence
Our Clients Share
Score
“We’re proud to have one of the lowest fraud rates of any gaming marketplace globally and we are always searching for new solutions to better improve the safety of our customers. Shufti provided the most effective KYC solution, allowing us to streamline our customer’s experience on the Kinguin Marketplace, ensuring purchases are as secure and convenient as possible.”
Onboarding
Rate
“We take our clients’ privacy very seriously, and we want them to know that we are constantly looking for new innovative solutions to ensure a safe banking experience. This is why we are proud of our recent partnership with Shufti, the AI-powered identity verification solutions provider, which will provide state-of-the-art identity verification. This collaboration falls under our strategy to provide a seamless and secure digital experience for our valued customers who prefer to use our online platform. We aim to improve our online banking and create an even safer service through the “Safwa Mobile” application.”
“As a relatively new brand, we need to absolutely ensure that initial brand interactions between Mintus and our customers are slick and smooth. To achieve this we need technology that is highly customisable to our needs and able to accurately verify individuals from across the globe. Not only does Shufti deliver this, it also does it quickly and easily – something our customers truly appreciate. We estimate that £150m of painting investments will be verified by Shufti this year.”
Score
“When potential customers informed us that our lengthy verification processes were hindering their due diligence verification, we knew we needed to make changes. Shufti had a reputation as a leading authentication expert that would be able to streamline our processes, while enhancing our risk detection. Through partnering with the team at Shufti we’ve been able to grow our customer numbers by 20%. At the same time we’re able to streamline their experience while on our platform and stop under-aged users and potentially fraudulent users from accessing our services. It’s a win win.”
“Given that we’re working with such vulnerable people, knowing exactly who is volunteering with us is vital, particularly as we need to have a large team on the ground. We needed a secure system that was not only highly accurate, but also time-saving. Shufti eliminated the need for our staff to implement extensive, manual ID verification processes and instead enabled us to focus on our two main projects in Ukraine – to deliver support to as many people as we can, and to grow the capacity of the charity so we can help even more people.”
INDEPENDENT VALIDATION
Shufti's Recognition Across Independent Evaluations
Trusted By 2000+ Businesses Across 240+ Countries And Territories
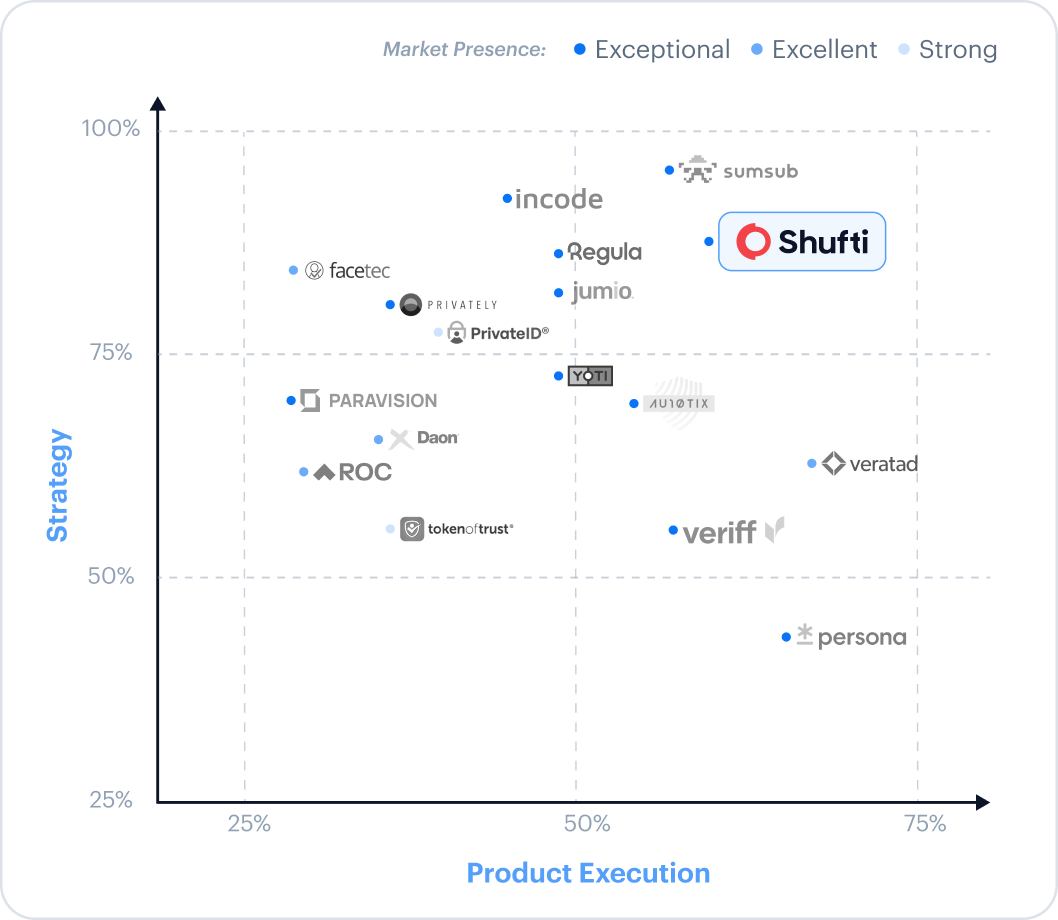
Ranked Exceptional in the Liminal Index 2026 for age estimation
View Report
Differentiated by Gartner on document diversity and country coverage
Read more
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
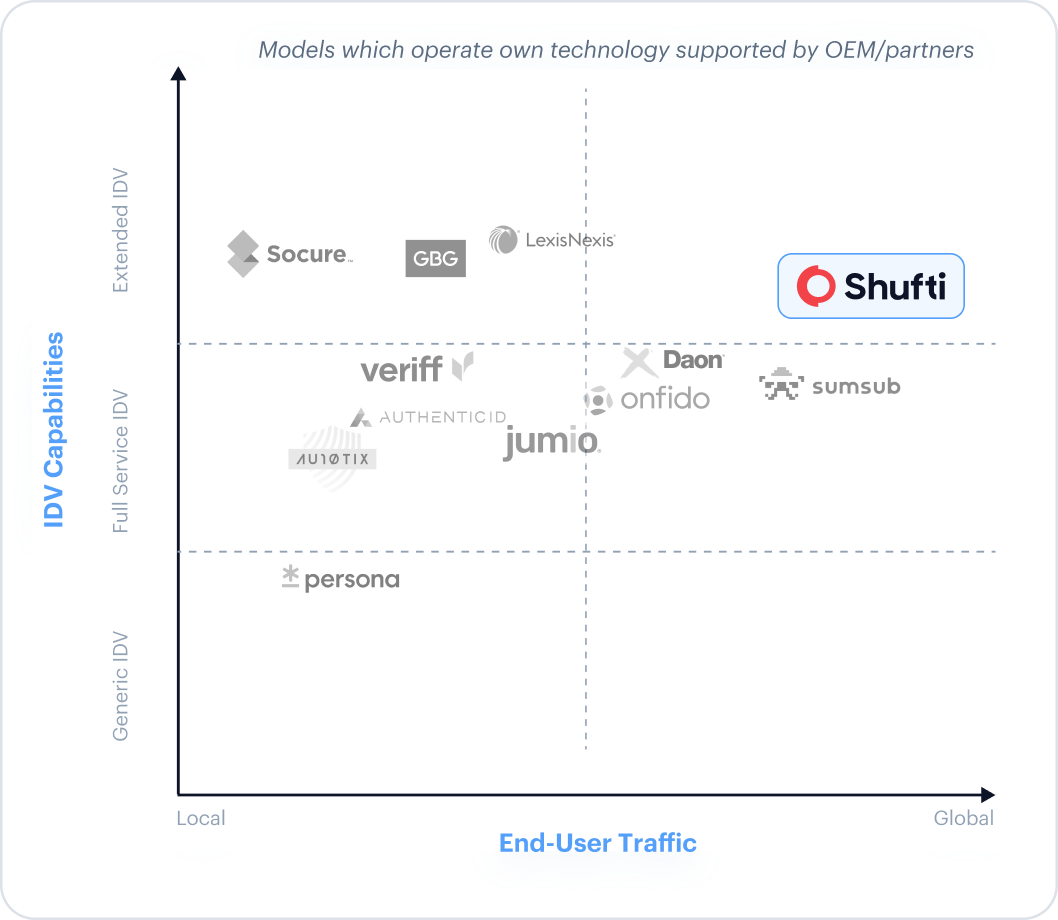
Broadest global reach in the 2025 KuppingerCole Extended IDV report
Download Report
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
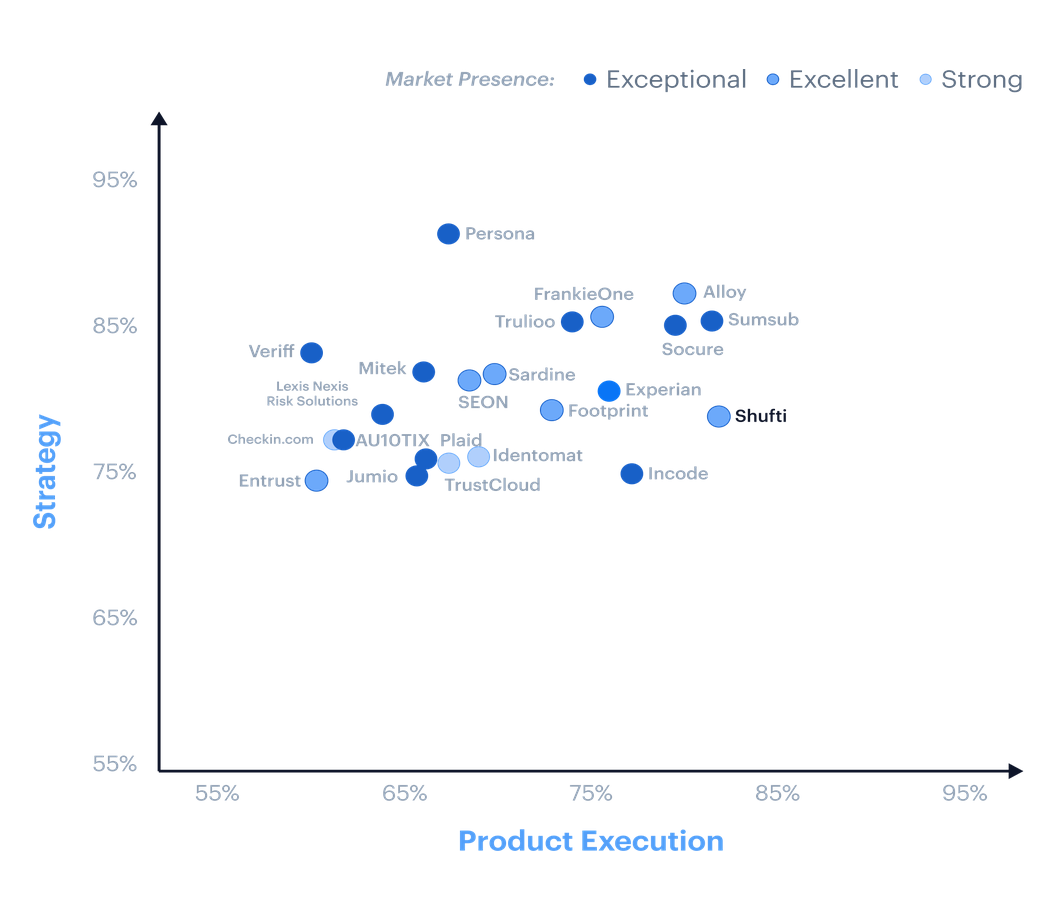
Top Vendor for Product Execution in the Liminal Index for KYC 2026
View Report
Ranked Exceptional for age verification by Liminal Index 2026
View Report
Recognised as a Leader in G2 Fall 2026 reports
Read More
THREE-STEP MIGRATION
Plan the switch around the controls you already run
Decide what moves to Shufti, how you will prove it works and what a good rollout looks like before you touch live traffic.
- 1
Map the data and the workflow
List the transaction fields, customer context, decisions, rules and case records you rely on today. Map each one to what your Shufti integration will send.
- 2
Test fraud and AML side by side
Run Shufti on the same historical transactions and compare approvals, alert volume and review workload. Test the AML scenarios and report outputs your regulator expects.
- 3
Agree the rollout
Set responsibilities, acceptance criteria, support and rollback before cutover. Scope a full replacement or an AML addition alongside Sift.
QUESTIONS YOU MAY HAVE
Answers for teams comparing Shufti and Sift
Direct answers to the questions that come up in evaluations, including the ones where Sift is the better fit.
For Fraud Control, yes. Payment Protection scores payments in real time, and Sift's fintech page describes stopping unauthorised deposits, transfers and withdrawals. As of September 2026, Sift does not advertise AML transaction monitoring, typology rules such as structuring or smurfing, or SAR and STR preparation, so those need a separate tool.
Shufti scores each transaction against 1,600+ data points, including the customer's verified identity, KYC status, screening outcome, beneficiary details and device signals, then compares it with a 90-day behavioural baseline. The context available depends on the data you send with each transaction.
Shufti is the stronger fit when you need native AML screening and transaction monitoring alongside fraud controls. If Sift already handles your fraud prevention and account-takeover cases well, keep it and add Shufti for AML. That pairing is a scoped integration, not an off-the-shelf connector.
Shufti prepares the report pack in the regulator's native format, including FinCEN BSA XML 2.0 for the US and goAML for financial intelligence units across Europe, the Middle East, Africa and Asia Pacific. Your MLRO reviews, edits and authorises it, and your firm submits it.
Yes. Shufti runs the same feature set across cloud, on-premises, hybrid and offsite deployment, with data residency in the EU, UK, US, APAC and MENA. Transaction-monitoring scope, backup locations and subprocessors are agreed during contracting.
Neither vendor publishes transaction-monitoring pricing, so compare quotes on the same volumes, AML services and support. Shufti's published pricing page lists identity verification at $1.50 per check on the Essentials plan and places transaction monitoring on the Enterprise plan, which is priced on request.
It depends on how much you move. A typical plan maps your transaction and customer fields, runs Shufti in parallel on historical data, then cuts over in stages. You get a timeline once scoping is done.
Put a Verified Identity
Behind Every
Transaction Score
The next alert your team opens should already carry the person, the screening result, the device and the transaction on one governed risk profile with one composite score. Start in a sandbox provisioned within 24 hours, run your mapped rules against your own transaction history, and compare the evidence, analyst workload and reporting trail before you decide.