
The FRAML Convergence: Unifying Fraud and AML Monitoring
 Back
 A CPD Standards Office-Accredited Provider
The FRAML
Convergence

What the session covers
Fraud and AML were built as two functions with two clocks. Fraud stops a loss in seconds. AML reports to the state and works retrospectively.
Instant settlement closed the gap between them. The account that received a scam payment is a fraud case and a laundering case at the same moment, on the same customer record, in two systems that do not talk to each other.
Shufti and AML Certification Centre host a 60-minute practitioner panel on where the signal is lost between onboarding, authentication and ongoing monitoring, what the regulatory floor already requires, and how firms are bringing fraud and AML together across systems and teams.
Four Self-Assessment Questions
The hour closes on four questions you can put to your own fraud and AML teams the next morning.
How do you link a transaction back to the customer you verified at onboarding, and where does that link break?
Do your fraud and AML teams work from one typology list or two?
Can an examiner follow a single record from alert to filing, whoever worked the case?
When a typology shifts, how long does it take you to change a rule and test it, and who signs it off?
Why does this matter?
Instant settlement has narrowed the window retrospective monitoring relied on
Instant settlement removed the overnight window that retrospective monitoring was built around.
Important risk signals can get lost across the customer lifecycle
A fraud signal caught at onboarding rarely reaches the analyst reviewing the same account three weeks later.
Regulatory expectations increasingly require stronger coordination
Verification of Payee has been mandatory for euro area PSPs since 9 October 2025, the UK has made both ends of a payment liable, and the AMLR applies from 10 July 2027. None of these land inside one function.
Disconnected systems increase the pressure on investigation teams
When a typology shifts, changing the detection logic takes an engineering cycle the fraud does not wait for.
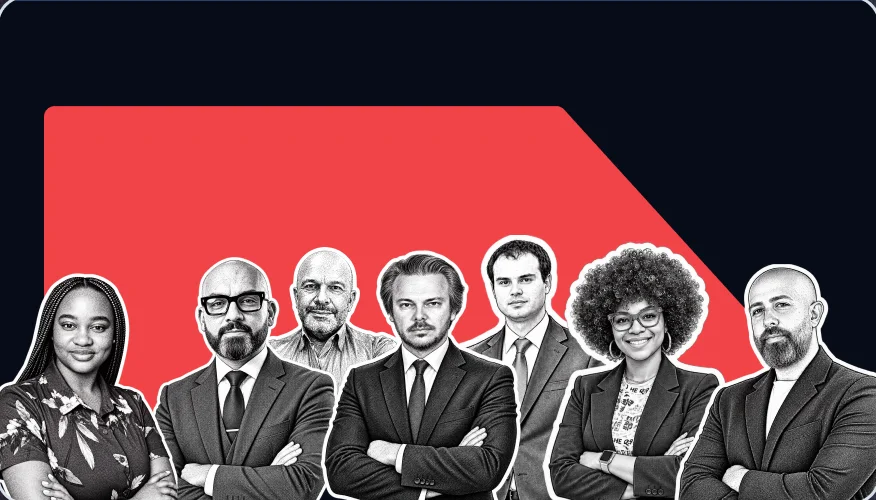
Meet the Panel
Senior Product Marketing Manager at Shufti
Daniela Marin is a Senior Product Marketing Manager at Shufti, with experience spanning fraud and identity, risk intelligence, cybersecurity, and B2B technology. She has led global go-to-market strategy, product messaging, and thought leadership for international technology brands, bringing a strong understanding of how complex risk and fraud topics can be translated into clear, practical conversations for financial services audiences.

CEO & Co-founder - AML Certification Centre
Andrei Sribny is CEO and Co-Founder of AML Certification Centre, with 5,000+ financial crime professionals trained across 79 countries. A former PwC Senior Auditor, he was awarded a CEPOL contract in 2026 to develop the EU’s first Diploma Course on Financial Investigations.
VP Business Manager - Trade Finance & Working Capital, Crown Agents Bank
Julia Rusu is a Vice President at Crown Agents Bank, a wholesale bank serving emerging markets across Africa and the Middle East. She has more than ten years in financial services, covering sanctions, trade-based money laundering and correspondent banking risk, with over fifty onsite reviews completed across six regions. She now works in Trade Finance and Working Capital, where she sees both the regulatory bar and the commercial pressure to keep business moving.
Head of AML & Security Department, Citadele banka Estonian Branch
Viktor Tkatsenko leads the AML and Security Department at Citadele Banka’s Estonian branch, where he also serves as MLRO. He has spent more than five years in the role, following earlier work in KYC project delivery at SEB and AML consulting in the digital asset sector. Viktor is an AML Expert with the AML Certification Centre and sits on the advisory board of the Banking CEE Network, a regional platform for financial services across Central and Eastern Europe.
Watch the recording
Certifications
Independently audited and certified for enterprise-grade security and data protection.
Frequently Asked Questions
Five parts across the hour. Why running fraud and AML separately has stopped working, how APP fraud behaves on an instant payment rail, the technical requirements for bringing the two together, how firms are structuring a unified risk team, and ten minutes of live questions.
Join at least 80 per cent of the live hour and complete the feedback form afterwards. AML Certification Centre issues the certificate.
Verification of Payee, mandatory for euro area PSPs since 9 October 2025. The UK reimbursement rules that made both ends of a payment liable, and the evaluation the Payment Systems Regulator published in July 2026. The AMLR, which applies from 10 July 2027. PSD3 and the PSR were politically agreed in November 2025 and the final texts endorsed in April 2026, and neither applies yet, so the panel treats them as a planning item.
No. The session is free, and so is the certificate.
15:00 CET, which is 14:00 GMT, 16:00 EEST and 09:00 ET. The session runs 60 minutes including live questions.
LIVE EVENT
Global Transactions, Local Rules: Closing Fraud Detection Gaps
LIVE EVENT
Financial inclusion and AML/CFT: Managing access and risk in practice
LIVE EVENT
PIX Fraud 2026: Are Your Fraud Controls Ready for the Next Generation of Instant Payment Scams?
LIVE EVENT
First Annual Fintech Executive Roundtable in Cyprus | 2025
LIVE EVENT
Innovation Roundtable Summit 2025: Build vs Buy vs Partner vs Prompt
LIVE EVENT
Meet Shufti at the UK AI Showcase, London Tech Week 2026
LIVE EVENT
Built by Shufti: A Podcast on Compliance Lifecycle
20th August
Online
LIVE EVENT
The Lifecycle of a Compliant Crypto Transfer : Travel Rule, Wallet Verification & Counterparty Risk
LIVE EVENT
Beyond the First Check: How AMLR Extends KYC Across the Customer Lifecycle
Launch Verification Instantly
Get access to Shufti’s Self-Service Portal and start verifying users with flexible, usage-based pricing.
Get Started