

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Advanced Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


ONGOING MONITORING
Verification Doesn’t End at Onboarding
Shufti continuously screens your existing customer base against sanctions, PEP lists, adverse media, and suspicious transaction patterns, so compliance gaps don’t build up between periodic reviews and regulatory obligations are met in real time.
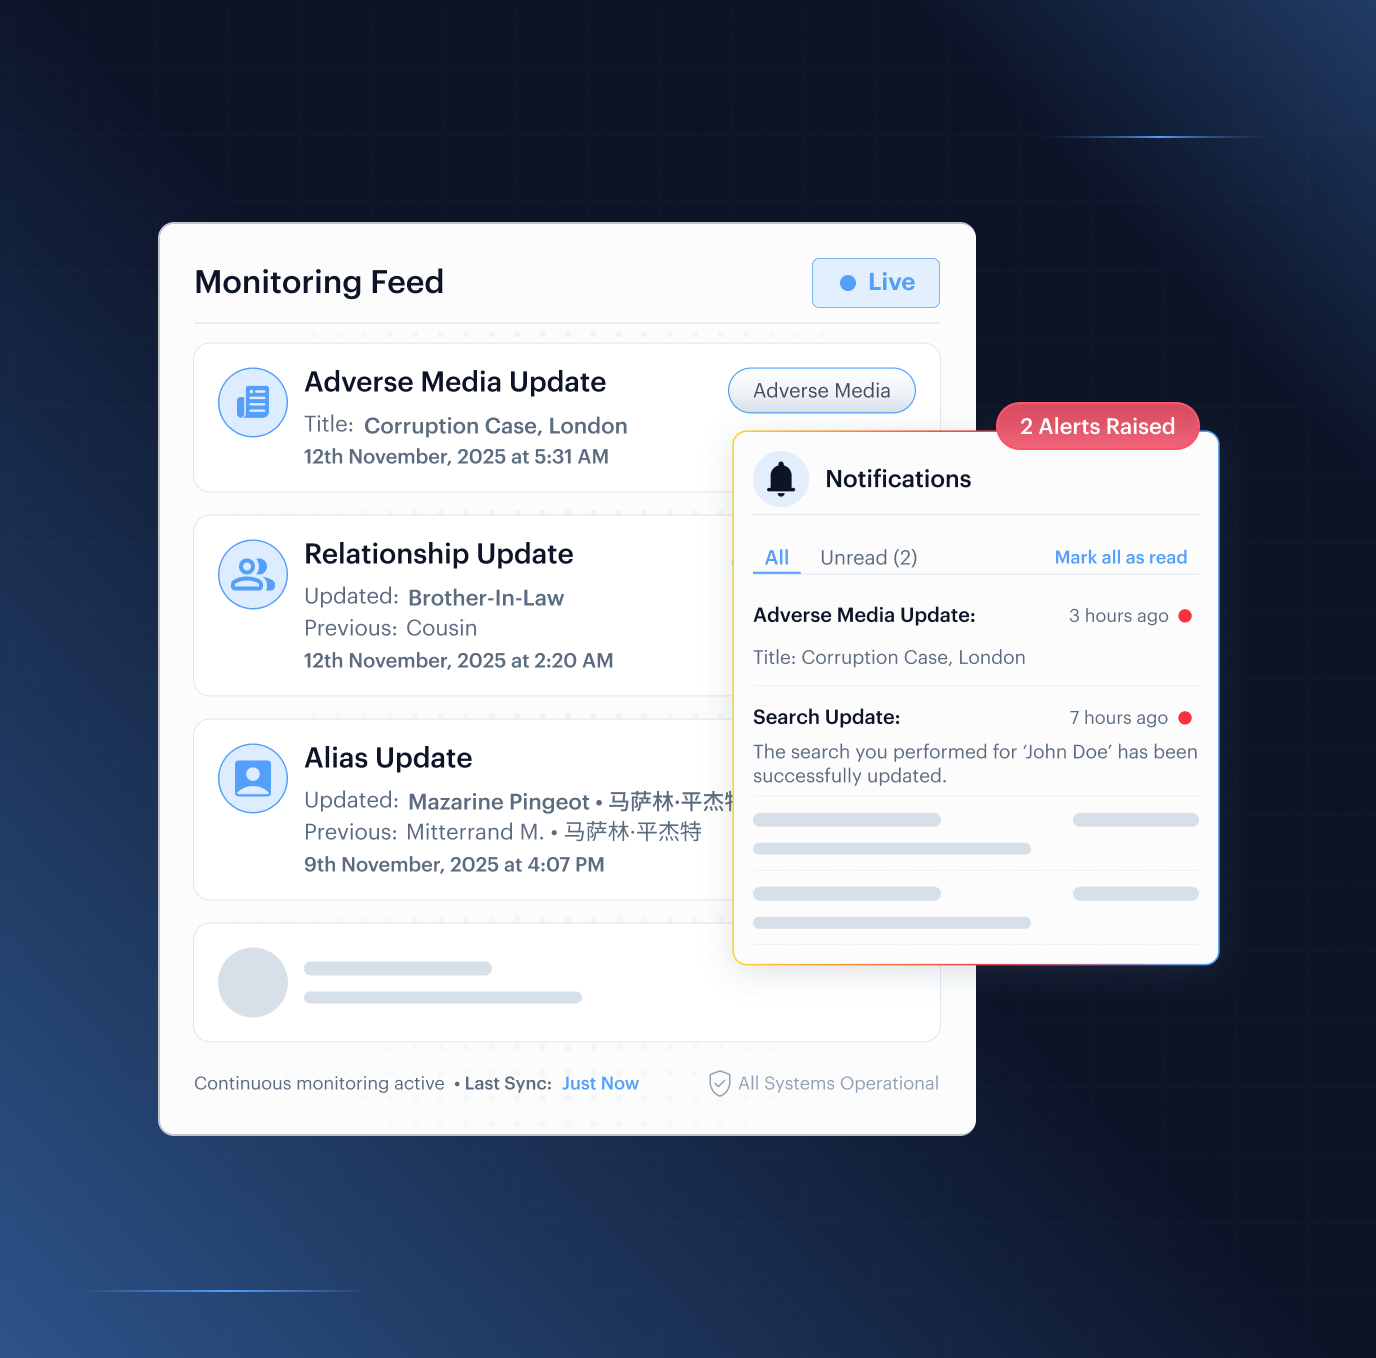


Continuous Compliance, Not Periodic Guesswork
Rescreening Without Blind Spots
Batch screening creates compliance gaps between scheduled checks. Shufti monitors sanctions, PEP, and adverse media changes continuously, so customer records are rechecked within minutes of a list update, not weeks later.
Reports Built For Filing
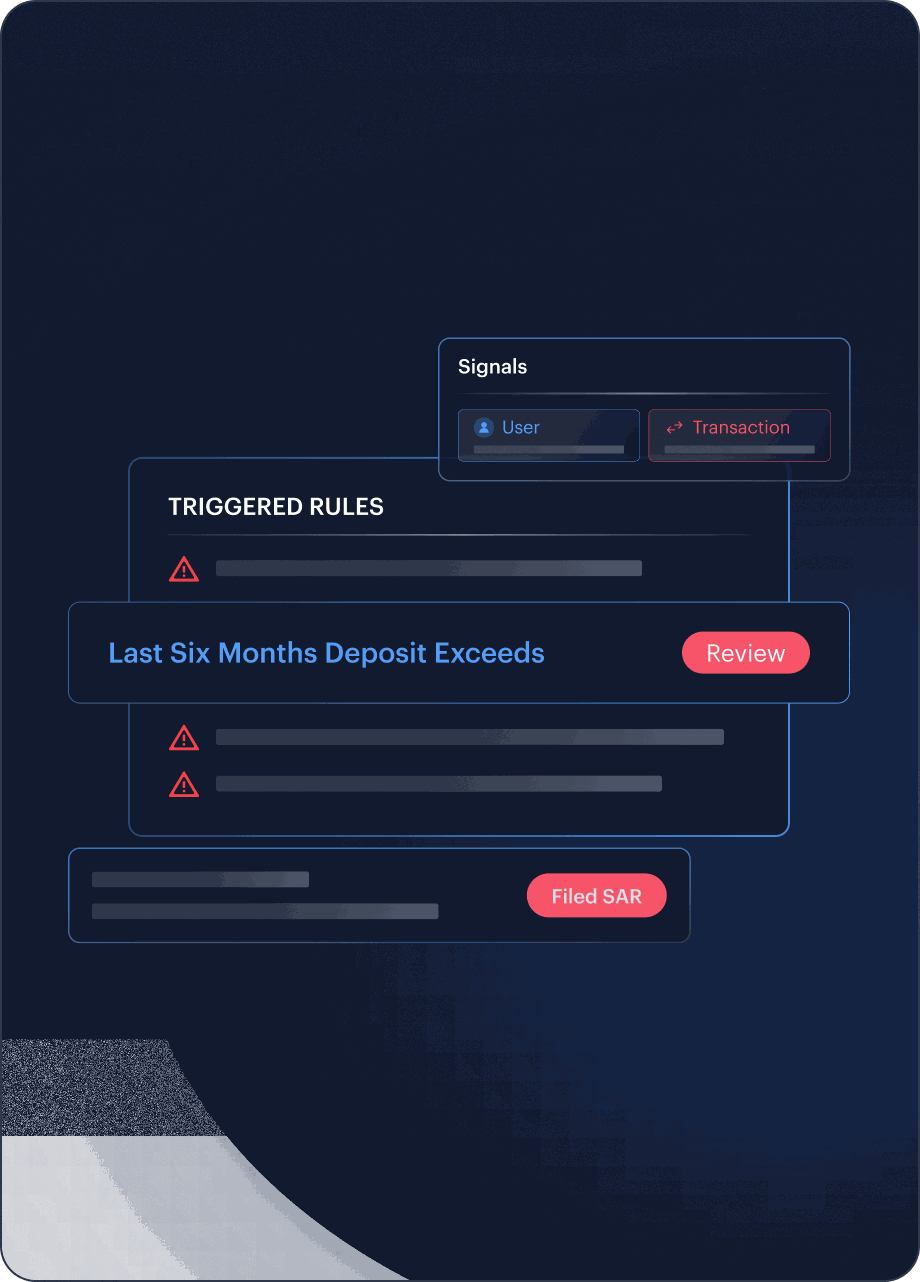
SAR preparation slows teams down when evidence has to be collected manually. Shufti detects suspicious patterns, connects transaction trails with customer history, and generates risk-scored SAR packages analysts can review and file faster.
Risk Profiles That Stay Current
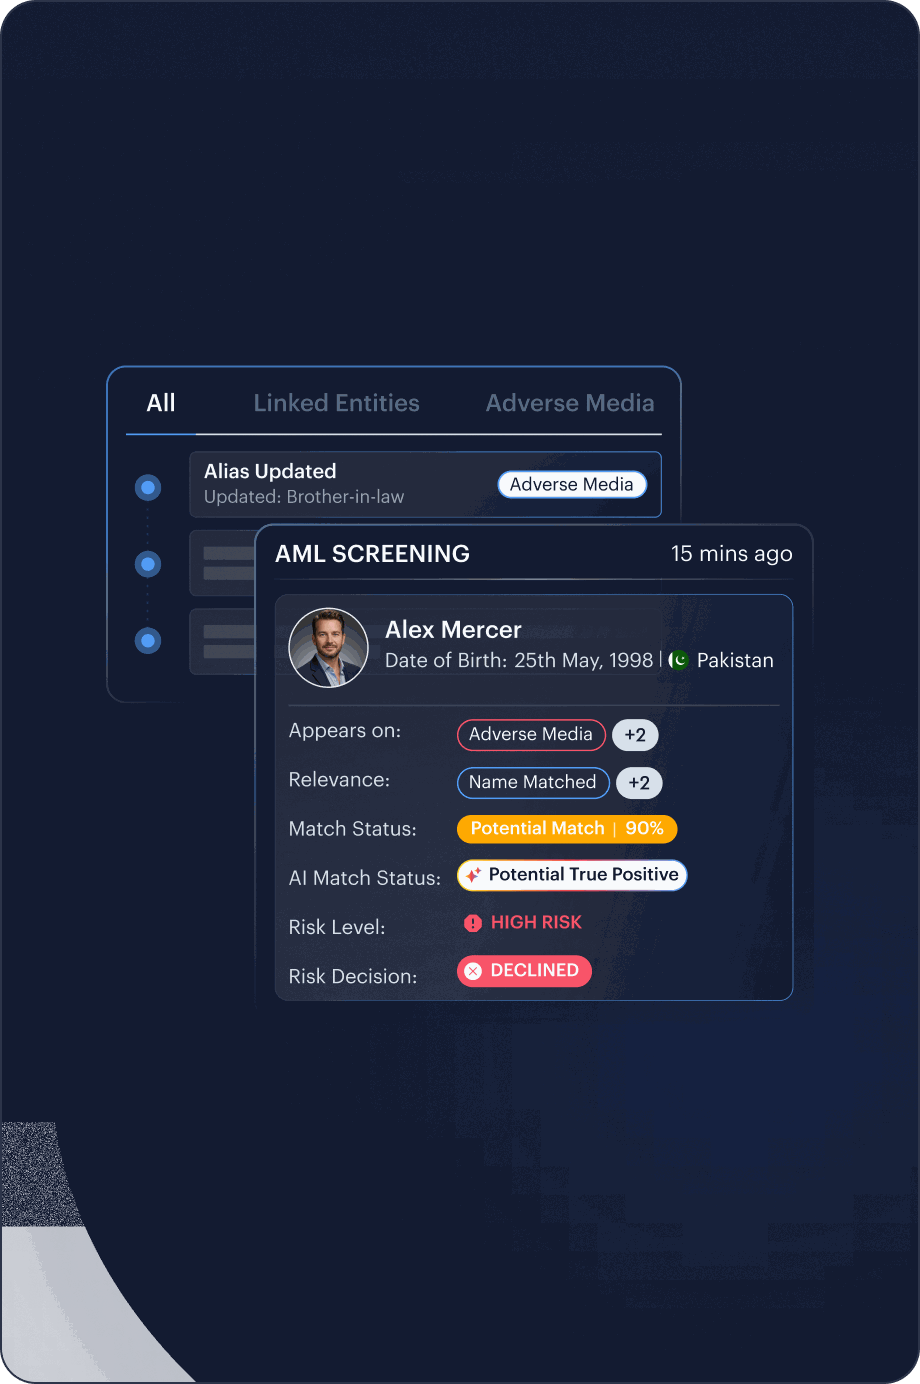
A low-risk customer can become high-risk long after onboarding. Shufti tracks profile, watchlist, media, and transaction changes over time, then explains what changed, when it changed, and which obligation it affects.
EXPLORE THE STACK
Everything You Need To Monitor Under One Hub
Screen continuously report automatically
Shufti's ongoing monitoring suite runs against your entire customer base, not just new applicants. Sanctions, PEP, adverse media, and transaction checks run as source data updates, triggering alerts and evidence packages the moment a risk profile changes.
-
Shufti enables ongoing AML monitoring by continuously re-screening verified individuals, businesses, UBOs, and crypto wallets after onboarding. Profiles are monitored against consolidated 4,000+ watchlists, 2.6M PEP records, adverse media in 80+ languages, and sanctioned wallet data. Data refreshes every 15 minutes from 100,000+ in-house sources, helping teams detect new risks as they emerge.
-
Detect suspicious patterns across customer transaction histories using rule-based triggers and ML models. Auto-generate defensible SAR packages with evidence chains ready for regulatory filing.
-
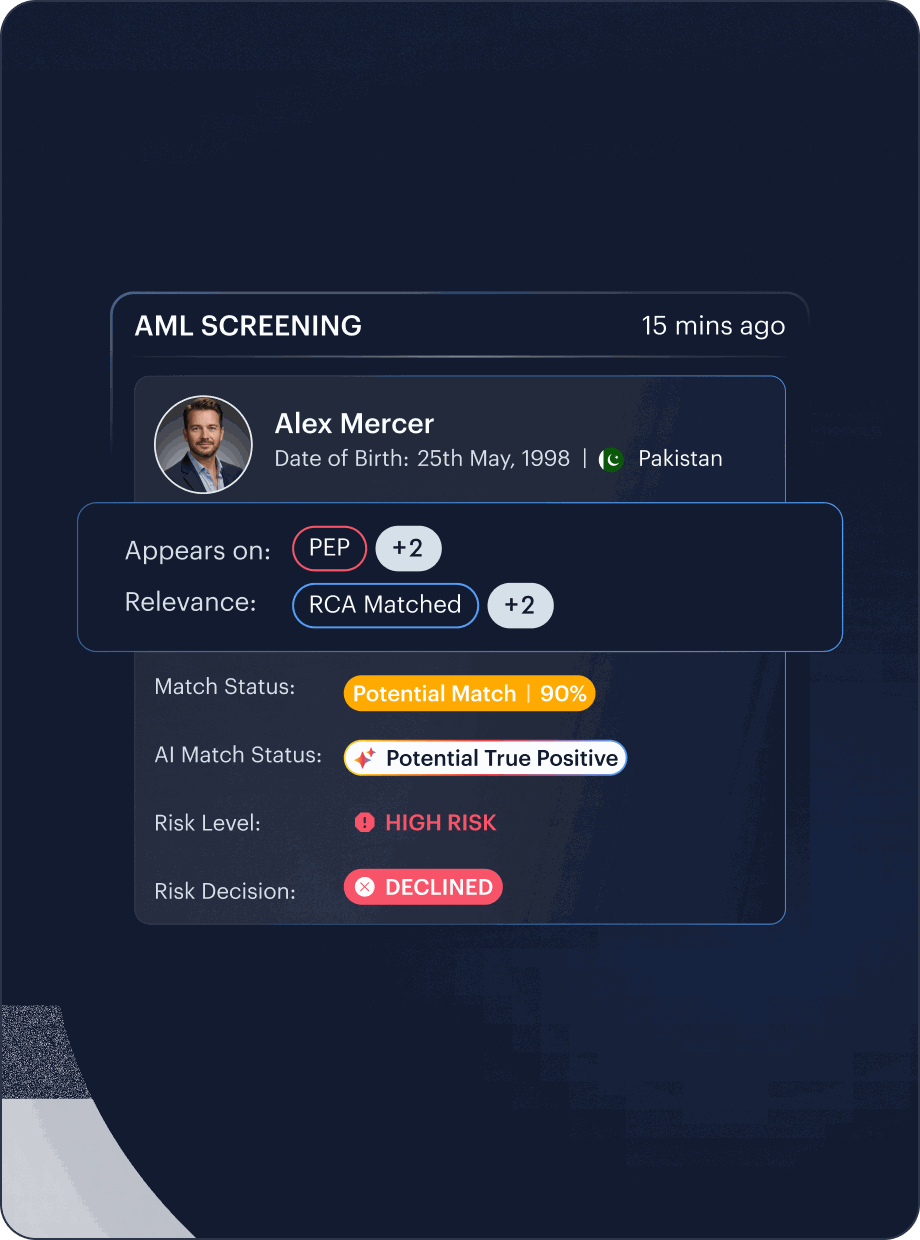
Monitor PEP status changes and new RCA connections across your existing customers. When a customer’s political exposure changes, the alert includes what changed and when.
-
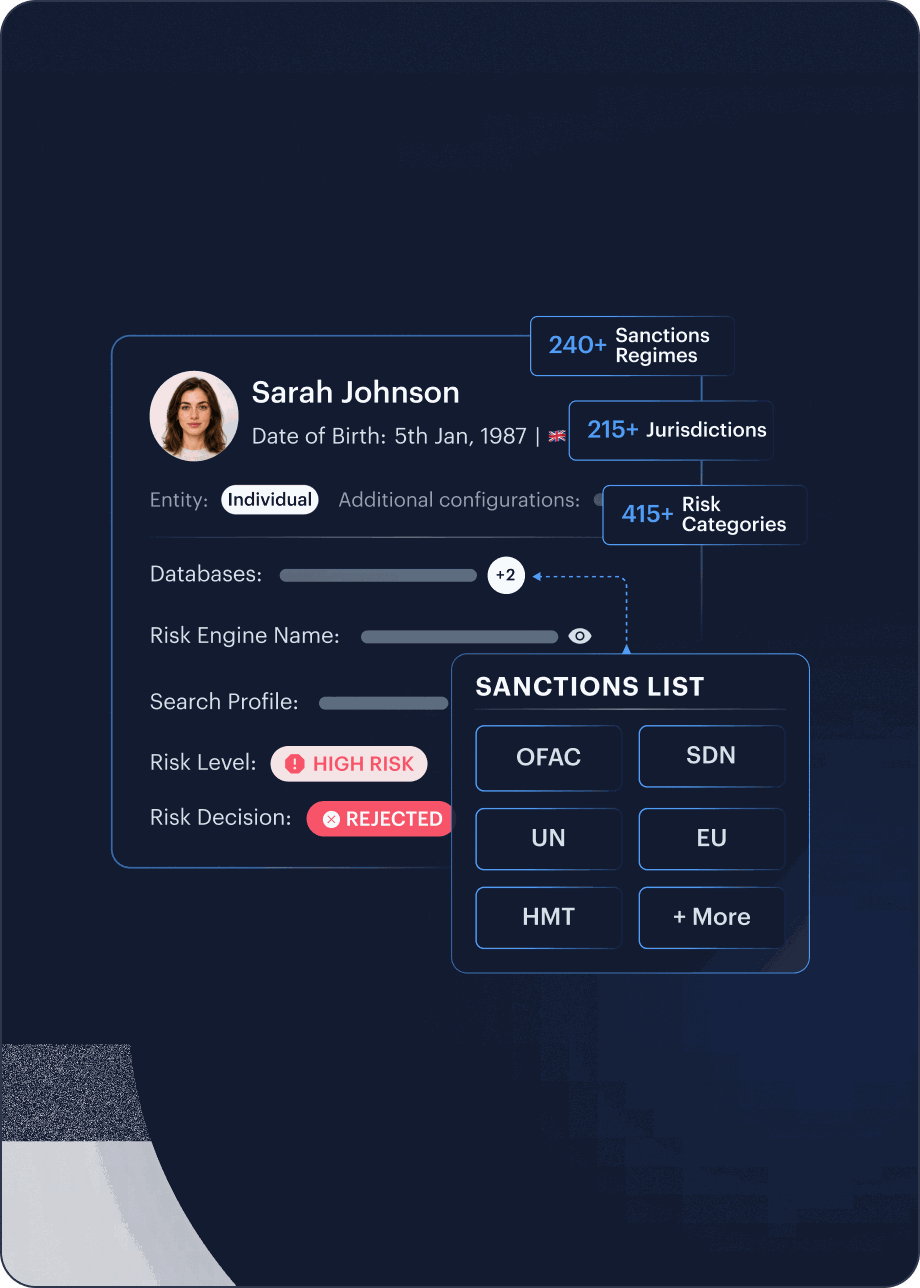
When a list changes, every matching customer in your base is flagged with the specific list and entry that triggered the match with 215+ sanction regimes (OFAC, HMT, EU, UN, Interpol, national FIUs). 415+ risk categories. Secondary and reciprocal sanction detection.
-
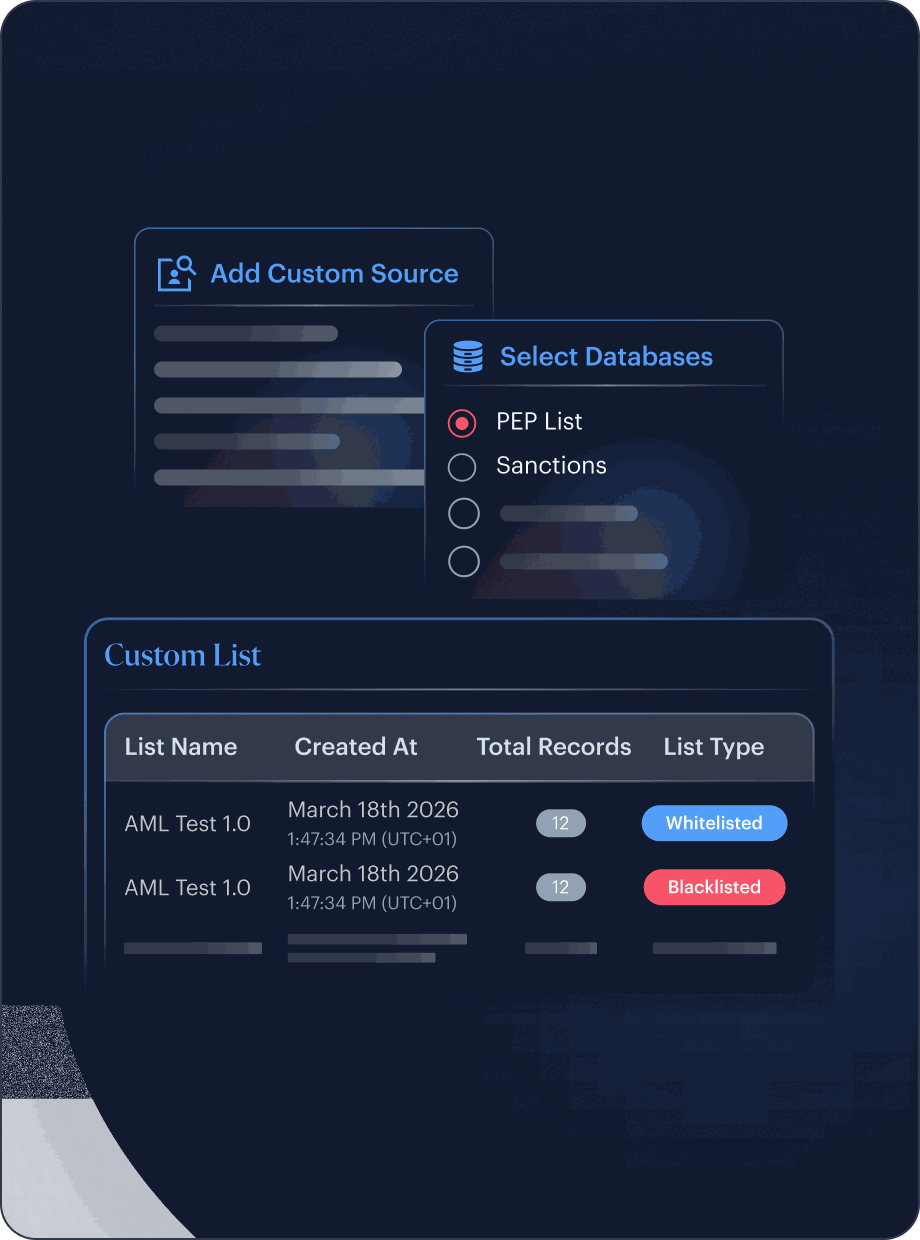
Screen against custom and proprietary watchlists beyond standard regulatory lists. Maintain internal blacklists and share flagged entities across multi-tenancy environments.
-
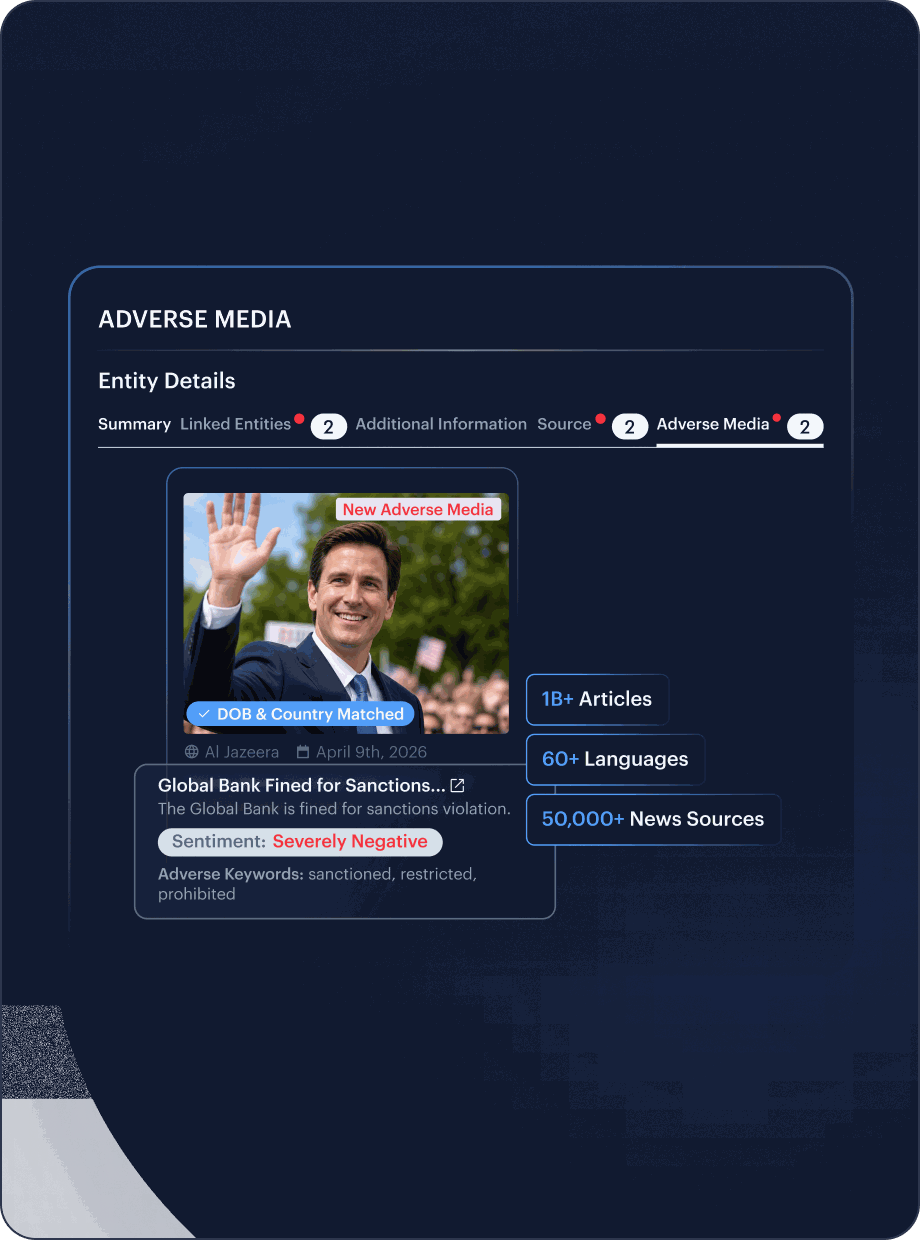
Continuously scan global news for negative coverage about your existing customers. NLP categorises hits by risk type and filters false positives, so your team reviews genuine signals.
-
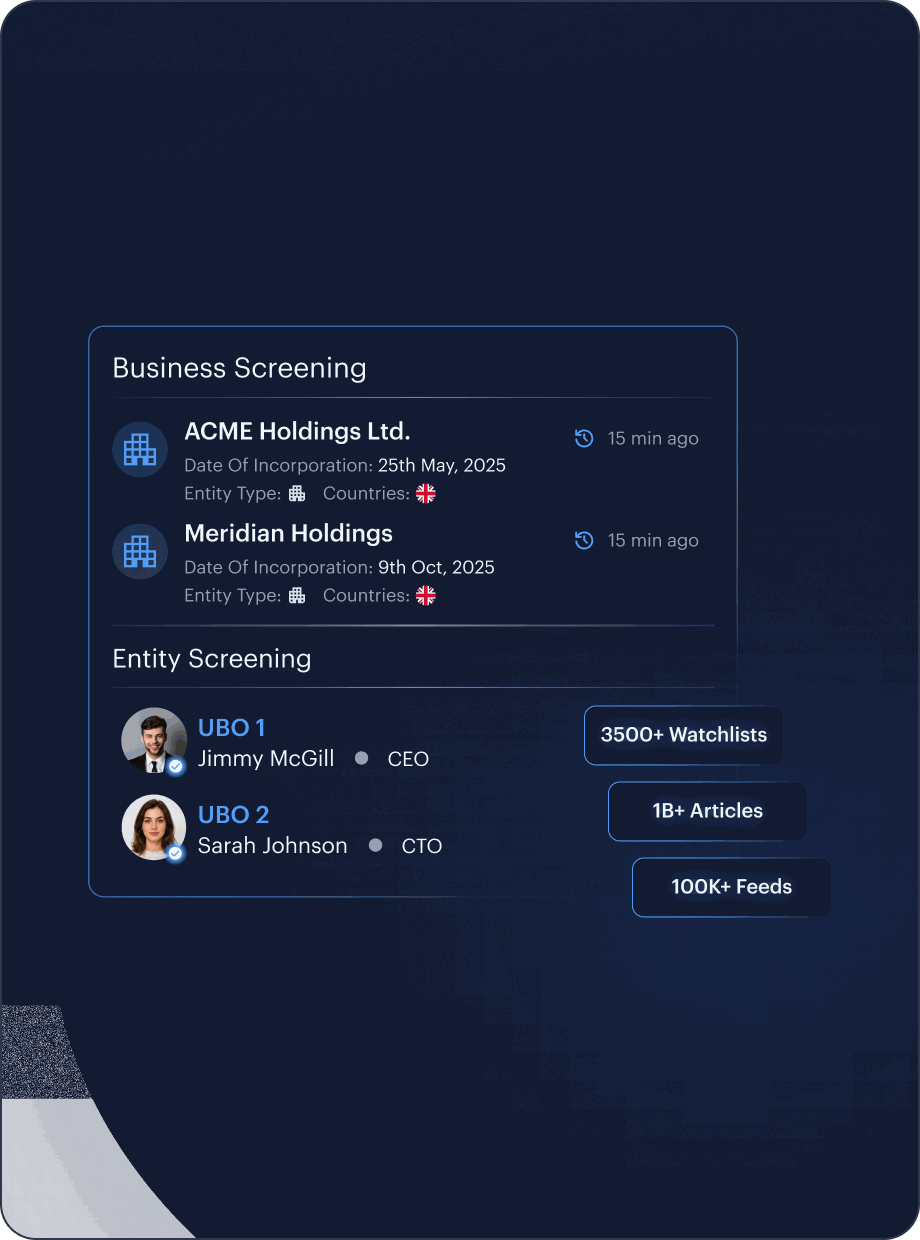
Extend ongoing monitoring to corporate customers. Screen entity names, directors, and UBOs against sanctions and PEP lists continuously, not just at B2B onboarding.


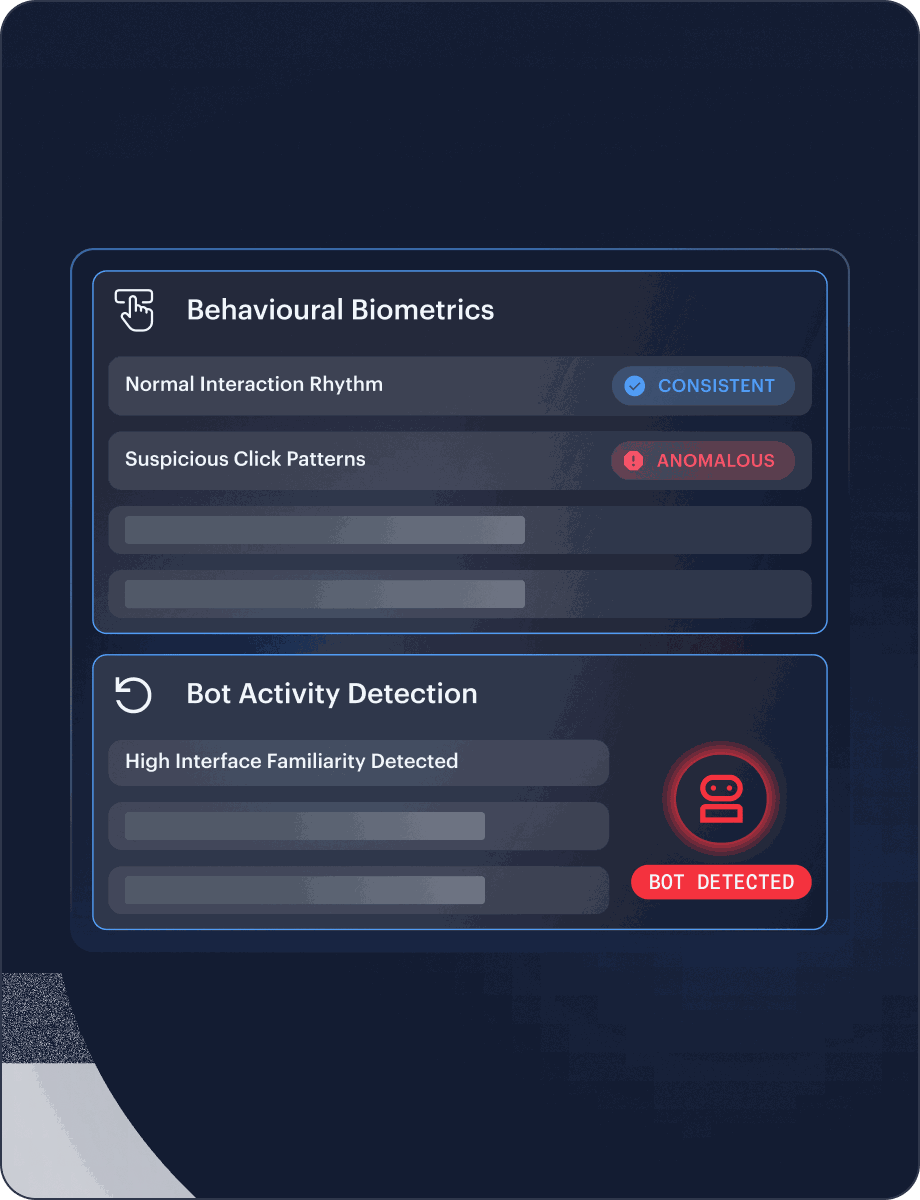
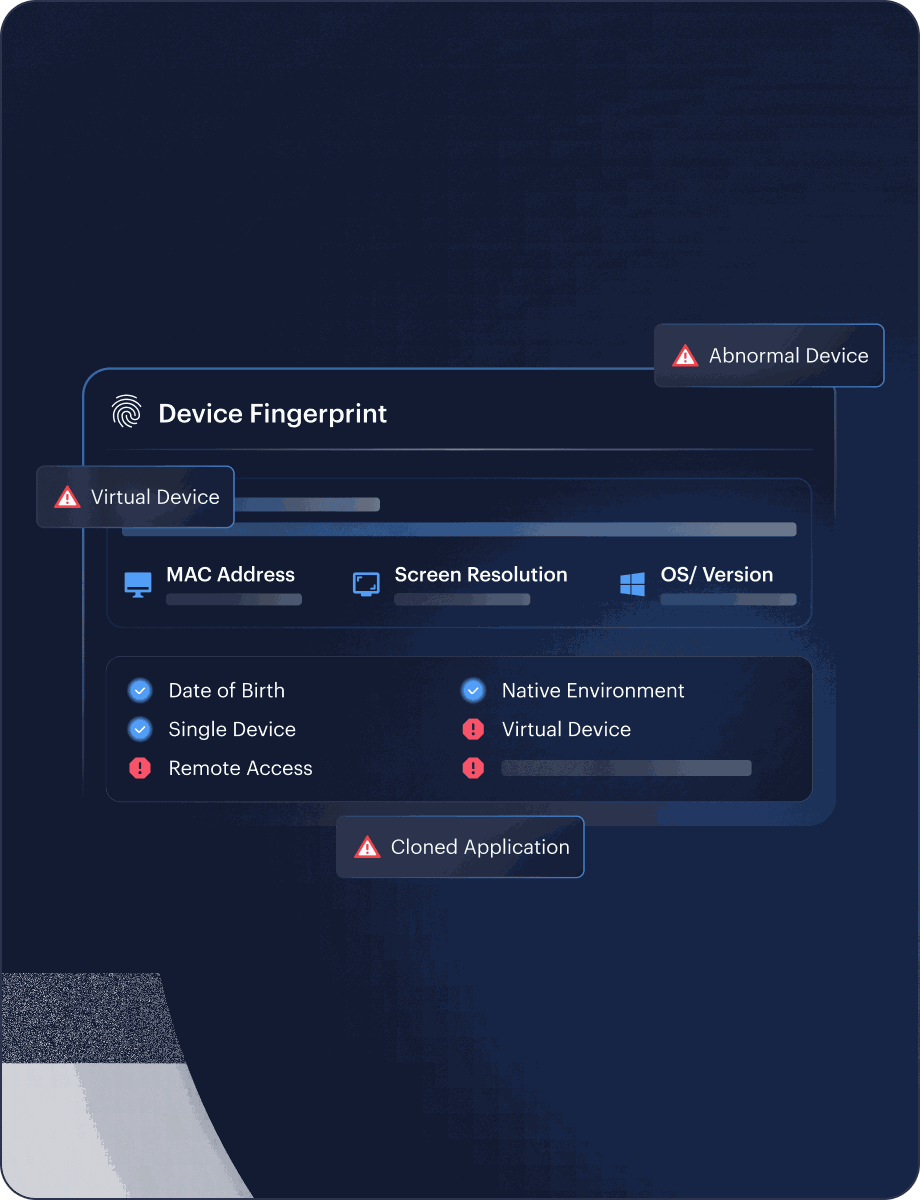
Detect account takeover and session anomalies post-onboarding
Ongoing monitoring isn’t just about AML. Shufti’s authentication layer detects behavioural changes that signal account compromise, device switching, and identity fraud in existing accounts.
-
Establish a behavioural baseline during onboarding, then monitor for deviations. When a customer’s typing pattern, device handling, or interaction speed changes significantly, flag the session for review.
-
Track device consistency across customer sessions. When a previously verified customer suddenly appears from a new device, different OS, or known-fraud fingerprint, trigger step-up verification.
-
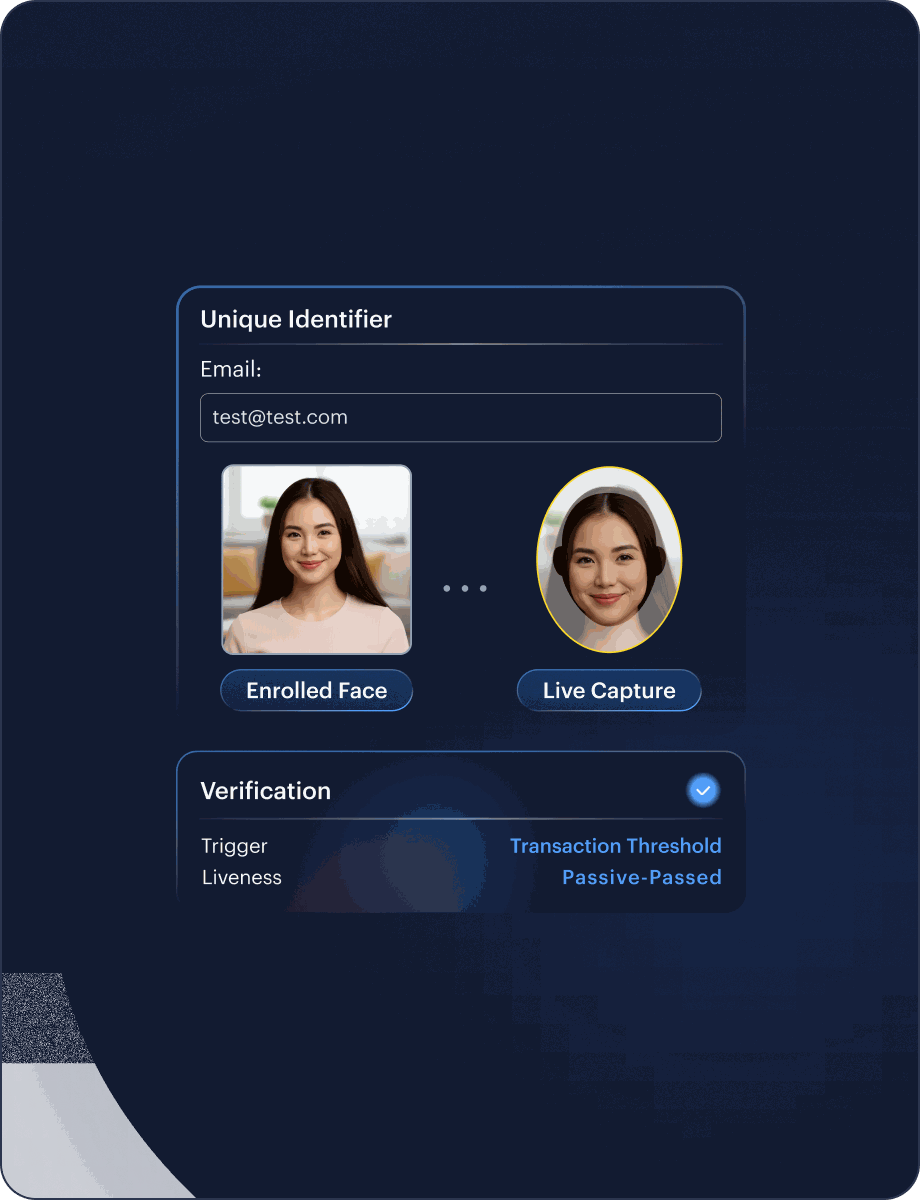
Periodically re-verify high-risk customers by matching a live selfie against their onboarding biometric. Trigger re-verification based on time intervals, transaction thresholds, or risk score changes.


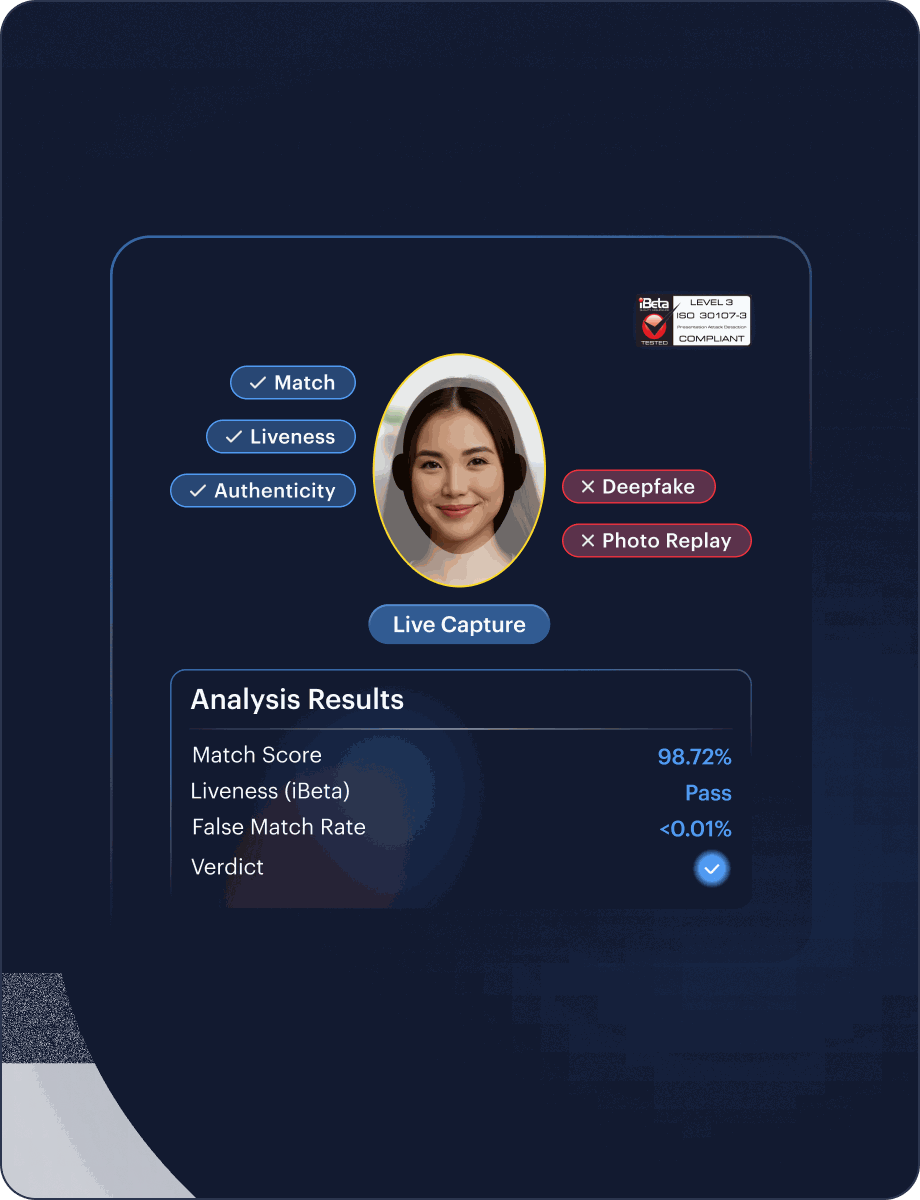
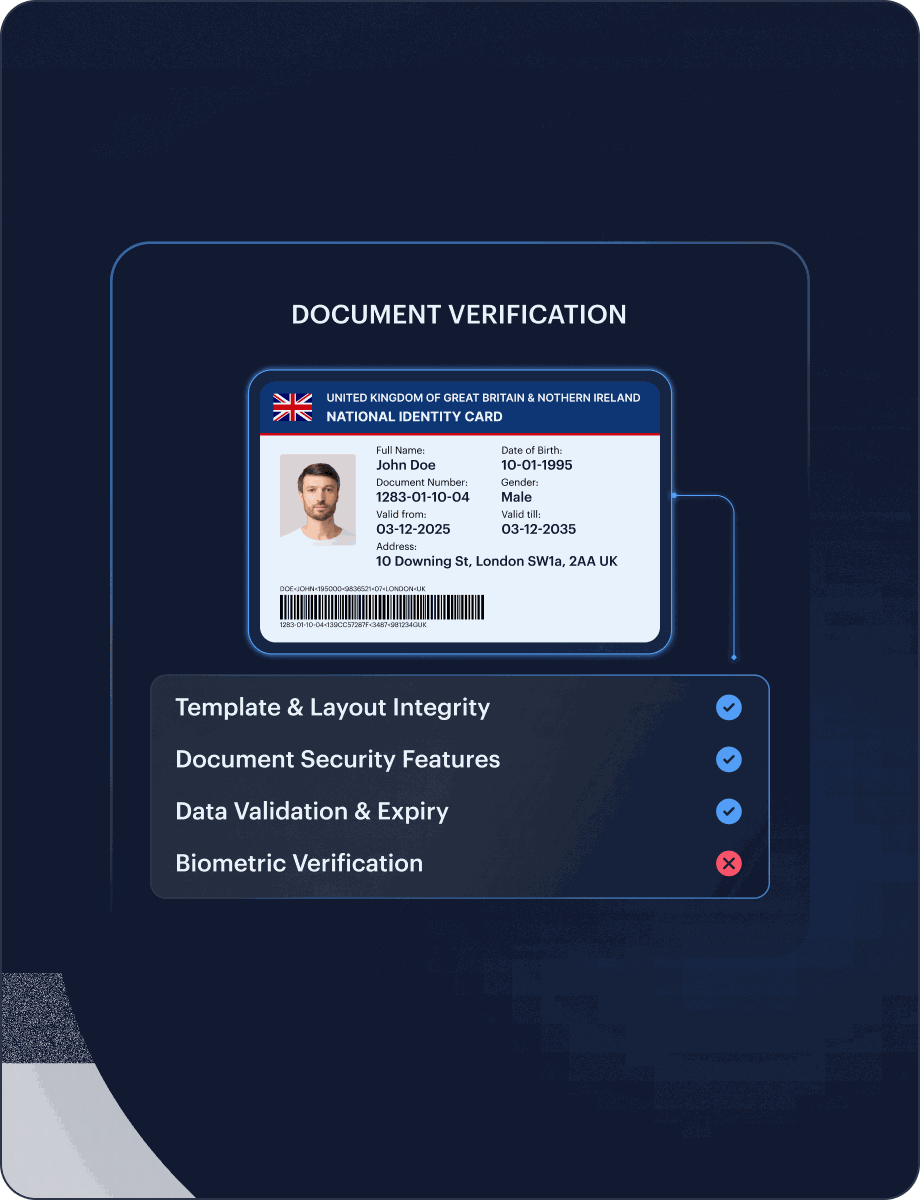
Re-verify when risk profiles demand it
When ongoing monitoring flags a change, a new sanctions hit, an adverse media alert, or a suspicious transaction, you may need to re-verify the customer’s identity. These products handle periodic and event-triggered re-KYC.
-
Re-verify customer identity for high-risk transactions or periodic account reviews. The same iBeta-certified liveness (98.72% accuracy) used at onboarding runs again to confirm the account holder is still the person verified.
-
When ongoing monitoring triggers re-KYC, request updated identity documents. The same forensic engine that authenticated the original ID now checks for changes, expired documents, or new security features.


Built For Every Role In Your Compliance Function
Build a continuous compliance layer across your customer lifecycle. Combine screening, transaction monitoring, and re-authentication to keep your customer base clean as risk profiles evolve.
Compliance Officer
Audit-ready evidence on every verification, structured for regulatory inspection across every jurisdiction you operate in.
Product Manager
Configurable verification flows that balance speed against risk tolerance, without rebuilding the integration each time.
Developer
REST API, mobile SDKs, and sandbox access. First verification call within hours of integration start.
Fraud Analyst
Pre-scored evidence and fraud signals on every flagged case, so your team reviews decisions, not raw submissions.
Detect Every Fraud Type Targeting Your Platform
Deepfake
AI-generated faces and synthetically forged documents bypass legacy liveness checks at scale. Shufti's passive liveness & document forensics detects synthetic media before it reaches your onboarding flow.
Identity Fraud
Credential theft, blended synthetic identities, and manipulated documents exploit gaps in manual review. Shufti's layered verification surfaces fraud signals before accounts are created.
Account & Platform Abuse
Duplicate registrations, bot-driven sign-ups, and referral exploits erode platform economics. Shufti links device, identity, and behavioural signals to flag abuse rings at scale.
Transaction & Payment Fraud
False chargeback claims, money mule networks, and sanctions evasion expose your business to financial and regulatory risk. Shufti ties identity verification directly to transaction context.
HOW IT WORKS
How Shufti Keeps You Ahead Of Compliance Risk
STEP 01
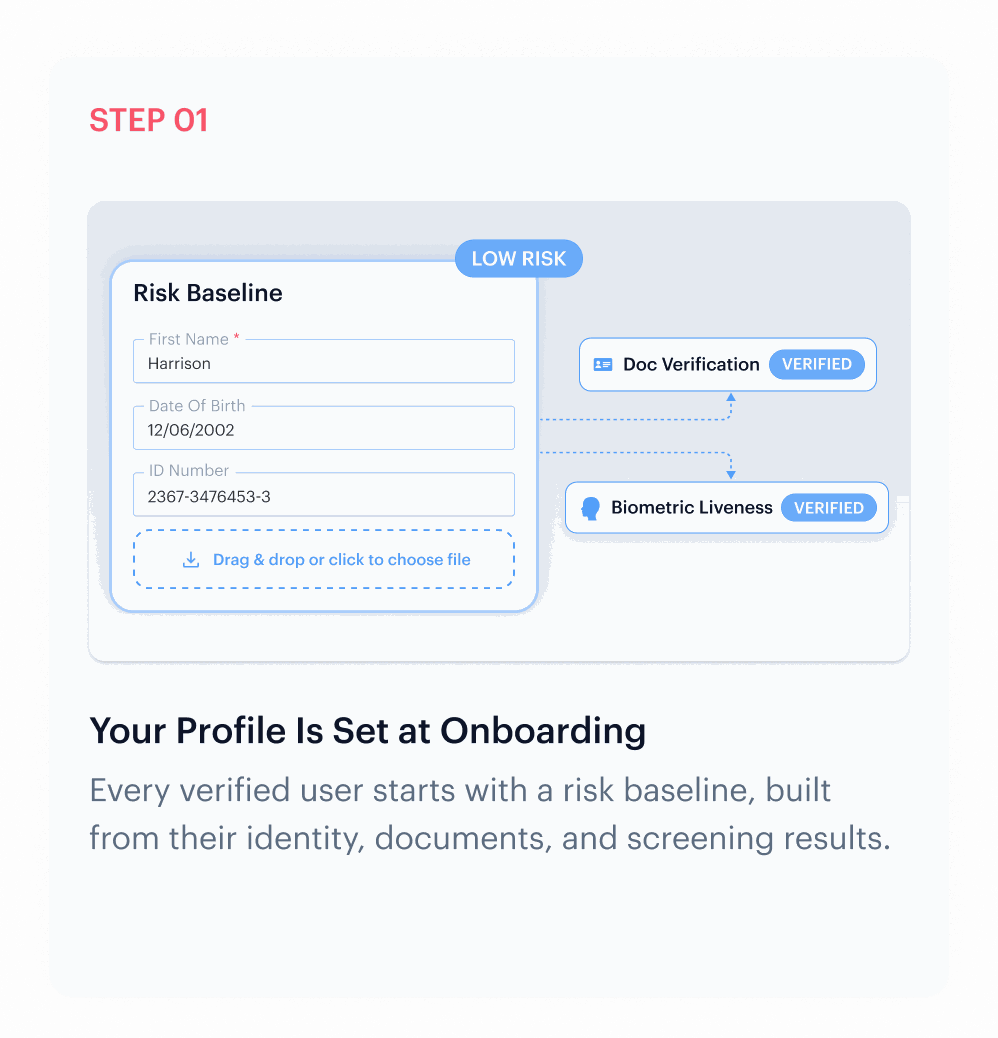
Your Profile Is Set at Onboarding
Every verified user starts with a risk baseline, built from their identity, documents, and screening results.
STEP 02
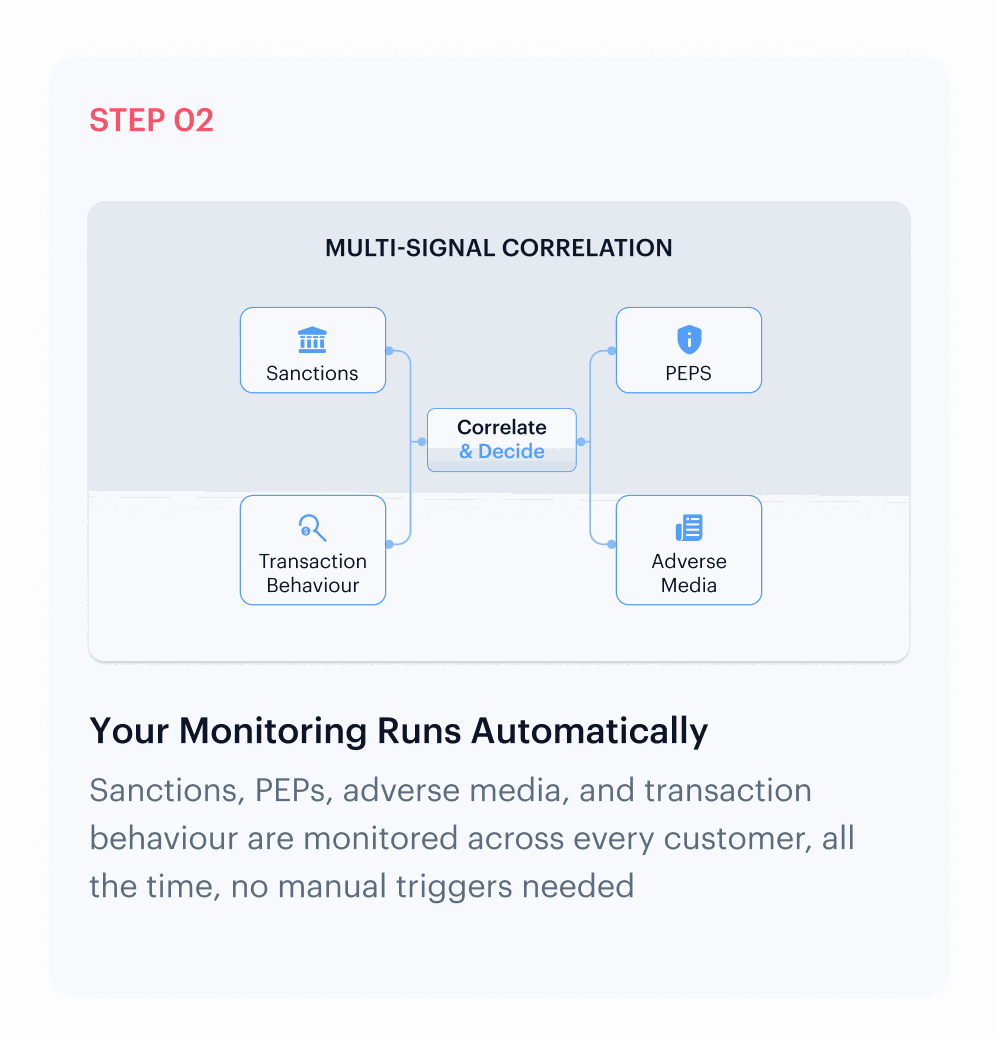
Your Monitoring Runs Automatically
Sanctions, PEPs, adverse media, and transaction behaviour are monitored across every customer, all the time, no manual triggers needed
STEP 03
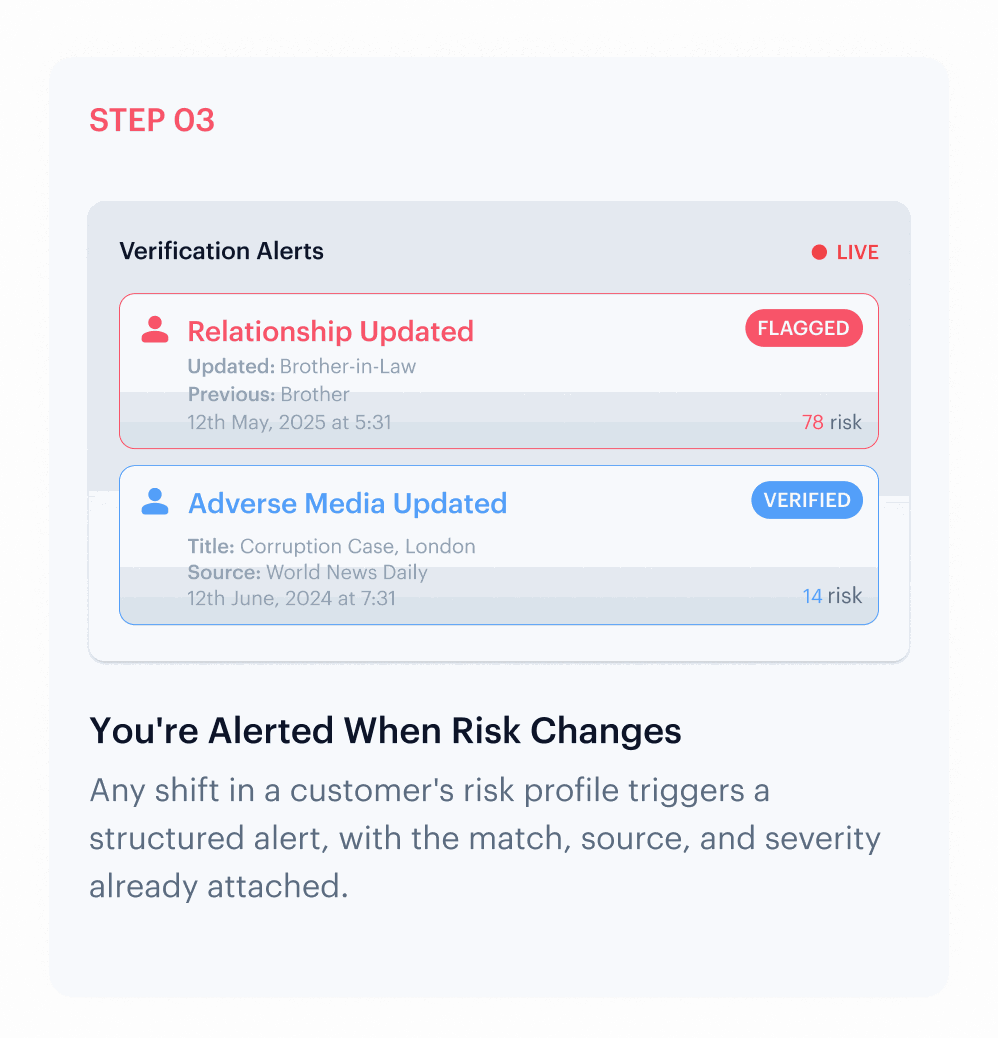
You're Alerted When Risk Changes
Any shift in a customer's risk profile triggers a structured alert, with the match, source, and severity already attached.
STEP 04
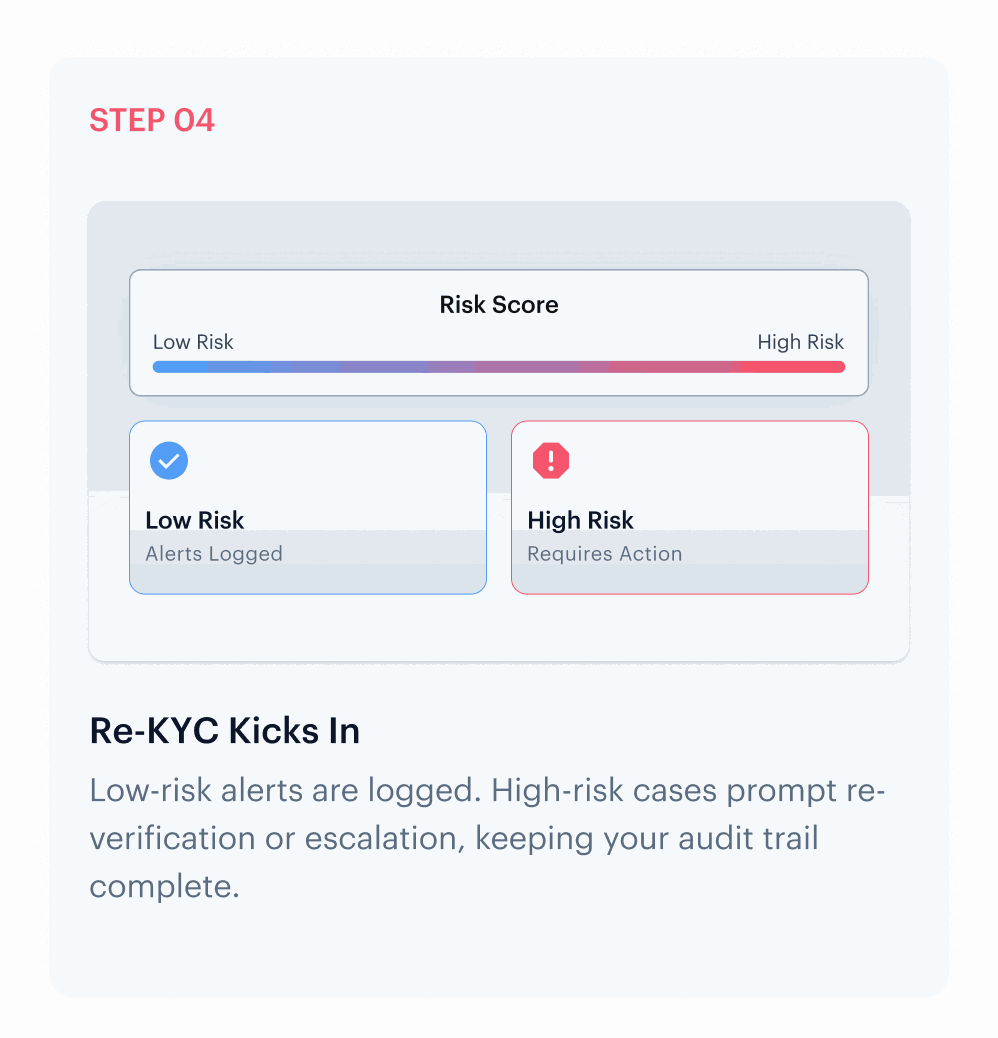
Re-KYC Kicks In
Low-risk alerts are logged. High-risk cases prompt re-verification or escalation, keeping your audit trail complete.
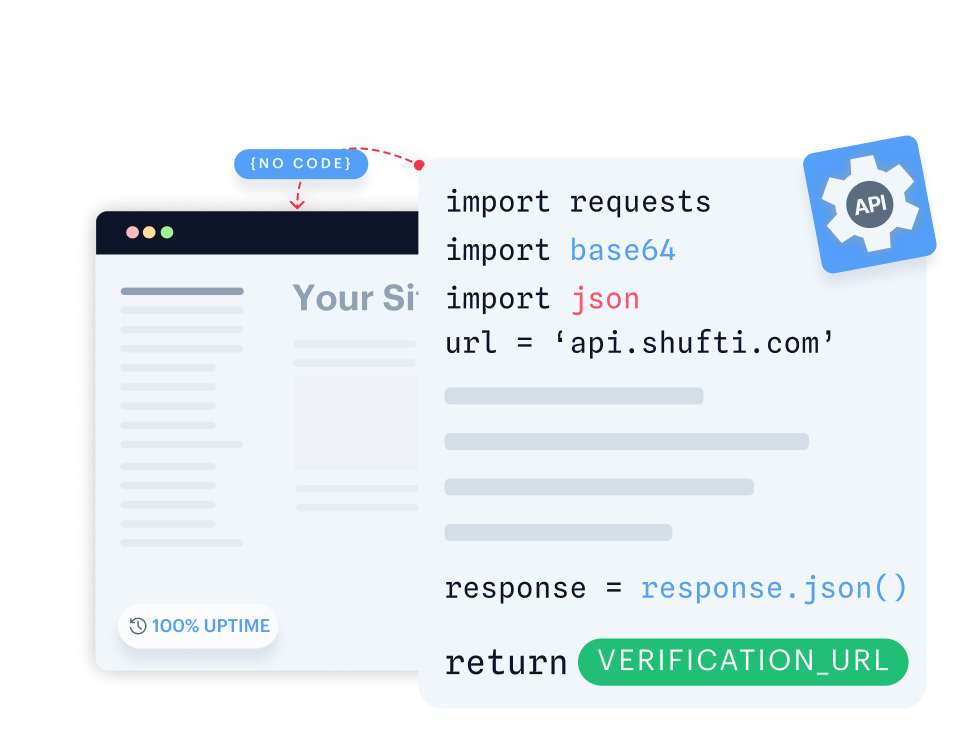
Live in Production Within Days, Not Months
Build fully customisable verification flows with seamless backend integration.
- Gain full control by customising verification flows end-to-end.
- Integrate seamlessly with your backend for quick implementation.
- Design flexible verification journeys tailored to your users.
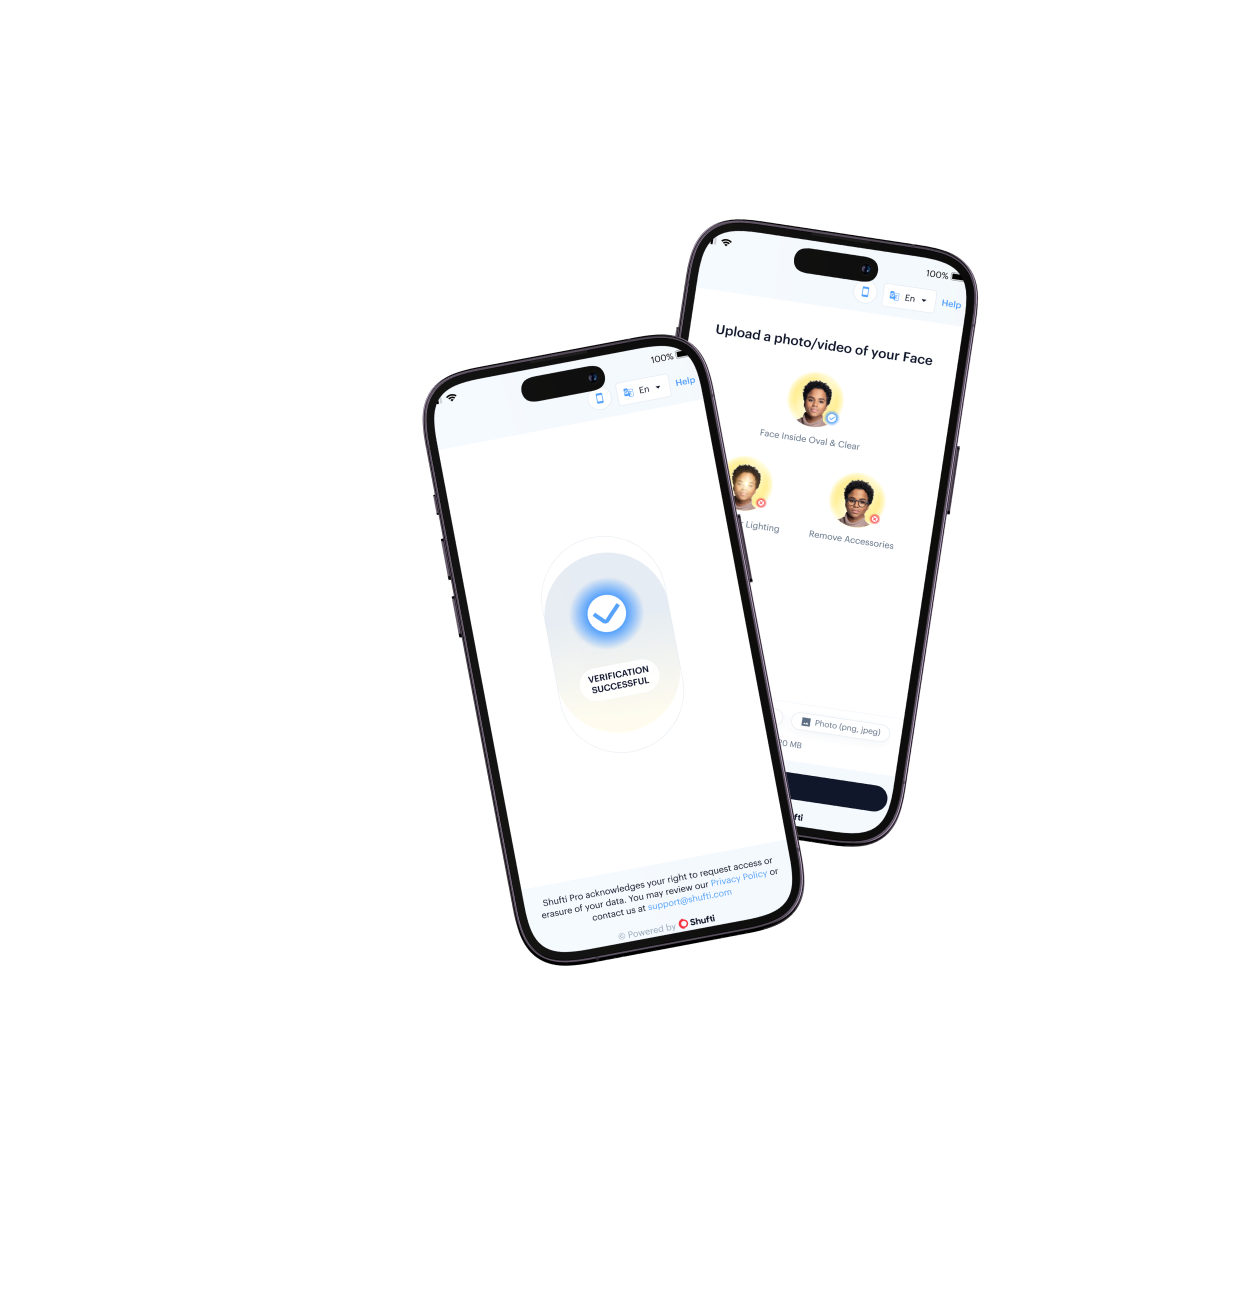
Launch a native verification experience in your mobile app within minutes.
- Launch native verification within minutes on iOS or Android.
- Use ready-made UI with camera, capture, and real-time feedback.
- Customise flows to fit seamlessly into your mobile app.
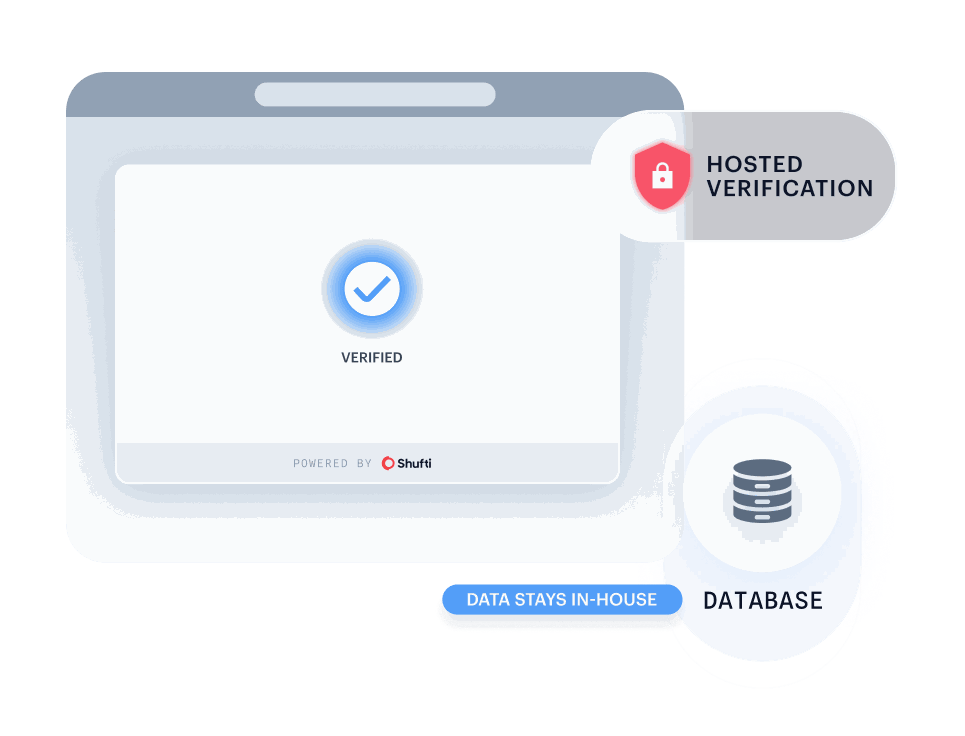
Run Shufti within your own identical-capability infrastructure for maximum data control and privacy.
- Keep all sensitive information in-house to meet strict governance and data residency requirements.
- Keep sensitive information fully private and secure in-house.
- Deploy in highly regulated sectors without compromising compliance.
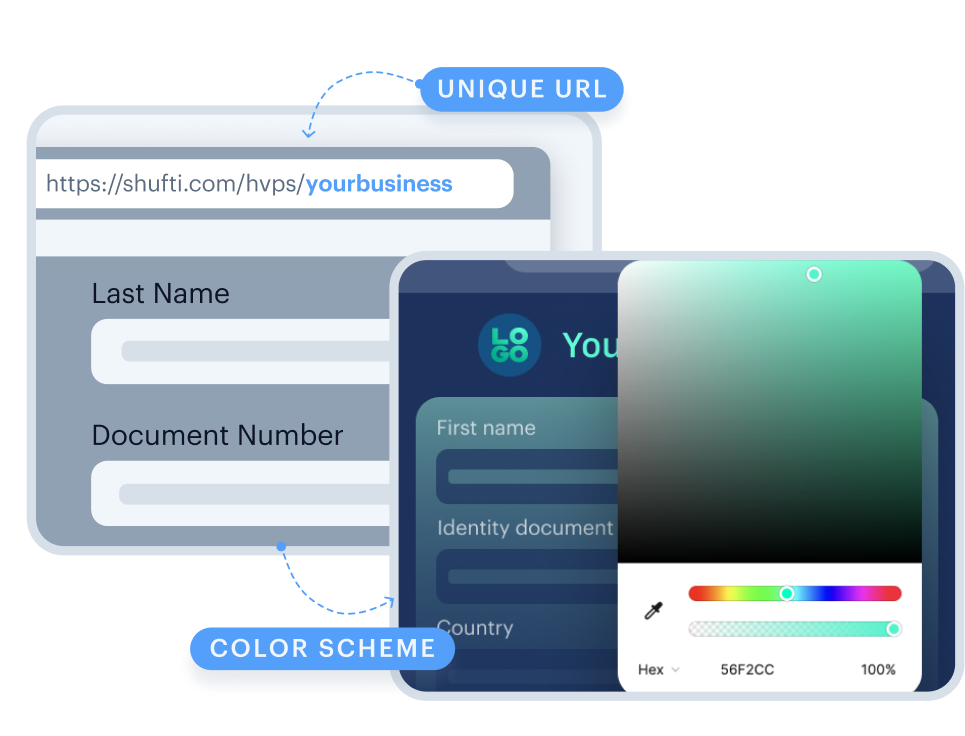
Quickly launch identity verification through a secure, customisable web link, no code required. Learn more.
- Start verifying users instantly with a no-code setup.
- Deliver a consistent identity experience via a link or embedded iframe.
- Deploy quickly via a secure link or embedded iframe.
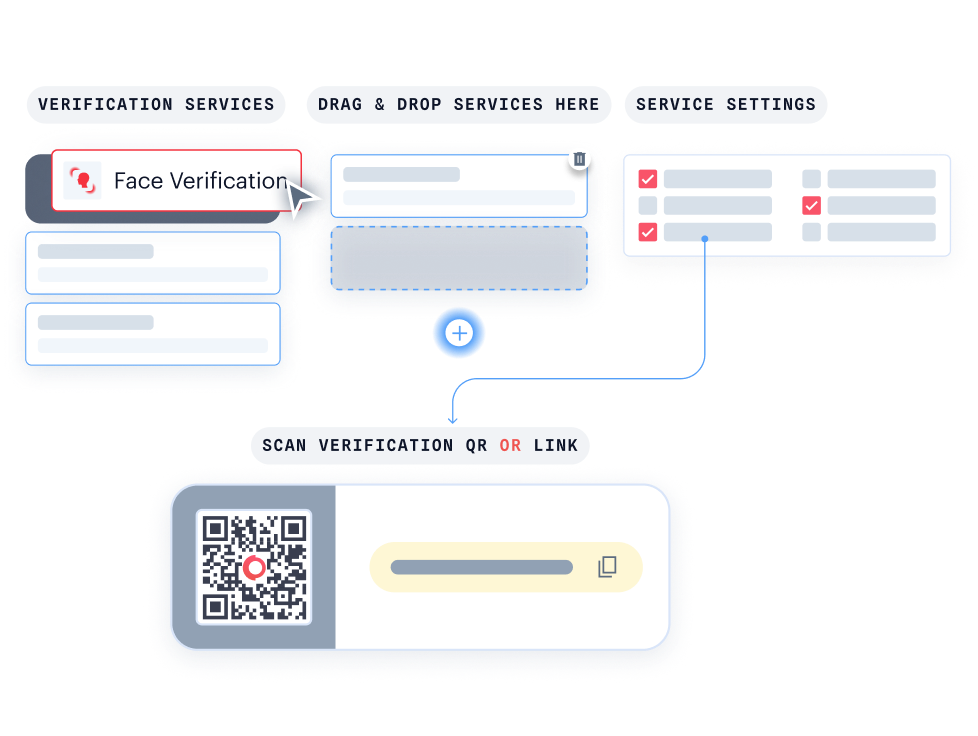
With KYC Journey Builder, create personalised verification journeys without writing a single line of code.
- Customise your journey effortlessly with drag-and-drop functionality.
- Instantly see how your verification flow looks for your users.
- Easily connect with Hosted Verification for a consistent, branded experience.
Validated By Leading Analysts And Certification Bodies
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
Ranked Exceptional for age verification by Liminal Index 2026
View Report
Recognised as a Leader in G2 Summer 2026 reports
View Reviews
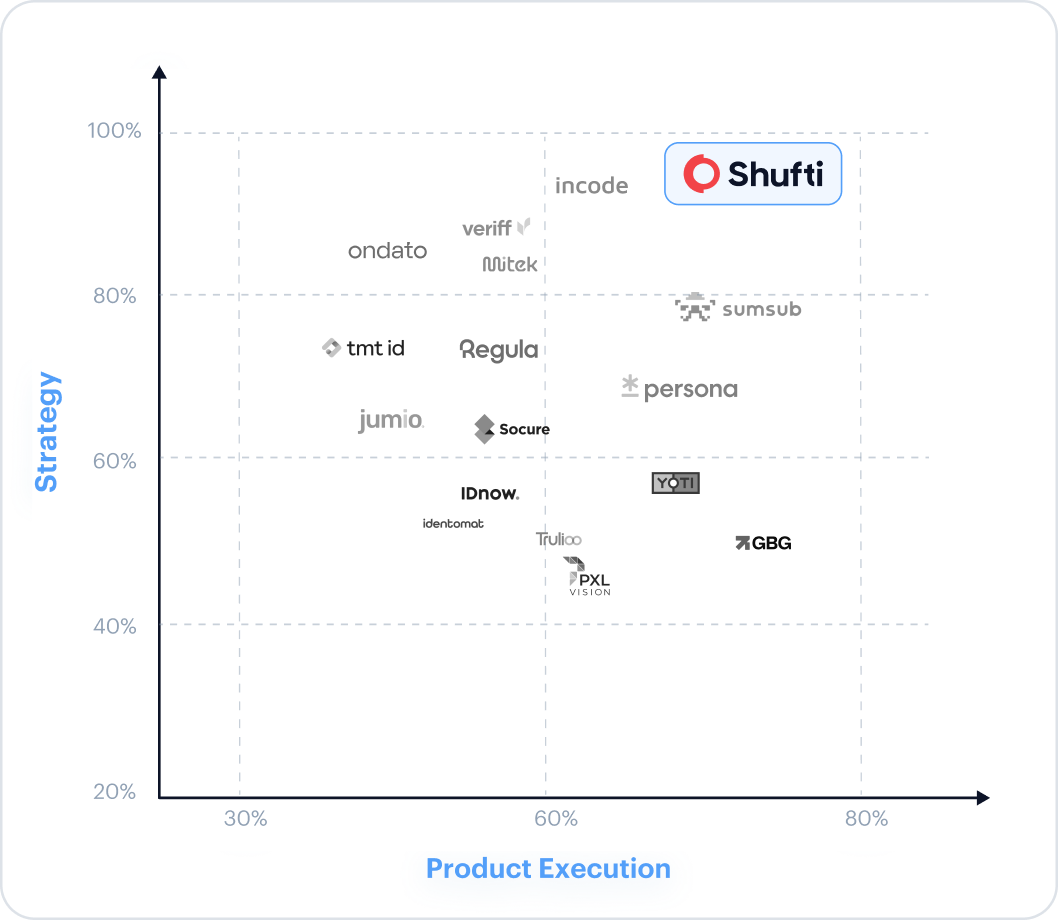
Differentiated by Gartner on document diversity and country coverage
Read more
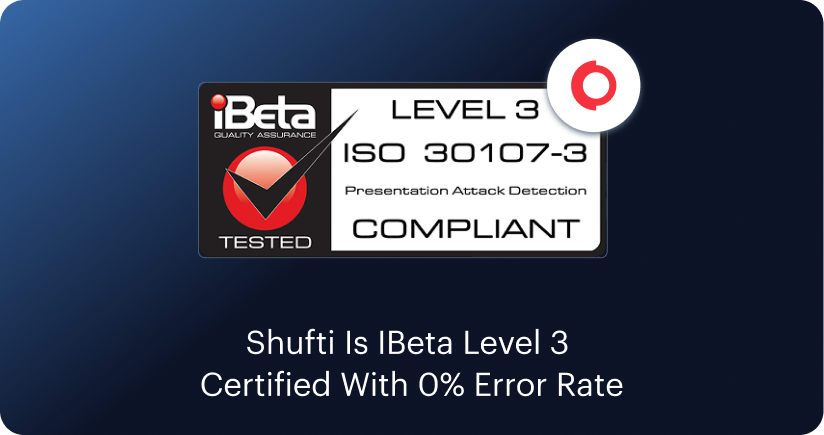
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
BUILT FOR YOUR INDUSTRY
Ongoing Compliance Built Around Your Industry
Stay Compliant As Customer Risk Evolves
Keep your customer book clean as risk profiles evolve, without triggering full re-onboarding. Automated CDD/EDD rescreening and SAR-ready alerts let your compliance team focus on true risk, not routine paperwork.


Frequently Asked Questions
What’s the difference between onboarding screening and ongoing monitoring?
Onboarding screening runs once, at the point a customer is verified. Ongoing monitoring runs continuously against your entire existing customer base, detecting changes in sanctions status, PEP exposure, adverse media, and transaction behaviour after onboarding is complete.
How quickly does Shufti detect a sanctions list change?
When OFAC, EU, UN, or any of 50+ jurisdiction-specific lists update, Shufti propagates the change within minutes. Every customer in your base is automatically rescreened against the updated data — no manual batch run required.
Can I configure screening frequency per customer risk tier?
Yes. High-risk customers can be rescreened daily or on every list update. Standard-risk customers can be set to weekly or monthly. Thresholds and frequencies are configurable via the backoffice or API.
Does the system generate SARs automatically?
When transaction monitoring or screening triggers an alert that meets your configured SAR threshold, the system generates a SAR package including transaction chains, customer history, screening results, and risk scoring. The package is formatted for regulatory filing.
How does ongoing monitoring work for business customers?
Business AML Screening extends continuous monitoring to corporate entities. Entity names, directors, and UBOs are screened against sanctions and PEP lists on an ongoing basis, not just at the point of B2B onboarding.
Can I trigger re-KYC from a monitoring alert?
Yes. When monitoring flags a risk change (sanctions hit, adverse media, suspicious transaction), you can configure automatic re-KYC requests. The customer receives a reverification flow using the same products (document verification, facial biometrics) used at onboarding.
Build A Monitoring Layer That Keeps Pace With Regulations
Sanctions lists update daily. Customer risk profiles change. Shufti’s continuous monitoring catches what batch screening misses.Button: Assess Your Monitoring Coverage