

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


Workforce IAM
Workforce IAM: Verified Human Identity at Every Access Control Point
Shufti workforce identity and access management (WIAM) closes the identity assumption gap in enterprise workforce access management. Verify human identity across onboarding, account recovery, privileged access, Information Technology Service Management (ITSM) approvals, remote access, and MFA re-enrollment without replacing your existing identity and access management stack.


Verified Human Identity at Every Workforce Access Control Point

Workforce Onboarding Creates the Identity Anchor
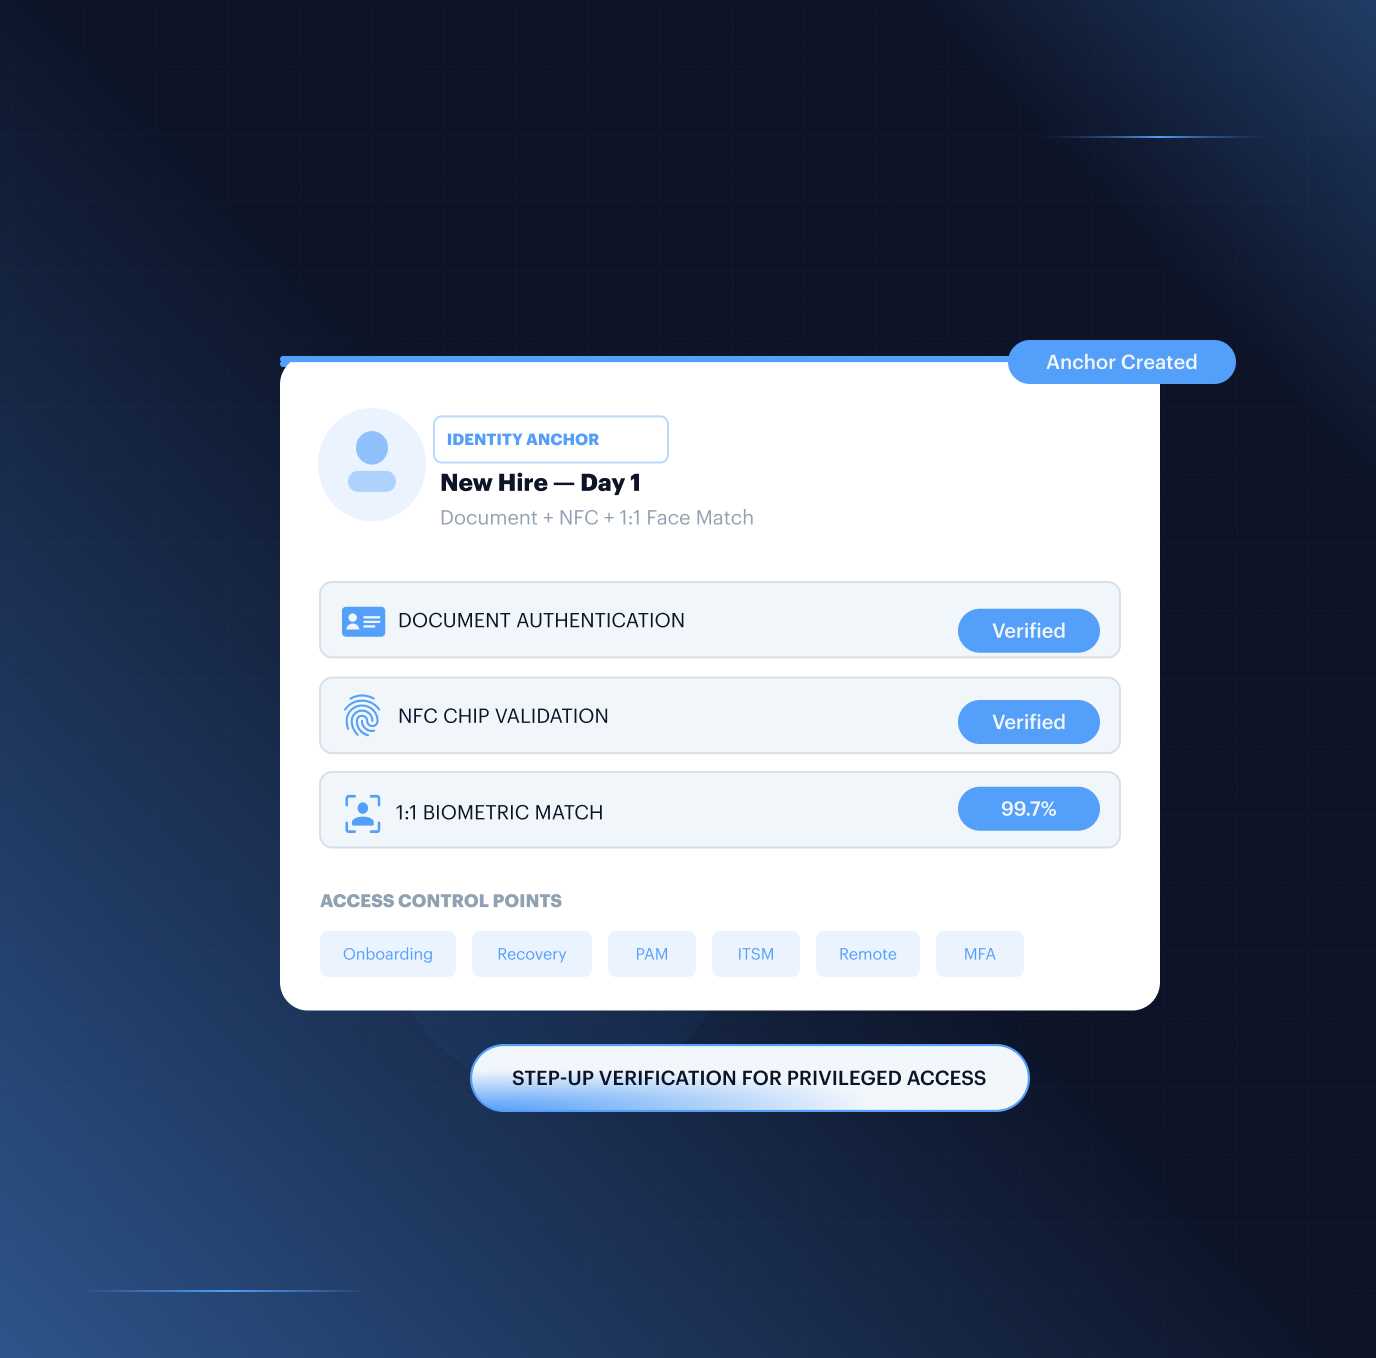
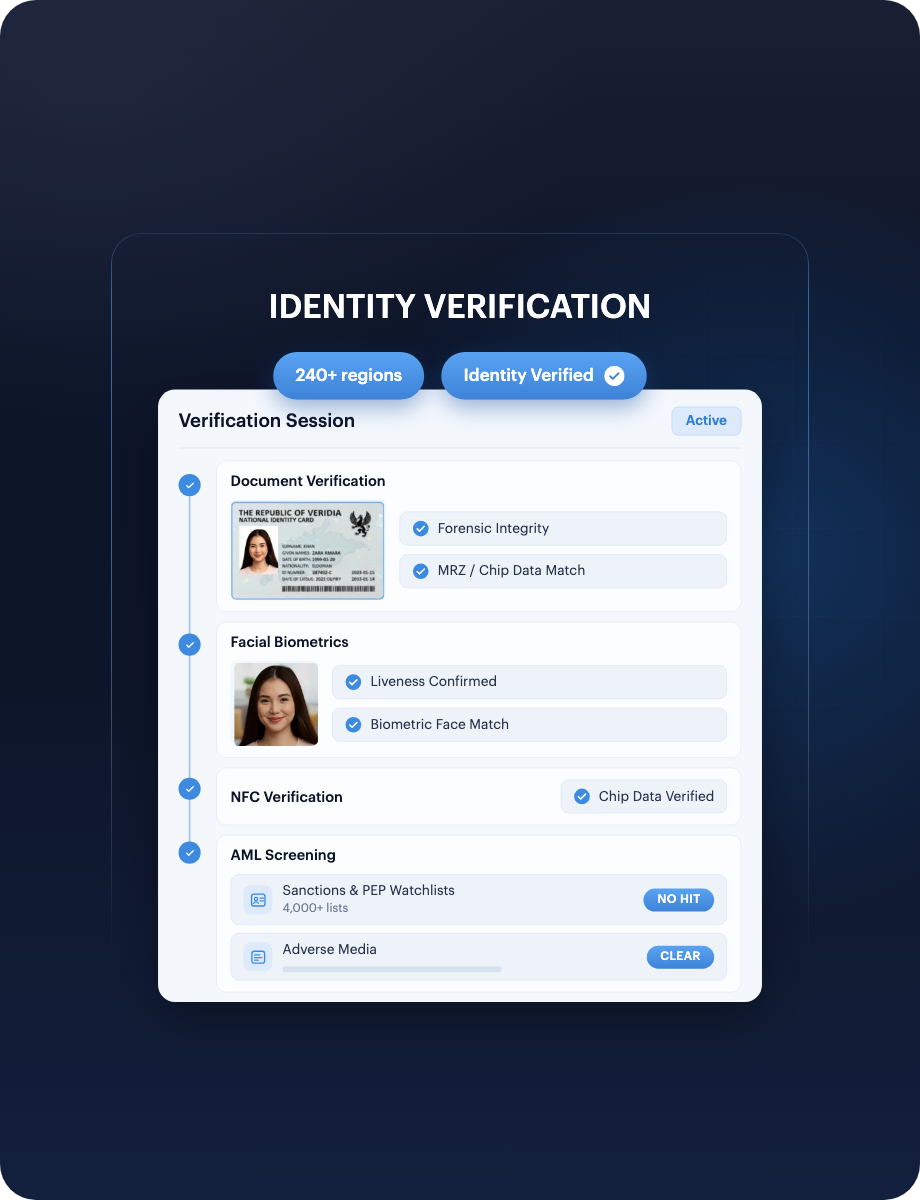
HR systems issue access on day one across distributed and remote workforces. Shufti verifies every joiner through document authentication, NFC chip validation, 1:1 biometric matching, and Right-to-Work / I-9 checks, creating a persistent identity anchor for every future IAM event.

Self-Service Recovery Backed by Verified Identity
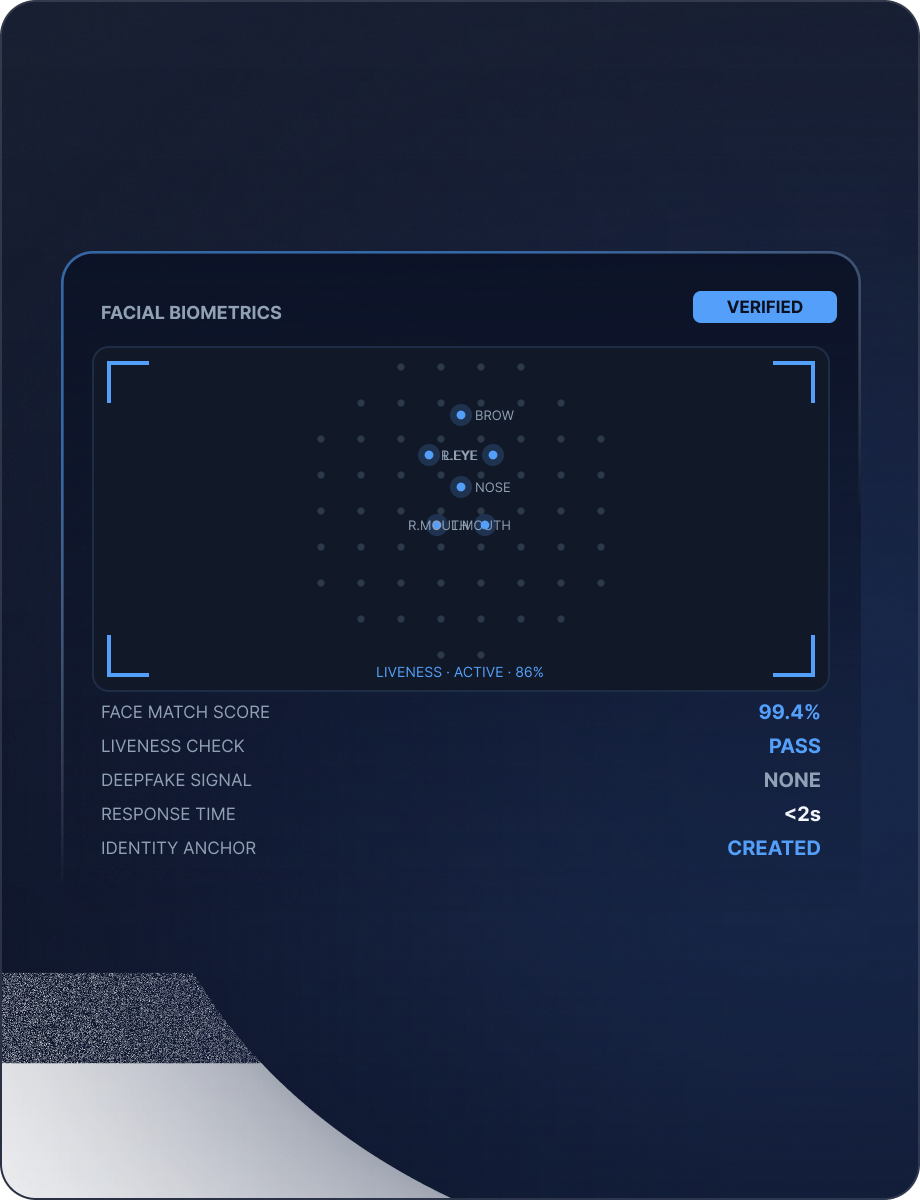
Modern workforce recovery flows require fast and secure identity confirmation. Shufti enables employees to self-recover accounts through a sub-2-second 1:1 face match against the onboarding identity anchor, with deepfake and injection attack resistance built in.

Privileged Access Verified Before Session Approval
Privileged access workflows demand verification of the human behind every high-risk session. Shufti performs inline 1:1 facial verification before privileged access is granted through CyberArk, BeyondTrust, Delinea, or custom PAM integrations, with full SIEM audit visibility.
Explore the Stack
Everything You Need for Workforce Identity Management
Identity Verification for IAM, Built for the Modern Workforce
Verify each new hire at the source, document authenticity, biometric match, NFC chip read, and Right-to-Work in a single pass. The verified record becomes the persistent identity anchor referenced at every IAM event that follows.
-
Confirm real identities in seconds, worldwide.
-
Confirm the joiner is the human on the document. 1:1 face match with liveness and deepfake detection, sub-2-second response. Becomes the identity anchor every later IAM event reuses.
-
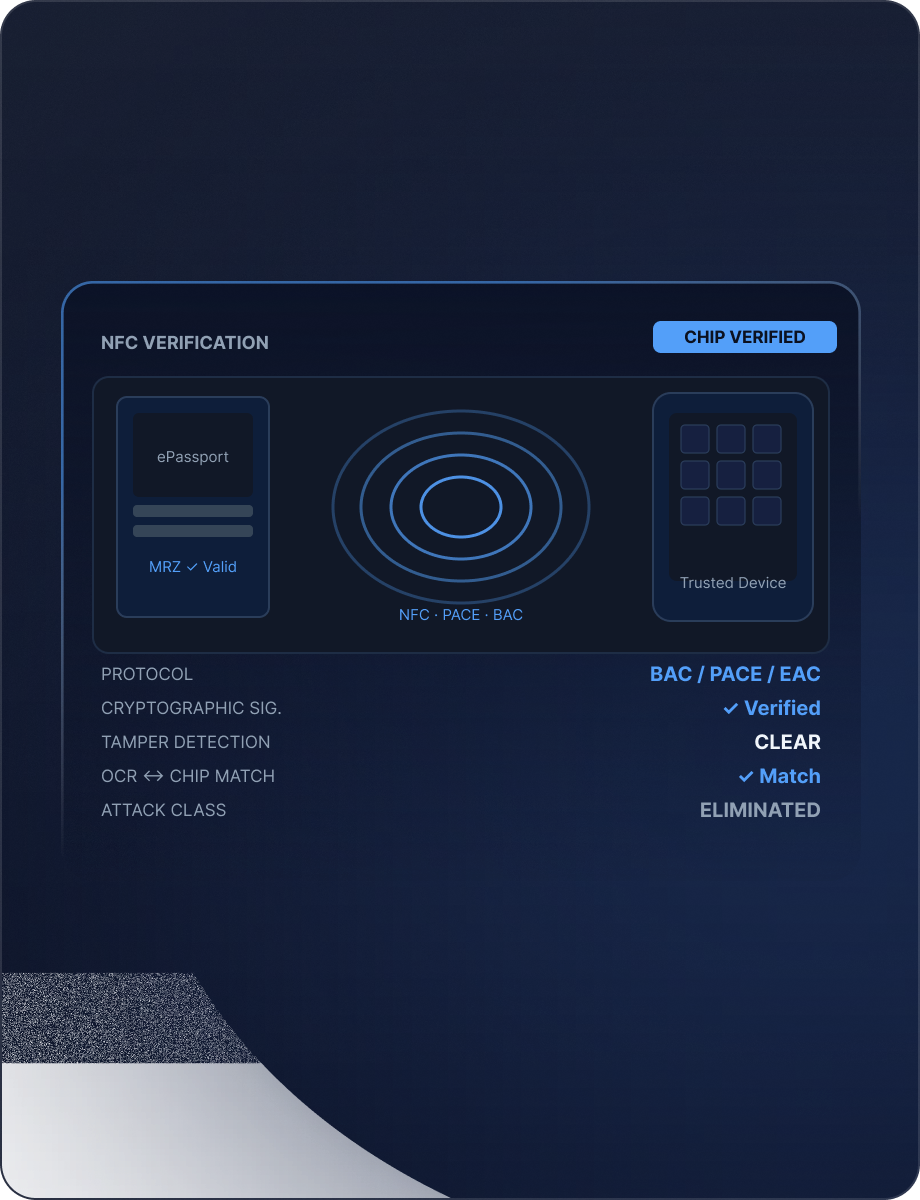
For ePassport and chipped national ID onboarding: read chip-stored data and cryptographically verify it matches OCR-extracted fields. Eliminates document tampering as an attack class.


Persistent Identity Assurance Beyond Initial Login
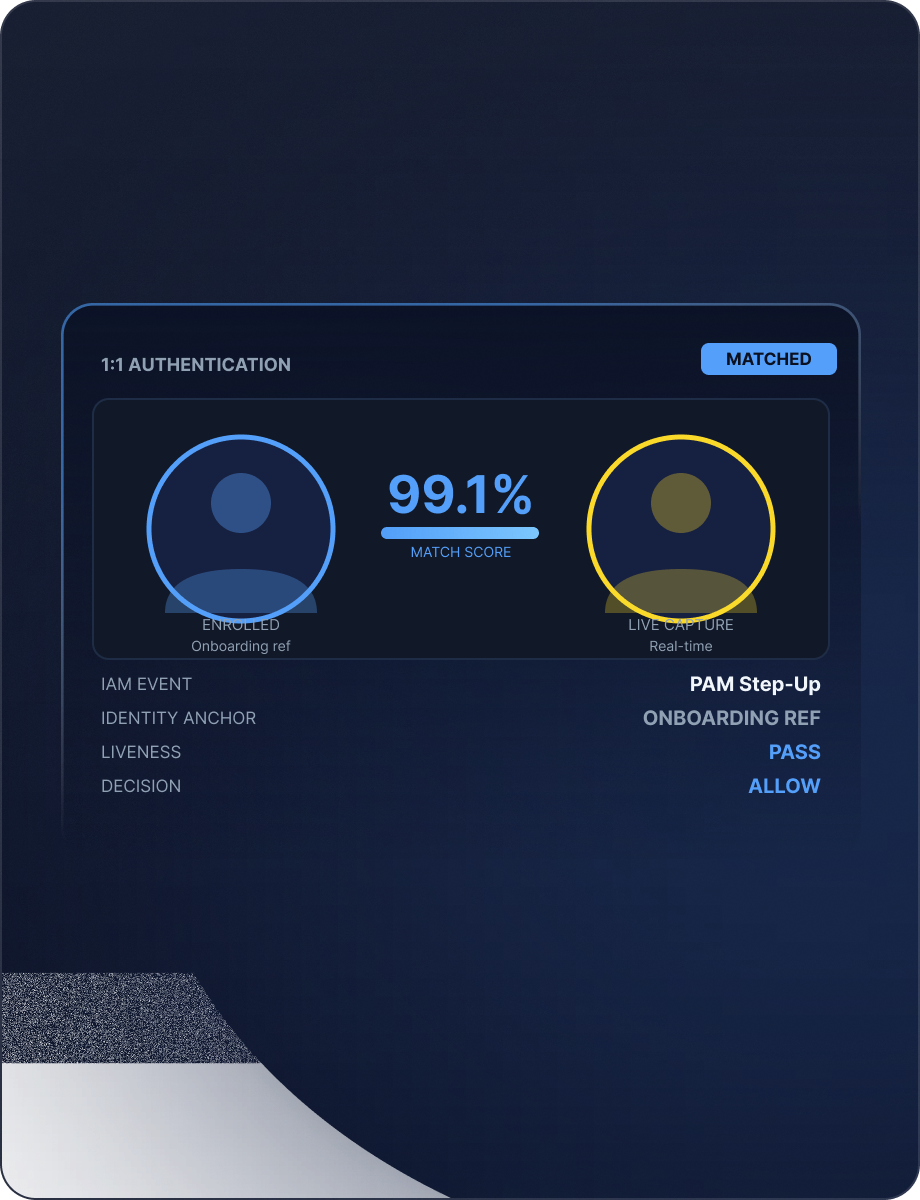
Re-match the live human against the identity anchor at recovery, ServiceNow approvals, remote/VPN, and MFA re-enrolment. Same standard, same record, every time.
-
Re-match the live face against the identity anchor at every IAM access event. The same standard applied at help-desk recovery, PAM step-up, and ServiceNow approval.
-
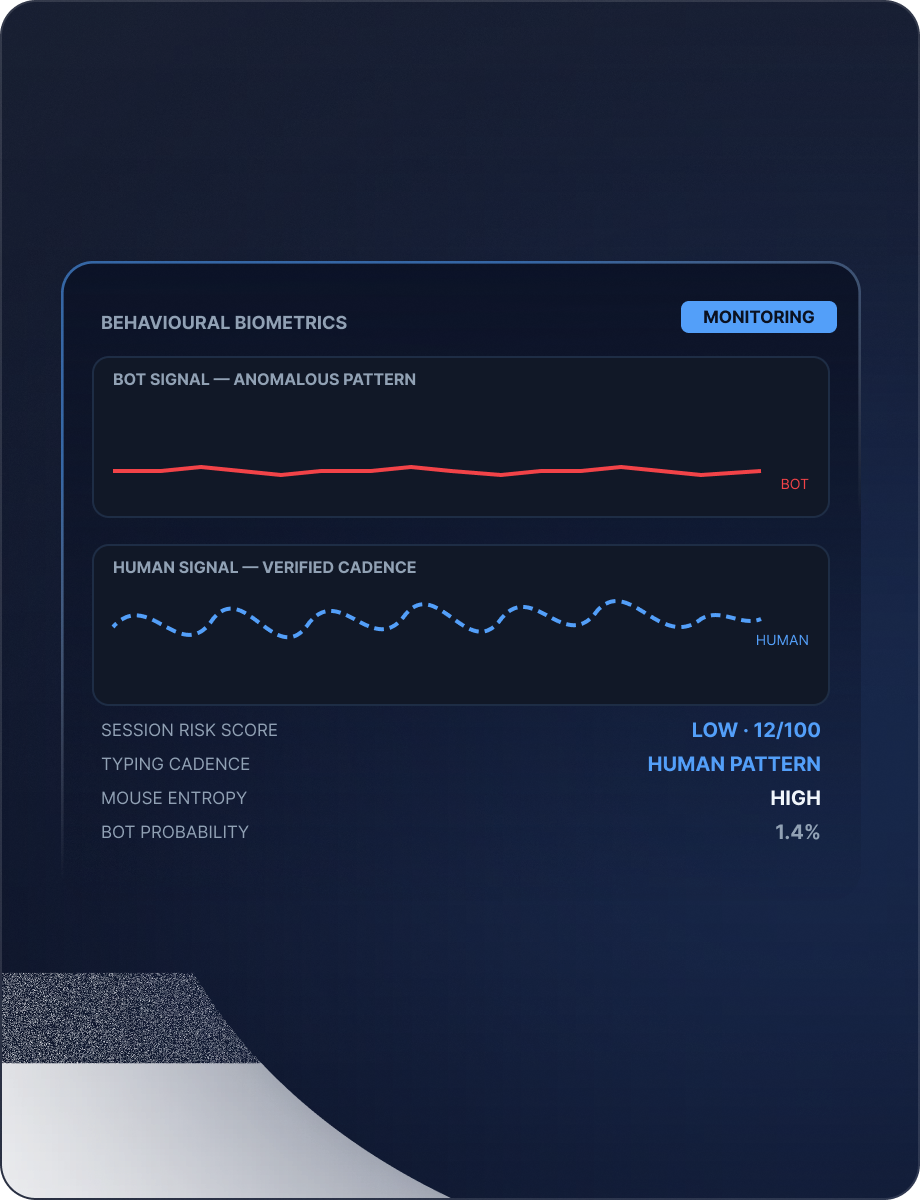
Continuous-signal layer that supports risk scoring on session behaviour. Used as supporting evidence, not the primary verification.
-
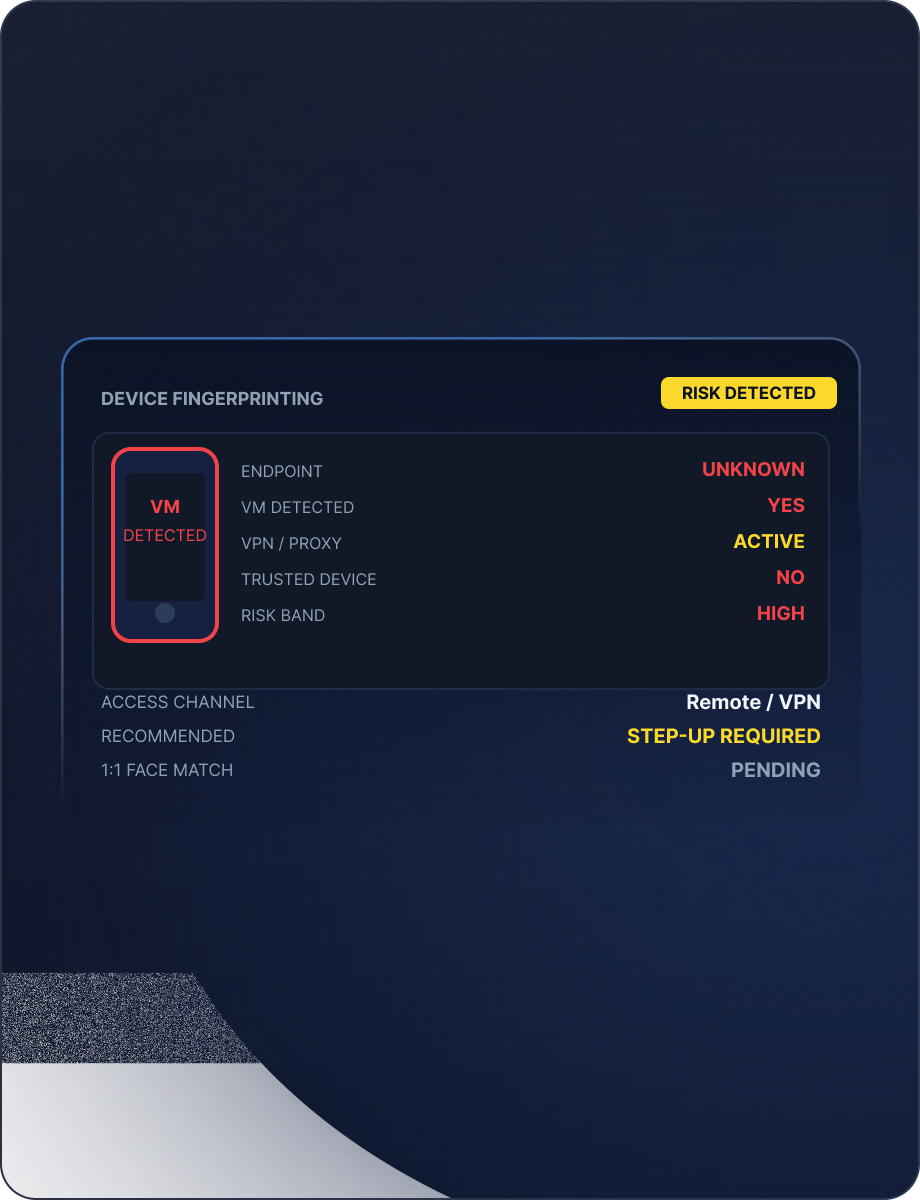
Recognise trusted versus unknown endpoints on remote and VPN access. Combined with the 1:1 face match for risk-proportional friction.
-
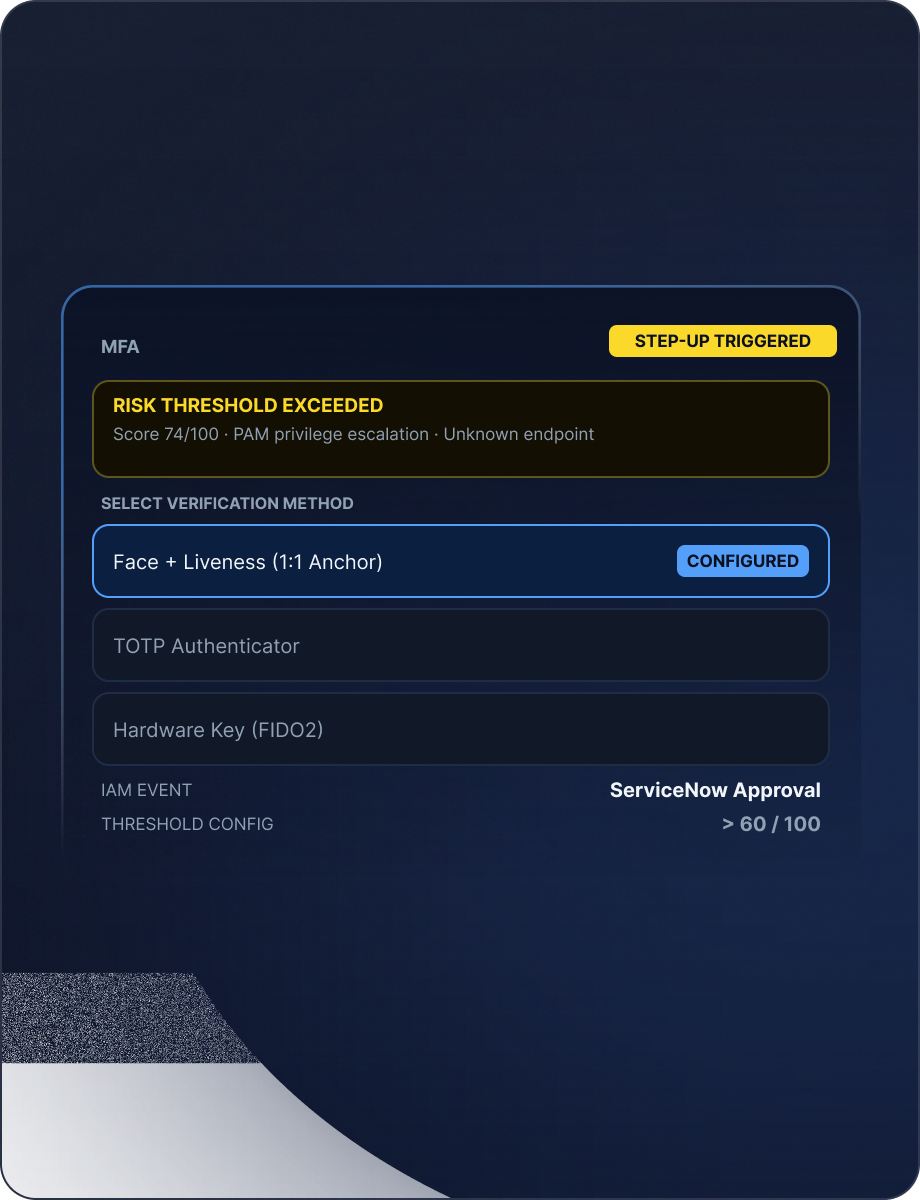
Step-up verification on risk-threshold breach. Configure verification methods (1:1 face match, TOTP, hardware key) and trigger thresholds per IAM event class.

Workforce Access Management Risks Shufti Closes
Deepfake
AI-generated faces and synthetically forged documents bypass legacy liveness checks at scale. Shufti’s passive liveness & document forensics detects synthetic media before it reaches your onboarding flow.
Identity Fraud
Credential theft, blended synthetic identities, and manipulated documents exploit gaps in manual review. Shufti’s layered verification surfaces fraud signals before accounts are created.
Account & Platform Abuse
Duplicate registrations, bot-driven sign-ups, and referral exploits erode platform economics. Shufti links device, identity, and behavioural signals to flag abuse rings at scale.
Transaction & Payment Fraud
False chargeback claims, money mule networks, and sanctions evasion expose your business to financial and regulatory risk. Shufti ties identity verification directly to transaction context.
How Workforce IAM Works
From First Credential to Last Access Event
STEP 01
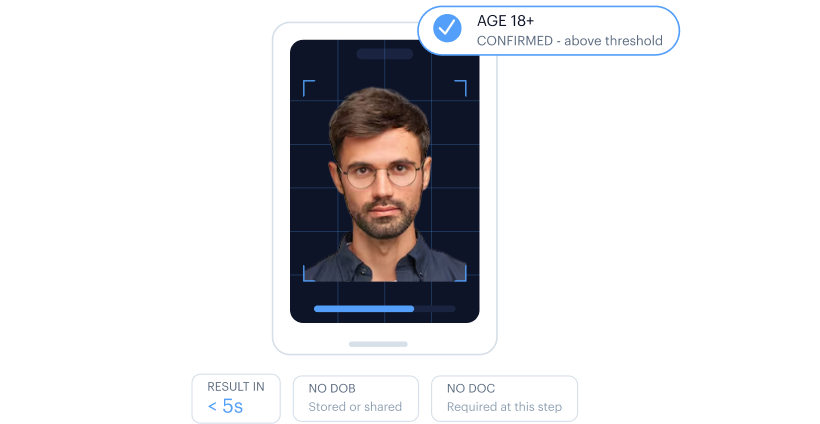
Verify the Joiner, Create the Identity Anchor
Confirm every new hire is who they claim to be before a single credential is issued. Document authentication, NFC chip read, 1:1 face match, and Right-to-Work create a persistent identity anchor for every later IAM event.
STEP 02
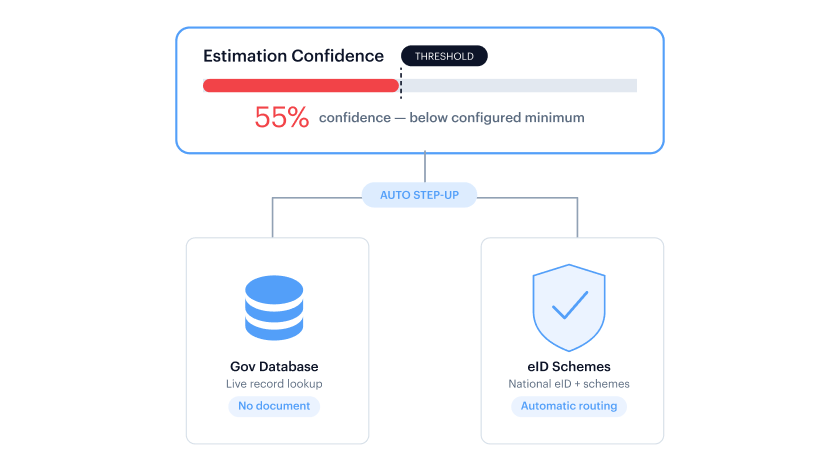
Connect to Your Existing IAM Stack
No rip-and-replace. Shufti integrates with Okta, Entra ID, Ping, CyberArk, BeyondTrust, ServiceNow, and SailPoint through API and SDK, so the identity anchor becomes a signal your existing IdP, PAM, and IGA already trust.
STEP 03
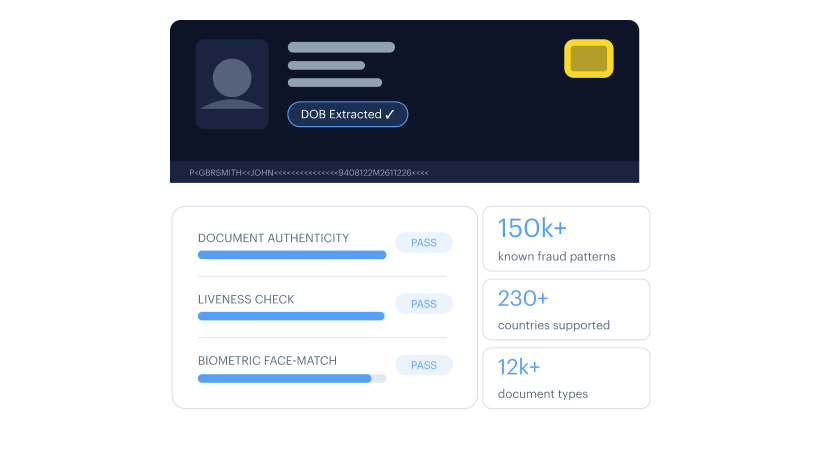
Enforce at Every Access Control Point
The same identity anchor is invoked at every IAM event, joiner onboarding, help-desk recovery, PAM step-up, ServiceNow approvals, remote/VPN access, and MFA re-enrolment, so verification standards never drift between contexts.
STEP 04
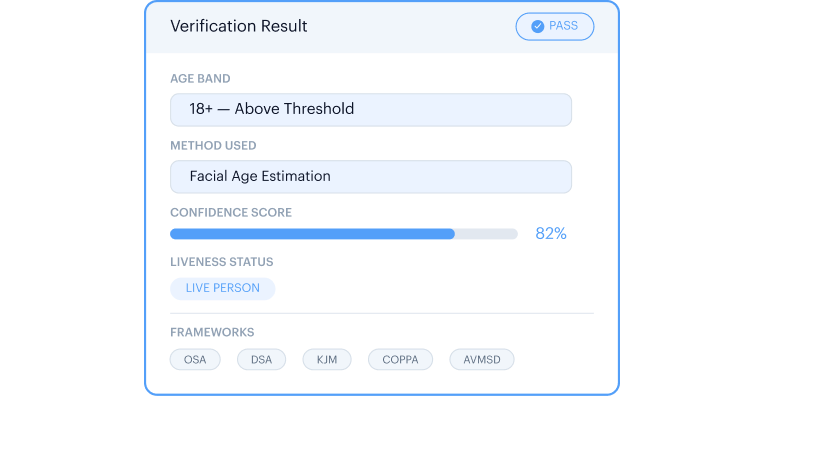
Audit Every Decision
Every verification event returns method used, confidence score, liveness status, decision standard applied, and audit hash, ready for DORA operational resilience evidence and EU AI Act Article 14 oversight, without a separate compliance pipeline.
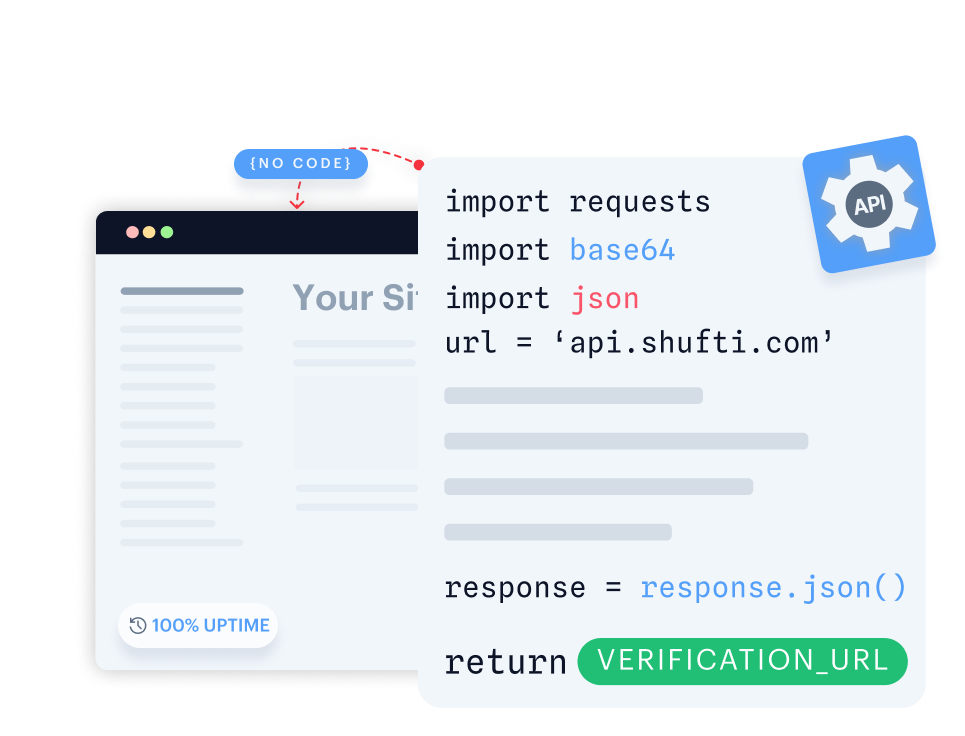
Single API, Seamless Integration
Build fully customisable verification flows with seamless backend integration.
- Gain full control by customising verification flows end-to-end.
- Integrate seamlessly with your backend for quick implementation.
- Design flexible verification journeys tailored to your users.
Launch a native verification experience in your mobile app within minutes.
- Launch native verification within minutes on iOS or Android.
- Use ready-made UI with camera, capture, and real-time feedback.
- Customise flows to fit seamlessly into your mobile app.
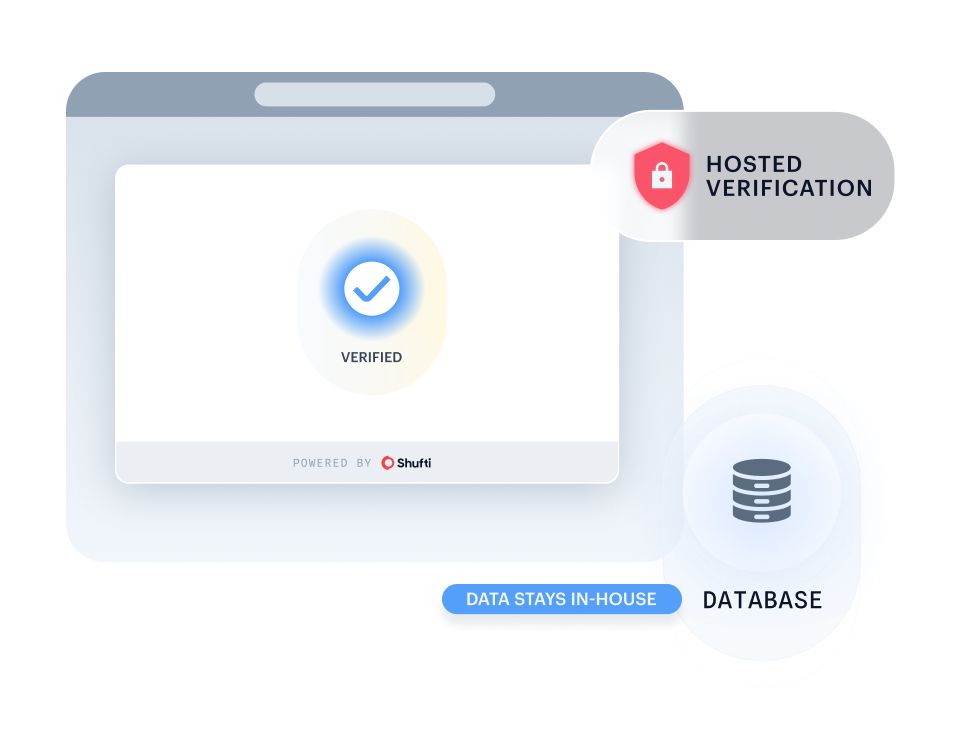
Run Shufti within your own identical-capability infrastructure for maximum data control and privacy.
- Keep all sensitive information in-house to meet strict governance and data residency requirements.
- Keep sensitive information fully private and secure in-house.
- Deploy in highly regulated sectors without compromising compliance.
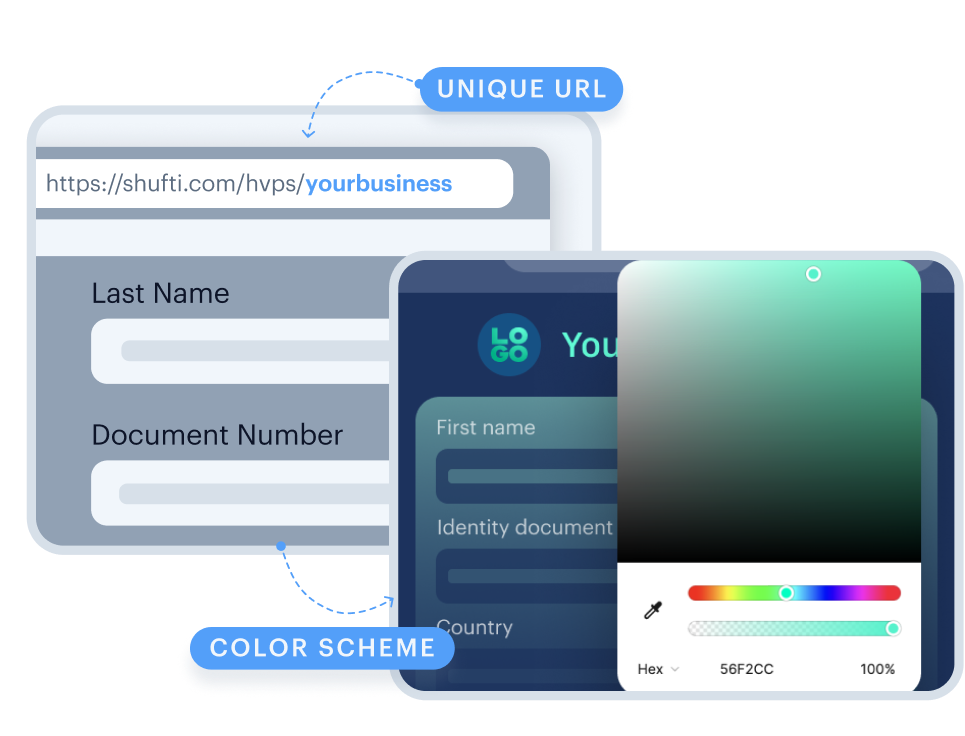
Quickly launch identity verification through a secure, customisable web link, no code required. Learn more.
- Start verifying users instantly with a no-code setup.
- Deliver a consistent identity experience via a link or embedded iframe.
- Deploy quickly via a secure link or embedded iframe.
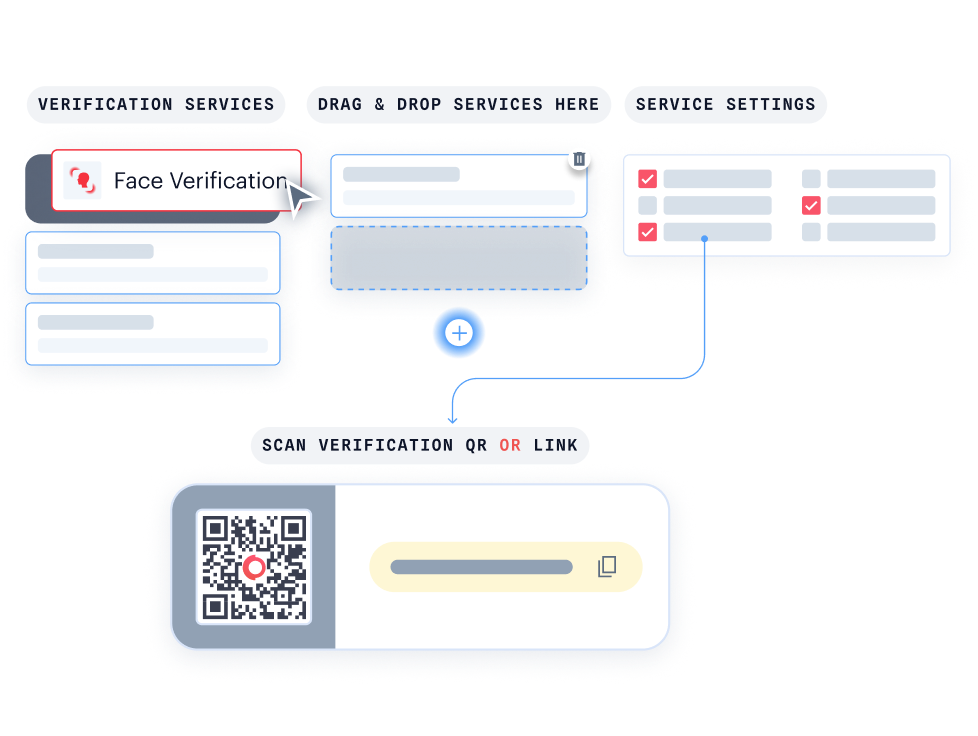
With KYC Journey Builder, create personalised verification journeys without writing a single line of code.
- Customise your journey effortlessly with drag-and-drop functionality.
- Instantly see how your verification flow looks for your users.
- Easily connect with Hosted Verification for a consistent, branded experience.
Recognised by the Analysts Your Committee Trusts
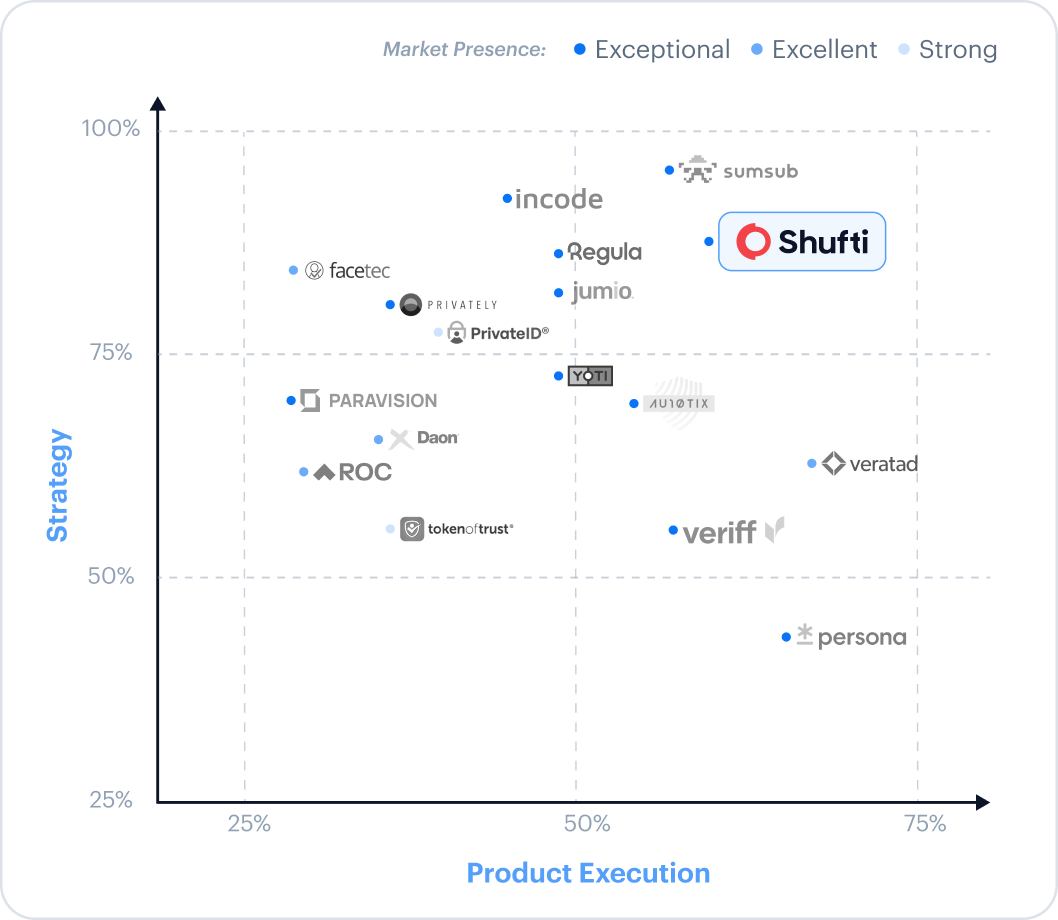
Ranked Exceptional in the Liminal Index 2026 for age estimation
View Report
Differentiated by Gartner on document diversity and country coverage
Read more
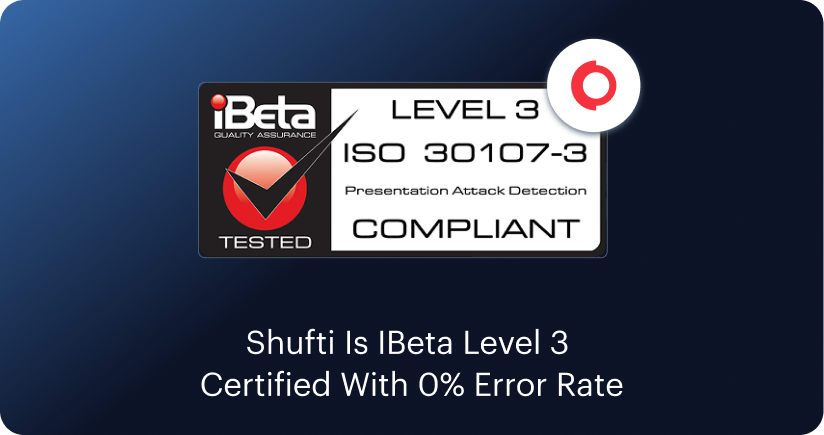
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
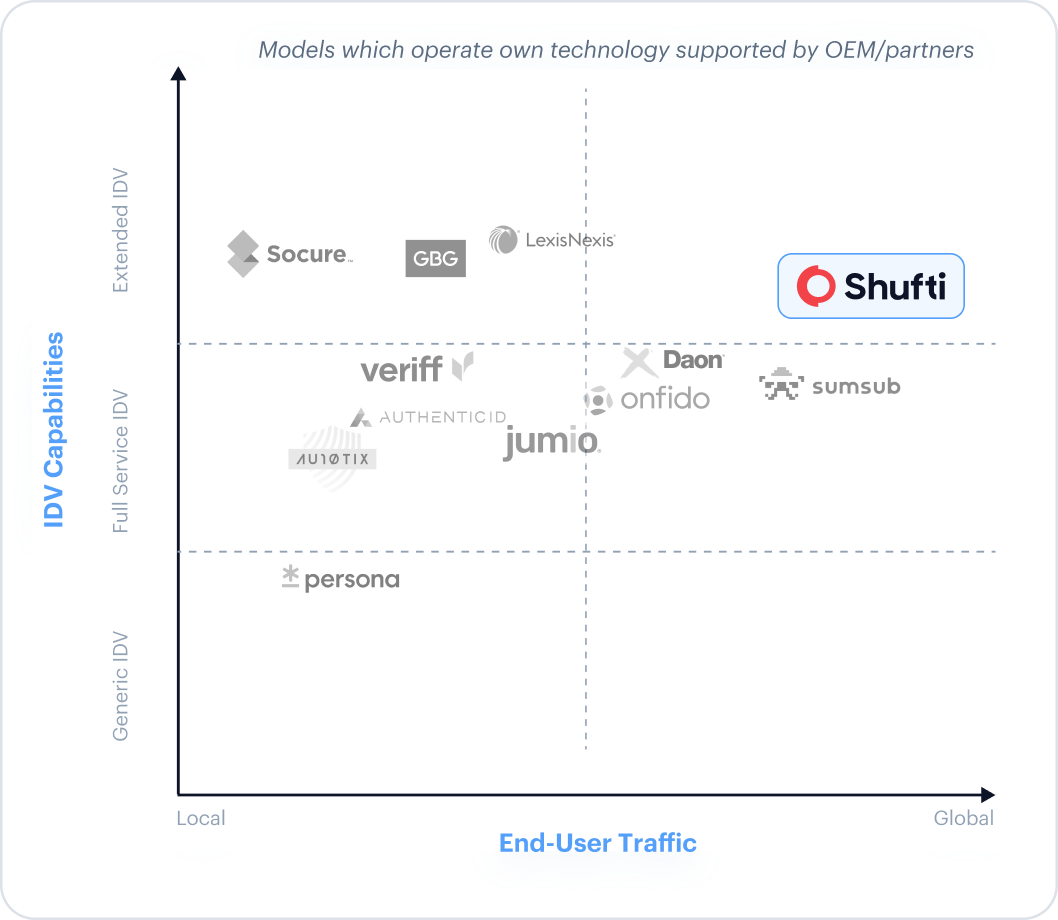
Broadest global reach in the 2025 KuppingerCole Extended IDV report
Download Report
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
Ranked Exceptional for age verification by Liminal Index 2026
View Report
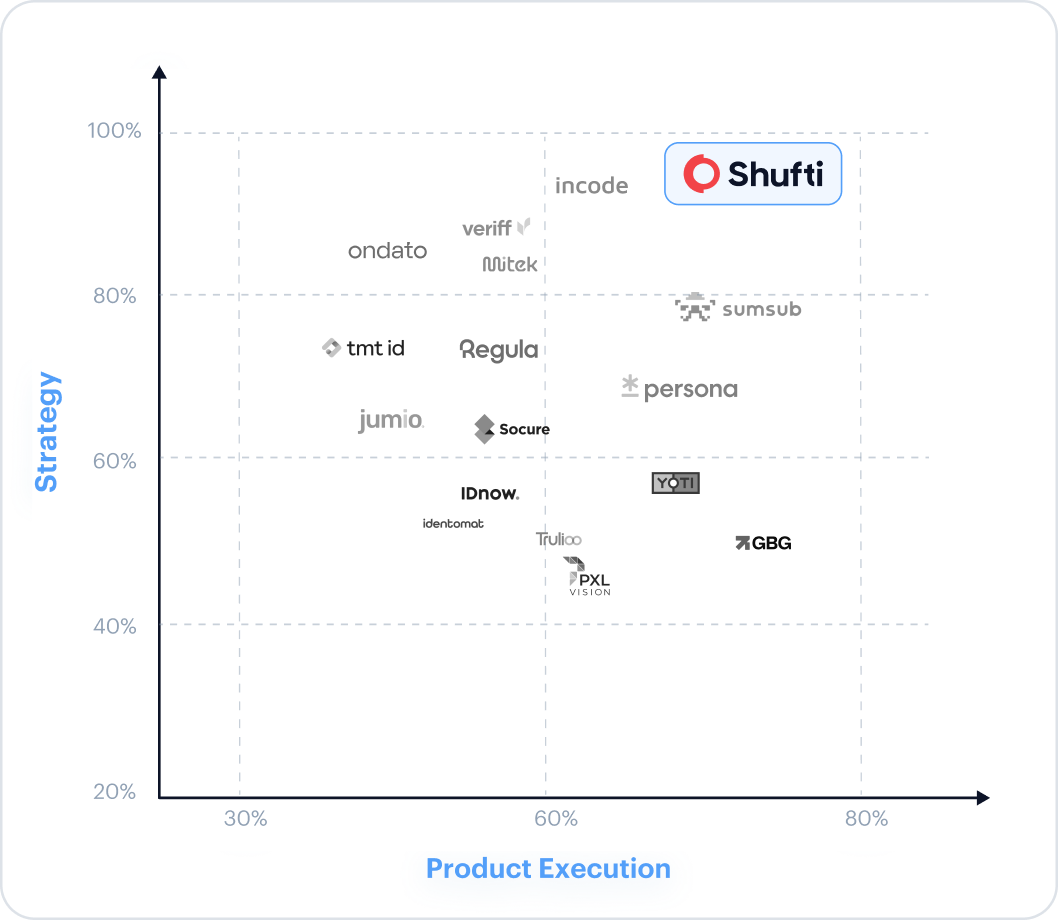
Recognised as a Leader across four G2 Summer 2026 reports
View Report
Built for Your Sector
Workforce Identity Risks Vary by Industry. The Control Point Doesn’t.
Contractor and Gig Workforce Identity, Verified at Every Re-engagement
Verify the seller is real at onboarding, then prevent re-joins with duplicate detection and optional 1:N matching across the marketplace.

Don't just take our word for it, hear from our customers
The Confidence Our Clients Share
The future of digital identity is defined by trust, interoperability, and regulatory alignment, so our partnership with Shufti reinforces DevCode Identity's commitment to supporting our global customers with the most secure, best-in-class, complaints identity verification solutions available today.
Combining our Conversion Driven Compliance Orchestration Platform with Shufti's global KYC and IDV capabilities allows our customers not only to navigate complex regulatory demands but also to maintain a seamless customer onboarding experience with the highest achievable conversion rates.
Shufti gives us verification journeys we can trust across every market we serve. The ability to route players through passive database checks, eID authentication, and full biometric liveness — all behind one API — has reshaped how we think about onboarding compliance.
Their team acts like an extension of ours. When regulators added new requirements across two European markets, Shufti’s journey builder let us adapt in days, not months.
FXBO customers demand speed without compromising AML rigour. Shufti’s eIDV fits exactly there — high-assurance verification for large deposits, invisible background checks for everything else, and one compliance trail across the board.
Integration took a single sprint. The SDK handled the full journey, so our product team stayed focused on trading features instead of building KYC screens.
As a regulated European payments platform, we need identity verification that meets eIDAS 2.0 and AMLD6 without multi-vendor stitching. Shufti delivers both — native eID authentication for high-assurance markets and docless database checks where eIDs don’t reach.
One contract, one audit log. That changes the compliance conversation entirely.
Frequently Asked Questions
What is workforce identity and access management (WIAM)?
Workforce identity and access management (WIAM) proves the human behind an employee credential at every access event, rather than only issuing and governing the credential. Traditional IAM asks "does this account have rights?". WIAM asks "is this the right person?
Does workforce identity management cover contractors, gig workers and third-party staff?
Yes. The identity anchor is human-bound, not employment-status-bound, so contractors and vendor staff are verified on the same standard and re-verified on every re-engagement.
Which workforce access management gaps does identity verification close?
The six control points where the credential is trusted but the human is not: joiner onboarding, help desk recovery, PAM step-up, ITSM approvals, remote and VPN access, and MFA re-enrolment.
Does Shufti replace Okta, Entra ID, Ping, CyberArk, or SailPoint?
No. Shufti is complementary, it adds verified identity to the IAM stack you already run. Your IdP still issues the credential. Your PAM still vaults the secret. Your IGA still governs the entitlement. Shufti confirms the human at the access events where identity matters most.
Which IAM access control points does Shufti cover?
Six: joiner onboarding, help-desk account recovery, privileged access step-up, ServiceNow ITSM approvals, remote / VPN access, and MFA re-enrolment. Each invokes the same verified identity anchor captured at onboarding.
What is the persistent identity anchor?
A single verified identity record created at onboarding from document authenticity, NFC chip read where available, 1:1 face match, and Right-to-Work / I-9. Every later IAM event re-matches the live human against this anchor instead of issuing a fresh challenge.
How is IAD High different from PAD certification?
Presentation Attack Detection (ISO 30107-3) catches printed photos, masks, and replay attacks. Identity Assurance Detection at the High level (CEN/TS 18099) extends to deepfake, generative-AI face, and injection attacks, the contemporary attack surface. Shufti is the first vendor globally certified at IAD High.
How does Shufti satisfy DORA and the EU AI Act?
Operational resilience evidence is captured automatically against every verification event for DORA. EU AI Act Article 14 oversight records, model used, decision standard applied, audit hash, are returned with every API response. No separate compliance pipeline is required.
Does Shufti work with BYOD and unmanaged devices?
Yes. The 1:1 facial match runs in any modern browser or via SDK on managed and unmanaged devices. Device fingerprinting is supported but not required, the identity anchor is human-bound, not device-bound.
How is Shufti priced for workforce IAM?
Per verification event with volume bands. No per-seat licence and no minimum directory size. Favours organisations adding verified identity to existing IAM rather than rebuilding it.
Identify the Gaps in Your Workforce IAM Identity Controls
Most Workforce IAM systems authenticate credentials, not the human behind them. Assess your stack across onboarding, recovery, privileged access, remote login, and MFA reset flows to see where verified identity is missing.