

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


Watchlist Screening
Global Watchlist Screening for Defensible Control
Shufti Watchlist Screening solution screen against 4,000+ global watchlists, refreshed every 15 minutes, with multilingual matching across 80+ languages that surfaces real risk and cuts irrelevant noise across every regulatory authority and enforcement register.
Coverage, Speed, and Control at Scale
lists monitored
multilingual matching
refresh cycle




Screen Every Watchlist With One Defensible Workflow
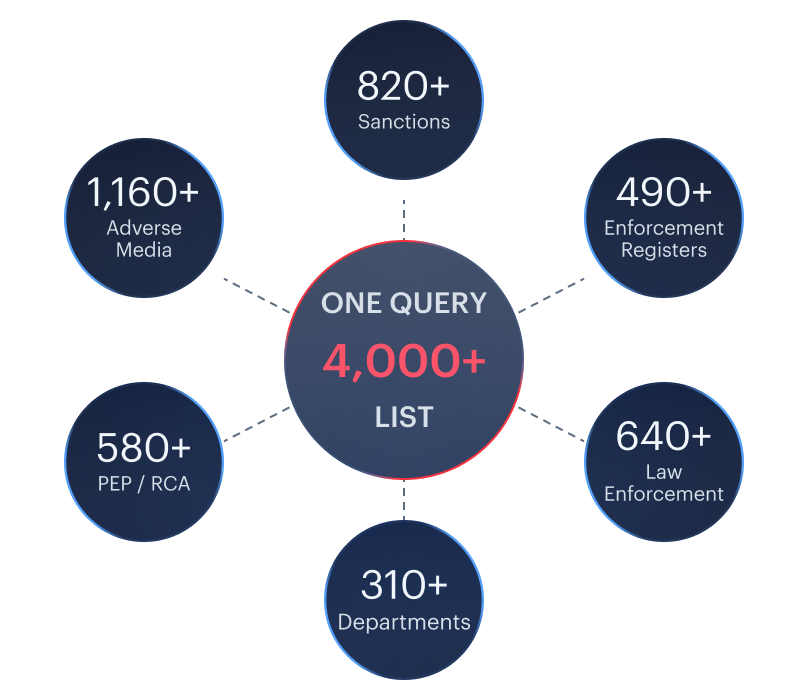
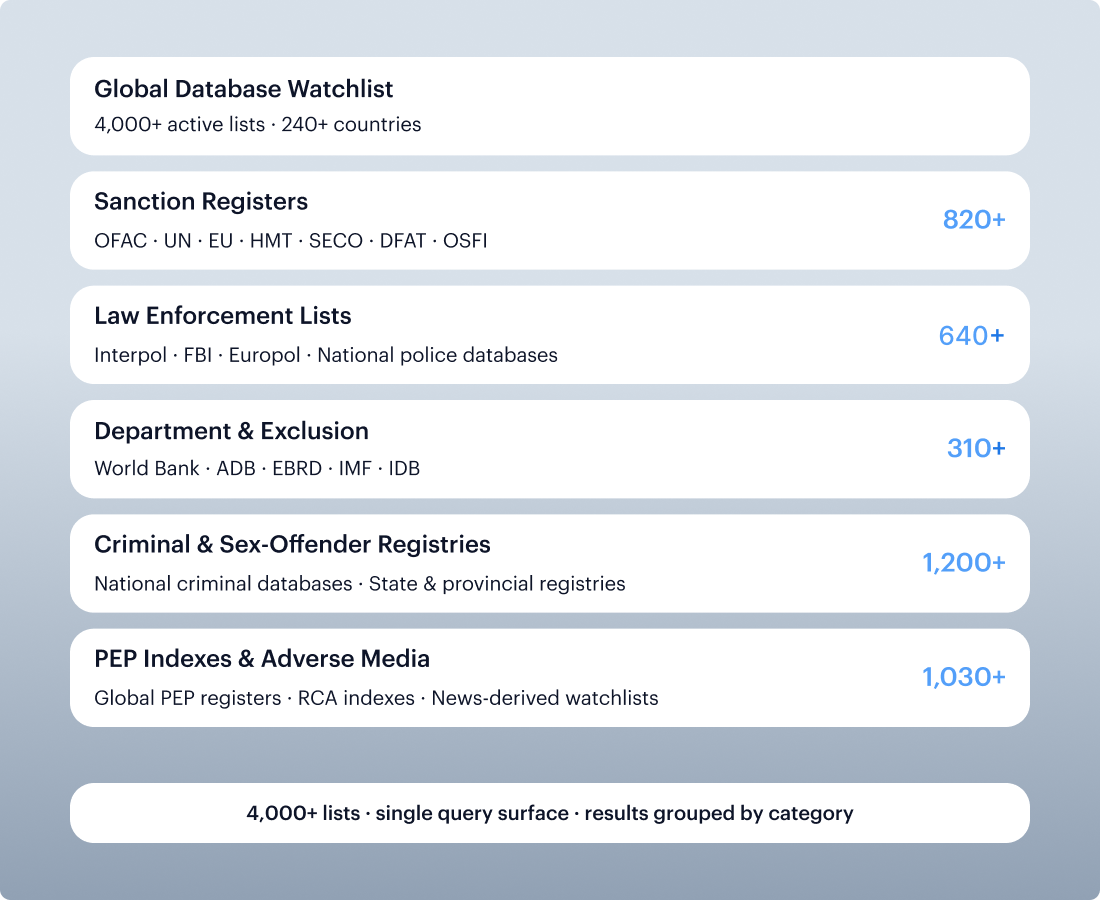
4,000+ Watchlists, One Query
Sanctions, enforcement registers, law-enforcement lists, department lists, PEP indexes, and adverse media, all consolidated into a single screening surface. One query covers every list, results grouped by category.
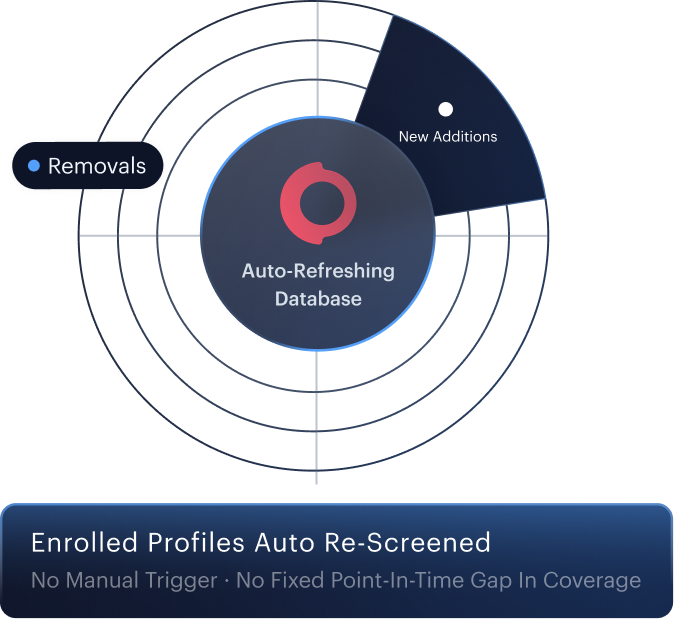
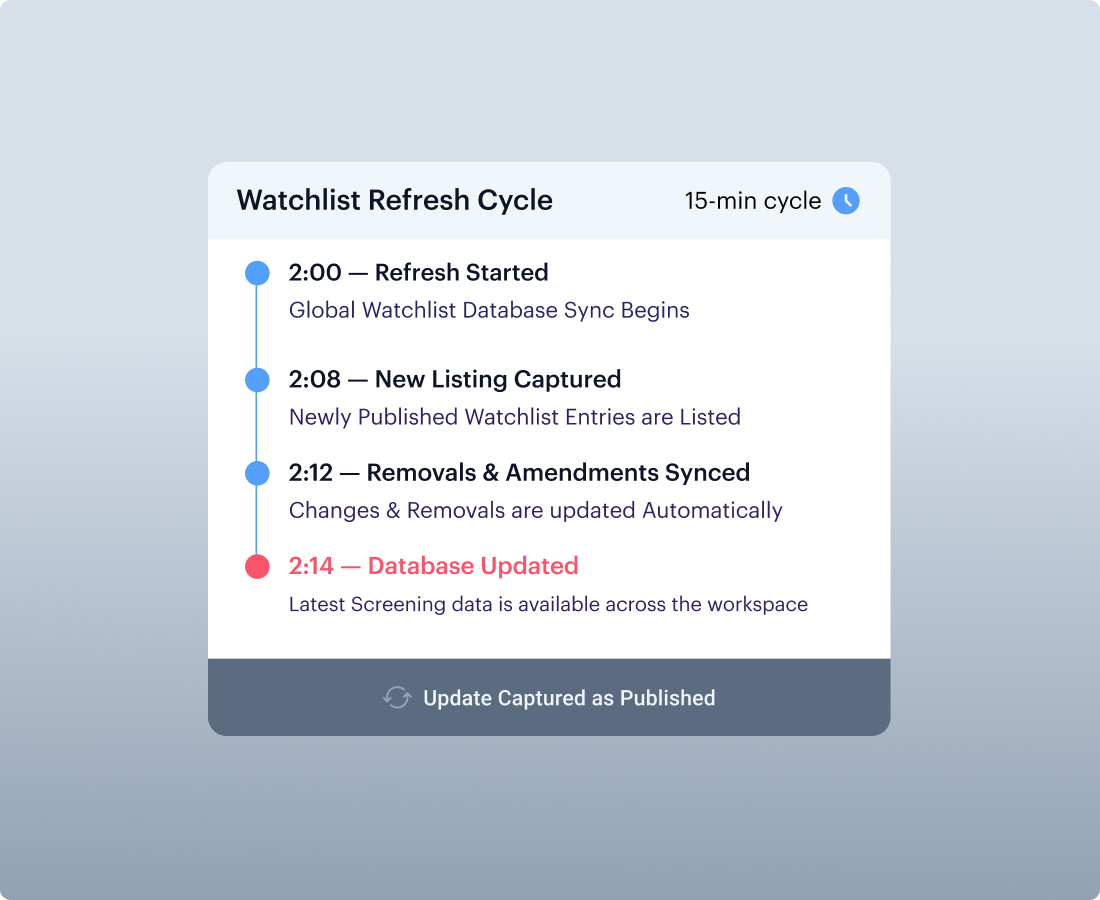
15-Minute Refresh
The full proprietary database refreshes every 15 minutes. New additions, removals, and amendments are captured as published. Enrolled profiles re-screen automatically each cycle.
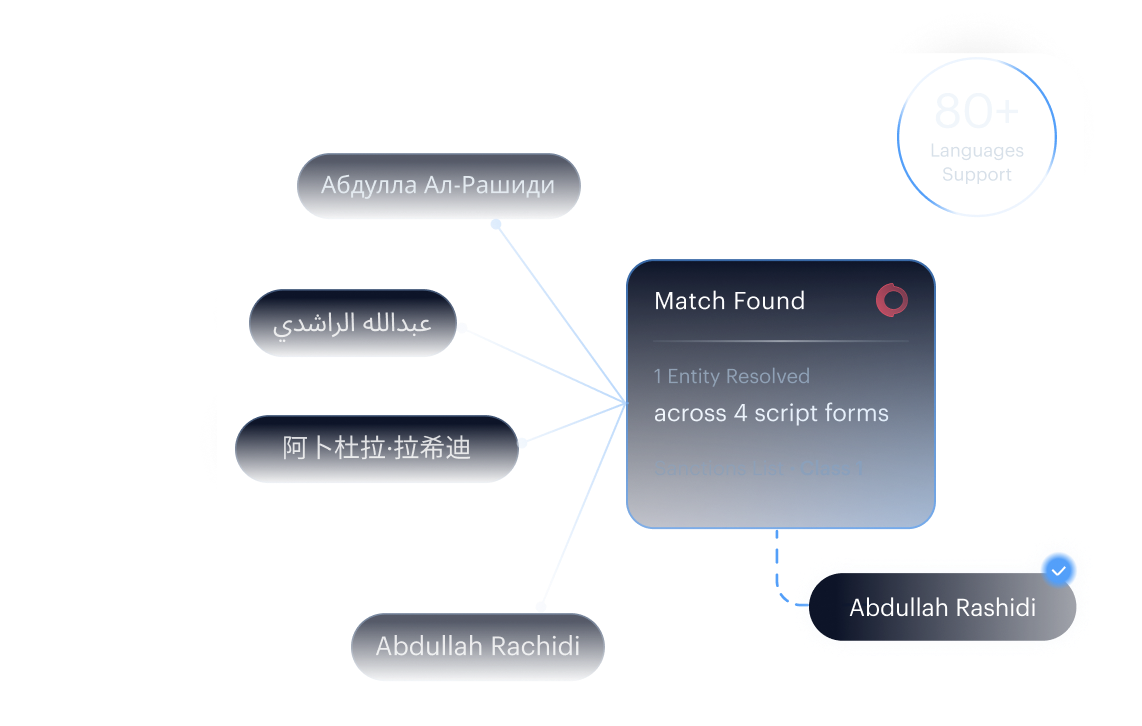
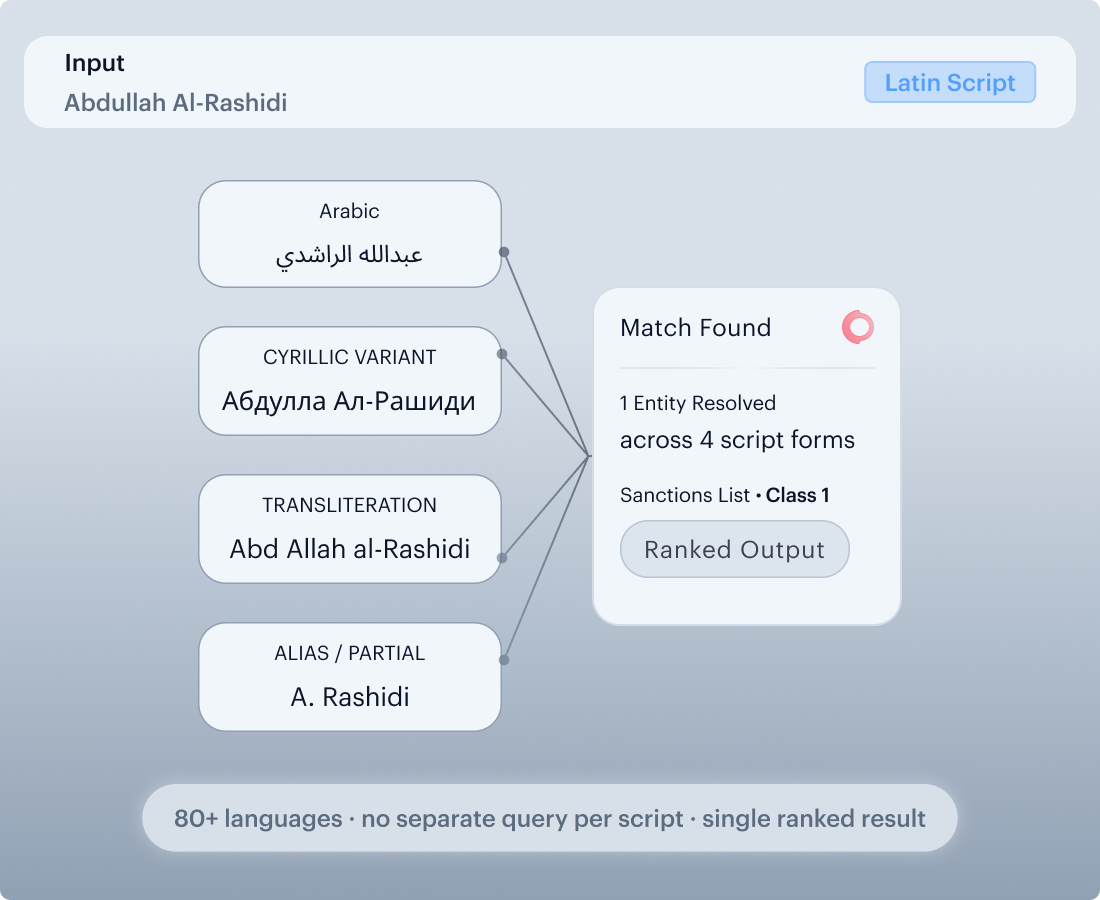
80+ Languages, Cross-Script Matching
Shufti's proprietary fuzzy, phonetic, and transliteration matching across Cyrillic, Arabic, Chinese, Persian, and Latin scripts. A name listed in any script surfaces regardless of input format.
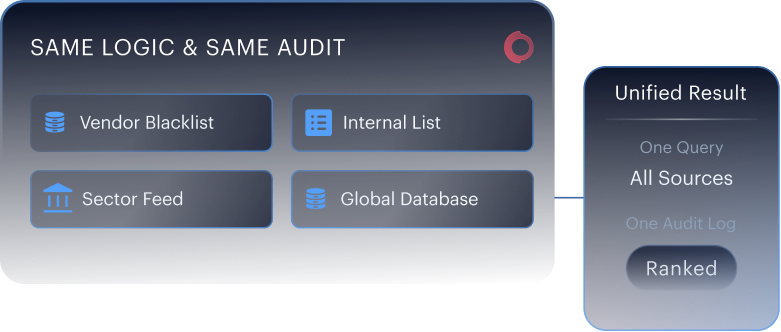
Custom Watchlists Built In
Internal lists, vendor blacklists, and sector-specific feeds ingest into the same workspace. Custom sources screen alongside the global database with the same matching logic and consolidated audit trail.
EXPLORE THE FULL AML SUITE
Watchlist Screening Is One Layer. Here are the Rest
PEP & RCA Screening
Surface political exposure and map relatives and close associates across jurisdictions with real-time multilingual profiling.
Learn More
Adverse Media Screening
Detects negative news across global sources with real-time multilingual monitoring and contextual risk insights.
Learn More
Sanctions Screening
Screen individuals and entities against global sanctions regimes with consolidated coverage and real-time enforcement updates.
Learn MoreG2 Leader in Anti-Money Laundering, Fall 2026
Shufti has earned multiple G2 distinctions in Anti-Money Laundering this season, rated by real compliance users and trusted by regulated firms worldwide.
CORE CAPABILITIES
Screening That Fits Compliance Programmes
Real-Time Coverage and Data
Real Time Global watchlist coverage
Shufti's proprietary watchlist screening software screen against 4,000+ global watchlists, including regulatory enforcement registers, law enforcement lists, debarment lists, criminal records, sex offender registries, and adverse media-derived watchlists.
15-minute refresh cycles
The entire proprietary watchlist database refreshes every 15 minutes. New listings, removals, and amendments are captured as they are published.
Continuous monitoring
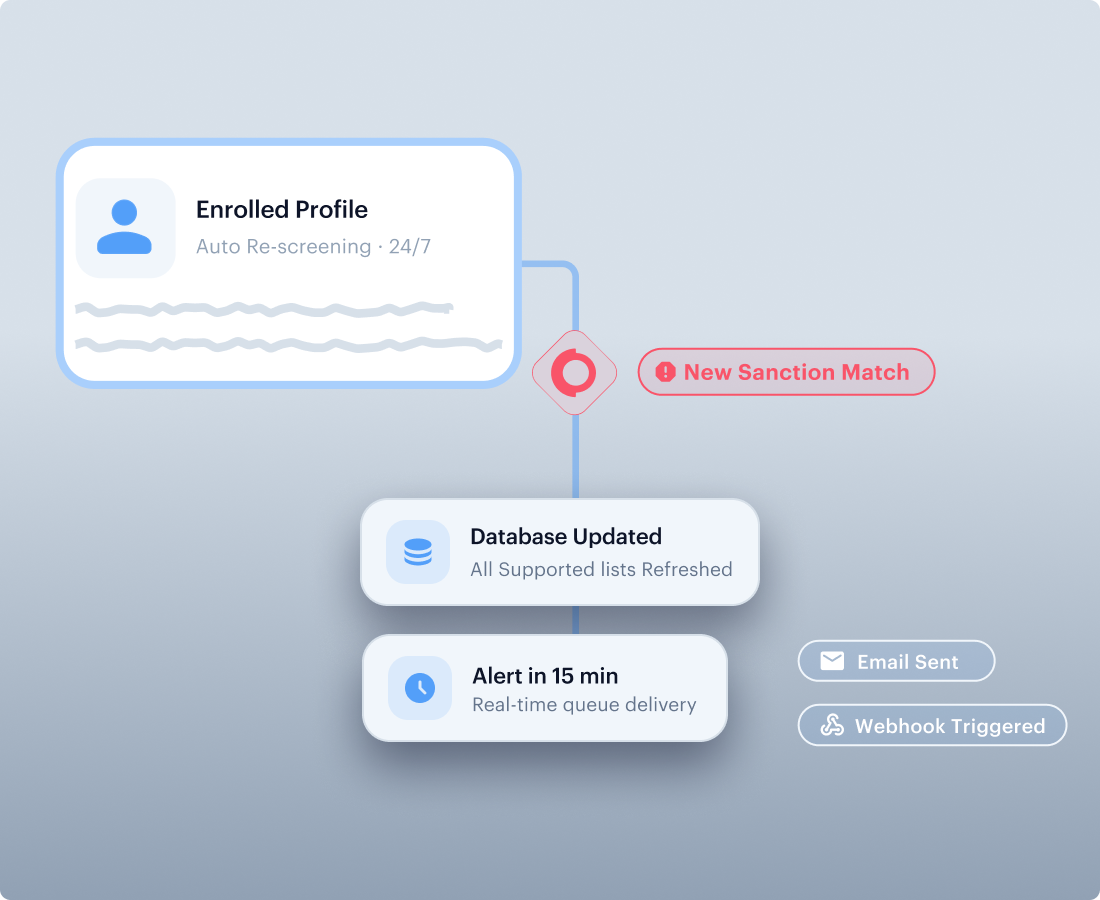
Screening covers Once a profile is enrolled, Shufti re-screens it automatically each time the database updates. Any match against a newly listed party surfaces in the alert queue within 15 minutes, delivered via email or webhook per team configuration., legal entities, vessels, aircraft, and crypto wallets against every supported list type.
Accurate Matching Across Markets
Multilingual cross-script name matching
Name matching operates across 80+ languages and multiple scripts simultaneously. Transliterations, script variants, name order differences, and alias structures resolve without requiring a separate query per language.
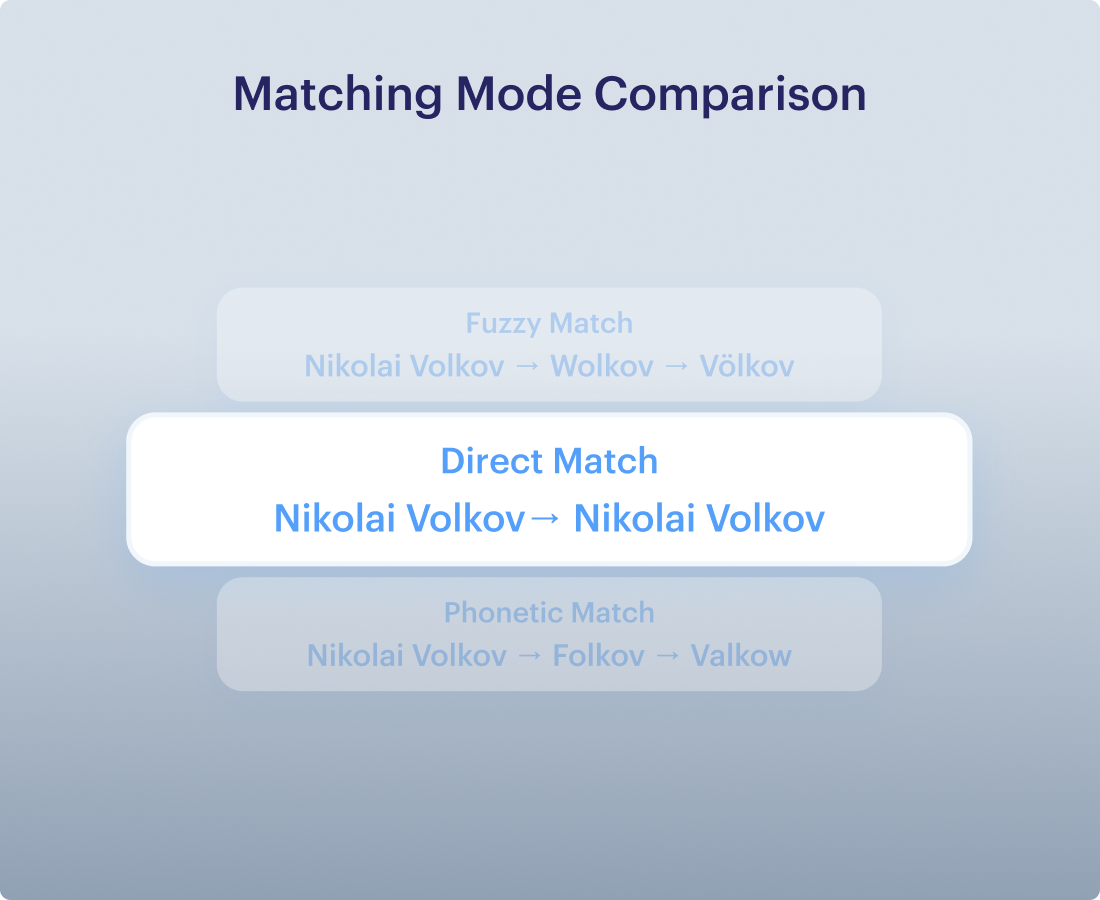
Fuzzy, phonetic, and direct matching modes
Direct matching applies exact or near exact logic for high precision use cases. Fuzzy matching extends coverage to names with spelling variations or incomplete data. Phonetic matching catches similar sounding names written differently.
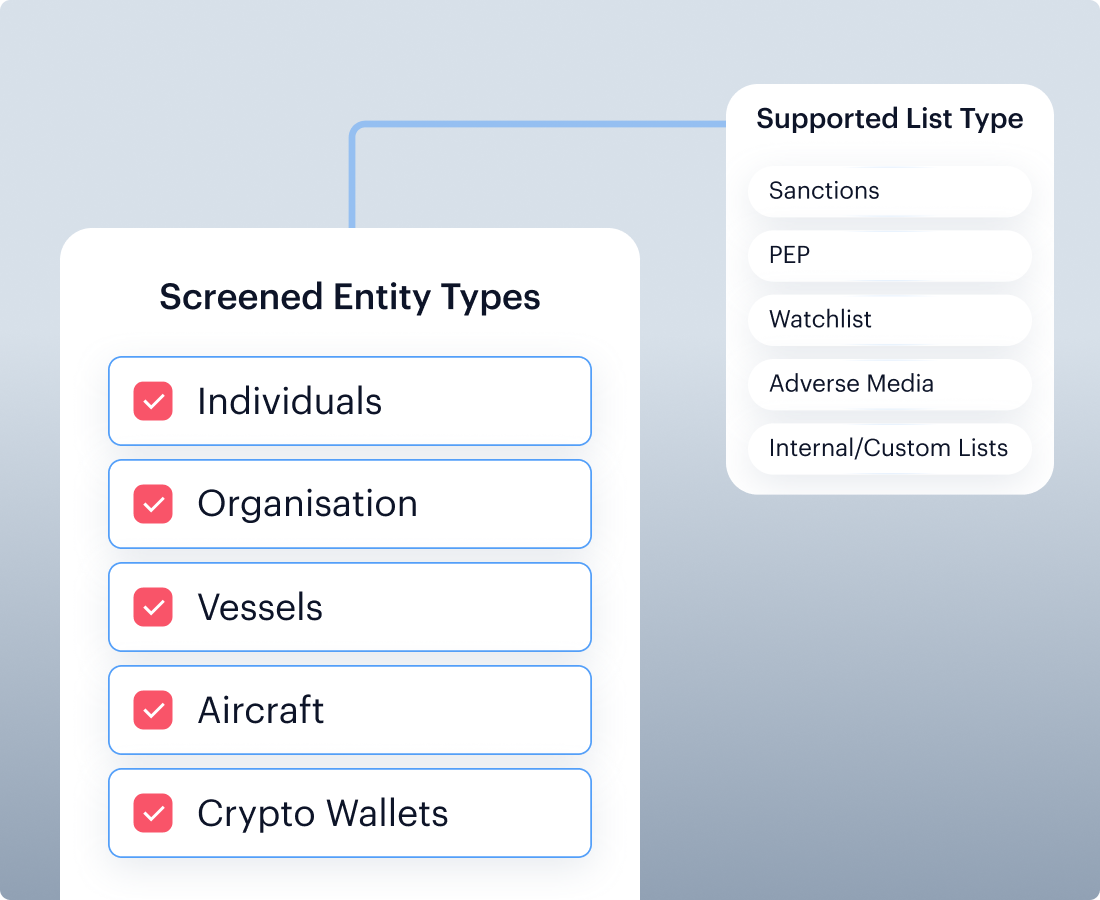
Entity type coverage
Screening covers individuals, legal entities, vessels, aircraft, and crypto wallets against every supported list type.
Configurable Controls and Workflow
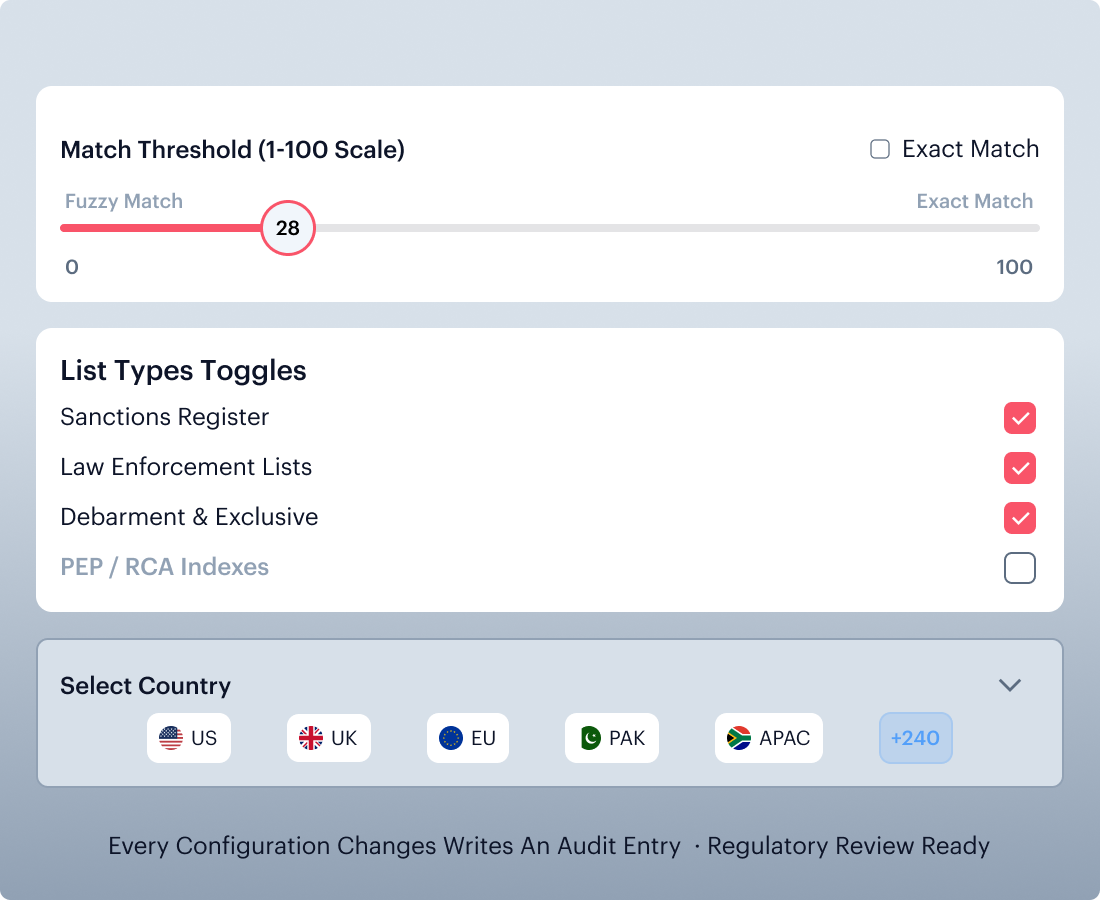
Configurable scoring and threshold controls
The compliance team controls scoring weights, match thresholds on scale, country filters, and list type toggles, tuned by product line, customer segment, or jurisdiction. Every configuration change writes an audit entry, so the calibration trail supports defensible regulatory review.
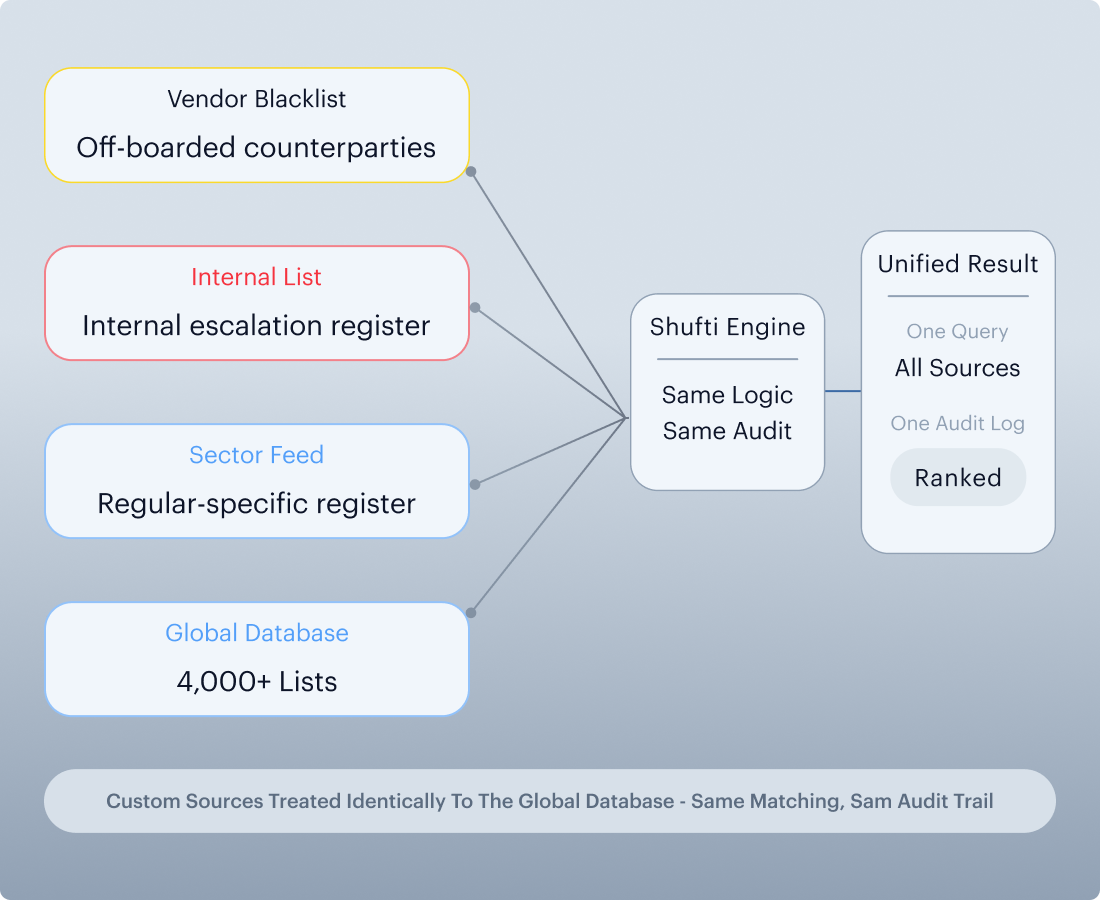
Custom watchlist ingestion
Internal lists, vendor blacklists, regulator specific feeds, and sector specific enforcement databases ingest into the same workspace and appear in every future screen alongside the global database.
Monitoring and Evidence
Case management workspace
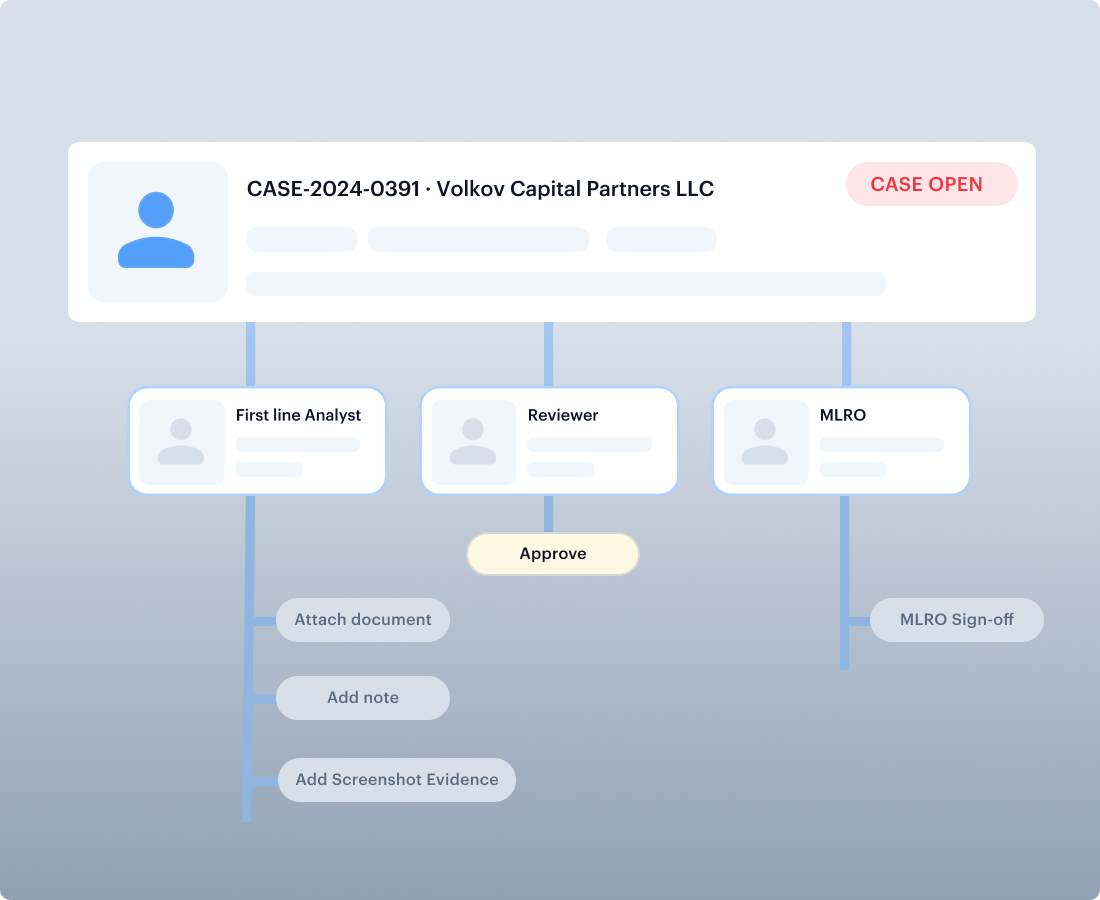
Every alert opens as a case with structured investigation context. Investigators attach documents, correspondence, and screening evidence to a single record; reviewers approve, escalate, or close with written rationale. Role based access separates first line review from MLRO sign off, and every action writes to the consolidated audit trail automatically.
Monitoring cadence that matches risk
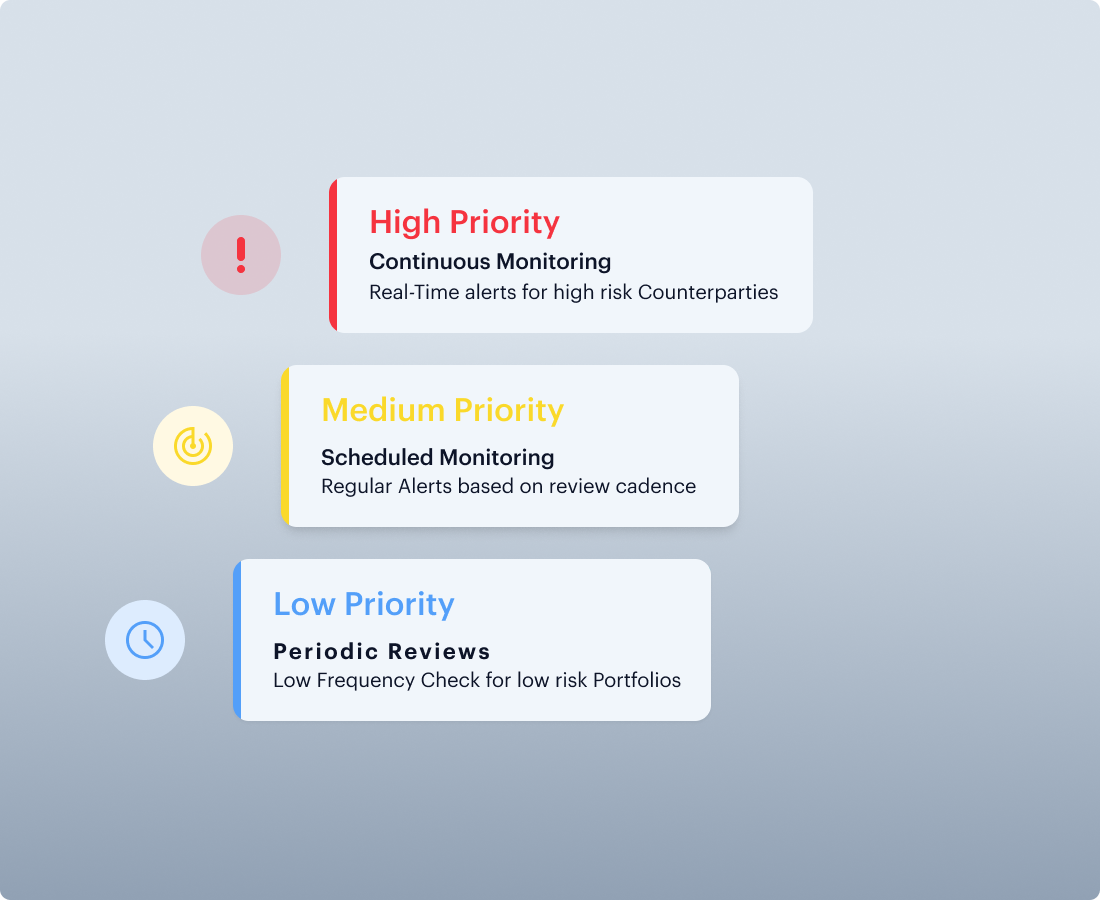
Monitoring durations and alert frequencies match entity risk levels, from continuous monitoring on high risk counterparties to periodic reviews on lower risk portfolios. Configurable per profile, per jurisdiction, per customer segment.
AI Compliance Co-Pilot
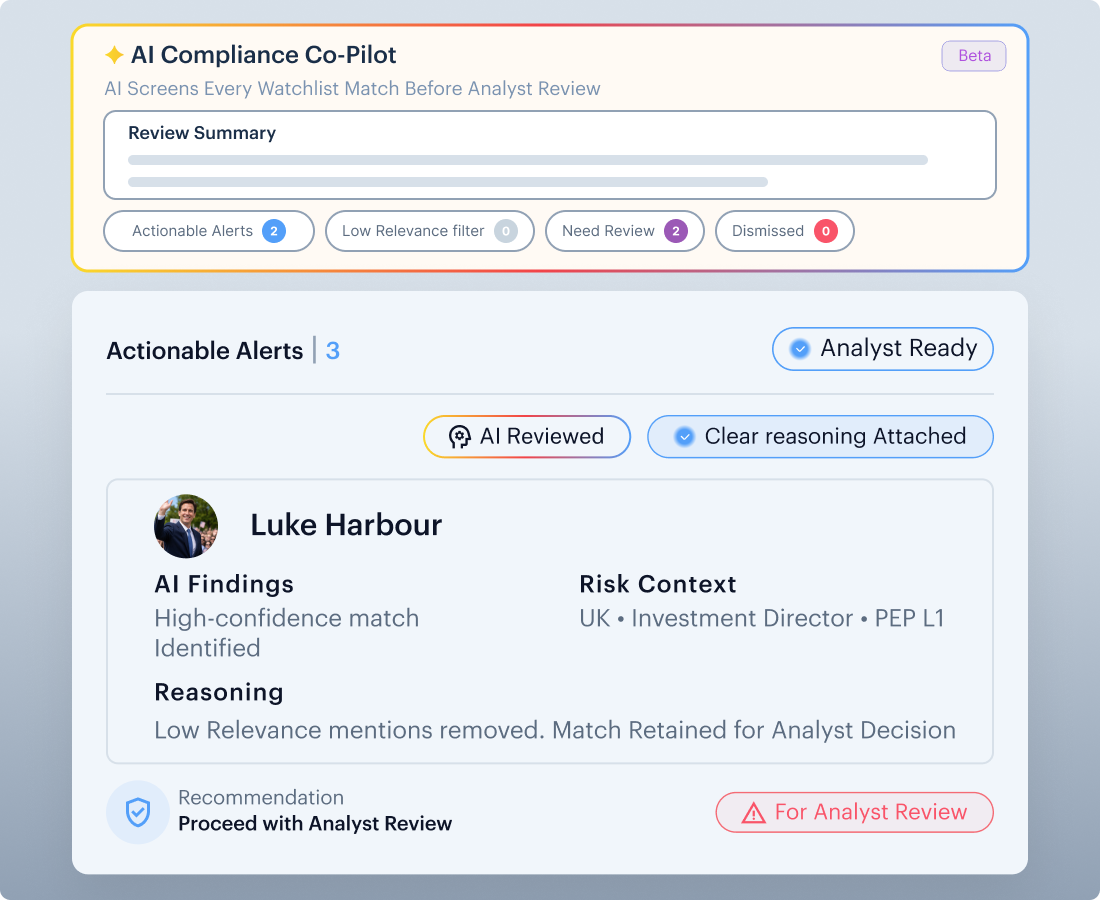
Shufti's proprietary AI layer reads every watchlist match before it reaches an analyst, filtering out low relevance hits. Reviewers see only actionable alerts, with clear reasoning attached to every flag so decisions are fast, consistent, and defensible.
WHERE WATCHLIST SCREENING FITS
Built for Regulated and High-Risk Businesses
Trusted Sellers, Cleared Against Every Authority
Seller cycling and counterfeit networks slip past name-only screening when watchlist coverage is shallow. Shufti's broad watchlist database and custom internal-list ingestion catch indirect exposure and block off-boarded sellers from re-entering.

Don’t just take our word for it, hear from our customers
The Confidence Our Clients Share
The future of digital identity is defined by trust, interoperability, and regulatory alignment, so our partnership with Shufti reinforces DevCode Identity’s commitment to supporting our global customers with the most secure, best-in-class, compliant identity verification solutions available today.
Combining our Conversion Driven Compliance Orchestration Platform with Shufti’s global KYC and IDV capabilities allows our customers not only to navigate complex regulatory demands but also to maintain a seamless customer onboarding experience with the highest achievable conversion rates.
We’re proud to continue our partnership with Shufti as we expand into new jurisdictions.
Shufti’s verification technology not only strengthens our compliance framework but also ensures our players enjoy a smooth, secure onboarding experience.
We aim to offer our clients and their traders the very best tools with which to do their jobs, we’re excited to be able to work with Shufti.
They’re a leading company, and we’re looking forward to offering their solutions to our clients through our CRM.
The relationship with Shufti was born out of frustration with an existing provider, so we started our discussion with Shufti.
The response time was excellent, from the start of speaking to sales to getting up and running with the demo.
EVERYTHING YOU NEED TO KNOW IN ONE PLACE
Frequently Asked Questions
What is watchlist screening?
Watchlist screening checks individuals, businesses, vessels, aircraft, and crypto wallets against global enforcement registers, regulatory action lists, debarment lists, criminal records, sex-offender registries, and adverse-media-derived watchlists to identify high-risk parties before they access a service or complete a transaction.
How does Shufti differ from keyword or link-list watchlist tools?
Basic tools return link lists or yes-no hit outputs. Shufti structures each match into decision-ready attributes including entity matching, list-type categorisation, match-logic explanation, and a full decision export, so reviewers assess exposure faster and more consistently.
Which watchlists does Shufti cover?
Coverage spans 4000+ global watchlists across regulatory enforcement registers, law-enforcement lists, debarment lists, criminal records, sex-offender registries, PEP and RCA indexes, and adverse-media-derived sources, drawn from authorities in 240+ regions actively processed. A full coverage matrix is available on request.
How often does Shufti update its watchlist data?
The database refreshes every 15 minutes, capturing new listings, amendments, and removals from every source as they are published. Continuous monitoring re-screens enrolled profiles each cycle, so the control runs continuously rather than at fixed points in time.
How does multilingual and cross-script matching work?
Fuzzy, phonetic, and transliteration matching run in parallel across 80+ languages and multiple scripts. A Cyrillic, Arabic, Chinese, or Persian listing surfaces the same record as its Latin-script transliteration. Results consolidate into a single ranked output per subject.
Can internal watchlists be combined with the Shufti database?
Yes. Internal lists, vendor blacklists, regulator-specific feeds, and sector-specific enforcement databases ingest into the same workspace and appear in every future screen alongside the global database, with the same matching logic and audit trail.
Can Shufti screen entities, vessels, aircraft, and crypto wallets?
Yes. Coverage extends to natural persons, legal entities, vessels and aircraft, and crypto wallet addresses, against every supported list type.
How are false positives controlled?
Configurable scoring weights, match thresholds on a 1 to 100 scale, country filters, and list-type controls allow compliance teams to tune sensitivity to internal policy. Cross-script multilingual matching and identity-aware logic reduce noise at the script level before it reaches the review queue.
Where is client data processed, and what privacy controls apply?
Processing regions are available in the EU, UK, US, APAC, and MENA, selectable at onboarding. Retention is client-configurable per data category. DPA and SCC or UK IDTA are available on request. Shufti is certified to ISO 27001:2022 and operates in line with GDPR requirements.
Ready To Strengthen Watchlist Controls
See how 4000+ watchlist coverage, 15-minute refresh, and multilingual matching help your team catch real risk faster.
Your Go-To for KYC/AML & Fraud
Resources
11 August, 2026
Shufti's 2026 Context Gap in AML Risk Assessment
False positives climb when alerts reach analysts without context. Shufti's 2026 report shows what customer and risk context teams need to decide cases much faster.
Guide