AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


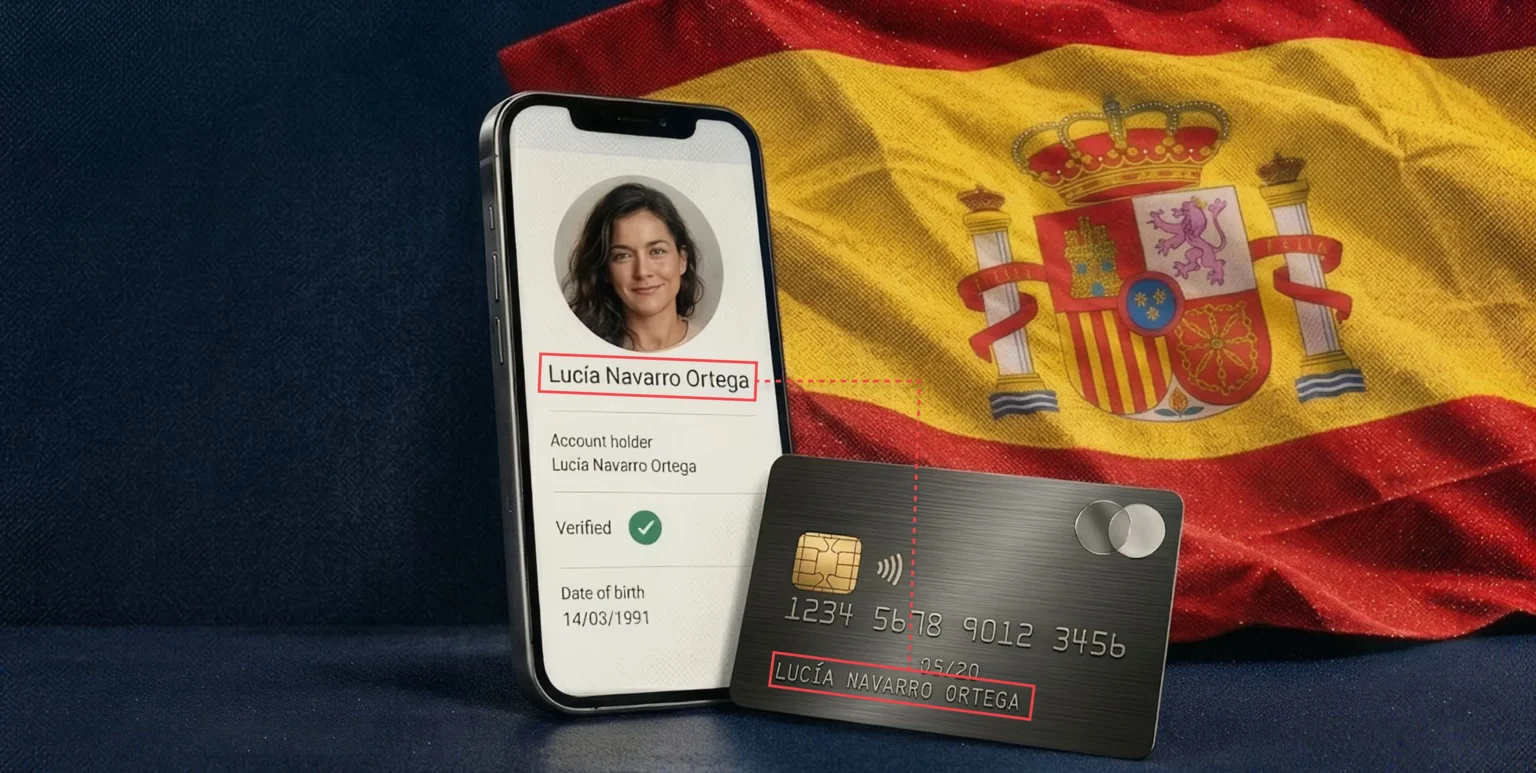

Spain will require online gambling operators to confirm that the person holding the payment method used for deposits and withdrawals is the same person who holds the gambling account, under Royal Decree 813/2026 published in the Boletín Oficial del Estado (BOE) on 8 October 2026. The rule takes effect on 28 October 2026, and players registered before then have six months to comply, during which they cannot withdraw winnings.
The decree, dated 7 October and proposed by the First Vice-President and Minister of Economy, Trade and Business Carlos Cuerpo, amends 11 royal decrees across the financial sector. Its fifth article updates the customer identification requirements in Spain’s anti-money laundering regulation, which is approved by Royal Decree 304/2014.
Under the revised Article 21.2, establishing a gambling customer’s identity through electronic, computer, telematic and interactive means requires, in addition to meeting the conditions in Article 21.1, verification that the holder of the payment method used for deposits and withdrawals is the holder of the gambling account. The provision refers to payment methods generally, without limiting the requirement to bank cards or specifying a method for verifying payment-method ownership.
Article 21.1 retains the option of establishing a business relationship where the customer’s first deposit comes from an account in their own name at an institution based in Spain, the EU or an equivalent third country. Other secure remote procedures for identifying customers must meet the minimum requirements that are in the general authorisations published by Sepblac, Spain’s financial intelligence unit. According to its preamble, the reform prepares Spain for the FATF mutual evaluation beginning in 2026 and partially transposes EU Directive 2024/1640.
The first transitional provision gives the players registered before the requirement takes effect six months to make changes that are required. During the transition period, players may keep depositing funds through their existing payment methods and can play games, but the decree states that they may not withdraw their winnings. Accounts that are still unverified at the deadline must be terminated from the contract by the operator, who must notify the Directorate General for Gambling Regulation (DGOJ). The same six months apply to operators to implement the necessary technical gaming systems.
The revised Article 21.2 requires the operators to verify that the holder of the payment method used for deposits and withdrawals is the holder of the gambling account. This check is required along with the remote identification conditions in Article 21.1. Therefore, a remote identification route on its own no longer completes the identification for a gambling customer, and the decree does not specify how the check must be carried out.
Bank account verification covers this match for the bank-funded accounts by comparing the account holder name against the customer’s verified identity. Since Article 21.2 covers all the payment methods that are used for deposits and withdrawals, the operators must verify that each method belongs to the same person who actually holds the gambling account.
Suggested Read: