
Roast My Compliance: Where Player Journeys go wrong
 Back
Where Player Journeys go wrong
 01:00PM GMT
When Player Protection Turns Into Player Frustration
What happens when a verified account shows suspicious activity, a shared Wi-Fi connection leads to a bonus-abuse flag, or a failed location check leaves a player stuck?
These are just a few examples of how poorly designed processes can put legitimate players at risk or create unnecessary friction.
Join Shufti, iGB, DeGaming and GeoLocs for a 60-minute interactive session where we put these player journeys in the hot seat.
Why Does This Matter?
A Passed KYC Check Doesn't Establish Who Controls an Account Today
Identity verification establishes evidence about the person who registered. It does not automatically confirm who is using that account months later. When an unfamiliar device signs in, the password changes, a new payout account is added and a withdrawal is requested, relying solely on historical KYC approval can leave important questions unanswered.
Operators need to assess relevant account changes together and determine when additional authentication or review is justified, without forcing every returning player through onboarding again.
A Shared Connection Doesn't Automatically Mean Bonus Abuse
Multiple verified players accessing an iGaming platform through the same internet connection may raise questions, but a shared Wi-Fi connection alone does not establish fraud. Automatically restricting accounts without considering promotion terms, account activity and supporting evidence risks penalising legitimate players.
Effective bonus-abuse controls should distinguish suspicious patterns from reasonable explanations, giving reviewers enough context to reach proportionate decisions.
A Failed Location Check Needs the Right Response, Not Another ID Request
When location permissions are disabled, asking a player to repeat identity verification does not resolve the issue. Generic messages such as “Verification failed” can leave legitimate players retrying without understanding what went wrong. Support teams may then request unrelated documents because the actual failure has not been communicated clearly.
Operators need to distinguish incomplete location checks from results that prevent an action, provide relevant recovery instructions and preserve the necessary location controls.
Better Player Journeys Start With Better Decisions
An unnecessary restriction, a repeated verification request or a sensitive action proceeding without sufficient assessment can all result from disconnected processes. Improving these journeys means understanding what each check is supposed to establish, which information should inform the decision and what the player should experience next.
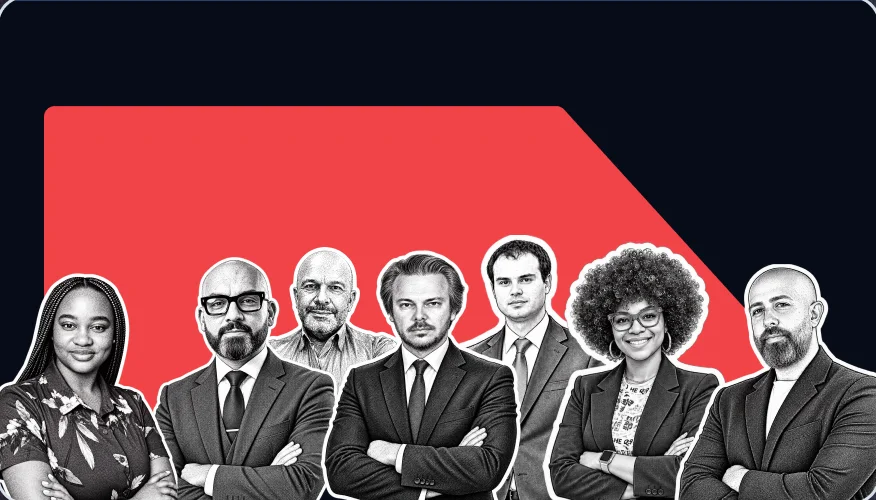
Meet the Panel
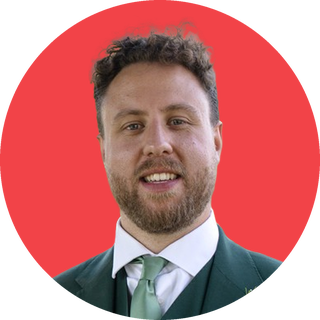
James Swann Phillips
Moderator, iGB
James Swann-Phillips is a Features Editor and Journalist at iGaming Business (iGB), with extensive experience in sports betting, gambling and sports media. He has worked across editorial strategy, industry reporting and content development, and has hosted interviews and webinars for iGB. Previously, he held senior content roles at Clarion Gaming and Une Forte, where he managed editorial teams and content strategy. His expertise spans iGaming markets across Europe, Africa and Latin America.
Johan Palm
Head of Product, DeGaming
Johan Palm is the Head of Product at DeGaming, with 17 years of experience in the iGaming industry. He specialises in product management, business intelligence, IT and software development. Throughout his career, he has helped launch over 20 casino brands worldwide and contributed to the development of casino and betting platforms. Previously, he held product leadership roles at MBG Digital, Oddsium and Futureverse, working on gaming technology, loyalty solutions and product innovation.
Ben Scobie-Trumper
Head of Sales, GeoLocs
Ben Scobie-Trumper is the Head of Sales at mkodo, with over 15 years of experience in the gaming industry. He specialises in geolocation services, gaming technology and player engagement. Previously, he held senior sales roles at Soft2Bet, Future Anthem and 3radical, working with gaming operators and technology providers. His experience covers responsible gambling, AI-driven player experiences and regulatory requirements across multiple gaming markets.
Sebastien Joseph
Enterprise Account Executive APAC, Shufti
Sebastien Joseph is an Enterprise Account Executive at Shufti, focused on helping regulated businesses across APAC with identity verification, KYC, KYB and AML solutions. He has over eight years of experience in B2B sales across SaaS, cloud, AI and technology sectors. His experience spans APAC, ANZ and EMEA, with a focus on helping businesses adopt technology that addresses their operational needs.
Reserve your spot
 Time01:00PM GMT
 Date30th November, 2026
 Event FormatVirtual
Certifications
Independently audited and certified for enterprise-grade security and data protection.
LIVE EVENT
Global Transactions, Local Rules: Closing Fraud Detection Gaps
LIVE EVENT
Financial inclusion and AML/CFT: Managing access and risk in practice
LIVE EVENT
PIX Fraud 2026: Are Your Fraud Controls Ready for the Next Generation of Instant Payment Scams?
LIVE EVENT
First Annual Fintech Executive Roundtable in Cyprus | 2025
LIVE EVENT
Innovation Roundtable Summit 2025: Build vs Buy vs Partner vs Prompt
LIVE EVENT
Meet Shufti at the UK AI Showcase, London Tech Week 2026
LIVE EVENT
Built by Shufti: A Podcast on Compliance Lifecycle
20th August
Online
LIVE EVENT
The Lifecycle of a Compliant Crypto Transfer : Travel Rule, Wallet Verification & Counterparty Risk
LIVE EVENT
Beyond the First Check: How AMLR Extends KYC Across the Customer Lifecycle
Launch Verification Instantly
Get access to Shufti’s Self-Service Portal and start verifying users with flexible, usage-based pricing.
Get Started