


 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


Beyond the First Check: How AMLR Extends KYC Across the Customer Lifecycle
 Back
Beyond The First Check:

The AMLR Compliance Challenge
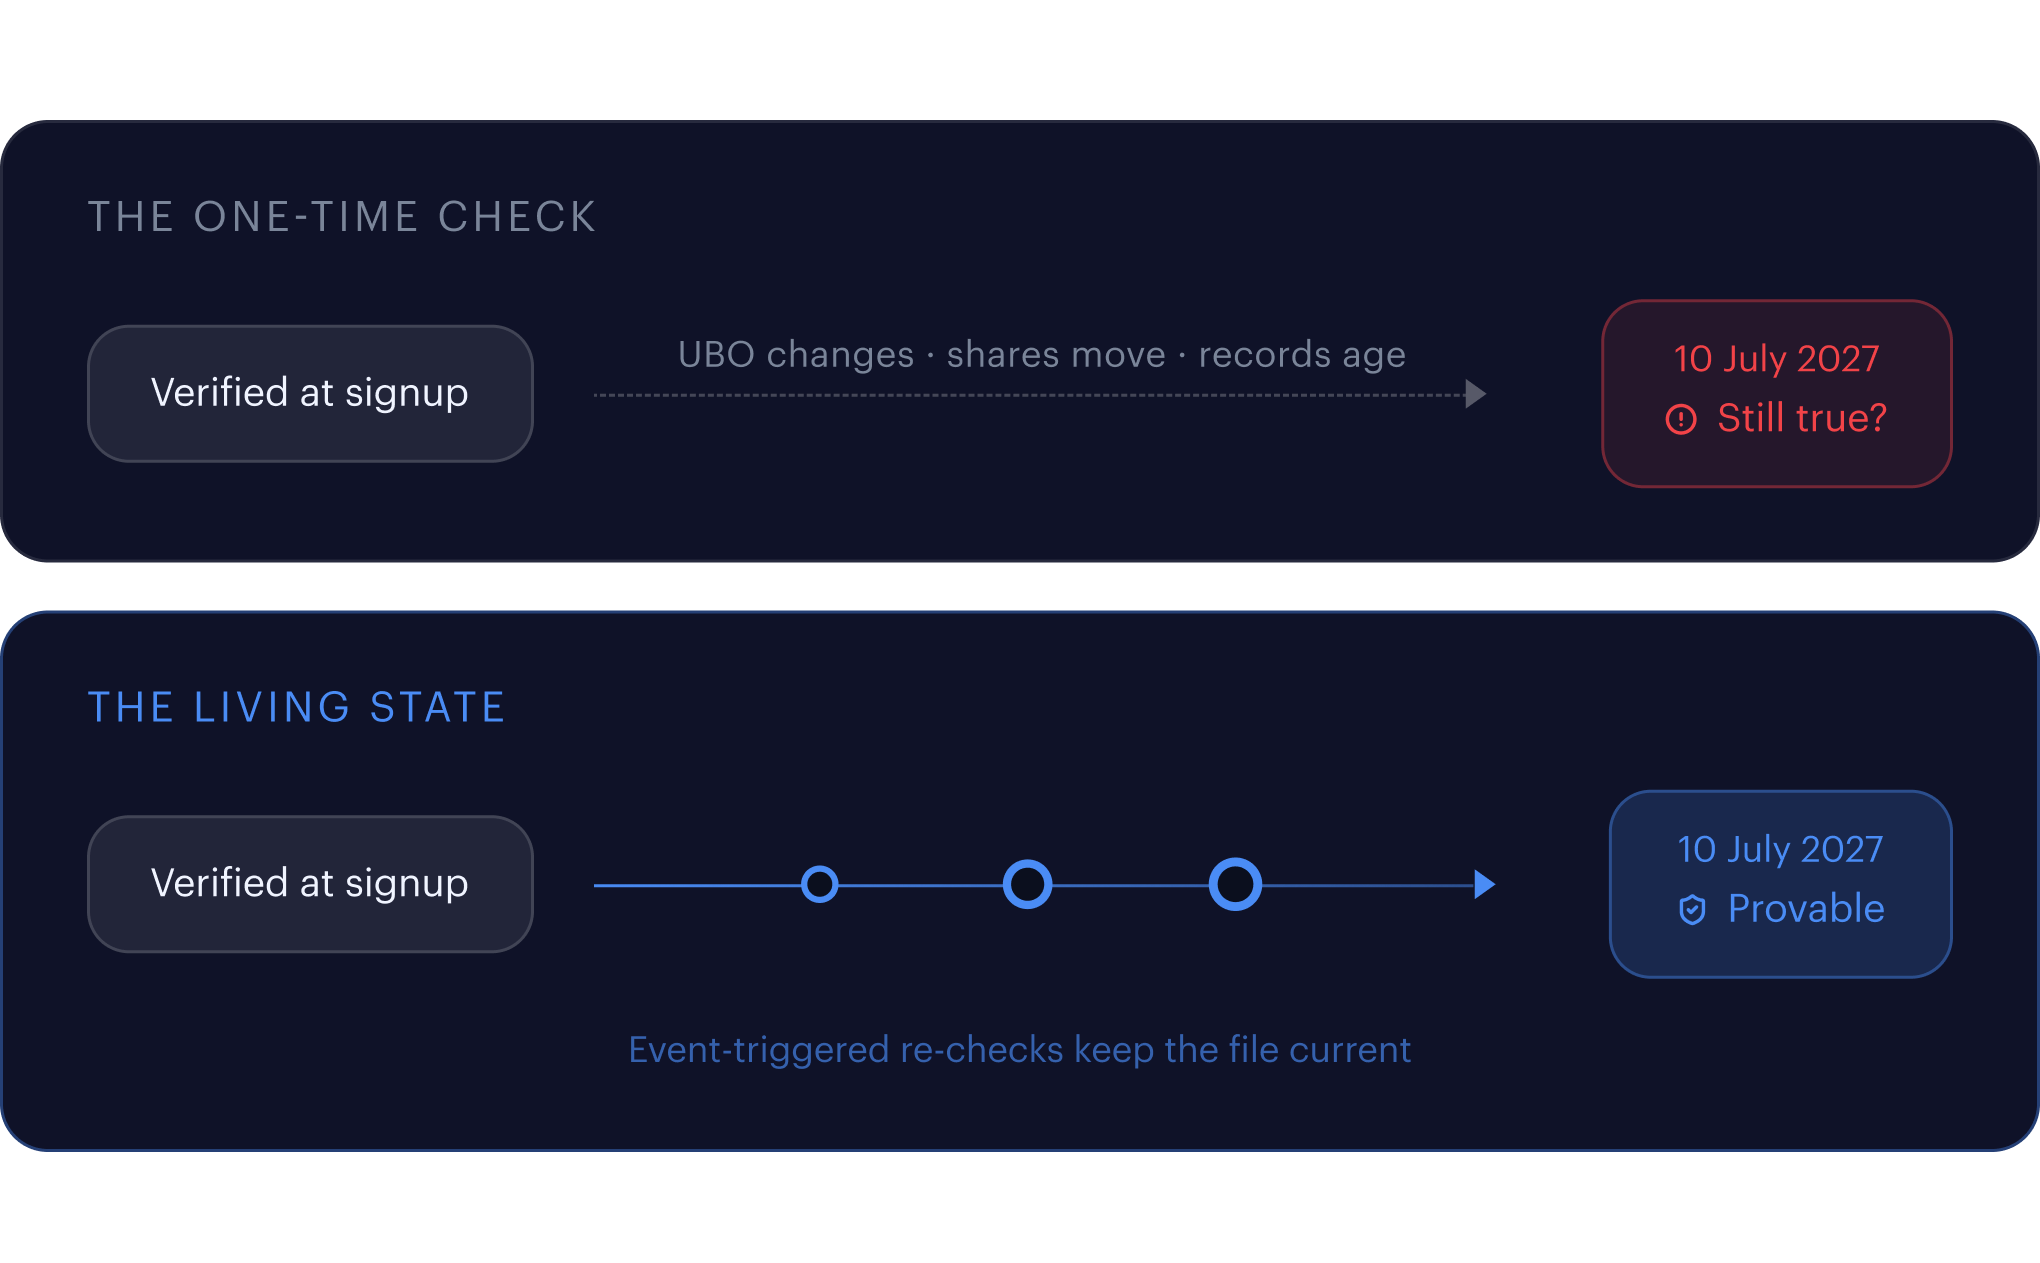
Customer verification does not stop at sign up. AMLR treats customer knowledge as a living state; one you maintain, keep current, and can demonstrate.
Join us for a live conversation on the three shifts that decide readiness:
- ✓Continuous CDD
- ✓Existing customer files
- ✓Vendor chain behind your KYC
Can you show your files are current?
Why does this matter?
Verification no longer ends at signup
Point-in-time verification is still necessary but no longer sufficient. AMLR pushes ongoing monitoring and behavioural signals to the centre of CDD, so re-checks are triggered by events and risk.
Most firms sit somewhere on the ladder between periodic review and perpetual KYC. Knowing your rung and the gap to the next one is where readiness starts.
Your existing customers are in scope too
Article 26 makes it explicit: existing customer files must be brought up to the new requirements, risk-based, high-risk first.
Everyone budgets for new-customer onboarding, almost no one budgets for the files they already hold.
You can outsource the work, not the accountability
Article 18 allows AML tasks to be outsourced, but regulatory responsibility stays with you. Every provider in your KYC chain, and every sub-provider behind them, is a dependency you must identify, oversee, and be able to explain.
Outsourcing isn't a risk. Invisibility is. The more hidden links in the chain, the harder end-to-end compliance is to prove.
Meet the Panel
Lead Global Sanctions Procedures at Rabobank
Zhanel specialises in translating legislation into clear, practical bank-wide policies and procedures. Her experience spans sanctions, AML, KYC, complex investigations and global policy. One of her current focus areas is the AMLR and its implications for financial institutions - from customer due diligence to group-wide compliance and effective implementation.
Senior Correspondent at AML Intelligence
Paul works as the Senior Correspondent for AML Intelligence where he leads the publication’s editorial coverage. As part of this, he provides in-depth analysis on areas including tech, finance, AML and law. He also writes the publication’s bi-weekly newsletter, as well as its weekly tech newsletter.
VP, Product Development & Marketing, Shufti
Raja Hassan Fayyaz is Chief Product Officer at Shufti, where he leads the teams building its identity verification, AML and fraud prevention products, working with clients including Mastercard, Stripe and Binance.
Before Shufti, he was Chief Development Officer at QuickBit, building a blockchain payment gateway handling over 20,000 transactions a month and custom crypto wallets for Bitcoin, Bitcoin Cash and Litecoin.
Watch the recording
Certifications
Independently audited and certified for enterprise-grade security and data protection.
LIVE EVENT
PIX Fraud 2026: Are Your Fraud Controls Ready for the Next Generation of Instant Payment Scams?
LIVE EVENT
First Annual Fintech Executive Roundtable in Cyprus | 2025
LIVE EVENT
Innovation Roundtable Summit 2025: Build vs Buy vs Partner vs Prompt
LIVE EVENT
Meet Shufti at the UK AI Showcase, London Tech Week 2026
LIVE EVENT
Built by Shufti: A Podcast on Compliance Lifecycle
20th August
Online
LIVE EVENT
The Lifecycle of a Compliant Crypto Transfer : Travel Rule, Wallet Verification & Counterparty Risk
LIVE EVENT
Beyond the First Check: How AMLR Extends KYC Across the Customer Lifecycle
Launch Verification Instantly
Get access to Shufti’s Self-Service Portal and start verifying users with flexible, usage-based pricing.
Get Started