

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


Napier AI Alternative for Identity-Anchored Transaction Monitoring
Compare Shufti and Napier AI across transaction monitoring, fraud prevention and AML. Napier monitors the transaction. Shufti verifies the person behind it, generates its own device and behavioural fraud signals, screens against data it owns, and scores every payment in 500 milli seconds against 1,600+ enriched data points, all on one platform and one audit trail.
Compare the Identity Behind Each Monitoring Decision
Both platforms apply rules and machine learning to transaction risk. For businesses evaluating alternative to Napier AI and its Continuum platform, the difference lies in what each platform knows about the person behind the account when an alert fires. This comparison shows which identity, device, behavioural, screening and investigation capabilities are native, partner-delivered or customer-supplied, and how each platform performs across the compliance lifecycle. Where the published evidence supports neither side, the row is marked Comparable.
Built in. Document forensics, iBeta Level 3 liveness and face matching verify identities on the same platform that scores transactions and raises alerts.
Partner-delivered KYC, identity verification is not offered natively; onboarding and KYC are delivered through Delta Capita's Karbon platform, KYCP and Strise.
Native device, network and behavioural signals, biometric re-authentication and document forensics feed transaction scores without a second vendor.
Partner-delivered behavioural biometrics through ThreatMark (October 2024). Native detection uses the ML anomaly score within transaction monitoring.
Fully in-house. Sanctions, watchlist, PEP and adverse media data are ingested, normalised and matched internally, with 15-minute refreshes.
Third-party data. Works with all third-party vendors; listed providers include Dow Jones, LSEG and Dun & Bradstreet, licensed alongside Napier.
Identity-anchored scoring across 1,600+ enriched data points: verified identity, KYC status, screening outcomes, device/IP intelligence, beneficiary history and the customer’s own baseline.
Rules and ML use supplied transactions, watchlists and historical customer behaviour. Data-point counts are not published.
500ms payment-path decision. One API call returns risk score, approve/decline/review/custom action, triggered rules and inline sender/beneficiary sanctions and AML screening. Batch review supported.
Real-time alerts with stated sub-second responses, routed to Napier’s case tool or yours via Continuum Flow. No specific latency figure or public API reference.
50+ industry-ready rule sets cover structuring, smurfing, mule activity, corridor/beneficiary risk and linked accounts. Manual rules support thresholds, weights, filters and velocity windows.
100+ built-in AML typologies. Celent counted 160 prebuilt rules in 2023, mapped with UK regulators. Includes a no-code rule builder. Comparable.
Review-gated backtesting. New or changed rules replay against 90 days of customer and transaction history; compliance approval is required before production.
Integrated sandbox tests rules on production data before go-live, without disrupting daily operations. A long-established Napier strength. Comparable.
AI wizard drafts rules from risk scenarios. Compliance review and MLRO approval precede deployment; every version is retained.
AI rule drafting is not publicly documented. Published Insights AI capabilities cover scoring and investigation.
Missing required data triggers Not Assessable and review when a transaction cannot be scored; it is never classified as low risk.
Not publicly documented. Current product pages do not explain how incomplete fields are classified.
Compares amount, frequency, timing, device consistency and transaction type against each customer’s own 90-day behavioural profile.
ML uses historical behaviour; Insights AI compares activity against global, local or peer-group norms. No time window stated. Comparable.
End-to-end investigation and filing: L1/L2/MLRO escalation, four-eyes review, SLA tracking, goAML-ready data and SAR/STR/CTR packs, with a five-year append-only audit trail.
Native case workflow, 80-widget dashboard and Regulatory Reporting Manager auto-fill up to 80% of US SAR, Canadian STR and Australian SMR fields. Comparable; regional depth differs.
Identity, device and behavioural context detect account takeover, mule activity, synthetic identities, multi-accounting and bonus abuse, feeding findings into transaction scores.
Native ML detects behavioural patterns in payment data. ThreatMark’s behavioural biometrics provide phishing and account-takeover detection.
Re-scores onboarding, login, deposit and withdrawal in under 5 seconds per event. Returns persistent Visitor Fingerprint ID and composite Threat Level; detects VPNs, residential proxies, TOR, emulators and shared devices.
Not native. Perpetual Client Risk Assessment ingests device or fraud events from onboarding, AML, fraud and CRM systems; another system must generate them.
API/webhook reason codes on every behavioural biometrics decision Shufti returns.
Partner-delivered behavioural biometrics through ThreatMark under the October 2024 partnership.
Native liveness and document forensics detect presentation attacks, replay, virtual-camera injection and AI-generated documents before account creation.
Not applicable. No identity verification, liveness or document checks offered.
Identity controls independently evaluated: iBeta Level 3 PAD conformance, 0% error across iOS/Android, and all DHS Remote Identity Validation Rally 2025 performance goals met.
No like-for-like control to compare. Napier’s independent evidence relates to AML transaction monitoring and screening, covered.
Links accounts by face, device, email, phone, IP, payment identifiers and beneficiary overlap for investigation as a network.
Transaction-monitoring link analysis is not publicly documented. Published capabilities describe ML pattern detection and peer-group comparison.
Models analyse native identity, document, device, behavioural, screening and transaction signals from one platform.
Insights AI analyses transaction flows against global, local and peer-group norms, using transaction and customer records supplied to Continuum.
AI Compliance Co-Pilot provides verdicts, key drivers, recommendations and confidence levels; analysts decide. No public regulatory sandbox testing published.
Insights AI models tested in the FCA Supercharged Sandbox under Project Theseus before the March 2026 launch. A Napier strength.
MLRO AI Agent triages Level 1 alerts, reducing triage time by up to 60%. Analysts retain final decisions; MLROs approve production rules.
Insights AI explains anomaly root causes in plain language, with human judgement retaining control. Comparable.
First-party MCP integration lets supported AI clients initiate IDV, KYB and AML checks.
No first-party MCP integration publicly documented.
One consolidated identity profile: 4,000+ watchlists, 215+ sanction regimes, 2.6M+ PEP profiles across four risk tiers, and 50,000+ news sources in 80+ languages.
Vendor-agnostic Client Screening covers sanctions, PEPs and adverse media in real time or batch, using licensed Dow Jones, LSEG or Dun & Bradstreet data.
Sanctions and watchlists refresh every 15 minutes; adverse media is ingested continuously.
Refresh cadence depends on the licensed data provider. No figure published.
Opt-in monitoring re-evaluates each screened identity against new listings and adverse media, with email or webhook alerts.
Perpetual Client Risk Assessment continuously recalculates client risk from screening, monitoring and external KYC or fraud events. Comparable.
Native entity verification, UBO due diligence and AML screening of the entity and every extracted director and owner, within one audit trail.
Partner-delivered business onboarding and KYB through providers such as Delta Capita and Strise.
SaaS, private cloud, on-premises and air-gapped deployment options.
SaaS in any Azure data centre, public/private cloud, air-gapped or hybrid deployment, with multi-org single tenancy. Comparable.
Documented regional residency across the EU, UK, US, APAC and MENA.
Residency follows your chosen Azure data centre or private cloud. Comparable.
Sandbox within 24 hours. Typical API integration: 2-5 business days; SDK: 1-3. Dedicated integration team through go-live; public transaction-endpoint documentation.
Sales-led implementation: go-live in as little as 21 days; Starling’s CTO cites six weeks. Continuum Live bundles licensing, hosting and professional services. No public API reference.
ID verification and AML screening: 10 free checks/month, then $1.50/check on self-serve Essentials, up to 20,000 checks. Transaction monitoring priced by volume during evaluation.
Subscription pricing is unpublished. Twice-yearly innovation updates at no extra cost; screening data licensed separately from the provider.
24/7 support and a dedicated Customer Success Manager on every plan.
Dedicated Customer Success Manager and 24-hour support portal for every customer. Comparable.
Included in The Forrester Wave: Anti-Money-Laundering Solutions, Q2 2025; one of 15 vendors evaluated.
Celent Technology Standout for AML Transaction Monitoring (2023); one of 16 vendors profiled. Model Risk Manager awards with Banco do Brasil (2024) and Australia Post (2025).
Identity-verification recognition from Gartner, KuppingerCole and Juniper; top performer in DHS RIVR 2025.
Not applicable. No identity verification offered.
No regulatory sandbox validation published.
FCA Supercharged Sandbox participant; Insights AI models tested under Project Theseus.
iBeta Level 3 conformance to ISO/IEC 30107-3, with 0% error rate.
Not applicable.
SOC 2 Type II, ISO 27001:2022, PCI DSS, Cyber Essentials Plus and QG-GDPR.
ISO 27001:2022, SOC 2 Type 2. Comparable.
Praised for speed and a simple flow.
No profile located as of 3 September 2026. Trustpilot serves end users and rarely covers AML vendors.

Reviewers cite ease of use and flexible onboarding journeys.
2 incentivised reviews (2022, 2025). Too few to indicate performance either way.
Fast checks and easy device switching.
Listing exists, with no user reviews.
Methodology note. Review scores were pulled from Trustpilot, G2 and Capterra on 3 September 2026. Napier AI product, partner and press pages were reviewed on 3 September 2026. Analyst references include Celent’s 2023 AML Transaction Monitoring report, The Forrester Wave: Anti-Money-Laundering Solutions, Q2 2025, iBeta conformance letters and DHS RIVR 2025 coverage. Rows marked Comparable indicate that published evidence does not support a claim of advantage for either platform.
Test Us With Your Edge Cases
Alert queue growing faster than your team? False positives eating analyst hours? Screening and monitoring in two systems that never talk? Bring a difficult investigation to the demo. We’ll walk through the customer evidence, triggered rules, review steps and reporting workflow, so your team can assess how Shufti handles the case.
Request A Transaction Monitoring Demo
Unified Platform or Partner Stack: Where the Difference Appears
With Napier AI, the identity layer, the behavioural fraud layer and the screening data are supplied by partners. That can preserve an existing vendor stack, and Napier's partner directory is deliberately broad. But each partner is a separate contract, integration and data perimeter, and every handoff between them is another place where evidence can drop out of the risk decision. Napier's own August 2026 partnership announcement describes the problem it is trying to solve: onboarding, KYC and AML “operating on fragmented systems”.
Shufti brings identity verification, device and network intelligence, behavioural biometrics, screening and transaction monitoring into one platform, so the identity check, the transaction decision and the case file are the same record.
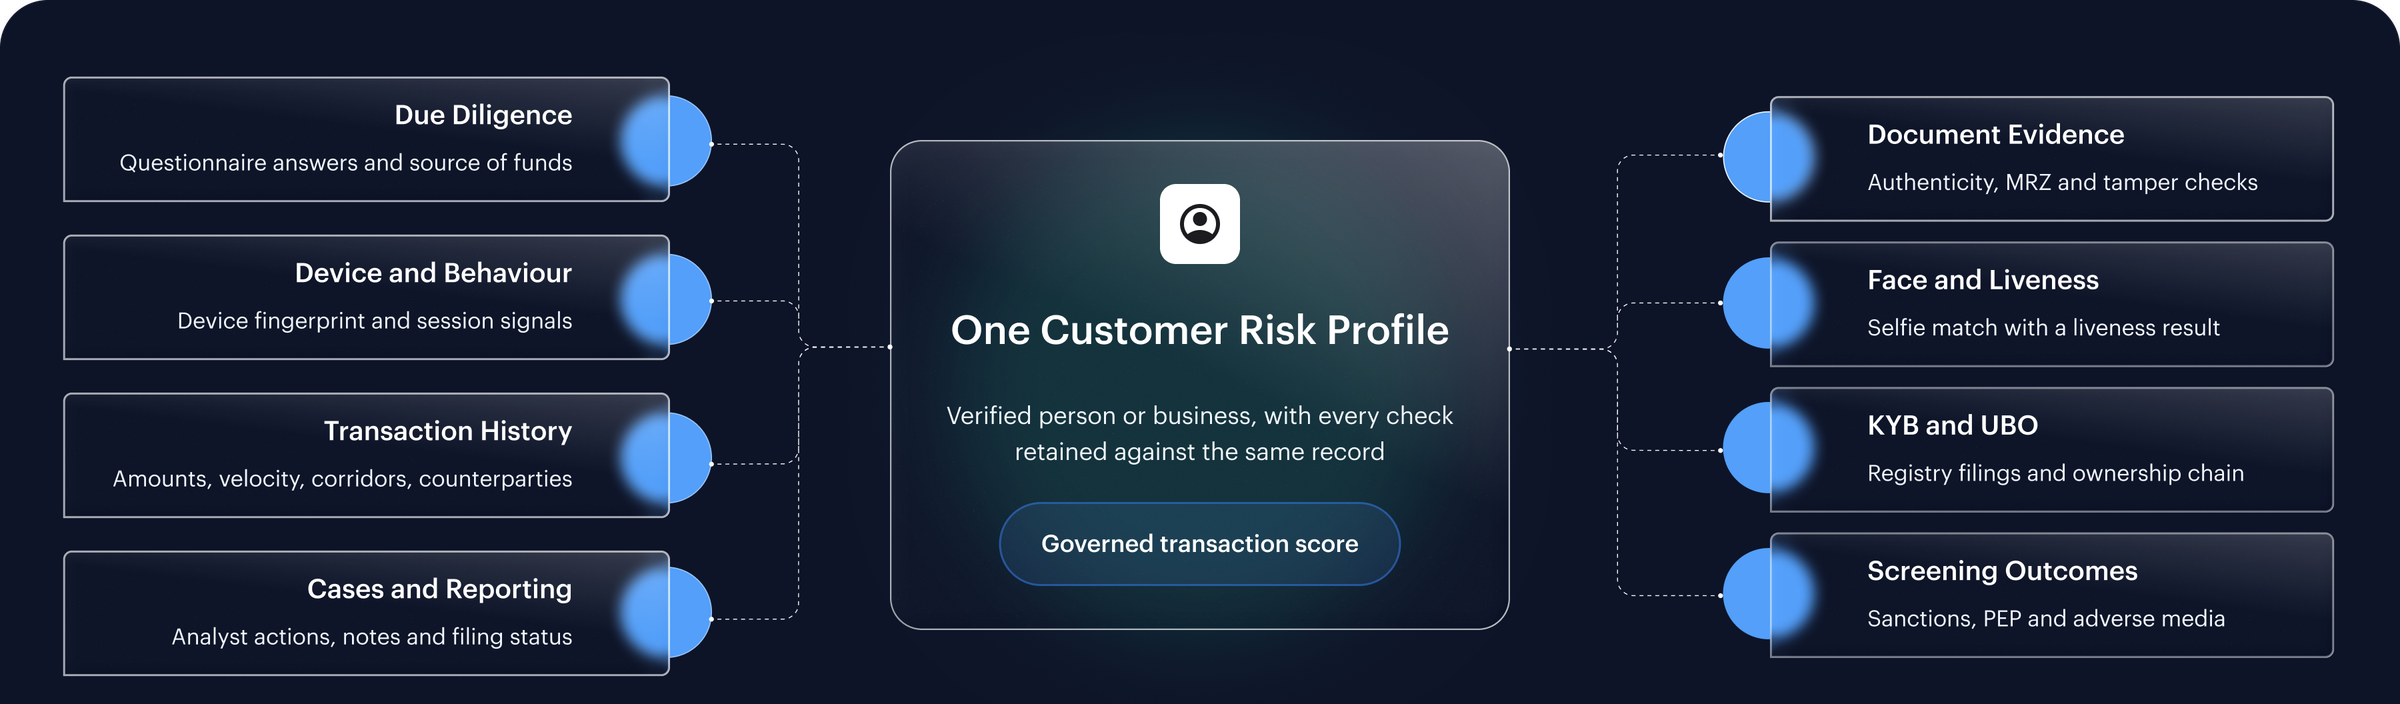
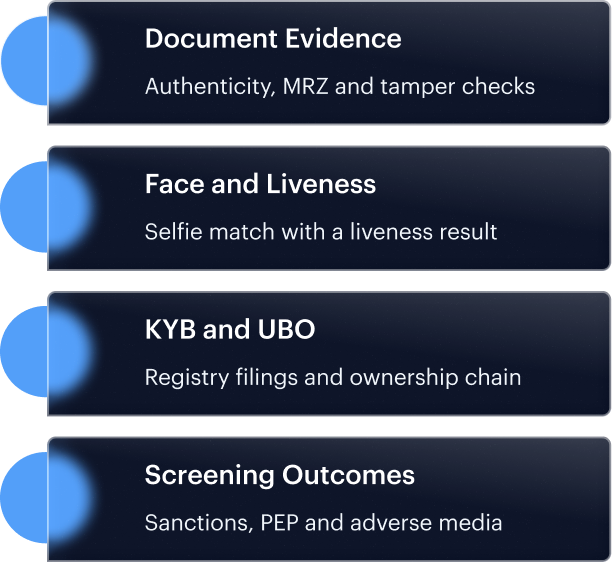
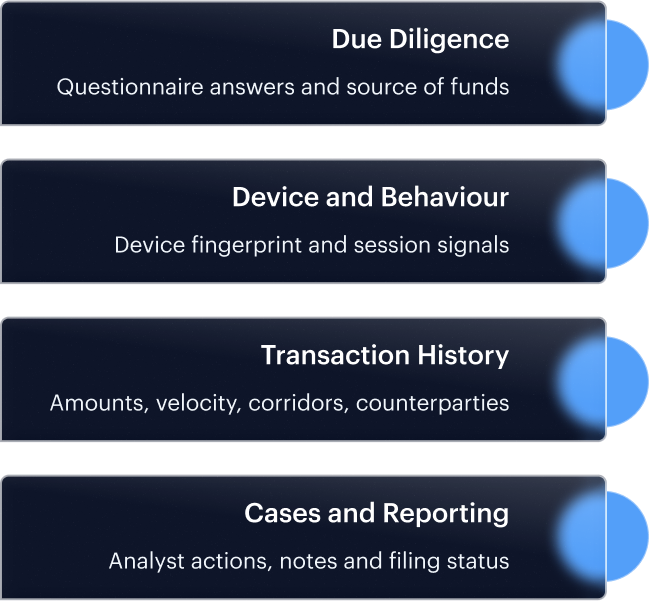
See the Evidence Behind the Alert
A €9,400 payment leaves a two-month-old account for a new beneficiary in a higher-risk corridor. Here is the context Shufti can bring into the review.
Spot the Pattern
An unfamiliar device and a sudden increase in payment activity flag the transaction for review. The alert is the starting point.
Know the Customer
Review document and liveness results alongside available onboarding information, including the customer's declared source of wealth where collected and linked.
Connect the Evidence
Check the beneficiary's available screening status and linked accounts sharing the device to investigate whether the payment fits a wider pattern.
Keep Analysts in Control
The analyst reviews the case evidence. If reporting is warranted, AI drafts a SAR narrative from the case record for human review and approval.
Illustrative scenario. Evidence depends on collected data, enabled services and configured links. SAR = suspicious activity report.
DON’T JUST TAKE OUR WORD FOR IT, HEAR FROM OUR CUSTOMERS
The Confidence
Our Clients Share
Score
“We’re proud to have one of the lowest fraud rates of any gaming marketplace globally and we are always searching for new solutions to better improve the safety of our customers. Shufti provided the most effective KYC solution, allowing us to streamline our customer’s experience on the Kinguin Marketplace, ensuring purchases are as secure and convenient as possible.”
Onboarding
Rate
“We take our clients’ privacy very seriously, and we want them to know that we are constantly looking for new innovative solutions to ensure a safe banking experience. This is why we are proud of our recent partnership with Shufti, the AI-powered identity verification solutions provider, which will provide state-of-the-art identity verification. This collaboration falls under our strategy to provide a seamless and secure digital experience for our valued customers who prefer to use our online platform. We aim to improve our online banking and create an even safer service through the “Safwa Mobile” application.”
“As a relatively new brand, we need to absolutely ensure that initial brand interactions between Mintus and our customers are slick and smooth. To achieve this we need technology that is highly customisable to our needs and able to accurately verify individuals from across the globe. Not only does Shufti deliver this, it also does it quickly and easily – something our customers truly appreciate. We estimate that £150m of painting investments will be verified by Shufti this year.”
Score
“When potential customers informed us that our lengthy verification processes were hindering their due diligence verification, we knew we needed to make changes. Shufti had a reputation as a leading authentication expert that would be able to streamline our processes, while enhancing our risk detection. Through partnering with the team at Shufti we’ve been able to grow our customer numbers by 20%. At the same time we’re able to streamline their experience while on our platform and stop under-aged users and potentially fraudulent users from accessing our services. It’s a win win.”
“Given that we’re working with such vulnerable people, knowing exactly who is volunteering with us is vital, particularly as we need to have a large team on the ground. We needed a secure system that was not only highly accurate, but also time-saving. Shufti eliminated the need for our staff to implement extensive, manual ID verification processes and instead enabled us to focus on our two main projects in Ukraine – to deliver support to as many people as we can, and to grow the capacity of the charity so we can help even more people.”
INDEPENDENT VALIDATION
Shufti's Recognition Across Independent Evaluations
Trusted By 2000+ Businesses Across 240+ Countries And Territories
Ranked Exceptional in the Liminal Index 2026 for age estimation
View Report
Differentiated by Gartner on document diversity and country coverage
Read more
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
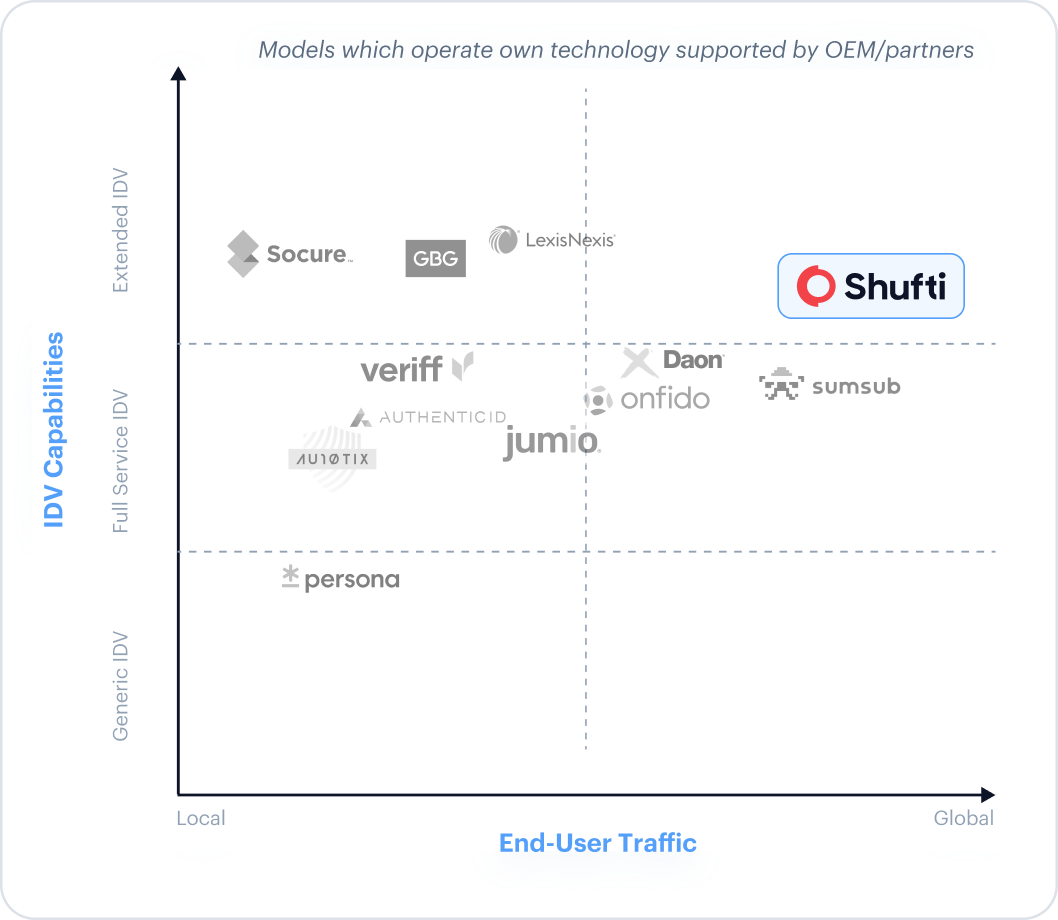
Broadest global reach in the 2025 KuppingerCole Extended IDV report
Download Report
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
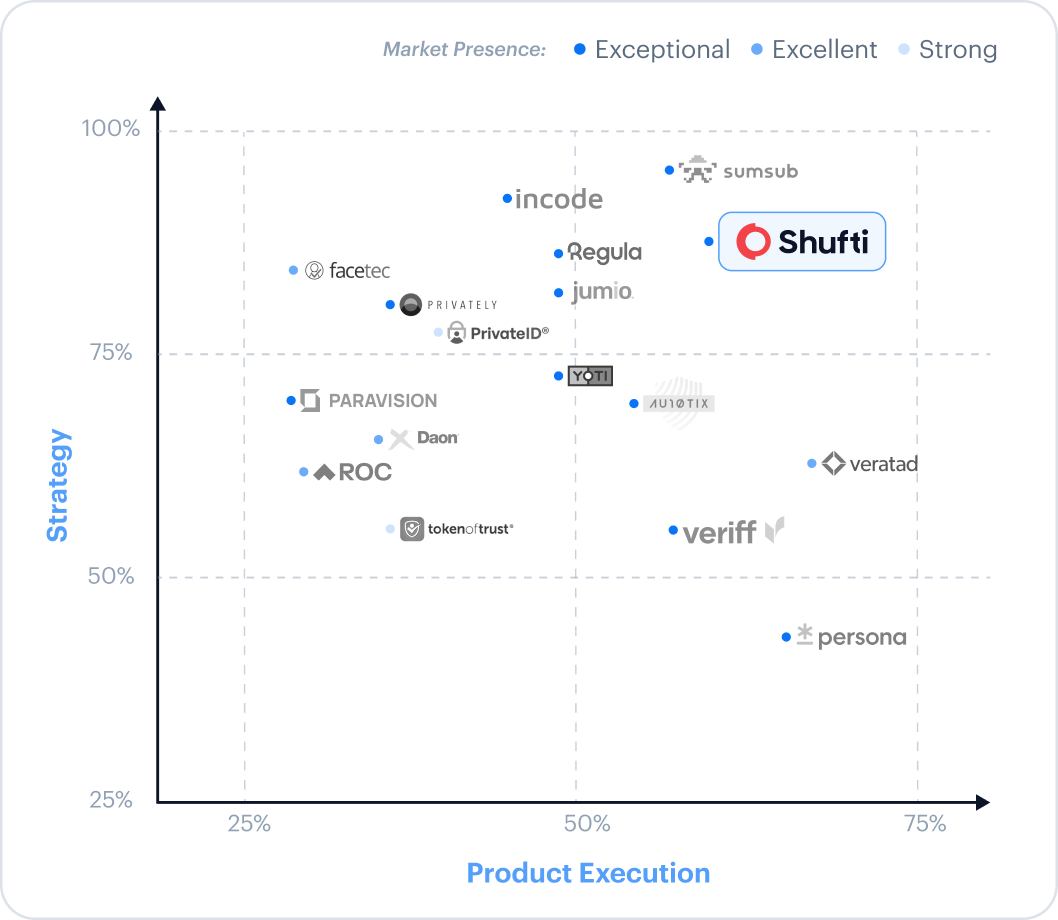
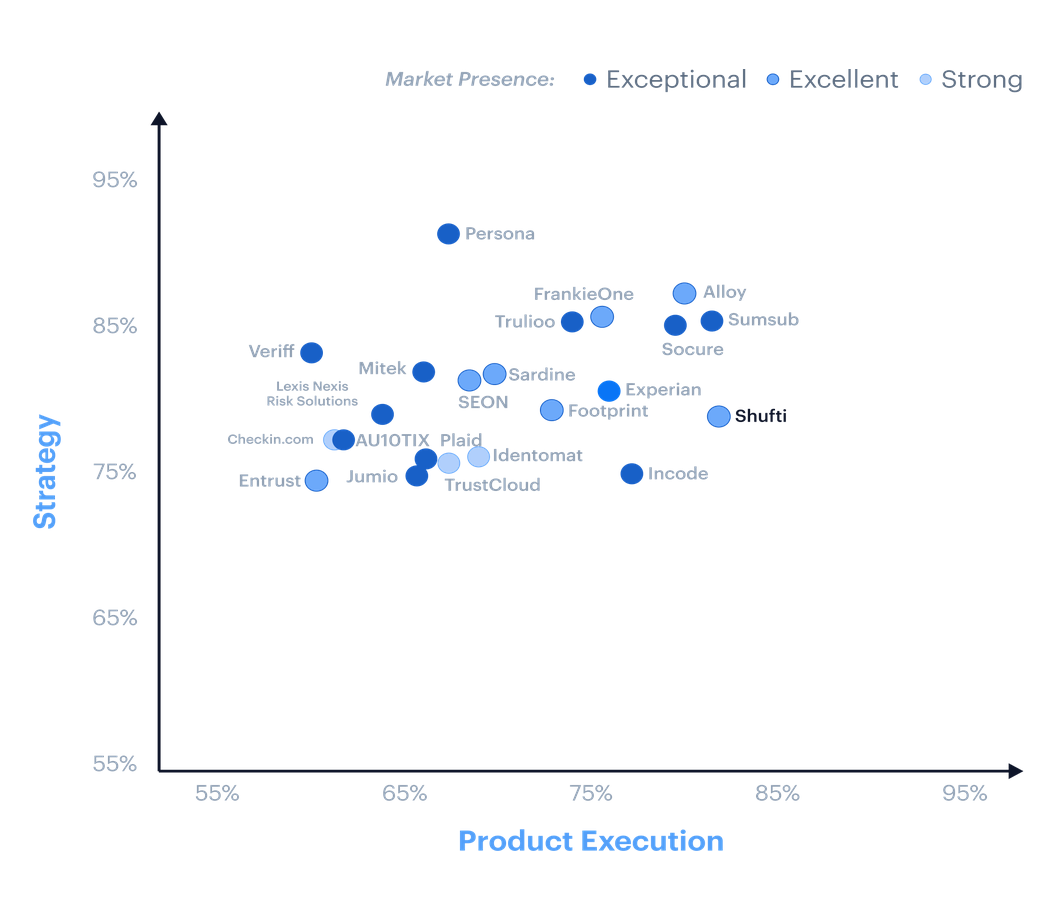
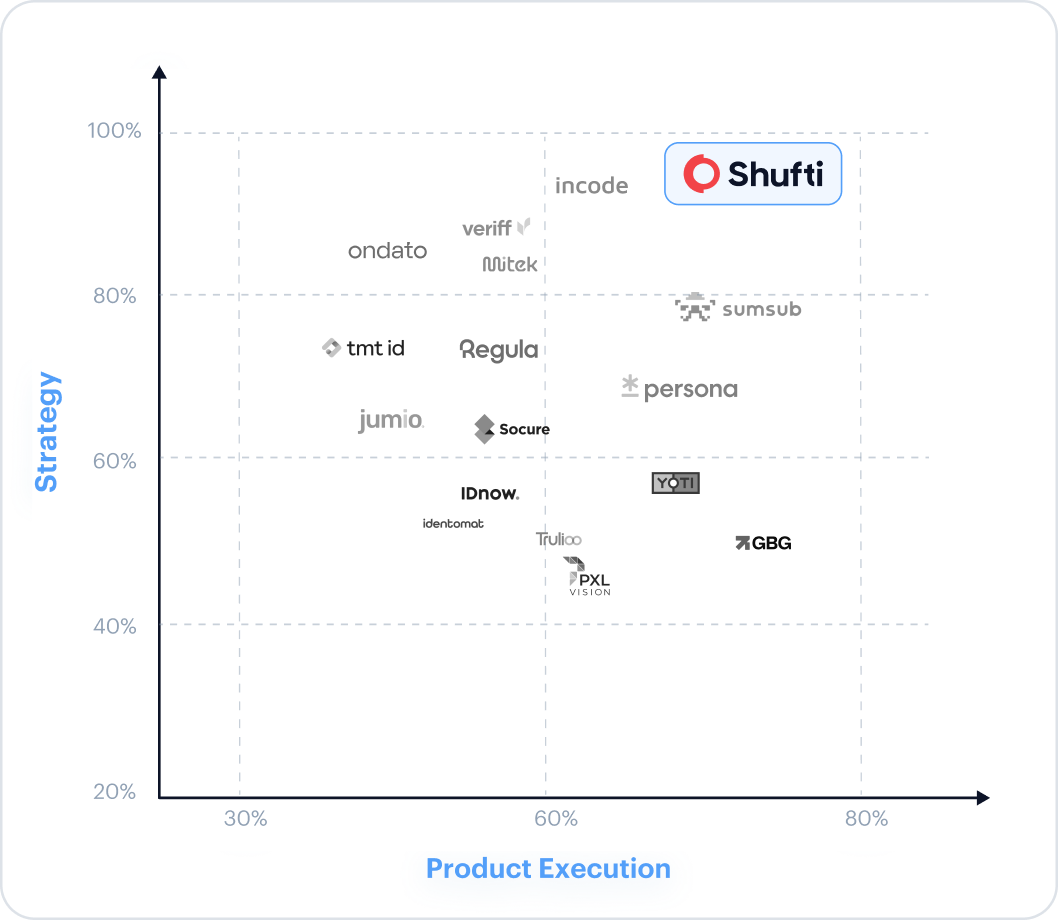
Top Vendor for Product Execution in the Liminal Index for KYC 2026
View Report
Ranked Exceptional for age verification by Liminal Index 2026
View Report
Recognised as a Leader in G2 Fall 2026 reports
Read More
Run Shufti Beside Napier AI Before You Decide
Review your existing integrations, monitoring rules and historical-data requirements with our team. Agree the testing, approvals and cutover plan before moving production traffic.
What Teams Ask Before They Switch
Direct answers to the questions that come up in evaluations, with dates where the answer has changed recently.
Start from what Napier does not cover. Napier AI is an AML platform for screening, transaction monitoring and client risk assessment. It does not verify identities, generate its own device or behavioural fraud signals, or own its screening data. Those come from Delta Capita, KYCP or Strise, from ThreatMark, and from Dow Jones, LSEG or Dun & Bradstreet. Shufti runs all of those layers in-house and scores every transaction in 500ms against the identity it verified at onboarding, which is why teams evaluating Napier AI competitors shortlist it.
The same engine that runs Shufti's identity verification, fraud detection and AML screening for 2,000+ businesses, with ID document coverage across 240+ countries and territories. Its 40+ ensemble models, nine-layer document forensics, device fingerprinting, behavioural biometrics and screening data refreshed every 15 minutes all feed the transaction score, and every alert carries the evidence trail behind the decision.
Either. Shufti's transaction endpoint accepts sender, beneficiary, device and payment fields, returns a decision with evidence, and supports batch submission of historical transactions. Most teams comparing Napier AI vs Shufti run both for one quarter, compare alert quality, then switch traffic.
Yes. Rules start from a library of 50+ industry-ready sets, are created manually or drafted by an AI wizard, and are backtested against 90 days of customer and transaction history before publishing. Every change is review-gated and versioned. Napier offers a comparable no-code builder and production-data sandbox, and the comparison table says so.
It does not pass it. Where a required field cannot be assessed, the transaction is marked Not Assessable and routed for review rather than scored as low risk. Every alert also carries the KYC status, screening outcome and device context of the account, so an analyst knows whether the person behind the account was ever verified.
A one-to-one match claim would be misleading, because Napier screens on whichever third-party data you license and providers disclose coverage differently. When evaluating Napier AI vs Shufti, compare sanction regimes, PEP records, adverse-media sources, refresh frequency, language coverage and performance against your own high-risk sample. Shufti publishes coverage across 215+ sanction regimes, 4,000+ watchlists and 2.6 million+ PEP records, refreshed every 15 minutes.
FinCEN-style suspicious activity workflows and NFIU and CBI reporting requirements are supported. Cases export as SAR, STR and CTR packs in a goAML-ready structure for FIUs in markets such as the UAE, Pakistan and India, with narrative, evidence and decision history attached and a five-year immutable trail. Napier's Regulatory Reporting Manager names SARs (US), STRs (Canada) and SMRs (Australia), so compare against the jurisdictions you file in.
Yes. The platform deploys as SaaS, private cloud, on-premises or air-gapped, with residency documented across the EU, UK, US, KSA and UAE. Napier also offers on-premises and air-gapped deployment in any Azure region or private cloud, so for organisations comparing Shufti vs Napier AI, deployment choice is unlikely to decide the evaluation. The identity behind the alert is.
Napier AI has broader market coverage specifically in transaction monitoring. Shufti’s market coverage excels for businesses seeking a complete identity verification lifecycle alongside efficient transaction monitoring, bringing both capabilities together in one platform.
Migration from Napier AI to Shufti can be done in 48 to 72 hours. Sandbox access is provisioned within 24 hours, API integration typically takes 2 to 5 business days and SDK integration 1 to 3. Define success metrics, replay an approved 90-day sample through both platforms and plan production migration around your technical, governance and procurement requirements. Rule tuning and MLRO sign-off sit on top of that for any vendor
Compare Both Platforms on Your Own Transactions
Replay 90 days of your own transactions to compare alert quality, evidence depth, workflow fit and deployment requirements. See whether scoring each payment against a verified identity, native device and behavioural signals and in-house screening data reduces the handoffs your team manages today. Shufti supports identity and risk workflows for more than 2,000 businesses globally.