

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


SEON vs Shufti
SEON Alternative for Transaction Monitoring, AML and Fraud Prevention
Shufti scores every transaction against a verified customer risk profile, so the KYC result, screening outcome, due-diligence answers and source of wealth sit inside the decision rather than beside it. Rules go live only after MLRO approval, and every action lands on one append-only trail that feeds SAR, STR and CTR filing. Send us a week of your own alerts and see the same cases with the identity evidence attached.
DETAILED CAPABILITY COMPARISON
Shufti vs SEON: What Each Platform Knows When It Scores a Transaction
Compare the controls your team will use every day: customer evidence attached to alerts, approval of rule changes, investigation workflows and reporting. See how Shufti and SEON address each requirement, with sources and limitations alongside the comparison. For enterprises evaluating SEON alternative, the comparison table below covers transaction monitoring, fraud, AI governance, AML and KYB, operating model and independently verified proof. Third-party information was checked against SEON's public pages on 11 September 2026.
Customer evidence alongside transaction risk. Shufti connects monitoring to identity verification, screening and available due-diligence records, helping analysts assess activity against the customer’s profile.
Signal and transaction context. Profiles combine device, behaviour, screening and transaction data; public materials do not show the same KYC, due diligence or source-of-wealth context in each decision.
Five signal families in one profile. KYC, device, 90- day behavioural baselines, geolocation and address matching, and velocity analysis, plus ring links across shared identifiers and beneficiaries.
Signal and transaction layer. Email, phone, IP, device, behaviour, location, velocity and transaction fields, with network views.
Named AML and identity typologies. Structuring, smurfing, mule activity, corridor and beneficiary risk, and layering, plus synthetic identity, deepfake, document and impersonation fraud.
Named AML and fraud patterns. Structuring, layering, rapid fund movement, bonus abuse and multi-accounting.
Real-time, identity-anchored decisions. Rules, baselines and ring links return Approve, Decline or Custom Review, with batch review and hosted User Risk Assessment.
Real-time fraud and AML scoring. Rules, AI scoring and enriched signals support real-time decisions; enrichment timeouts are configurable.
Review rules before they affect customers. Draft detection rules with AI assistance, backtest them against historical transactions and require MLRO approval before activation.
Flexible rule configuration. Configurable rules, sandboxing, AI-assisted authoring and historical batch tests support analyst-led tuning.
Custom Review with MLRO escalation. Route alerts by risk, typology, jurisdiction, customer tier or data completeness through L1/L2 and four-eyes review, with SLA tracking and Not Assessable for missing data.
Workload routing and AI triage. Alerts route by priority, risk, workload or SLA, with checklists and confidence-scored screening recommendations.
Immutable case record. IDV and AML cases, verification sessions and screening outcomes sit on an append-only five-year log, with SAR, STR and CTR filing to FinCEN, NFIU and CBI.
Centralised investigations and FinCEN filing. Notes, evidence, tasks, approvals, network views and exports support direct SAR, CTR and Form 8300 filing.
Governed suppression. Sanctions matches and prior SARs cannot be suppressed; backtesting shows projected analyst workload before activation.
Confidence-scored recommendations. Configurable fuzzy matching and an AML Screening Agent help analysts prioritise likely false positives.
Named, testable product. Transaction monitoring has its own product and pricing-page listing, alongside AML case management and regulatory reporting, with a free tier.
Premium tier only. AML Transaction Monitoring, Payment Screening and Case Management are custom-priced; Starter covers fraud checks.
Multi-signal risk plus certified proof. Email, phone, IP, device and velocity checks combine with document forensics, biometric matching and iBeta Level 3 liveness.
Identity verification plus fraud signals. Document, passive liveness, proof of address and eID checks combine with device and behavioural signals.
Continuous signals with biometric step-up. Behavioural biometrics, device fingerprinting, MFA, geofencing and monitoring rules can trigger 1:1 face authentication with iBeta Level 3 liveness.
Passive session detection. Device, keystroke, mouse, automation, device-farm, remote-access and call-state signals identify takeover patterns.
Biometric and device-linked duplicates. Connect reused faces, documents, emails, phones and devices across accounts, with configurable abuse controls.
Signal-led controls. Device and behavioural rules target bonus abuse and multi-accounting.
Transaction, counterparty and crypto controls. Transaction monitoring, Bank Account Verification, Crypto Wallet Screening and Travel Rule checks tie payment risk to verified customer and beneficiary context.
Authorisation-time payment screening. Check names, BIC and SWIFT codes, wallets, velocity and sanctioned-country indicators before settlement.
Certified document and biometric controls. Nine- layer document forensics with published DHS RIVR 2025 results, iBeta Levels 1 to 3 and metadata- independent deepfake detection.
Identity verification with injection detection. Template-free document analysis, passive liveness, injection and deepfake detection; no public iBeta or ISO/IEC 30107-3 PAD listing was found.
Identity-, device- and transaction-linked networks. Connect accounts through shared identifiers, biometrics, documents, payments or beneficiaries, with relationship mapping.
Transaction-cluster graph. Network Detection finds clusters in transaction history and maps linked activity.
Cross-layer inputs. Identity, document, device, behavioural, screening and transaction signals feed the same models.
Signal and transaction inputs. Models show which enriched signals drove the AI score and retrain daily on labelled data.
Advisory AI, authoritative rules. Compliance Co-Pilot explains one of five statuses with a 0-to-100 confidence score; humans decide, while missing data returns Not Assessable.
Whitebox scoring and rule suggestions. Ranked signal contributions and human-readable suggestions keep decisions traceable.
In-house model stack. Shufti states that it builds and runs its document, face, screening and monitoring technology internally under one platform owner.
First-party fraud models; IDV provenance not public. SEON describes first-party fraud models, but does not publicly confirm whether its document and biometric engines are built or licensed.
Broad verification choice. Document, biometric, NFC, docless eIDV, VideoIdent, mDL and EUDI wallet options.
Integrated identity verification. Document, passive liveness, proof of address, eID and NFC checks combine with device and behavioural signals.
Entity screening tied to KYB. AML, Business AML, PEP and RCA, sanctions, watchlists, adverse media, crypto wallets and bulk CSV screening.
Customer and payment screening. Separate modules check customers and, at authorisation, names, BIC and SWIFT codes, wallets and sanctioned-country indicators.
Continuous re-screening and tiered PEPs. API, webhook, email or back-office alerts, four PEP tiers, RCA inheritance and multilingual adverse media with phonetic matching.
Configurable cadence. Daily-to-yearly or event- triggered monitoring across sanctions, PEP, watchlist and adverse-media coverage.
Registry KYB with multi-layer UBO. Quick KYB in under 15 seconds, enhanced KYB in one to three business days, configurable ownership thresholds and re-screening.
Entity screening is documented. Businesses, vessels and NGOs can be checked; registry-based KYB and UBO discovery are not publicly documented.
SaaS, private cloud, on-premise and hybrid. Full feature parity across deployment options.
Cloud only in public materials. No on-premise option is published.
Five documented regions. EU, UK, US, APAC and MENA, with QG-GDPR, CCPA and CPRA.
EU and US regions. GDPR, UK GDPR, CCPA and PCI DSS are stated; other regions are not publicly confirmed.
Journey Builder with 18 services. REST API, hosted link, iframe, QR and Android, iOS, Flutter, React Native and Cordova SDKs, plus automatic code generation.
Fraud-specific integration depth. Dedicated APIs, web, iOS, Android and Flutter SDKs, a workflow builder, Shopify Flow and label feedback.
One-hour response on the top tier. Email, tickets and chat are available, with a 24-hour response on lower tiers.
24/7 on Premium only. Starter includes ticket and email support; Premium adds 24/7 support, account management and Managed Risk Services.
Verification-led entry. 10 free verifications monthly; Essentials starts at $1.50 per verification up to 20,000; enterprise pricing is on request.
Fraud-check package; AML on Premium. Starter is $699 monthly for 2,500 fraud checks, 10 users and 50 rules; Premium is custom-priced.
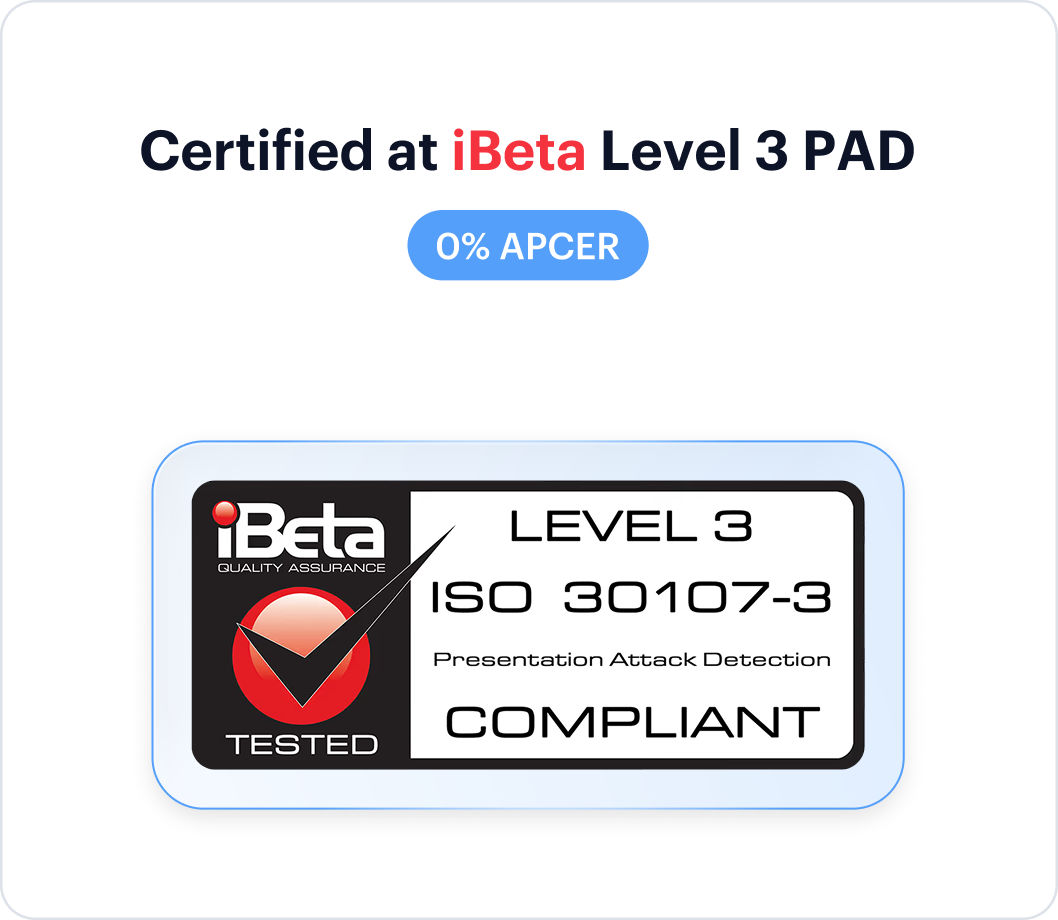
iBeta Levels 1 to 3. ISO/IEC 30107-3 conformity on iOS and Android, with 0% APCER at Levels 1 and 2 and published certification details.
No publicly listed PAD certification. Injection and deepfake detection are enabled by default for IDV, but no iBeta or ISO/IEC 30107-3 listing appears publicly.
Published DHS RIVR 2025 results. Shufti attributes document and face-match results to the US Department of Homeland Security evaluation.
Not published. No independent document or biometric accuracy test appears on SEON's public pages.
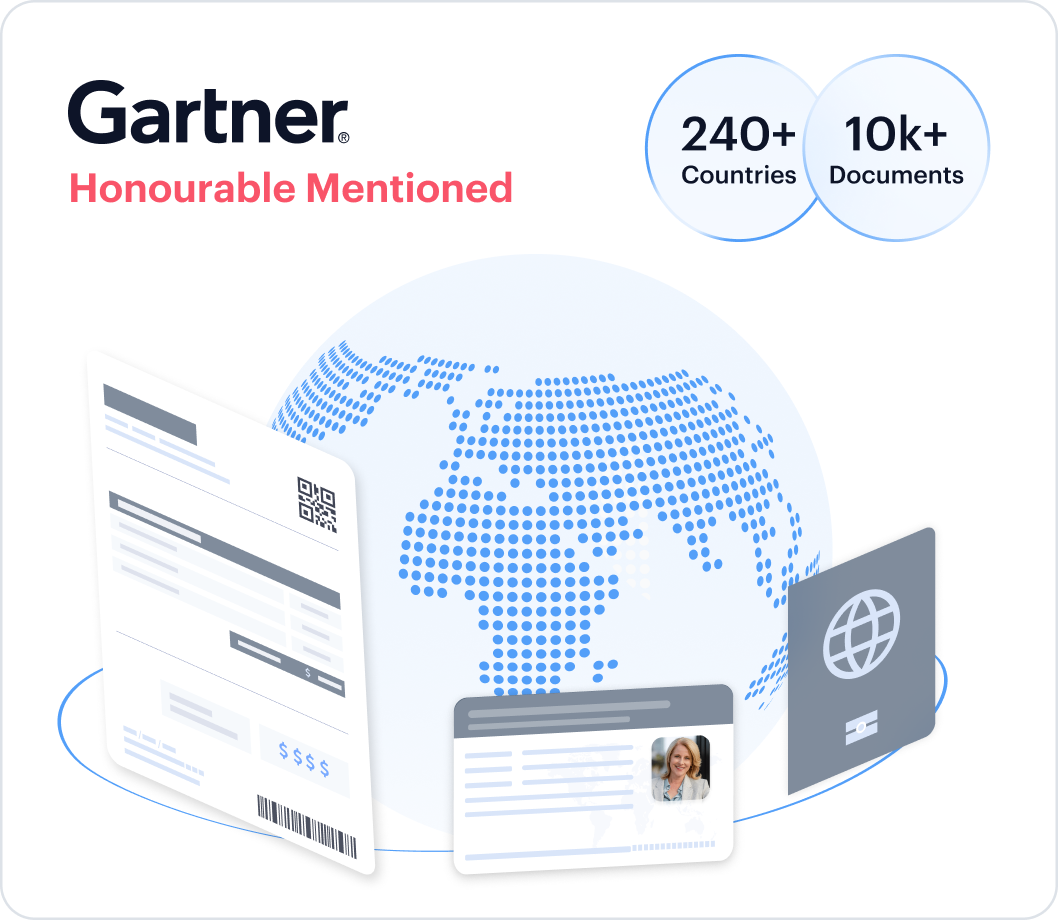
Honorable Mention in the 2026 Gartner Magic Quadrant for Identity Verification. Announced 28 July 2026.
No equivalent listing published. SEON's pages do not cite an identity-verification analyst placement.
SOC 2 Type II, PCI DSS 4.0, Cyber Essentials Plus and QG-GDPR. SOC covers 12 months; PCI was independently assessed by a QSA.
ISO 27001, SOC 2 Type 1 and PCI DSS badge. Type 1 dates to September 2024; SEON also states Type 2 without a date.
Shufti scores. AML 10.0 (20 reviews), Liveness Detection 10.0, Identity Verification 9.6 and Quality of Support 9.3. Read 11 September 2026. (G2)
SEON scores. E-commerce Fraud Protection 9.1, Fraud Detection 8.6, AML 7.9 and Quality of Support 9.3. Read 11 September 2026. (G2)
Shufti holds 4.8/5 on Trustpilot from 4,019 reviews, most left by end users completing verification inside our clients' flows. It is a completion-experience signal rather than a buyer rating, and we present it as one. SEON on the the other hand has an unclaimed profile on Trustpilot with no reviews.
All SEON information on this page was read on 11 September, 2026. Plan names and prices are from SEON's pricing page. Deployment and hosting statements are from SEON's status and legal pages. Fraud and AML capability statements are from SEON's product, case management, network detection and AML data documentation. Certification statements reflect SEON's public security pages and the absence of a SEON entry in iBeta's published ISO/IEC 30107-3 confirmation letters list as at that date. Shufti product, pricing and deployment figures are from shuftipro.com. Shufti liveness results are from iBeta's ISO/IEC 30107-3 confirmation letters page (Level 3, 24 April 2026). DHS RIVR 2025 results are anonymised by DHS; Shufti was one of five systems that met all performance goals in the selfie-to-document track. G2 and Trustpilot scores were read on 11 September, 2026 and review counts are shown for both vendors.
LET'S GET SPECIFIC
Test Us With Your Edge Cases
Alert queue growing faster than your team? False positives eating analyst hours? Screening and monitoring in two systems that never talk? Bring a difficult investigation to the demo. We’ll walk through the customer evidence, triggered rules, review steps and reporting workflow, so your team can assess how Shufti handles the case.
Request A Transaction Monitoring Demo
PLATFORM ARCHITECTURE
The Context Behind Every Transaction Score
Shufti brings verified identity, screening, due diligence, device and behavioural signals, and transaction history into one customer risk profile. Every score stays linked to its supporting evidence, giving teams the context to investigate alerts and defend decisions. Rules pass through compliance approval before going live, while an append-only, five-year audit trail preserves every action and supports SAR, STR and CTR filing.
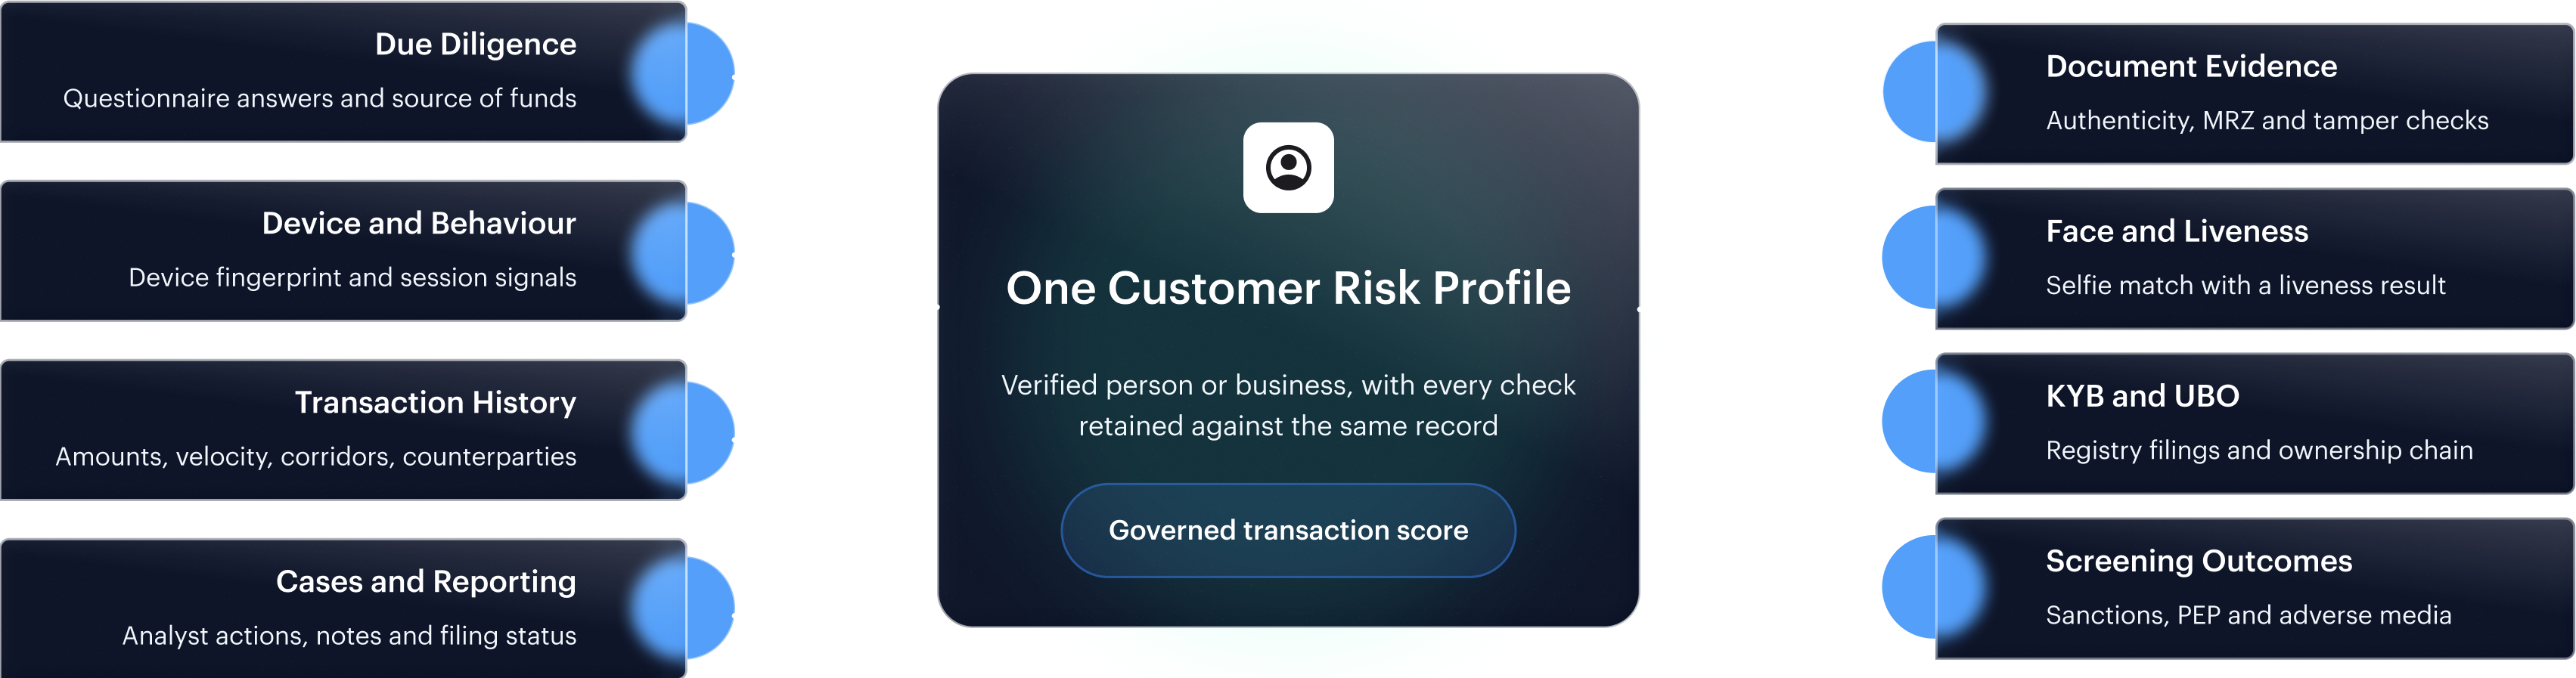
- Document Evidence
- Authenticity, MRZ and tamper checks
- Face and Liveness
- Selfie match with a liveness result
- KYB and UBO
- Registry filings and ownership chain
- Screening Outcomes
- Sanctions, PEP and adverse media
- Due Diligence
- Questionnaire answers and source of funds
- Device and Behaviour
- Device fingerprint and session signals
- Transaction History
- Amounts, velocity, corridors, counterparties
- Cases and Reporting
- Analyst actions, notes and filing status
- One Customer Risk Profile
- Verified person or business, with every check retained against the same record
- Governed transaction score
Rule Approval
Rules pass through compliance approval before they touch live traffic.
Context With the Alert
Alerts arrive with the evidence that produced the score.
Five-Year Audit Trail
Append-only retention that feeds SAR, STR and CTR filing.
IDENTITY-LED INVESTIGATIONS
See the Evidence Behind the Alert
A €9,400 payment leaves a two-month-old account for a new beneficiary in a higher-risk corridor. Here is the context Shufti can bring into the review.
01
Spot the Pattern
An unfamiliar device and a sudden increase in payment activity flag the transaction for review. The alert is the starting point.
02
Know the Customer
Review document and liveness results alongside available onboarding information, including the customer's declared source of wealth where collected and linked.
03
Connect the Evidence
Check the beneficiary's available screening status and linked accounts sharing the device to investigate whether the payment fits a wider pattern.
04
Keep Analysts in Control
The analyst reviews the case evidence. If reporting is warranted, AI drafts a SAR narrative from the case record for human review and approval.
Illustrative scenario. Evidence depends on collected data, enabled services and configured links. SAR = suspicious activity report.
DON’T JUST TAKE OUR WORD FOR IT, HEAR FROM OUR CUSTOMERS
The Confidence
Our Clients Share
Score
“We’re proud to have one of the lowest fraud rates of any gaming marketplace globally and we are always searching for new solutions to better improve the safety of our customers. Shufti provided the most effective KYC solution, allowing us to streamline our customer’s experience on the Kinguin Marketplace, ensuring purchases are as secure and convenient as possible.”
Onboarding
Rate
“We take our clients’ privacy very seriously, and we want them to know that we are constantly looking for new innovative solutions to ensure a safe banking experience. This is why we are proud of our recent partnership with Shufti, the AI-powered identity verification solutions provider, which will provide state-of-the-art identity verification. This collaboration falls under our strategy to provide a seamless and secure digital experience for our valued customers who prefer to use our online platform. We aim to improve our online banking and create an even safer service through the “Safwa Mobile” application.”
“As a relatively new brand, we need to absolutely ensure that initial brand interactions between Mintus and our customers are slick and smooth. To achieve this we need technology that is highly customisable to our needs and able to accurately verify individuals from across the globe. Not only does Shufti deliver this, it also does it quickly and easily – something our customers truly appreciate. We estimate that £150m of painting investments will be verified by Shufti this year.”
Score
“When potential customers informed us that our lengthy verification processes were hindering their due diligence verification, we knew we needed to make changes. Shufti had a reputation as a leading authentication expert that would be able to streamline our processes, while enhancing our risk detection. Through partnering with the team at Shufti we’ve been able to grow our customer numbers by 20%. At the same time we’re able to streamline their experience while on our platform and stop under-aged users and potentially fraudulent users from accessing our services. It’s a win win.”
“Given that we’re working with such vulnerable people, knowing exactly who is volunteering with us is vital, particularly as we need to have a large team on the ground. We needed a secure system that was not only highly accurate, but also time-saving. Shufti eliminated the need for our staff to implement extensive, manual ID verification processes and instead enabled us to focus on our two main projects in Ukraine – to deliver support to as many people as we can, and to grow the capacity of the charity so we can help even more people.”
INDEPENDENT VALIDATION
Shufti's Recognition Across Independent Evaluations
Trusted By 2000+ Businesses Across 240+ Countries And Territories
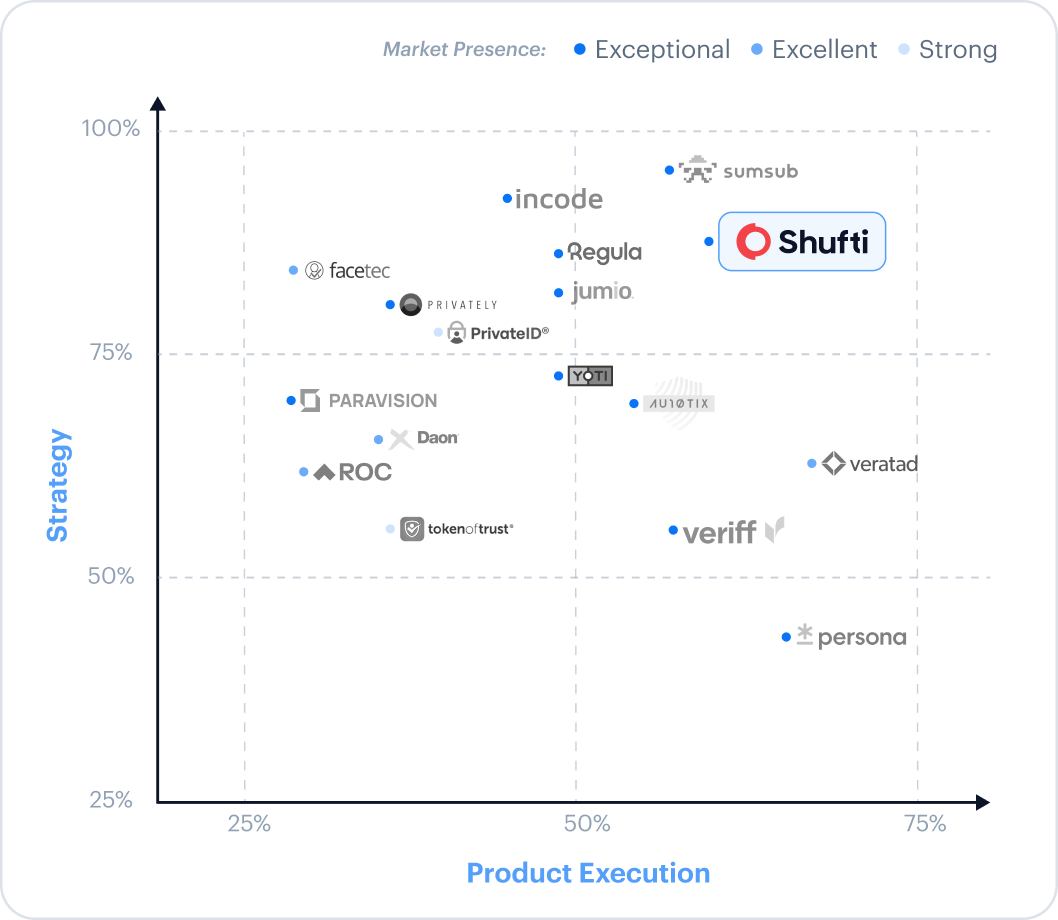
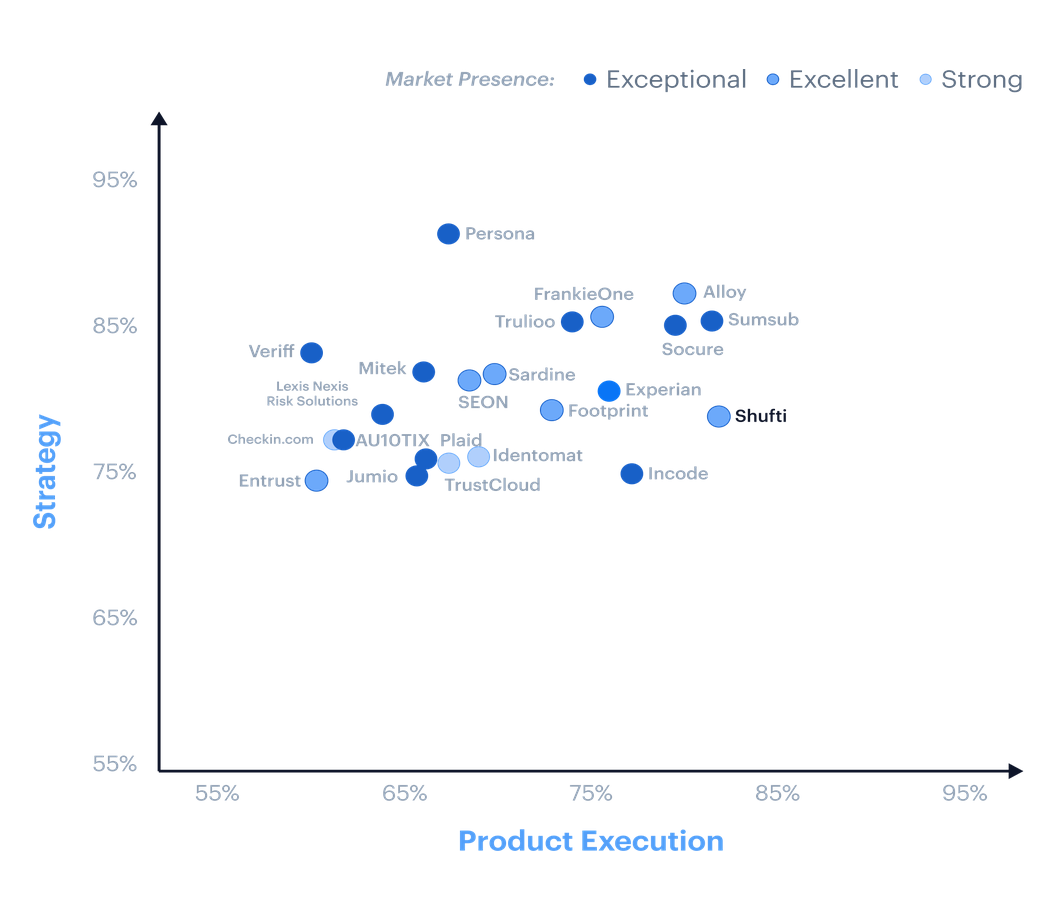
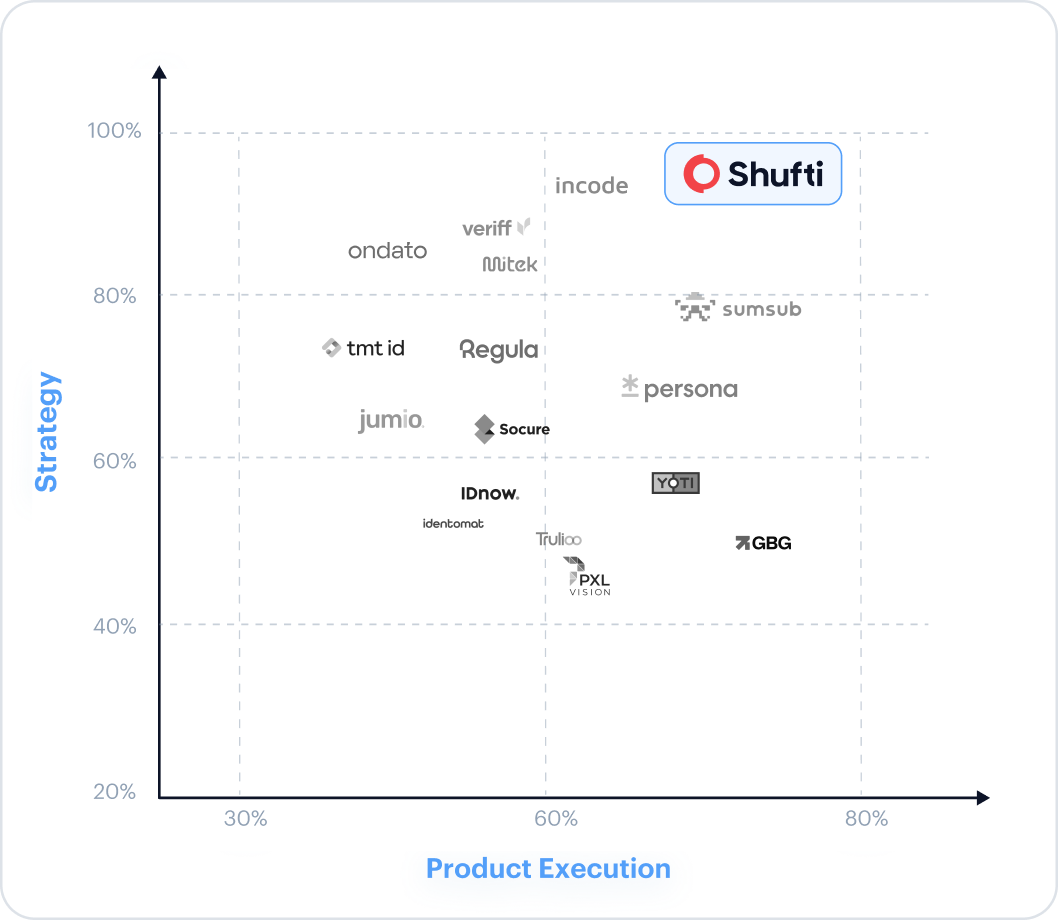
Ranked Exceptional in the Liminal Index 2026 for age estimation
View Report
Differentiated by Gartner on document diversity and country coverage
Read more
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
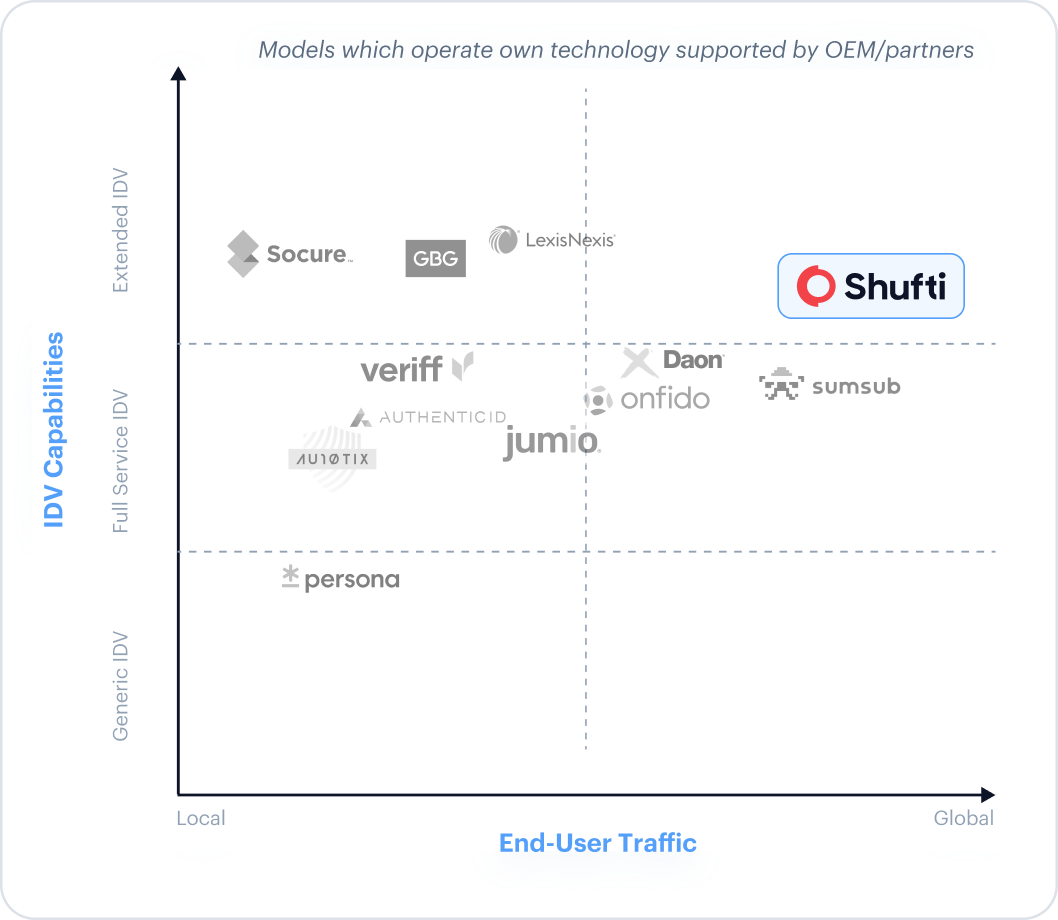
Broadest global reach in the 2025 KuppingerCole Extended IDV report
Download Report
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
Top Vendor for Product Execution in the Liminal Index for KYC 2026
View Report
Ranked Exceptional for age verification by Liminal Index 2026
View Report
Recognised as a Leader in G2 Fall 2026 reports
Read More
ZERO DISRUPTION
Plan Your Move to Shufti With Clear Implementation Steps
Review your existing integrations, monitoring rules and historical-data requirements with our team. Agree the testing, approvals and cutover plan before moving production traffic.
- 0DAY 0. MAP THE WORKFLOW
Map the workflow
Your current logic maps onto Journey Builder.
- 1DAY 1. REDIRECT ENDPOINTS
Redirect endpoints
One config file points at Shufti's API. Same request and webhook shape.
- 2DAY 2. GO LIVE
Go live
Switch live traffic when you are ready. No downtime.
QUESTIONS YOU MAY HAVE
What Teams Ask Before They Switch
Direct answers to the questions that come up in evaluations, with dates where the answer has changed recently.
Yes. SEON offers fraud prevention, identity verification, AML screening, payment screening, transaction monitoring and case management. Its AML Compliance and Case Management capabilities are listed on the custom-priced Premium plan, and direct SAR, CTR and Form 8300 filing is documented for FinCEN.
Shufti scores activity against a customer risk profile that carries verified identity, screening, due-diligence, behavioural and prior-decision context. It adds compliance-reviewed rules, historical backtesting, protected suppression, linked-case evidence and an append-only five-year trail. Buyers should verify the advantage on their own rules, alerts and reporting outputs before cutover.
As read on 2 September 2026, SEON Starter is $699 per month for 2,500 fraud checks, 10 users and 50 rules; Premium is custom-priced and includes AML Compliance and Case Management, with a free trial available on request. Shufti pricing varies by product and volume. Compare matched quotes for the same mix of transaction monitoring, screening and verification rather than per-check figures from different services.
Shufti competes with SEON where transaction monitoring, screening, fraud signals and identity meet. It adds certified liveness, registry-based KYB and UBO, and deployment choice that SEON does not publicly document.
Shufti is the stronger fit when the use case extends beyond signal screening into transaction monitoring on a verified customer, biometric duplicate detection, KYB and UBO, governed investigations and reporting. Fintech and payment teams can tie transactions to a verified customer profile, iGaming teams can connect duplicate biometrics and devices across accounts, and crypto firms can add Travel Rule and wallet-screening controls.
Shufti can consolidate transaction monitoring, AML screening, identity and business verification, fraud signals, authentication, case management and reporting in one platform. It can also run alongside existing controls during a phased transition, so replacement decisions are based on tested outputs rather than assumptions.
Export representative SEON decisions, labels and transaction history, define acceptance criteria, and compare both systems on the same data. Then map customer, business, fraud and AML logic into Journey Builder, validate rules in parallel for an agreed cycle, and cut over once decision, case and reporting outputs meet the target.
In the EU, UK, US, APAC or MENA region you select, or on your own infrastructure through on-premise, private cloud or hybrid deployment with full feature parity. SEON's publicly listed regions are EU and US.
Put a Verified Customer Behind Every Transaction Score
Bring the person, the business, the screening result, the due-diligence answers, the device and the transaction into one governed risk profile. Run a side-by-side test on your own transaction history and compare the alerts, evidence, analyst workload and reporting trail before you decide.
Evaluate Shufti Against Your Own Monitoring Requirements