

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


SymphonyAI vs Shufti
SymphonyAI Alternative. Know Who’s Behind Every Transaction.
Shufti scores every transaction against the identity it verified at onboarding. The KYC result, screening status, device context and a 90-day behavioural baseline sit inside each decision, and fraud and AML risk return as one composite score. Rules go live only after an MLRO approves them, and every action lands on one audit trail that feeds SAR, STR and CTR filing.
DETAILED CAPABILITY COMPARISON
Compare the Identity Behind Each Monitoring Decision
A transaction alert is only part of the picture. Investigators also need a clear view of the customer behind it. For businesses evaluating a SymphonyAI alternative, this comparison examines Shufti and SymphonyAI across identity context, monitoring capabilities, and investigation workflows to help you assess the right fit for your compliance team.
Scores transactions against verified onboarding identity, KYC outcome, screening status, device context and behaviour in one decision trail.
Entity Resolution unifies imported internal/external records. Partners or other vendors supply document and biometric verification; neither is built in-house.
One FRAML (fraud and AML) score per transaction, carrying onboarding fraud signals into AML monitoring.
Separate NetReveal Payment Fraud and Transaction Monitoring products share SRI Investigation’s subject-centric case view.
1,600+ datapoints enriched per transaction: device, IP, card, BNPL, bank transfer and merchant. Velocity windows: 1 minute-6 months. Ring detection links shared identifiers/beneficiaries. Full attributes published.
FinCrime ontology unifies third-party signals; ThreatMark supplies device/behavioural data (May 2025). Native email, phone and IP intelligence is not publicly documented.
10 merchant datapoints, including seller ID, merchant category code (MCC), industry, average sales price and sub-seller, drive high-risk merchant/industry rules and dedicated seller evidence.
Merchant-side scoring is not publicly documented on reviewed pages.
Agentic Rule Builder drafts plain-language rules from field, velocity and baseline primitives. Each requires six-KPI backtesting and MLRO activation. Sanctions, structuring and terrorist-financing rules remain non-suppressible.
Scenario self-service claimed (2022); full MLOps described today. Celent cautioned about limited business-user configurability in 2023.
50+ industry-ready rule sets; remittance live. Published roadmap: fintech, banking, gambling, trading, crypto and lending packs through Q2 2027.
2,500+ ready-to-use scenarios for retail banking, capital markets, insurance and correspondent banking. SymphonyAI leads here.
Identity-anchored Approve, Decline or Custom Review in under 500 ms using rules, baselines and ring detection. Historical batch review supported.
Millions of transactions monitored in real time; payment-fraud scores in under 50 ms. Fraud-score latency differs from Shufti’s full-decision latency.
Custom Review routes by risk, typology, jurisdiction, customer tier or data completeness, with L1/L2 queues, four-eyes review, MLRO escalation and SLA tracking. Alerts missing required data are held for review rather than auto-cleared.
Triage agent reviews every alert, auto-hibernating known false positives; manager agent coordinates investigation workers.
Sanctions, structuring and terrorist-financing rules cannot be suppressed. Backtesting forecasts analyst workload before a rule goes live. Where a transaction arrives without the data a rule needs, it is never scored as low risk.
SensaAI for AML is sold separately for false-positive reduction, with published reduction figures that vary by page.
Scores device mismatch, mule patterns, velocity spikes, account takeover and unusual receiver changes alongside onboarding document forensics, biometric liveness and injection-attack detection.
45+ scenarios cover romance scams, account takeover and money mules; intra-day corporate batch/ACH interdiction. Application/onboarding fraud products are not stated.
Native: 24 device datapoints, five device- ID/reputation signals, proxies/VPNs (Tor/residential), emulators/virtual machines and email/phone validity/velocity checks. No third-party contract.
ThreatMark supplies behavioural biometrics, device and threat data. Consortium data and email/phone intelligence are not stated.
Approve, Decline or Custom Review in under 500 ms, with risk score, supporting evidence and rule hits.
Hold, block, release or step up in under 50 ms, including authentication and investigation holds. PSD2 transaction risk analysis rulesets support strong customer authentication (2022).
In-house document, face, screening and monitoring technology. Compliance-owned fraud/AML rules share one MLRO-gated builder under one platform owner.
Citizen data scientists create/tune models; optional Managed Analytics Service (2022). Current pages do not describe a fraud UI rule builder.
Links accounts by email, phone, IP, device, payment identifiers and shared beneficiaries, plus onboarding biometric/document links.
Entity Resolution and SRI Copilot expose investigation networks. Graph features in real-time fraud scoring are not stated.
Identity, document, device, behavioural, screening and transaction signals feed the same models.
Supervised/unsupervised models score anomalies and prioritise alerts across the FinCrime ontology. Imported KYC records supply identity evidence.
Agents draft rules, triage alerts and pre-assemble cases. Compliance Co-Pilot is advisory; the MLRO signs every SAR/STR.
Triage, manager and worker agents automate workflows; auto-populated SARs require human review/approval. Reported agent/investigator adjudication alignment exceeds 90%. Both retain human final authority.
Eight-step question pack drafts rules for individual compliance acceptance, editing or rejection. Nothing auto-publishes.
Full MLOps: build/import models, deploy in weeks. AI-drafted rules for business users are not described.
First-party MCP: Claude, Cursor and ChatGPT access KYC, KYB, AML screening and 17 further verification tools. OAuth 2.1/PKCE security.
Azure OpenAI powers SRI Copilot inside SRI Investigation. No first-party MCP integration documented.
Native XML to three financial intelligence units: FinCEN (BSA XML 2.0), Nigeria NFIU (goAML v4.x), Iraq CBI (goAML v5.0.2). Plain-English XML view, CTR deadline guard, MLRO sign-off before transmission.
Five Disclosures frameworks: goAML, FinCEN, FINTRAC, AUSTRAC, UK NCA. Ready-to-use FinCEN SAR/CTR reports (2022). SymphonyAI covers more FIU frameworks.
Immutable five-year append-only log: verification sessions, screening outcomes, alert actions, filings and rule versions.
Default immutable audit trail for every model decision, agent action and SAR filing. Retention period unstated.
One platform: document, biometric, NFC, docless eIDV, VideoIdent, mobile driving licence and EUDI wallet verification; iBeta Level 3 liveness conformance.
Partner-provided IDV, not built in-house. Bits Technology capabilities announced December 2023; Entity Resolution links identity to transactions.
Continuous re-screening: 4,000+ watchlists, 2.6 million+ PEP records, refreshed every 15 minutes. Hits feed transaction evidence.
Separate NetReveal Sanctions Screening with AI overlay; Category Leader in Chartis’ Watchlist and Adverse Media Monitoring Solutions 2026 report (May).
Identical monitoring, case-management and reporting capabilities across SaaS, private cloud and on-premise deployment.
SRI marketed as cloud-native/evergreen on Azure; on-premise/hosted options (2022). Celent reported 93% on-premise monitoring installations and incomplete cloud containerisation in 2023.
Five documented regions: EU, UK, US, APAC and MENA.
Regional choice via Azure Marketplace and AWS partnership (2020). No published residency page.
Sandbox within 24 hours. API: 2-5 business days; SDK: 1-3. Public documentation covers endpoints, datapoints, attributes and response schemas.
First use case under three months (October 2025 SRI launch); 12-week fraud implementation described in blog. Public API documentation not found.
Response: Enterprise one hour; Free/Essentials 24 hours. Email, tickets and chat on every tier.
Support tiers/response times unpublished on reviewed pages. Celent customer references: 4.8/5 for support (2023).
10 free verifications/month. Essentials from $1.50/verification, up to 20,000. Transaction Trust Screening: Enterprise, priced on request.
Financial crime pricing, plan names and free trials unpublished; checked 10 September 2026.
One of 15 vendors that met Forrester's inclusion criteria for The Forrester Wave™: Anti-Money-Laundering Solutions, Q2 2025. Named a Leader in the G2 Anti-Money Laundering (AML) Grid® Report, Summer 2026, on verified customer reviews.
Forrester Wave Leader (Q2 2025); Chartis AML transaction-monitoring Category Leader (2025); Celent Luminary (2023); QKS SPARK Matrix enterprise-fraud Leader (2025). SymphonyAI leads here.
Gartner Magic Quadrant for Identity Verification: Honorable Mention; report published 28 July 2026.
Not applicable. No first-party identity verification product.
iBeta Levels 1-3; ISO/IEC 30107-3 conformance on iOS/Android, with Shufti-reported 0% attack presentation classification error rate (APCER).
Not applicable. No biometric product.
Shufti met every DHS RIVR 2025 selfie-to-document performance goal in published results.
Not applicable. No document or biometric product.
SOC 2 Type II, ISO 27001:2022, PCI DSS, Cyber Essentials Plus and QG-GDPR.
Certifications unlisted on reviewed financial services pages; request attestation letters.
 Category ratings matter more than overall averages.
Identity verification and AML categories. Read 10 September 2026. (G2)
Identity verification and AML categories. Read 10 September 2026. (G2)
LET'S GET SPECIFIC
Test Us With Your Edge Cases
Alert queue growing faster than your team? False positives eating analyst hours? Screening and monitoring in two systems that never talk? Bring a difficult investigation to the demo. We’ll walk through the customer evidence, triggered rules, review steps and reporting workflow, so your team can assess how Shufti handles the case.
Request A Transaction Monitoring Demo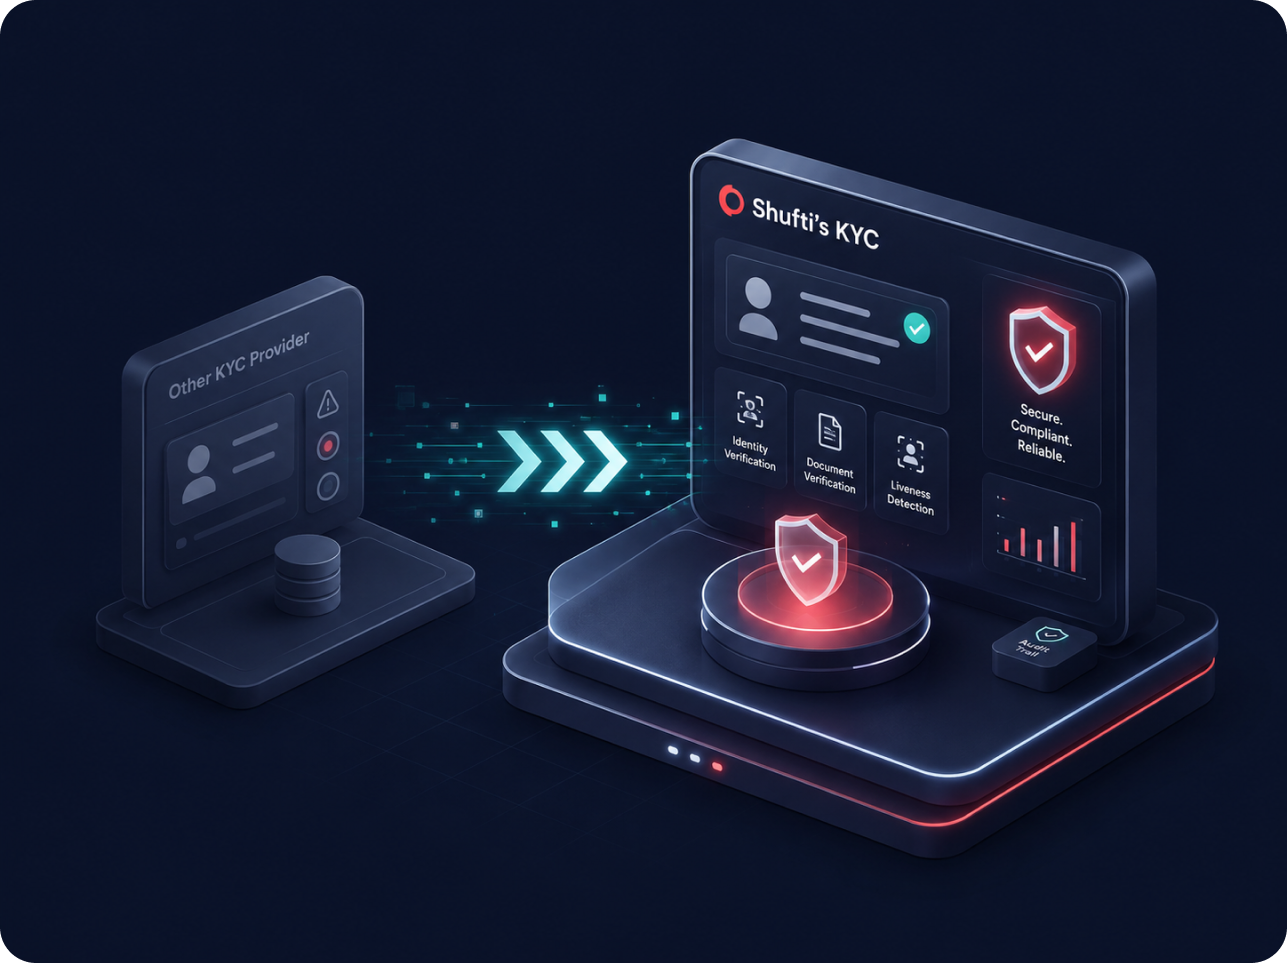
PLATFORM ARCHITECTURE
The Identity Behind Every Transaction Score
When identity checks and transaction monitoring sit in separate systems, investigators must piece together customer records before moving a case forward. Shufti brings identity checks, screening results, device signals and transaction history into one customer profile from the first session. Fraud and AML risk feed one score, rules require MLRO approval before going live, and alerts include supporting evidence. An append-only, five-year audit trail preserves every action and supports SAR, STR and CTR filing.
- Due DiligenceQuestionnaire answers and source of funds
- Device and BehaviourDevice fingerprint and session signals
- Transaction HistoryAmounts, velocity, corridors, counterparties
- Cases and ReportingAnalyst actions, notes and filing status
One Customer Risk Profile
Verified person or business, with every check retained against the same record
Governed transaction score- Document EvidenceAuthenticity, MRZ and tamper checks
- Face and LivenessSelfie match with a liveness result
- KYB and UBORegistry filings and ownership chain
- Screening OutcomesSanctions, PEP and adverse media
Rule Approval
Rules pass through compliance approval before they touch live traffic.
Context With the Alert
Alerts arrive with the evidence that produced the score.
Five-Year Audit Trail
Append-only retention that feeds SAR, STR and CTR filing.
IDENTITY-LED INVESTIGATIONS
See the Evidence Behind the Alert
A €9,400 payment leaves a two-month-old account for a new beneficiary in a higher-risk corridor. Here is the context Shufti can bring into the review.
- 01
Spot the Pattern
An unfamiliar device and a sudden increase in payment activity flag the transaction for review. The alert is the starting point.
- 02
Know the Customer
Review document and liveness results alongside available onboarding information, including the customer's declared source of wealth where collected and linked.
- 03
Connect the Evidence
Check the beneficiary's available screening status and linked accounts sharing the device to investigate whether the payment fits a wider pattern.
- 04
Keep Analysts in Control
The analyst reviews the case evidence. If reporting is warranted, AI drafts a SAR narrative from the case record for human review and approval.
Illustrative scenario. Evidence depends on collected data, enabled services and configured links. SAR = suspicious activity report.
DON’T JUST TAKE OUR WORD FOR IT, HEAR FROM OUR CUSTOMERS
The Confidence
Our Clients Share
Score
“We’re proud to have one of the lowest fraud rates of any gaming marketplace globally and we are always searching for new solutions to better improve the safety of our customers. Shufti provided the most effective KYC solution, allowing us to streamline our customer’s experience on the Kinguin Marketplace, ensuring purchases are as secure and convenient as possible.”
Onboarding
Rate
“We take our clients’ privacy very seriously, and we want them to know that we are constantly looking for new innovative solutions to ensure a safe banking experience. This is why we are proud of our recent partnership with Shufti, the AI-powered identity verification solutions provider, which will provide state-of-the-art identity verification. This collaboration falls under our strategy to provide a seamless and secure digital experience for our valued customers who prefer to use our online platform. We aim to improve our online banking and create an even safer service through the “Safwa Mobile” application.”
“As a relatively new brand, we need to absolutely ensure that initial brand interactions between Mintus and our customers are slick and smooth. To achieve this we need technology that is highly customisable to our needs and able to accurately verify individuals from across the globe. Not only does Shufti deliver this, it also does it quickly and easily – something our customers truly appreciate. We estimate that £150m of painting investments will be verified by Shufti this year.”
Score
“When potential customers informed us that our lengthy verification processes were hindering their due diligence verification, we knew we needed to make changes. Shufti had a reputation as a leading authentication expert that would be able to streamline our processes, while enhancing our risk detection. Through partnering with the team at Shufti we’ve been able to grow our customer numbers by 20%. At the same time we’re able to streamline their experience while on our platform and stop under-aged users and potentially fraudulent users from accessing our services. It’s a win win.”
“Given that we’re working with such vulnerable people, knowing exactly who is volunteering with us is vital, particularly as we need to have a large team on the ground. We needed a secure system that was not only highly accurate, but also time-saving. Shufti eliminated the need for our staff to implement extensive, manual ID verification processes and instead enabled us to focus on our two main projects in Ukraine – to deliver support to as many people as we can, and to grow the capacity of the charity so we can help even more people.”
INDEPENDENT VALIDATION
Shufti's Recognition Across Independent Evaluations
Trusted By 2000+ Businesses Across 240+ Countries And Territories
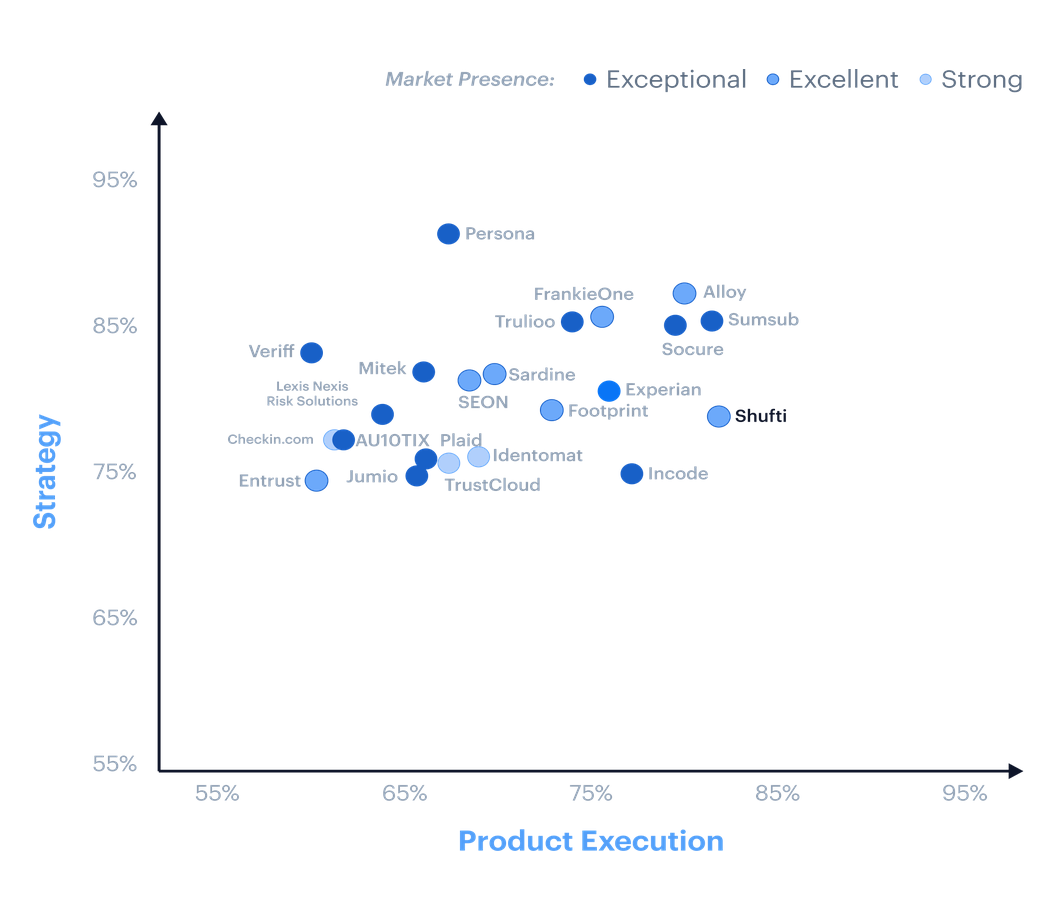
Ranked Exceptional in the Liminal Index 2026 for age estimation
View Report
Differentiated by Gartner on document diversity and country coverage
Read more
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
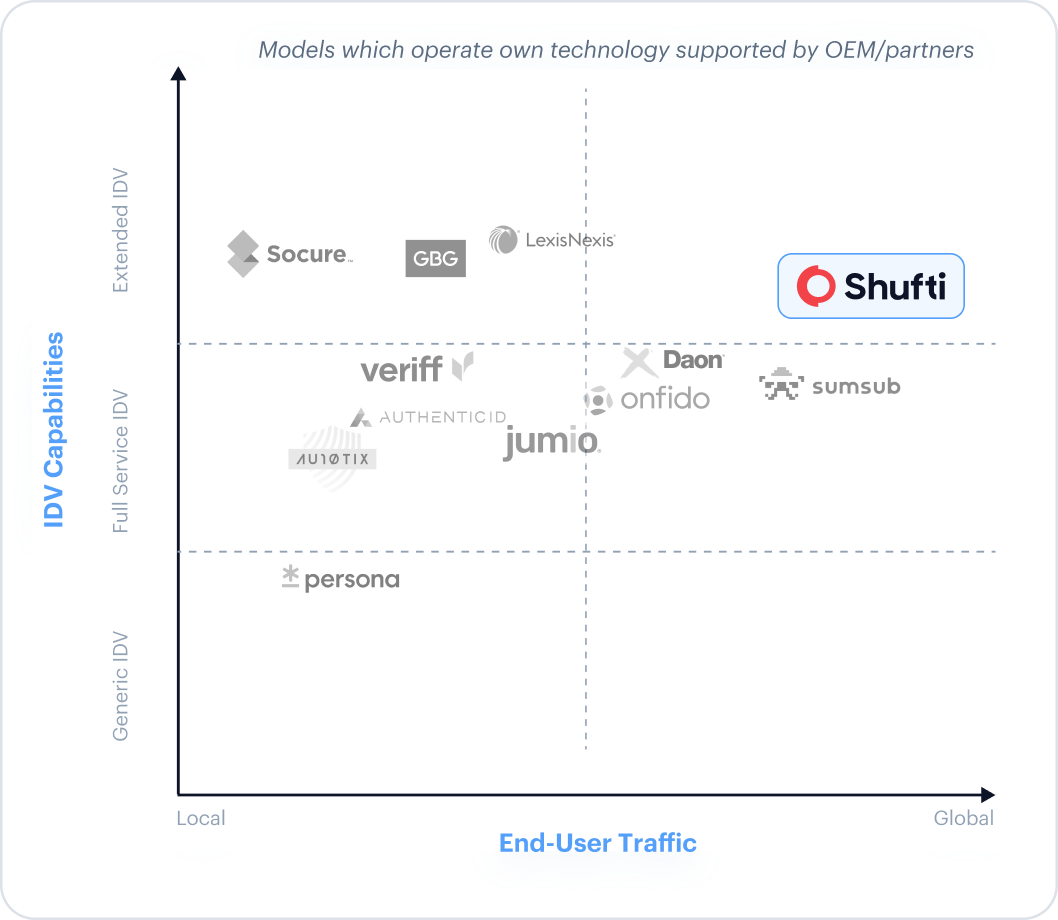
Broadest global reach in the 2025 KuppingerCole Extended IDV report
Download Report
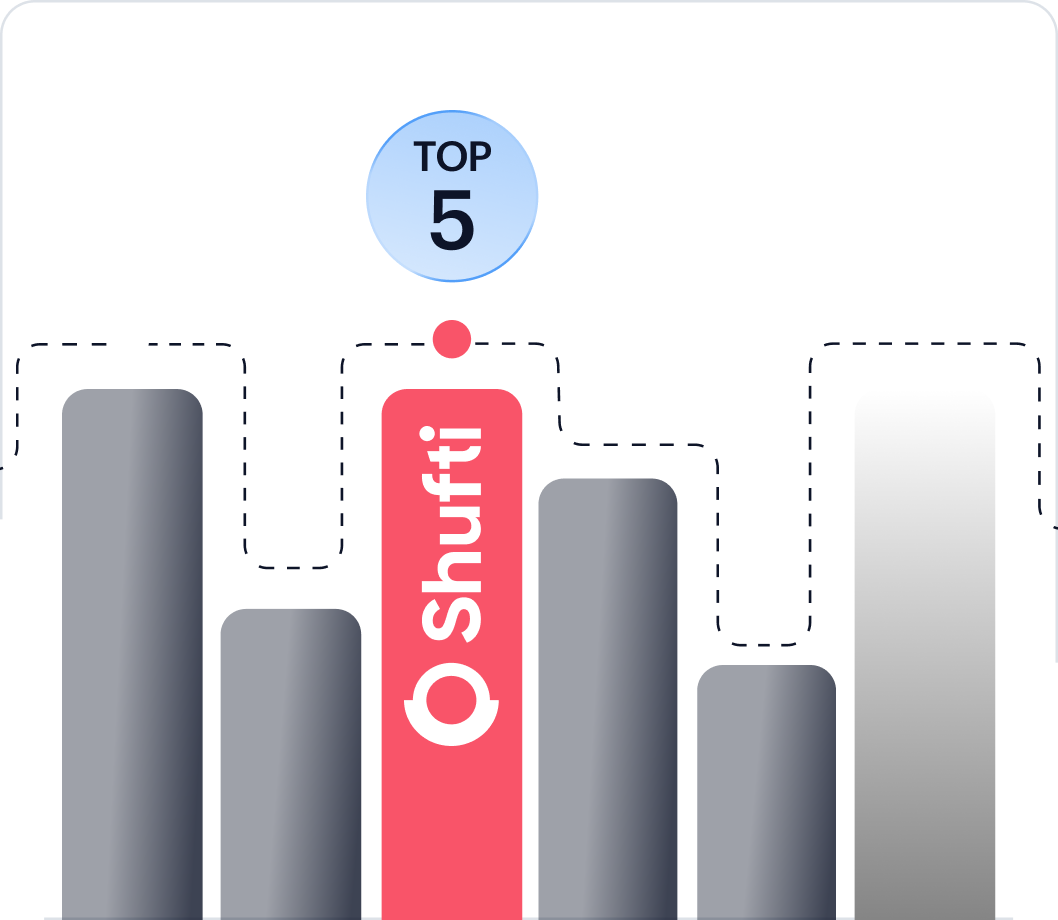
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
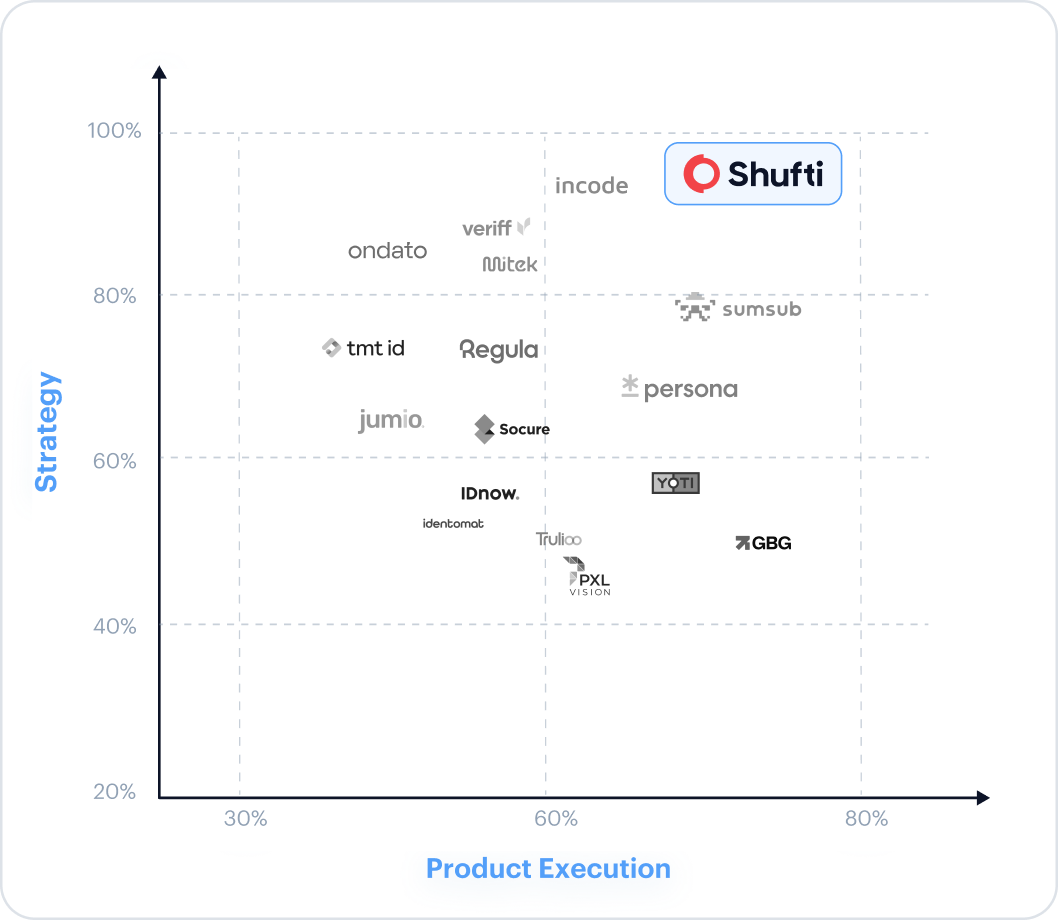
Top Vendor for Product Execution in the Liminal Index for KYC 2026
View Report
Ranked Exceptional for age verification by Liminal Index 2026
View Report
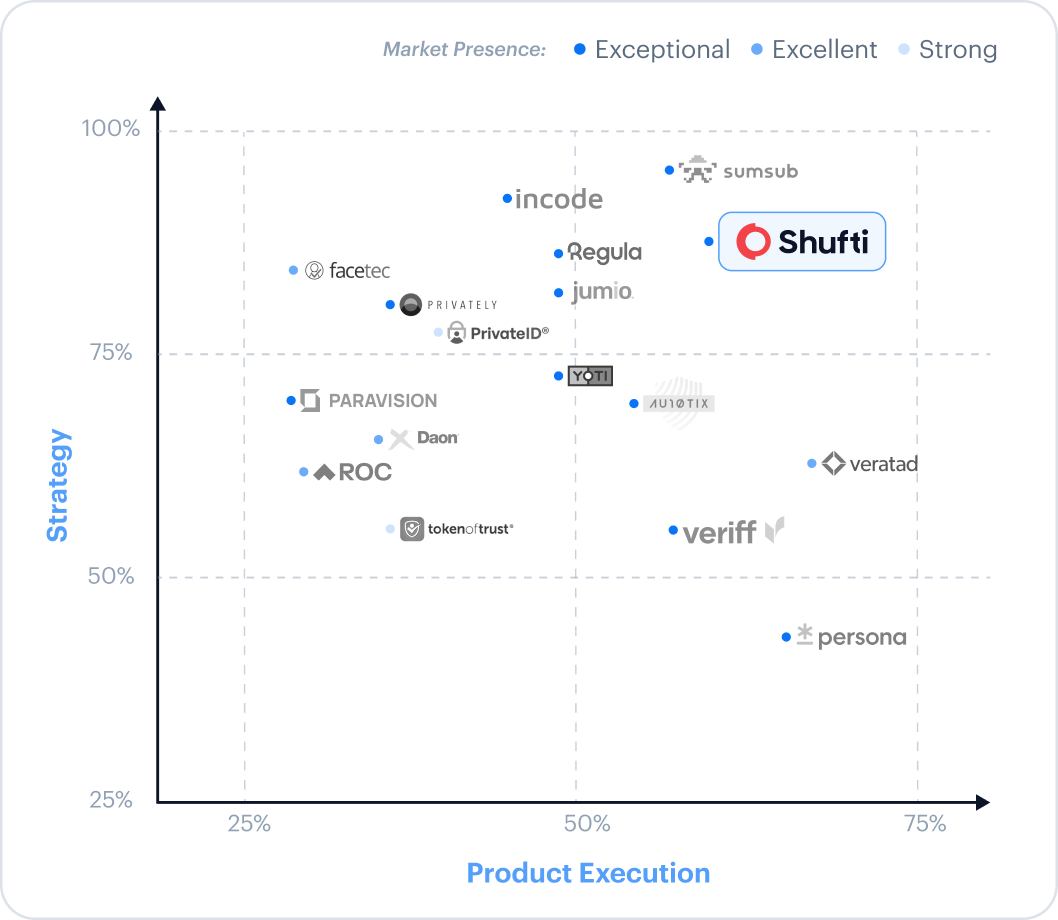
Recognised as a Leader in G2 Fall 2026 reports
Read More
ZERO DISRUPTION
Test Shufti Alongside SymphonyAI
Review your existing integrations, monitoring rules and historical-data requirements with our team. Agree the testing, approvals and cutover plan before moving production traffic.
- 0
Map the rules
Bring your NetReveal rules and 90 days of transaction history to prepare your sandbox.
- 1
Test and review
Review alert volume, false positives and expected workload. Your MLRO approves each rule before activation.
- 2
Move when ready
Compare results with your current setup, then move live transactions once testing and approvals are complete.
QUESTIONS YOU MAY HAVE
What Teams Ask Before They Switch
Direct answers to the questions that come up in evaluations, including the ones where SymphonyAI is the better fit.
Shufti scores activity against the identity it verified, returns fraud and AML risk as one composite score, lets compliance change rules without a vendor ticket and files to FinCEN, NFIU and CBI in native XML with MLRO sign-off. Integration takes days, against the three months SymphonyAI quotes for a first use case. Verify the advantage on your own rules, alerts and reporting outputs in the sandbox before cutover.
SymphonyAI does not publish pricing, plan names or a free trial for its financial crime products, and the 2020 AWS announcement described "a flexible commercial model with no upfront costs" without figures. Shufti pricing varies by product and volume, with 10 free verifications a month on the identity layer and Transaction Trust Screening on the Enterprise plan, priced on request. Compare matched quotes for the same scope rather than per-unit figures from different services.
In AML transaction monitoring SymphonyAI is benchmarked by Forrester, Chartis and Celent alongside enterprise vendors such as NICE Actimize and SAS. Shufti competes with SymphonyAI where transaction monitoring, fraud signals, screening and identity meet, and adds an identity layer SymphonyAI does not sell, rule activation that only an MLRO can approve, and sandbox access in 24 hours against the three months SymphonyAI quotes for a first use case. SymphonyAI publishes scenario self-service and a full MLOps environment, and does not describe an MLRO approval gate on its pages.
Shufti is the stronger fit when the use case runs from onboarding through monitoring on one platform, whether you are a bank, a fintech, a PSP, a remittance provider, an iGaming operator or a crypto exchange. Remittance teams get 50+ live rule sets, with fintech, banking, gambling, trading, crypto and lending packs following on the published roadmap. PSPs and marketplaces can score the seller side of a transaction through ten merchant datapoints, and iGaming and crypto teams tie transactions to the biometric and device links formed at onboarding.
Yes, and the evaluation should start with scenario coverage. SymphonyAI ships 2,500+ detection scenarios against Shufti's 50+ live rule sets, so a bank maps its active NetReveal scenarios to the Agentic Rule Builder first and confirms coverage in the sandbox before anything else. Where the bank also wants identity verification, screening, monitoring and filing on one platform with MLRO-owned rules, Shufti is the stronger fit. Where the priority is scenario breadth on day one or FINTRAC, AUSTRAC and NCA disclosure out of the box, SymphonyAI keeps the advantage, and the comparison above says so.
Export representative NetReveal alerts, decisions and 90 days of transaction history, define acceptance criteria, and describe your scenarios in plain language to the Agentic Rule Builder. Backtest each mapped rule on six KPIs, compare the results with your NetReveal baseline in the sandbox, and cut over once alert volume, false positives and reporting outputs meet the target and the MLRO signs off.
In the EU, UK, US, APAC or MENA region you select, or on your own infrastructure through private cloud or on-premise deployment. SymphonyAI markets SRI as a cloud-native platform on Azure, and its 2022 data sheets also list on-premise and hosted deployment.
Put a Verified Identity
Behind Every
Transaction Score
The next alert your team opens should already carry the person, the screening result, the device and the transaction on one governed risk profile with one composite score. Start in a sandbox provisioned within 24 hours, run your mapped rules against your own transaction history, and compare the evidence, analyst workload and reporting trail before you decide.