AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


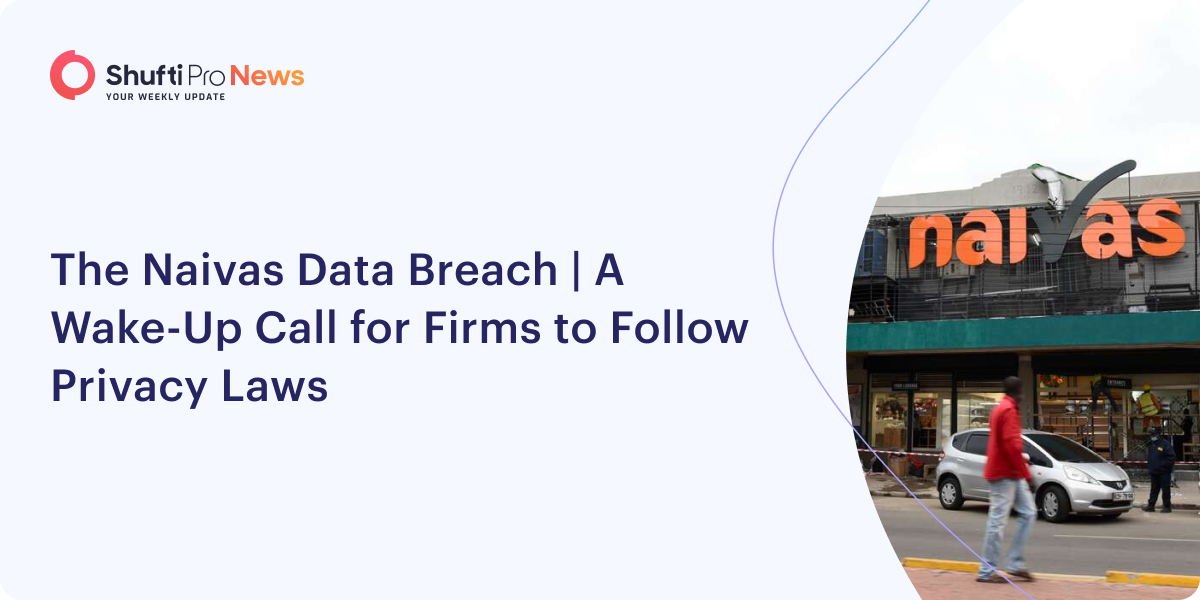
Naivas, one of Kenya’s largest supermarkets, recently suffered a data breach, highlighting the importance of companies collecting large quantities of personal information to adhere to the Kenya Data Protection Act (DPA, 2019).
Hackers allegedly stole customer and staff data from Naivas, one of the largest supermarkets in Kenya. The recent data breach illustrates how important it is for companies that collect large amounts of personal information to ensure strict compliance with the Data Protection Act.
Naivas says the breach has been acknowledged, and a cybersecurity firm has commissioned an investigation. The breach illustrates the importance of companies maintaining transparency about collecting and data usage. Data collection, usage, and protection of consumer information are fundamental rights consumers should know.
There has been dire consequences for retailers who have fallen victim to data breaches due to insufficient compliance with privacy laws, lets take a look at this around the world:
Target’s significant data breach in 2013 compromised 110 million customer records in the United States. Target has paid $18.5 million in settlements and fines in response to the breach, including $10 million in payments to class action lawsuits from affected consumers. Additionally, it left a permanent mark on the company’s image and a drastic downfall in the stocks.
Morrisons, a British supermarket, suffered a similar situation in 2014, when a former employee leaked the personal information of nearly 100,000 employees and customers. This included names, addresses, bank account numbers, and salaries. 5,000 Morrisons employees later filed a class action lawsuit against the retailer, and Morrisons was found liable. The employee was sentenced to eight years in prison for his part in the breach. After being found guilty of violating the UK Data Protection Act, the company was ordered to pay £2.5 million compensation. A significant amount of damage was also done to the company’s reputation.
Large and well-established companies can suffer severe financial and reputational ramifications from data breaches. Kenyan supermarkets are susceptible to data breaches. They should take appropriate measures to safeguard their customers’ information. The Naivas breach illustrates this point.
The Data Protection Commissioner is responsible for enforcing the Data Protection Act in Kenya. This Act imposes substantial fines for violations of the Act. In order to protect the privacy of their customers, Kenyan companies should comply with these regulations.
Suggested Reads:
CBN FINES GTBANK N128M FOR FAILING TO MEET AML AND CTF REQUIREMENTS
AUSTRALIANS LOST A RECORD AMOUNT OF OVER $3 BILLION TO SCAMS IN 2022