

 AMLR Solutions
 AMLR Consultation
 EUDI Wallet
 Onboarding
 Ongoing Monitoring
 FRAML
 KYC
 KYB
 KYI
 Age Assurance
 Workforce IAM
 Candidate Verification
 Account Takeover
 Bonus/ Promotion Abuse
 Chargeback Fraud
 Deepfake
 Document Fraud
 Fraud Networks
 Impersonation Fraud
 Money Mule Activity
 Multi-Accounting
 Party Fraud
 Regulatory & Compliance Risks
 Synthetic Identity Fraud
 Adult Content
 Banking
 Crypto
 Fintech
 Forex
 Compliance
 Fraud prevention
 Trust & safety
 Global expansion
 Compliance Officers
 Developers
 Fraud Analysts
 Product Managers
 Journey Builder
 Global Trust Platform
 Customer Profiles
 Vendor Comparison
 IDV Case Management
 AML Case Management
 Regulatory Reporting
 Agentic Rule Builder
 AI Compliance Co-Pilot
 Fraud Analytics
 Fraud Hub
 OCR
 Shufti AI
 Bank Account Verification
 Biometric Duplication
 Database Checks
 Document Intelligence
 Government ID
 Mobile Driver's License
 NFC
 Selfie Liveness
 Brand Personalisation
 Deployment Options
 Identity Methods
 IDV Modes
 Multi-tenancy
 On-Premise IDV
 Secure Capture
 Shufti MCP


- Australia
- Austria
- Bangladesh
- Belgium
- Brazil
- Bulgaria
- Canada
- China
- Croatia
- Cyprus
- Czech Republic
- Denmark
- Egypt
- Estonia
- Eswatini
- Ethiopia
- Finland
- France
- Germany
- Greece
- Haiti
- Hong Kong
- Hungary
- India
- Iraq
- Ireland
- Indonesia
- Italy
- Japan
- Jordan
- Kazakhstan
- Kenya
- Kosovo
- Kuwait
- Latvia
- Lithuania
- Luxembourg
- Malaysia
- Malta
- Mauritius
- Mexico
- Micronesia
- Moldova
- Mongolia
- Montenegro
- Morocco
- Mozambique
- Myanmar
- Namibia
- Nauru
- Nepal
- Nigeria
- Nicaragua
- Niue
- Norway
- Netherlands
- New Zealand
- Oman
- Pakistan
- Palau
- Palestine
- Panama
- Papua New Guinea
- Paraguay
- Peru
- Puerto Rico
- Philippines
- Portugal
- Poland
- Qatar
- Republic of Congo
- Romania
- Russia
- Rwanda
- Samoa
- San Marino
- Senegal
- Serbia
- Seychelles
- Sierra Leone
- Singapore
- Slovakia
- Slovenia
- Somalia
- South Africa
- South Korea
- South Sudan
- Spain
- Sri Lanka
- St Kitts and Nevis
- St Maarten
- St Lucia
- Sweden
- Switzerland `
- Syria
- Taiwan
- Tajikistan
- Tanzania
- Thailand
- Timor Leste
- Togo
- Tonga
- Trinidad and Tobago
- Turkey
- Turks and Caicos
- Turkmenistan
- Tunisia
- Tuvalu
- Uganda
- Ukraine
- UK
- USA
- Vietnam
FINLAND KYC, KYB AND AML
Scale Identity Verification and KYC Operations in Finland
Verify Finnish customers and businesses through Finland's notified Citizen Certificate, NFC, QES, documents, biometrics and KYB. Reduce manual review, maintain consistent audit evidence and run one connected workflow designed to support Act 444/2017 today and AMLR from 10 July 2027.
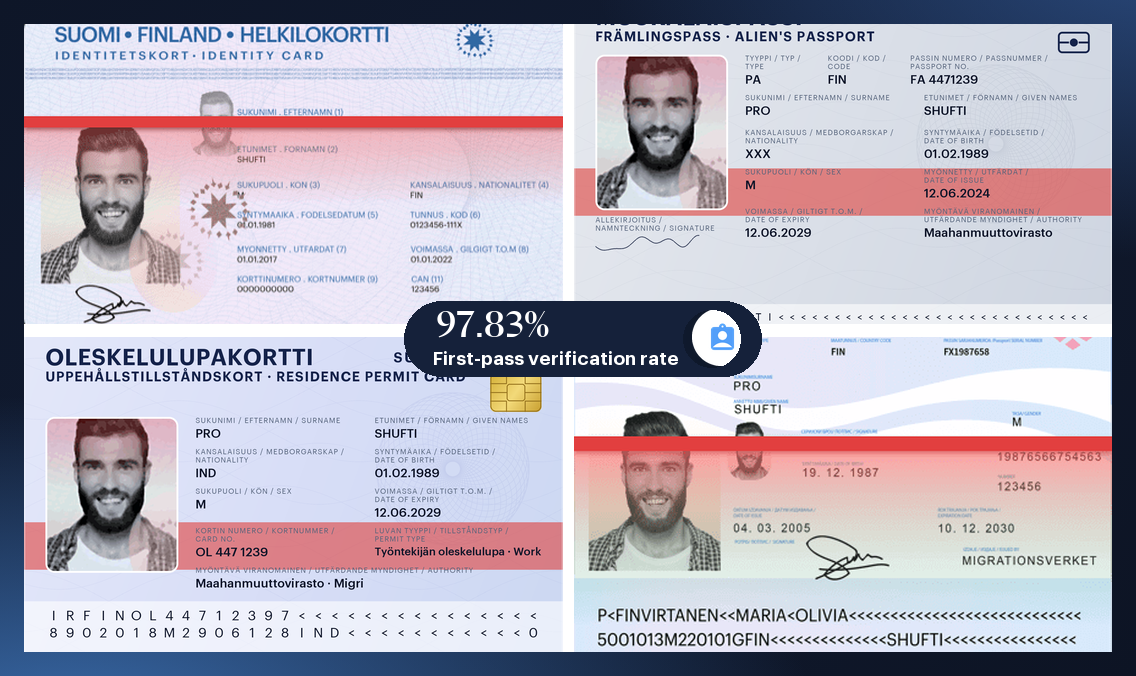


Operational Performance for Finland KYC
Our Numbers Speak Volumes
97.83%
First-pass
verification rate
< 10 sec
Median
verification time
5+
Finnish ID methods
supported
Finland IDV/KYC Challenges

The eID Split
Finland's only notified eID sits on the henkilökortti and needs a card reader. Everyday verification runs on bank IDs and Mobiilivarmenne, which need a Finnish bank or SIM.

Finnish Identifiers Break Global Matching
Since 2023 the henkilötunnus separator distinguishes people, so 100190-999P and 100190Y999P differ. Add ä, ö, å and four forenames, and matching breaks.

Ownership Data Is Gated and Set at a Different Line
Beneficial owner data sits inside the PRH Trade Register, not public, so extracts need identified recipients with an Act 444/2017 purpose. Finnish law uses over 25%; AMLR sets 25% or more, ownership or control, changing who is traced.

Registry Data Is Not Verification
The PRH Trade Register and the YTJ Business Information System confirm a company exists, not who controls it or whether they are sanctioned. KYB needs screening layered on top of registry lookups.
Regulatory Update
What AMLR Changes for Identity Verification in Finland
The EU Anti-Money Laundering Regulation (EU) 2024/1624 applies directly in Finland from 10 July 2027, with no transposition period. It sets the due diligence rules Act 444/2017 will operate under, with AMLA supervising from Frankfurt.
Timeline
- End of 2026 Member State wallet issuance target
- 2027 Suomi.fi Wallet, the Finnish wallet app, targeted for release
- 10 July 2027 AMLR applies, no transposition
- Late 2027 Acceptance duty begins, eIDAS 2.0 Art. 5f
- 2028 AMLA direct supervision begins
eIDAS Expressly Recognised
Article 22(6)(b) recognises eIDAS eID at assurance level substantial or high, with qualified trust services; Article 22(6)(a) expressly permits document-based verification. The strong electronic identification route under Chapter 3 Section 11 of Act 444/2017 continues, and firms should document why their method fits the risk.
The Ownership Test Tightens
AMLR harmonises the test at 25% or more of ownership, or control by other means, while Finnish law uses more than 25%. PRH data and KYB checks should confirm holdings at the 25% line. For higher-risk entity categories, the Commission may set lower ownership thresholds by delegated act under AMLR Article 52(2).
Existing Customers Get Re-Checked
AMLR expects existing customer records to be brought up to standard on a risk basis, not just new onboarding. Continuous monitoring keeps back-book files current between reviews.
Accountability Stays With You
Article 18 keeps customer due diligence accountable with the obliged entity even when verification is outsourced, so vendor evidence and clean audit trails matter more under AMLR.
FOR FIN-FSA-SUPERVISED BUSINESSES
Streamline FIN-FSA-Supervised Onboarding in Finland
Connect identity verification, QES, Penny Drop and compliance evidence in one configurable workflow for businesses operating within Finanssivalvonta's supervisory remit. Reduce customer drop-off and manual handovers while giving compliance teams a consistent, review-ready record of every decision.
FIN-FSA notes that non-face-to-face identification may require combining several methods and requesting further information from the customer and reliable, independent sources.
1. Verify the customer
Verify identity using the configured route, such as Finland's notified Citizen Certificate, a Finnish Trust Network bank ID or Mobiilivarmenne, NFC document reading, or document and biometric checks.
2. Complete qualified signing
Apply and validate the QES within the same journey, keeping the signed document, verification result and supporting evidence together.
3. Confirm the payment account
Penny Drop Verification confirms a payment from or into an account in the customer's name, an alternative measure under Chapter 3 Section 11.
Shufti's IDV/KYC Solutions for Finland
KYC Solutions
Clear onboarding for Finnish customers under Act 444/2017, with age and address checked in the same flow as identity, each check completing in seconds.
Explore More
Identity Verification
Shufti confirms every customer is real and present, not a spoofed or synthetic identity. Biometric face matching and liveness detection run against 10,000+ active ID document types.
.
Face Verification
Face verification binds the live person to the document with iBeta Level 3 Conformance to ISO/IEC 30107-3 liveness, stopping spoofs, masks and deepfakes.
.
Age Verification
Selfie-based age estimation combined with document verification fallback for age-restricted sectors such as gambling, alcohol retail and online marketplaces.
.
Address Verification
Shufti verifies Finnish address-bearing documents, including utility invoices, telecom bills and bank statements from major Finnish issuers. Proof-of-address checks remain common in regulated Finnish onboarding.
.
Document Verification
Verification of the henkilökortti identity card, the Finnish passport and the oleskelulupakortti residence permit card, including NFC chip reading and Finnish and Swedish language extraction. Remains a permitted route for remote verification under AMLR.
.
Bank Account Verification
Confirms a Finnish bank account (FI IBAN) belongs to the customer, returning the registered account holder name for matching against the verified identity.
.KYB Solutions
Shufti checks a business as deeply as the people behind it, supporting a risk-based approach. Shufti checks registry records, beneficial ownership and VAT details in real time, then screens UBOs against 4,000+ global watchlists for sanctions and adverse media exposure.
Explore More
Business Verification
Automated validation of PRH Trade Register data, the Y-tunnus business ID in 1234567-8 format, the Finnish VAT number as FI plus eight digits, and appointed directors and signatories. Reduces manual registry lookups and onboarding delays.
.
Enhanced Due Diligence (EDD)
Structured risk profiling for complex ownership chains, cross-border entities and higher-risk sectors, supporting Finland's risk-based AML obligations under Act 444/2017.
.AML Screening
Shufti screens customers and transactions in 240+ countries and territories, flagging sanctions, PEP, and adverse media matches as they happen. Ongoing monitoring surfaces suspicious activity in time to meet local reporting obligations.
Explore More
AI Compliance Copilot
Helps compliance teams review verification and AML data, investigate alerts, and understand the reasoning behind risk signals. It brings relevant case information together to support faster, more consistent compliance decisions.
.
Transaction Monitoring
Ongoing transaction monitoring calibrated to Finnish financial flows flags anomalies against AML rules, supporting the risk-based controls expected by Finanssivalvonta and the Financial Intelligence Unit.
.Supported Verification Methods for Finland
Every Verification Route Finland Uses, in One Platform
Shufti supports the full range of remote verification routes used in Finland, from the EUDI Wallet and the notified Citizen Certificate to bank IDs, chip reading and biometric checks. Each method below shows what is live today and what is ready for the 2027 rollout.
EUDI Wallet
Wallet-ready · from 2027Article 22(6)(b) points to electronic identification means at eIDAS substantial or high. The EUDI Wallet is not named in AMLR but meets that route. Suomi.fi Wallet, from the Digital and Population Data Services Agency, is targeted for 2027.
Notified eID
LiveeIDAS HighThe Citizen Certificate on the henkilökortti is Finland's only notified eID, at the High level. Shufti also supports Finnish Trust Network bank identification means and Mobiilivarmenne under Act 617/2009.
Docless Database (eIDV)
LiveDatabase-driven verification confirms identity in seconds for low-risk onboarding with no document upload, using permitted reference data sources. Shufti escalates to stronger checks as risk rises.
NFC Chip Verification
LiveShufti reads the secure chip in the henkilökortti, the Finnish ePassport and the oleskelulupakortti residence permit card, the high-assurance route where no card reader is available.
Document and Face Biometric
LivePermitted under AMLR Art. 22(6)(a). Section 11 accepts another electronic technique that is information-secure and evidential. Document authentication paired with iBeta Level 3 Conformance to ISO/IEC 30107-3 liveness.
Qualified Electronic Signature
LiveChapter 3 Section 11 sets enhanced due diligence for customers who are not present, and one route it allows is a qualified certificate for electronic signature under Article 28 of Regulation (EU) No 910/2014. Shufti runs eIDAS-qualified signing through Evrotrust, producing PAdES-LTV signatures via NFC and face biometrics.
Independent Validation
Shufti's Recognition Across Independent Evaluations
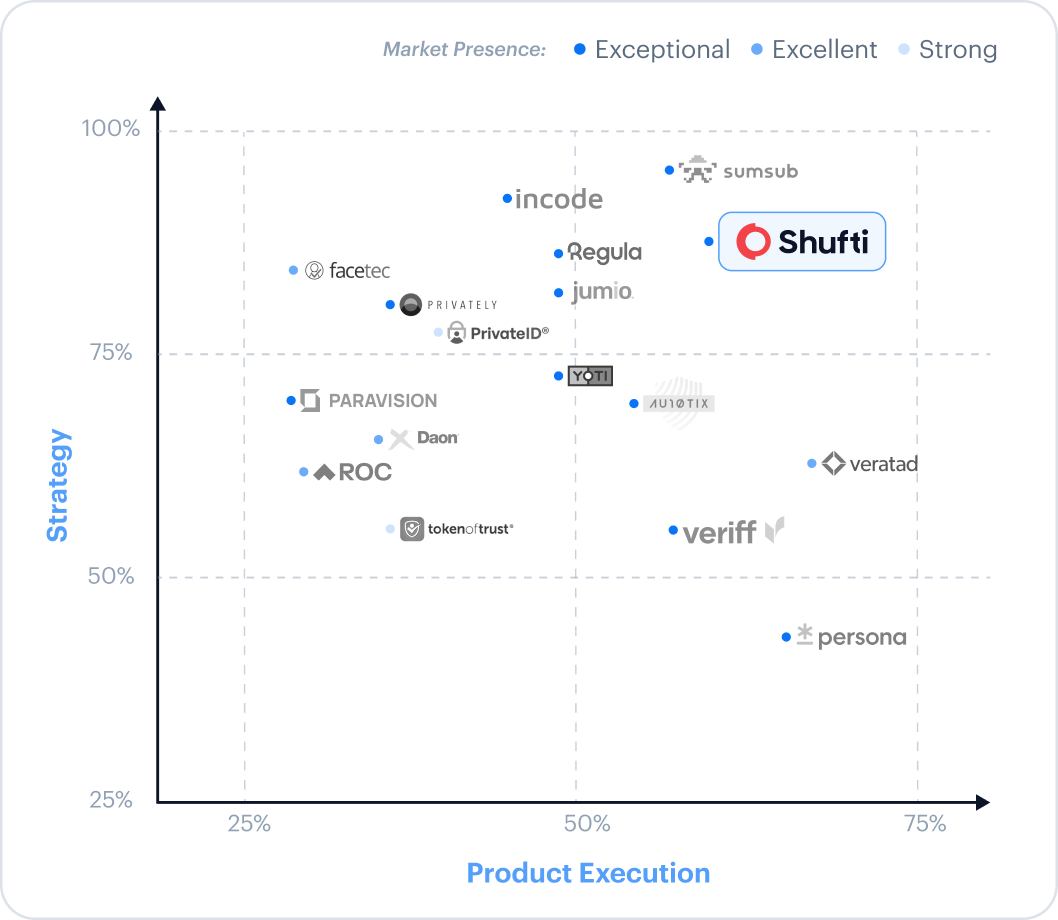
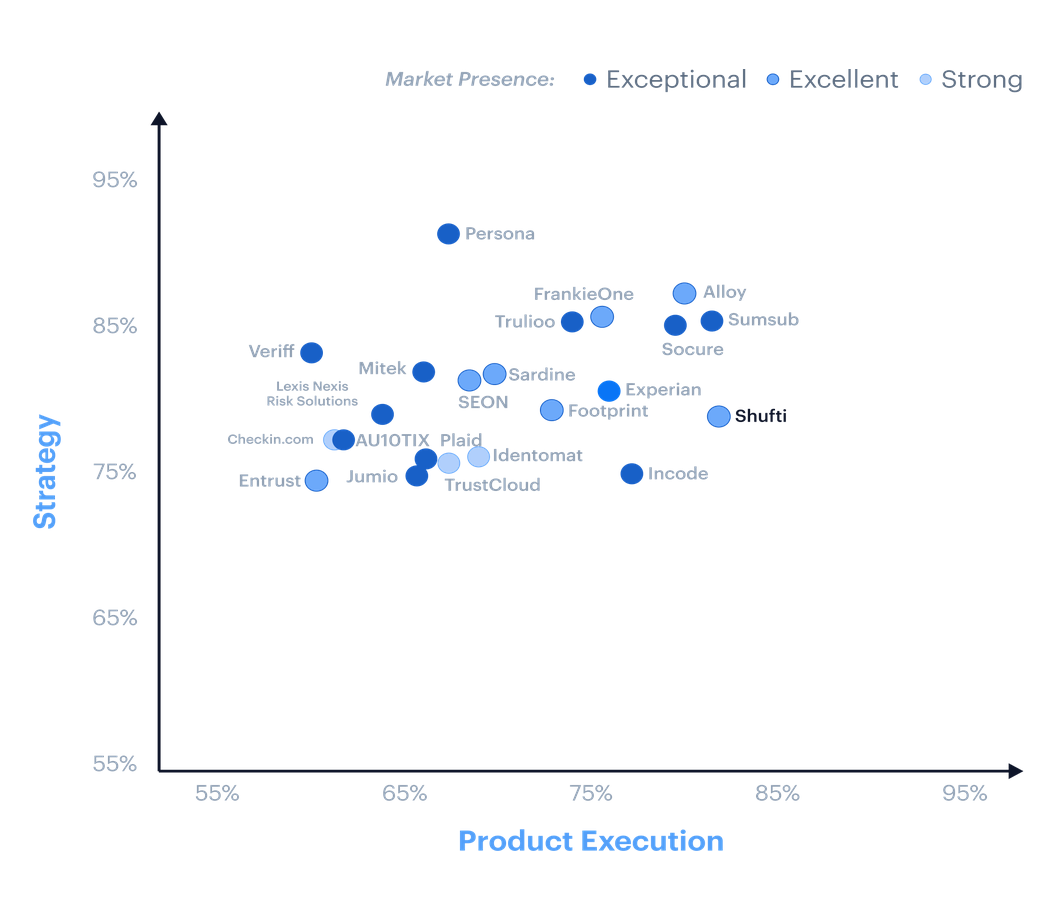
Ranked Exceptional in the Liminal Index 2026 for age estimation
View Report
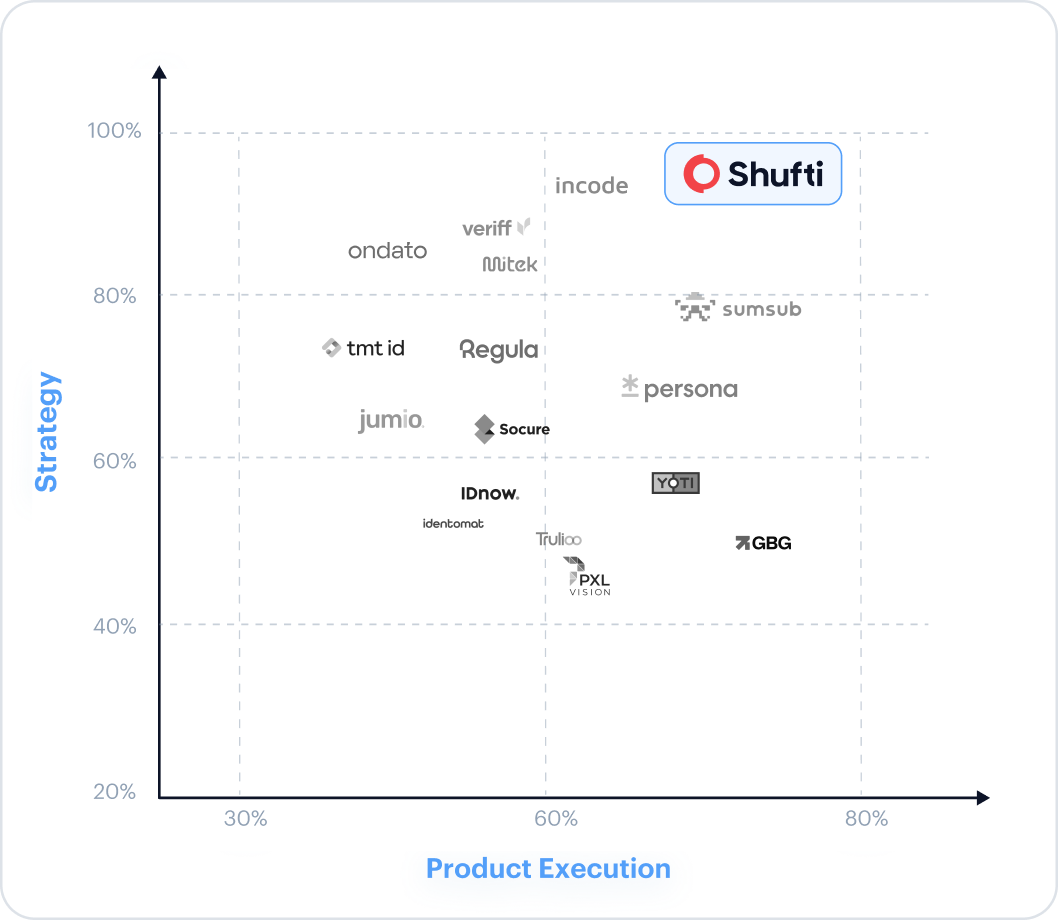
Differentiated by Gartner on document diversity and country coverage
Read more
Certified at iBeta Level 3 PAD with 0% APCER
Read Blog
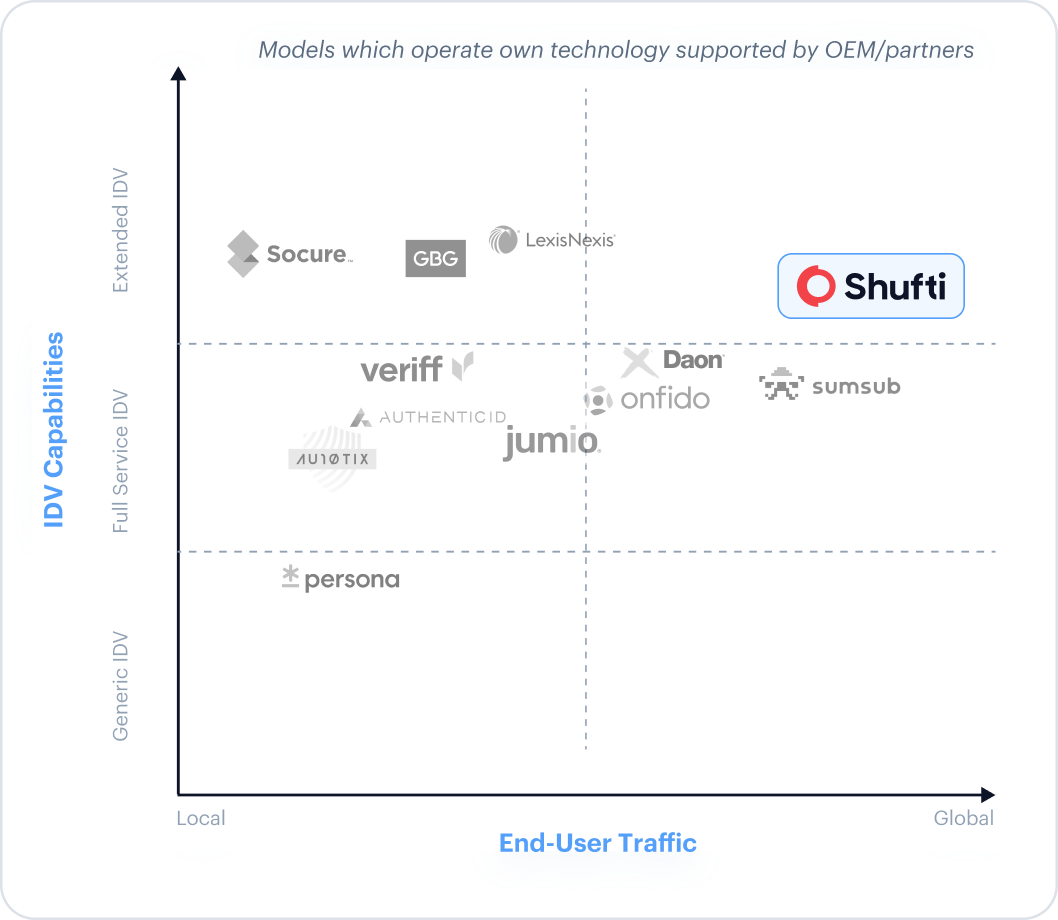
Broadest global reach in the 2025 KuppingerCole Extended IDV report
Download Report
Ranked Top 5 in the DHS RIVR 2025 for identity validation
Read Blog
Top Vendor for Product Execution in the Liminal Index for KYC 2026
View Report
Ranked Exceptional for age verification by Liminal Index 2026
View Report
Recognised as a Leader in G2 Fall 2026 reports
Read More
Evidence-Ready Checks Across People & Businesses
Verifications with robust evidentiary support
Individual Documents We Verify
Shufti supports 16+ Finnish document types.
View All Supported DocumentsFinnish Passport (Suomen passi)
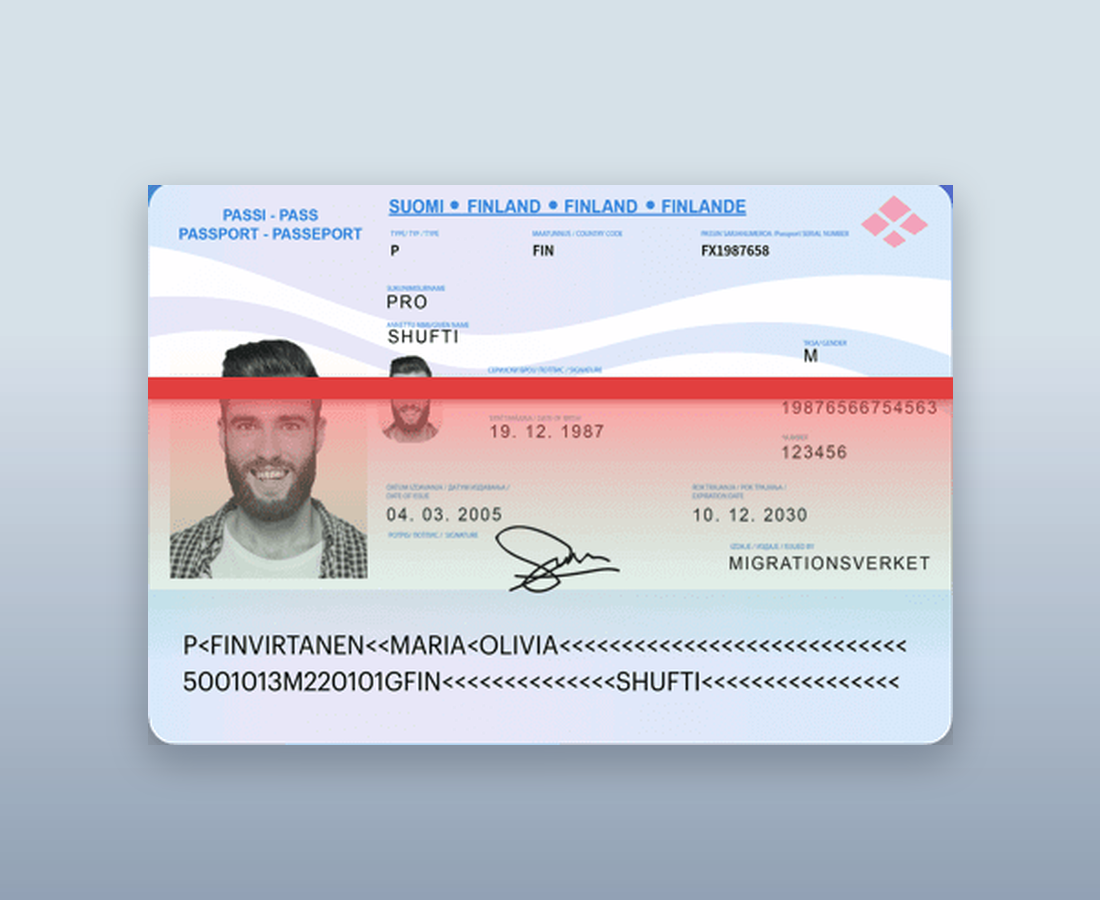
Biometric, ICAO-compliant passport issued by the police under the Passport Act (671/2006). Carries an NFC chip that supports chip-based checks for Finnish and cross-border onboarding.
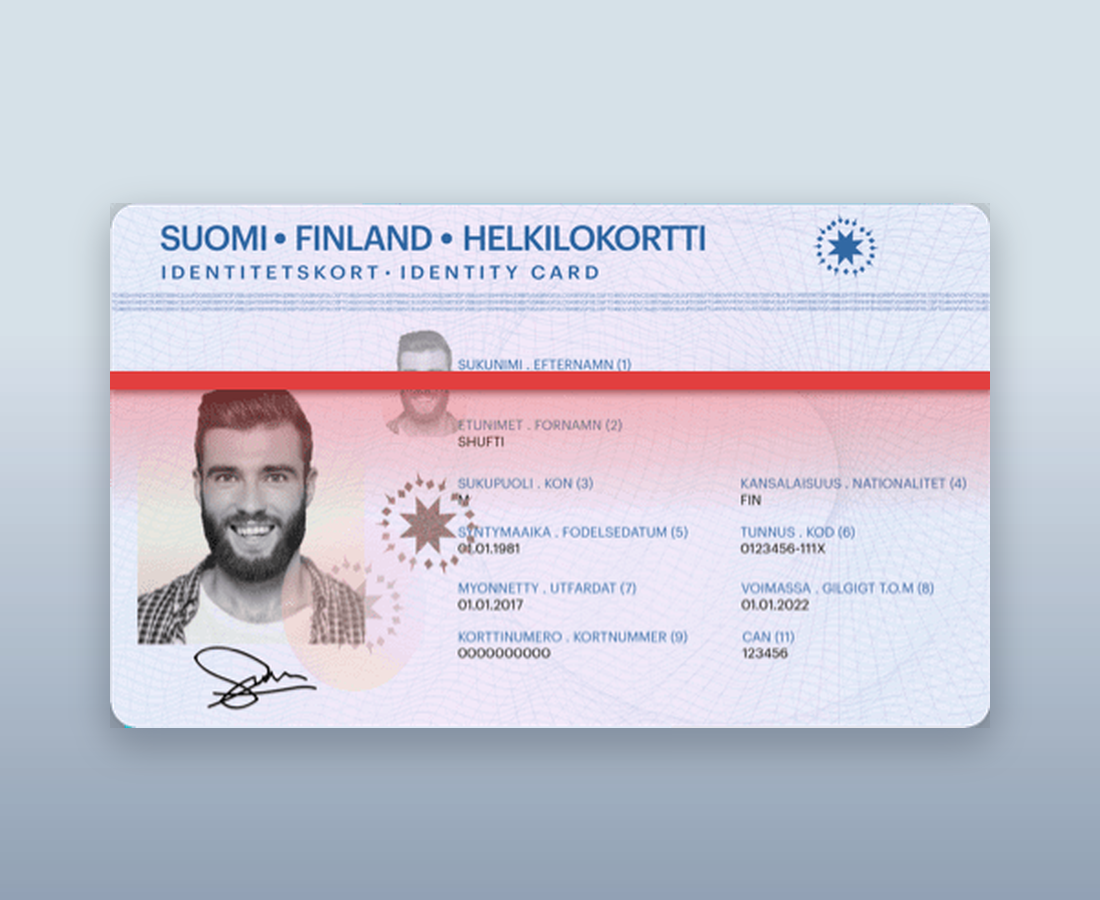
Finnish Identity Card (Henkilökortti)
Primary identity document issued by the police under the Identity Card Act (663/2016), valid for five years as a rule. Carries a chip and the Citizen Certificate, which is the eIDAS-notified eID at the High assurance level.
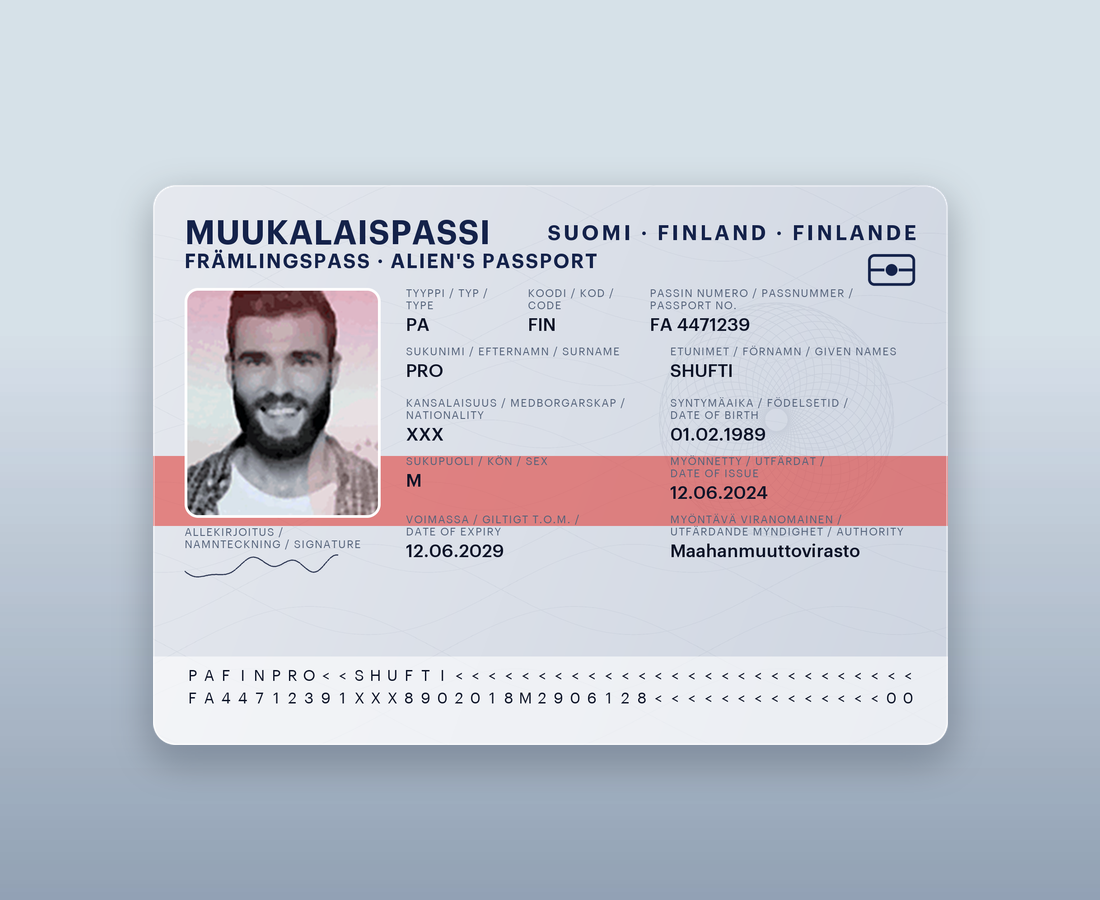
Alien's Passport (Muukalaispassi)
Travel document issued by the Finnish Immigration Service to people who cannot obtain a home-country passport. Migri states it is not an official identity document, so Shufti verifies it as supporting evidence alongside other checks.
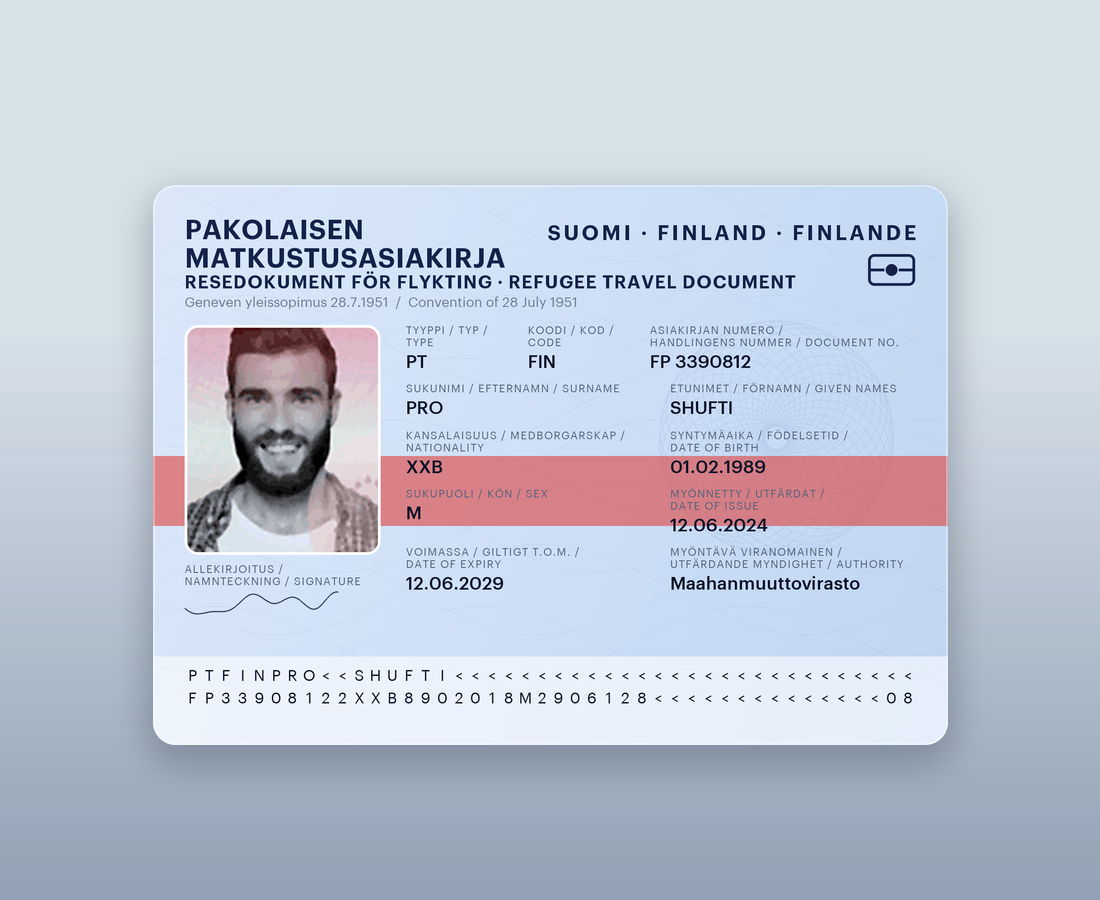
Refugee Travel Document (Pakolaisen matkustusasiakirja)
Travel document issued under the 1951 Geneva Convention to refugees residing in Finland. Migri states it is not an official identity document, so Shufti verifies it within a wider due diligence file.
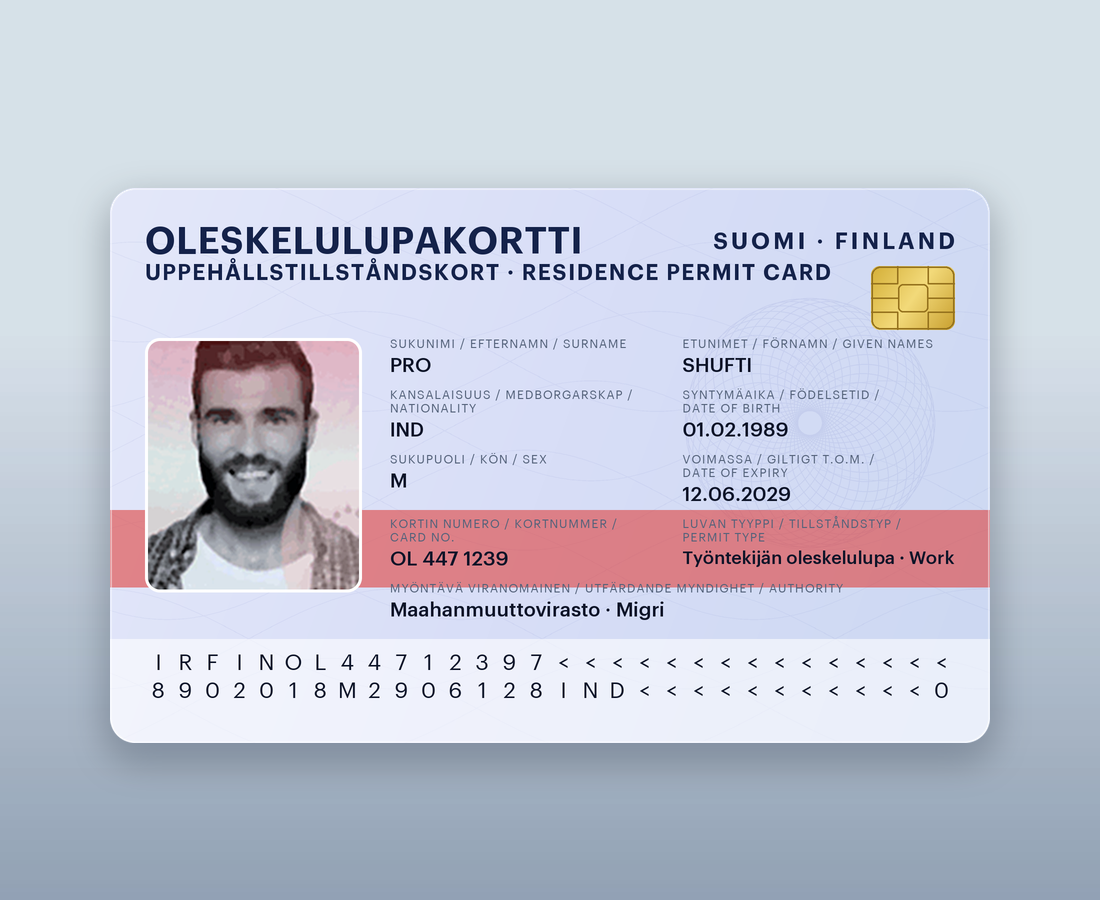
Residence Permit Card (Oleskelulupakortti)
Card issued by the Finnish Immigration Service to foreign nationals residing in Finland. It carries a biometric chip Shufti can read over NFC and is used alongside other evidence in customer due diligence.
Entity Identity
Trade Register Extract (Kaupparekisteriote)
Extract from the Trade Register held by the Finnish Patent and Registration Office. Confirms legal existence, registered address, company form, incorporation date, Y-tunnus and board composition.
Articles Of Association / Founding Documents
Filed with PRH at incorporation. Confirms company structure, governance rules and authorised signatories during KYB onboarding.
Business Information System (YTJ) Record
Record from ytj.fi, the system PRH and the Finnish Tax Administration maintain together. Confirms Y-tunnus status and core company registration data.
Tax Identity
Business ID (Y-tunnus)
Finnish business identifier in 1234567-8 format, seven digits, a dash and one check digit. Required for every entity registered in Finland and verified during KYB.
VAT Registration Certificate
Confirms VAT-registered status with the Finnish Tax Administration. The Finnish VAT number is FI followed by the Business ID without the dash, for example FI12345678.
Ownership & Control (UBO)
Beneficial Owner Extract (Tosiasiallisten edunsaajien ote)
Beneficial owner extract obtained from PRH. The data is not public, so an extract needs an identified recipient with a purpose under Act 444/2017. Shufti applies the AMLR test at 25% or more, ownership or control.
Shareholder Register / Ownership Register
Ownership register kept by the company itself and made available on due diligence request. Shufti uses it to map shareholdings and identify the people behind a Finnish company.
Languages We Cover
Finnish And Swedish Document Parsing
Native Finnish and Swedish parsing keeps ä, ö and å intact across the henkilökortti, the Trade Register and PRH beneficial owner data. Both are national languages under the Language Act (423/2003) and use Latin script, so no transliteration is needed.
Name Matching Logic
Matching handles Finnish and Swedish name forms, up to four forenames, and two-part surnames written with or without a hyphen. It also treats the henkilötunnus separator as distinguishing, which it has been since 2023.
Cross-Document Consistency Checks
Cross-document consistency checks reconcile names and identifiers across the henkilökortti, the Trade Register and PRH beneficial owner data, including bilingual municipality documents and Swedish-language documents from Åland, to catch mismatches.
Governance & Controls
Audit-Ready Decisions, Lower Operational Drag
Fewer avoidable re-submissions
Optimised capture for Finnish ID formats and NFC chip reading on the henkilökortti cuts avoidable re-submissions and manual review.
Cleaner audit trails
Structured logs aligned to the five-year retention rule in Chapter 3 Section 3 of Act 444/2017 and to Financial Intelligence Unit reporting keep every onboarding decision audit-ready.
Better name matching outcomes
Matching handles Finnish and Swedish diacritics, two-part surnames and the henkilötunnus separator, reducing false positives and manual review.
One workflow, one back office
KYC, KYB and AML screening are consolidated in one operational case view, so one back office team works on every customer file.
National ID-first flow design
Henkilökortti and bank ID first onboarding reflects Finland's national identity ecosystem and the way customers actually verify.
Continuous Compliance
Compliance that does not stop at onboarding
AMLR treats customer due diligence as a continuing obligation. Perpetual monitoring keeps the customer picture current between reviews, so risk is caught when it appears, not at the next annual check.
Surface Changes as it happens
DetectPerpetual monitoring flags risk when it appears, not at the next annual review. Behavioural biometrics, background fraud signals, and ongoing sanctions and PEP screening watch every active relationship.
Step up when the signal fires
VerifyWhen a signal fires, re-verification confirms the person or the ownership change using the same live methods above, so a flag turns into a resolved decision.
Keep the file audit-ready
ComplyEvery check and decision is logged to the record-keeping standard in Chapter 3 Section 3 of Act 444/2017, so the file is organised and retrievable for internal audit and supervisory review.
Perpetual KYC
pKYCKeeps individual customer risk current with behavioural biometrics, background fraud signals and ongoing AML screening, so back-book records stay standard-ready.
Perpetual KYB
pKYBMonitors PRH Trade Register filings and beneficial owner data for shareholding and control changes, so a shift past 25% or a change of control is caught between reviews.
Built To Fit Finland's Compliance Landscape
Financial Supervisory Authority (FIN-FSA)
Finanssivalvonta supervises banks, insurers, investment firms and payment institutions. Shufti supports its Regulations and guidelines 2/2023 on preventing money laundering with structured identity evidence, risk classification logs and ongoing monitoring controls.
Finnish Patent and Registration Office (PRH)
Maintains the Trade Register, holds beneficial owner data and supervises auditors. Shufti captures UBO data and screens controlling persons. Where your findings diverge from the register, Shufti flags the gap so you can file the valvontailmoitus to PRH under Chapter 6 Section 5 of Act 444/2017.
Finnish Supervisory Agency (LVV)
Lupa- ja valvontavirasto has supervised AML for non-financial obliged entities nationwide since 1 January 2026. Shufti AML workflows support real estate agents, pawnshops, accountants and trust and company service providers.
Ministry for Foreign Affairs
Acts as a competent authority for EU and UN sanctions in Finland and publishes sanctions compliance guidance. Shufti screens against these designations in real time on every check.
AMLA (EU Anti-Money Laundering Authority)
The new EU-level supervisor has been established in Frankfurt since July 2025. It begins direct supervision of selected high-risk cross-border entities from 2028 and shapes technical standards under AMLR.
Deployment Option
Cloud in EU regions, or on-premise, keeps Finnish customer data in-region and supports GDPR accountability.
Regulatory Alignment
Aligned with the customer due diligence, beneficial ownership and record-keeping duties in Act 444/2017, with GDPR and the Data Protection Act (1050/2018), and with AMLR requirements applying from 10 July 2027.
Retention Controls
Customer due diligence records are kept for five years under Chapter 3 Section 3 of Act 444/2017. The clock starts at the end of a permanent customer relationship, or at completion of an occasional transaction. From 10 July 2027, AMLR Article 77 keeps a five-year baseline and requires deletion at expiry, unless authorities require longer retention.
Encryption & Security
Encryption in transit and at rest, access controls and audit logging support Article 32 GDPR and Data Protection Act (1050/2018) duties under ISO 27001 certification.
Scope of Our Role
Shufti acts as a data processor and provides verification technology, not legal or regulatory advice. Customer due diligence and the choice among the Chapter 3 Section 11 measures remain with the obliged entity, documented in its own risk assessment.
Biometric Processing
The controller sets the lawful basis. Biometric identification engages Article 9 GDPR, and human review is available in the workflow.
Data and Privacy Controls in Finland
Finland AML Sources That Strengthen Decisions
We screen against 215+ sanction regimes, 4,000+ watchlists, 100,000+ adverse-media sources, and 6M+ PEPs across Finland and globally. A few of them are:
Financial Intelligence Unit (Rahanpesun selvittelykeskus), National Bureau of Investigation
Finnish Financial Supervisory Authority (Finanssivalvonta, FIN-FSA)
Finnish Supervisory Agency (Lupa- ja valvontavirasto)
Ministry of Finance (Valtiovarainministeriö)
Ministry of the Interior (Sisäministeriö)
National Police Board, Gambling Administration (Poliisihallitus)
Finnish Bar Association (Suomen Asianajajaliitto)
Finnish Patent and Registration Office (PRH)
Finnish Customs (Tulli)
Ministry for Foreign Affairs of Finland (Ulkoministeriö)
Financial Action Task Force (FATF)
EU Consolidated Financial Sanctions List
UN Security Council Consolidated List
European Banking Authority (EBA)
EU Authority for Anti-Money Laundering (AMLA)
SEE SHUFTI IN YOUR FINLAND WORKFLOW
Turn Finnish Verification Requirements into a Smoother Customer Journey
Share your customer types, risk rules and current onboarding process. A Shufti specialist will show you how to connect identity verification, KYB, QES, Penny Drop and ongoing monitoring, reducing operational hand-offs while keeping decision evidence organised for compliance review.
INDEPENDENTLY AUDITED. INDEPENDENTLY TESTED.
Certified to Global Standards




Frequently Asked Questions
Which identity documents can be used for Finnish onboarding?
Customers can use the Finnish passport and the henkilökortti identity card, including its chip and Citizen Certificate. Eligible EU and EEA identity cards, passports and the Finnish residence permit card can also be accepted when they meet the applicable requirements under Act 444/2017. Shufti supports document, eID, NFC and biometric verification within one configurable workflow.
How does Shufti support FIN-FSA-supervised businesses in Finland?
Shufti connects identity verification, KYB, AML screening, QES, account verification and decision evidence in one configurable workflow. This helps businesses within Finanssivalvonta's supervisory remit reduce manual hand-offs, standardise compliance records and prepare clearer evidence for internal audit and applicable supervisory review.
Can bank IDs or Mobiilivarmenne be used to satisfy customer due diligence in Finland?
Yes. Chapter 3 Section 11 of Act 444/2017 accepts identity verification using a strong electronic identification means under Act 617/2009, which covers Finnish Trust Network bank IDs and Mobiilivarmenne. Shufti supports these routes alongside chip reading and document plus biometric checks in the same workflow.
Does Finland operate an authorised video identification procedure?
No. Finland does not operate a separate authorised video identification procedure. Remote verification runs through the Chapter 3 Section 11 alternatives: additional documents or information from a reliable source, a payment from or into an account opened in the customer's name, or strong electronic identification, a qualified certificate for electronic signature, or another information-secure and evidential electronic technique.
What documents are required for KYB in Finland?
Typically a Trade Register extract from PRH, the Y-tunnus business ID, a VAT registration certificate and beneficial owner data. Shufti verifies these in real time and screens the UBOs behind them against sanctions and PEP lists.
How are Finnish name variants and identity codes handled in screening?
Matching accounts for Finnish and Swedish diacritics, up to four forenames, and two-part surnames written with or without a hyphen. It also treats the henkilötunnus separator as distinguishing, which it has been since 2023, so two codes that differ only by separator are not merged.
How long must AML records be retained in Finland?
Five years. Chapter 3 Section 3 of Act 444/2017 requires customer due diligence data to be retained for five years after the end of a permanent customer relationship, or five years from completion of an occasional transaction.
Is EU-region data hosting available?
Yes. Shufti offers EU-based cloud regions, so Finnish customer data stays in-region in line with GDPR and the Data Protection Act (1050/2018). On-premise deployment is available where residency requirements are stricter.
What changes for Finland under AMLR from July 2027?
AMLR applies directly, so no Finnish transposition law is needed for the Regulation itself. It expressly recognises eIDAS-notified eIDs and qualified trust services as one route, permits document plus biometric checks as another, and moves the beneficial ownership test from more than 25% to 25% or more.
How do QES and account verification work together in Finland?
Chapter 3 Section 11 of Act 444/2017 accepts a qualified certificate for electronic signature under Article 28 of Regulation (EU) No 910/2014 as one route, and a payment from or into an account already opened in the customer's name as another. Shufti connects QES, account verification and supporting evidence in one workflow.
When will the EUDI Wallet be usable for onboarding in Finland?
Under eIDAS 2.0, member states target wallet issuance by end of 2026, and firms required to use strong user authentication must accept the wallet under Article 5f. The Digital and Population Data Services Agency is building the Finnish wallet app and has published a release target of 2027. Shufti is built to accept wallet-based verification as the Finnish wallet goes live, so onboarding flows will not need to be rebuilt.
Let’s Build Trust Into Your Business
1B+Verifications Processed
240+Regions Actively Processed
99.7%Accuracy Rate
Samer Al Tamimi
CEO of Safwa Bank
“We take our client’s privacy very seriously and always look for new innovative solutions to ensure a safe banking experience. Working with Shufti feels like a breath of fresh air, as their 100% in-house tech keeps our customer’s data free from vulnerabilities and fully safe and protected.”
Trusted. Compliant. Certified
Explore Shufti For Your Business
Get a personalised demo from our experts.
PROVEN PLAYBOOKS
Explore Practical KYC & AML Resources
10 July, 2026
Identity Verification in Europe: eIDAS 2.0 & EUDI Wallet
A practitioner's guide to verifying identity in Europe, covering eIDAS 2.0, the EUDI Wallet, docless eIDV and how to choose an eID provider for onboarding in the EU.
Product Guide